u-root's newest release is titled as a toolchain deprecation notice, and the module has moved two versions past it
A fully Go userland with Linux bootloaders! u-root can create a one-binary root file system (initramfs) containing a busybox-like set of tools written in Go.
At a glance
- What is it?
- u-root is a Go reimplementation of a Linux userland that can be packed into a single binary and an initramfs, with Go bootloaders alongside. It is a serious piece of systems work with an unusually candid README, and the candidness is the story: the front-end command says it will be replaced, the release titles carry migration warnings, the demo runs on the wrong operating system, and three different Go versions are in play.
- Who is it for?
- Fit this if you are building firmware, a hypervisor payload or an initramfs and want a userland you can read in one language rather than assemble from a binary distribution. Work from the source rather than installing the front-end command, because the project says that command is on its way out in favour of another name from a sibling repository, and pin your toolchain to the module's declared version rather than the floor the usage section prints.
- Can I use it commercially?
- Yes. BSD-3-Clause is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
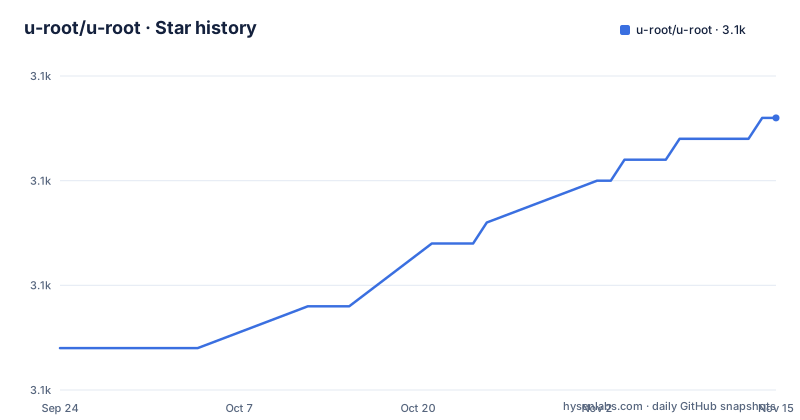
- u-root/u-root3,088 ★ · +11
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| u-root/u-root | 3.1k | 3.1k |
11 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The newest release is a deprecation notice and the module moved on twice
The release titles in this repository are notes rather than labels. The newest one says, in full, that it is the last release before moving to a particular Go language version. The one before it describes bare-metal support work and a conversion of commands into packages. The one before that announces breaking build-system changes. So the project version numbers double as changelogs, which is useful. It also means the newest release is explicitly a boundary marker. The module file has since moved past that boundary twice over, and the usage section still prints an older floor as its requirement. Three Go versions are therefore in play at once, and the two a newcomer reads first are both wrong.
Four tool names for one job
The file is careful to say that the front-end command is a wrapper. One note states that the command is the same as a tool in another repository with some defaults applied, and the same note says that a differently named command will replace it in the near future. A third tool is suggested for the narrower job of building only the busybox-style binaries. So there are four names in play for building an image: the one the install instructions tell you to fetch, the underlying tool it wraps, the planned replacement, and the busybox-only builder. The install path a newcomer follows points at the one the project describes as temporary, and nothing in the usage section says so at the point where it matters.
The demo runs on the operating system the project is not for
The demo section opens by saying what it looks like on one desktop operating system and adds, in parentheses, that it was tested on Linux too. The demo is a small tool that builds a throwaway image and boots it in a virtual machine, and recreating it takes a clone, a build and one cross-compiled invocation:
git clone --depth 1 https://github.com/u-root/u-root
cd u-root/tools/testramfs
go build
GOARCH=amd64 GOOS=linux ./testramfs ../.. # ../.. is the path to u-root source
The performance claims attached to it are specific: rewriting 115 commands into Go packages by walking the compiler's own syntax tree and recompiling all of that into one command takes seven seconds, about the same on two other architectures, and the whole set including booting the virtual machine and exiting takes thirty-one seconds. It also notes that you do not need to supply a kernel for any of the three architectures, because one is built in.
Every command becomes a symlink to one six-megabyte binary
The multi-module example is the clearest statement of what the busybox-style build produces. You set up a workspace with the main repository and a second one, ask for two commands from the first and one from the second, and the resulting archive listing shows a single executable of a little over six megabytes with three symbolic links beside it, one per requested command, all pointing back at that executable. Two details in the same listing are worth noticing. Every entry is stamped with the first of January 1970, which is what a reproducible build looks like when it works, and the permission bits are restrictive on the main executable compared with the symlinks.
The extra-files flag takes the destination before the source
There is a flag for putting host files into the image, and its separator reads the opposite way round from what most people assume. The documented example pairs a shell in one directory with a path under sbin, and the archive listing shows the file landing at the second path. A second example does the same with kernel modules, landing each one under a directory in the image rather than in the home directory it came from. So the left side is where the file ends up and the right side is where it is read from. By default, when the entry is a binary, its shared-library dependencies are discovered and added too, and a flag turns that off for three stated reasons: reproducible builds, cross-compilation, and controlling exact library versions.
Two of the four documented invocations depend on shell brace expansion
The examples section gives four ways to build an image. The first takes no arguments and takes a default set. The second names two templates that expand into sets of commands. The third lists commands inside curly braces, and the fourth uses a flag whose value is a brace list. Those last two only produce the intended set when they are typed into a shell that expands braces; handed to the program directly, as a script or a process spawn would, the braces arrive literally. There is also an admonition that the tool works exactly when the two standard Go build and list commands work, with a link to a section about processor architecture level, which is the project's way of saying that its behaviour is inherited from the toolchain rather than guaranteed independently.
Dependencies are vendored and most are pinned to a bare commit
The repository commits its vendor directory, which is what makes the offline build path possible and is why a truncated comment in one of the examples refers to vendored builds. The module file lists around forty direct requirements, and a striking number of them are pinned to a date-and-hash pseudo-version rather than to a release tag, including a kernel-side DHCP implementation, a traffic-control library, a virtual machine test harness, a kernel framebuffer library, and two of the project's own helper libraries. Pinning to a commit is defensible for a userland where a dependency is effectively part of the appliance, but it means the module file alone does not tell you which upstream releases you are running.
Six test libraries sit in the main dependency block
The first requirement block of the module file is where a project usually separates what the binary needs from what the tests need. Here they are mixed. A console-expectation library for driving terminals, a pty library, a unit-testing framework, a mocking library and two comparison libraries all appear as direct requirements rather than as indirect ones, which means they are linked into the shipped binary's module graph. Alongside them sit a packet-crafting library, a traffic-control library, and a pure-Go reimplementation of the interface-configuration utility. That last one is the pattern worth noting: rather than shelling out to an existing system tool, the userland reimplements it, which is the whole thesis of the project expressed as a dependency.
Editorial conclusion
Fit this if you are building firmware, a hypervisor payload or an initramfs and want a userland you can read in one language rather than assemble from a binary distribution. Work from the source rather than installing the front-end command, because the project says that command is on its way out in favour of another name from a sibling repository, and pin your toolchain to the module's declared version rather than the floor the usage section prints. Read the shared-library behaviour before adding host binaries to an image, because the default pulls the host's libraries in and quietly gives up reproducibility.
Frequently asked questions
what is u root
A set of Go versions of standard Linux tools, a way to compile many of them into one binary, a way to build an initramfs archive that can be embedded into firmware, and Go bootloaders that use the kernel loading mechanism to boot Linux or multiboot kernels. The project calls itself four projects in one.
how to install u-root
Either clone the repository and run the Go install command in it, or install the command directly from its module path at the latest version. The file notes the resulting binary lands in the Go workspace's bin directory, so it may need adding to your path.
What Go version does u-root need?
The usage section says a version at or above a stated floor, but the module file declares a much newer language version, and the newest release is titled as the last release before an intermediate Go move. Read the module file rather than the usage section.
How does u-root produce one binary from many commands?
It compiles the commands into a single executable and symlinks each requested command name to it inside the image. The workspace example shows one executable of a little over six megabytes with three symlinks beside it, and every entry stamped at the epoch for reproducibility.
Can I put my own binaries in a u-root image?
There is a flag for extra files, and its separator takes the destination first and the source second, so a pair like a home-directory shell and a path under sbin lands the file at the sbin path. By default the binary's shared-library dependencies are added too, which a second flag disables for reproducible builds or cross-compilation.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/u-root-u-root)Star history chart for your README
[](https://hysenlabs.com/projects/u-root-u-root)Was this useful?