Novamira's feature is PHP execution inside WordPress, and its warning is three words
MCP server that gives AI agents full access to WordPress through PHP execution and filesystem operations
At a glance
- What is it?
- A WordPress plugin that exposes PHP, the database and the filesystem to an AI agent over a local model-context protocol server, authenticated as an administrator. The page is clear about the capability and almost silent about the consequence.
- Who is it for?
- Read this as a description of remote code execution with a convenient interface, because that is what it is. The capability list is unambiguous: an authenticated agent can run PHP and WP-CLI commands, reach the database through the WordPress query object, read and edit files on disk, and start background processes, all under an administrator account, with no narrower scope described anywhere on the page.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 9 days ago.
- What is it written in?
- Mainly PHP, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
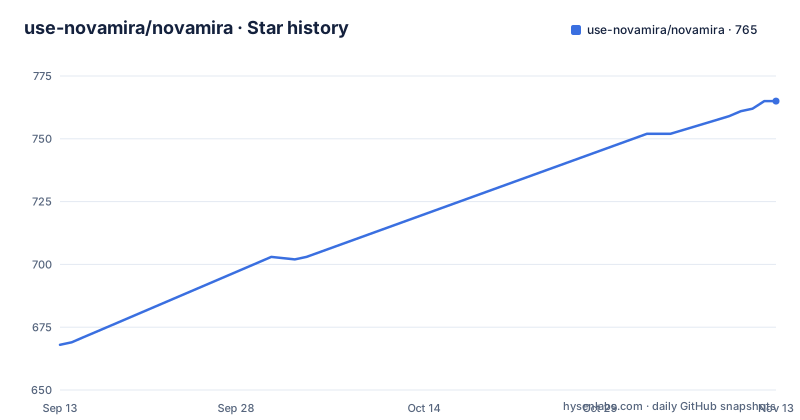
- use-novamira/novamira765 ★ · +97
| Repository | 2026-09-13 | 2026-11-13 |
|---|---|---|
| use-novamira/novamira | 668 | 765 |
97 Stars in the last 61 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The feature list is a remote code execution surface
The page describes what the plugin gives an agent, in its own words: full access through PHP execution including the database query object, loaded plugins, themes and the WordPress APIs; command line commands with foreground and background execution; filesystem inspection and editing, plus a recoverable sandbox for new PHP files; native block editor workflows, media uploads, reusable skills and design guidance. Put plainly, that is an authenticated caller who can run arbitrary PHP as the web server user, write files into the installation, and leave work running after the request ends. The connection model is direct, which is good for privacy and worth noticing for risk: the server runs inside the site rather than at a vendor, so the capability lives with your installation and is reachable by anything that can authenticate to it.
The entire safety instruction is three words
Between the description and the videos there is one warning block, and its whole content is that it is for development and staging environments, with backups, always. No elaboration follows it, no list of what to disable, no note about which roles should hold access, no mention of what an agent should never be pointed at. A longer document titled security and best practices is linked near the bottom of the page, so the guidance exists; it simply is not on the page, and the page is what a reader sees before installing. The requirement list compounds the gap by asking for a WordPress administrator account, which is the account that can do everything the plugin can do.
Administrator credentials plus PHP execution, with no narrower scope
Authentication is either OAuth or WordPress application passwords, and the requirements say you need an administrator account. Nothing on the page describes a narrower role, a per-tool allow list, a read-only mode, or a way to give an agent the database without the filesystem. The recoverability language applies to new PHP files in the sandbox, which is a sensible narrow guarantee, and the rest of the surface has no stated equivalent. The remote transport requirement is worth reading too: HTTPS is required for remote connections, and local development environments are supported without it, so the unsupported-configuration path is the one a developer will actually be on.
What you install is not what the repository contains
The installation section instructs you to use the release archive from the download page rather than the archive GitHub generates, and gives the reason: the source archive does not include the bundled Composer dependencies the server needs. That is a candid admission that the artefact you install cannot be reproduced from the repository alone, since those dependencies are resolved and bundled during a release build. For a plugin whose whole purpose is running code for an agent, that gap is the one to think about, because it means reviewing the repository is not the same as reviewing what runs. The repository itself is a proper plugin tree, with a main file, an uninstall routine, stub declarations, a test configuration, and a dependency lock file.
WordPress 6.9 is the floor, so most existing sites are excluded
The requirements are specific and one of them is decisive: WordPress 6.9 or later, alongside PHP 8 or later. A plugin that will execute agent-written code against a live site cannot be offered to a site on an older WordPress without a much larger discussion, and the page does not have one. and it also asks for HTTPS for remote connections and an administrator account, and for either a model-context-protocol client or a terminal agent driven by the project's own command line tool. So adoption is gated on a very recent WordPress, a hardened transport, and an account with the widest permissions the platform offers, and the page does not discuss what happens if an agent using it is prompt-injected by the content of a page it happens to be reading.
Four product names, and no page-builder statement
One repository is four things: the plugin and server, a command line tool for terminal agents, an experimental browser workspace where you watch an agent work in WordPress, and a set of documentation, video and download pages on a marketing site. The page names the block editor and mentions design guidance, and it never names a page builder, which is conspicuous because the questions people search for around this project are about one in particular. That gap is not a criticism so much as a boundary: the page describes what the project claims, and the ecosystem compatibility people ask about is not part of it.
Three patch releases in two weeks on a code-executing plugin
The release history is three tags in a fortnight, at patch level inside the same minor line, and the newest was published minutes after the last commit. That is a fast-moving project and it is also the update surface for something that executes code on your behalf. The repository reflects a codebase with several toolchains side by side: a Composer manifest and lock file for the plugin itself, a private package manifest whose only dependency is the WordPress build tooling, compiled through a task runner into the plugin's asset directory and then post-processed by a second script, a PHP formatting and analysis configuration, and a separate directory for the experimental workspace. Contributing requires an approved issue before any pull request, and the repository carries agent instruction files and directories alongside the human-facing documentation, which tells you something about who the intended caller is.
Editorial conclusion
Read this as a description of remote code execution with a convenient interface, because that is what it is. The capability list is unambiguous: an authenticated agent can run PHP and WP-CLI commands, reach the database through the WordPress query object, read and edit files on disk, and start background processes, all under an administrator account, with no narrower scope described anywhere on the page. The single safety instruction offered is a three-word warning telling you to use it on development and staging environments, with backups. A separate security document is linked but not summarised, and the page gives you no guidance on what an agent with this access should not be asked to do. If you need an agent inside a live site, the defensible version of this is a staging copy you can throw away, and the check before you deploy anything is whether your agent's tool calls are logged in a place you actually read. What this repository does document well is its build: a PHP plugin with a bundled chat interface, a single patch-level release line moving fast, and an install artefact that is not reproducible from the repository.
Frequently asked questions
What is Novamira?
An open-source WordPress plugin that also acts as a model-context-protocol server, letting an AI client work directly inside a WordPress installation: running PHP and command line commands, reaching the database, inspecting and editing files, and understanding the active plugins and theme. The connection is direct rather than proxied, so requests do not pass through the vendor's servers, and it is licensed AGPL-3.0-or-later.
Is Novamira safe to use?
The page carries one warning, and it is three words long: for development and staging environments, with backups, always. The capabilities it describes include PHP execution with database access, file editing and background commands, and the requirements ask for an administrator account. A separate security and best practices document is linked, but the page itself gives no guidance on restricting what an agent can reach.
How do you install Novamira?
The page gives three steps and puts its warning above them: download a release archive from the project site, upload and activate it through the plugin screen, then open its configuration screen and enable the AI abilities. It also says to use that release archive rather than the source archive GitHub generates, because the source archive does not include the bundled dependencies the server needs.
Does Novamira work with Divi?
The page does not address it. It describes native block editor workflows and design guidance, and it names no page builder at all. The only compatibility statements on the page are the client list, which covers several AI tools, and the platform requirements, which are WordPress 6.9 or later and PHP 8 or later.
Is Novamira free to use?
The page states the licence as AGPL-3.0-or-later and describes the project as open source, and it contains no price anywhere. It links a separate download page, documentation and video pages, so anything commercial would be described there rather than in the repository itself.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/use-novamira-novamira)Star history chart for your README
[](https://hysenlabs.com/projects/use-novamira-novamira)Was this useful?