Vendure: extending a headless commerce core through plugins, service overrides, and two GraphQL surfaces
Open-source headless commerce platform built with TypeScript, NestJS, React, and GraphQL
At a glance
- What is it?
- Vendure puts catalog, orders, pricing, promotions, channels, tax, shipping, payments, and stock on a single Node.js and GraphQL backend that you change through plugin contracts instead of forks. The core is GPLv3, while single sign-on, approvals, and contract pricing come with paid plans.
- Who is it for?
- Vendure fits teams that intend to change the commerce core and can own the deployment: the extension model is real, the commerce domain is built in, and the plugin license exception keeps your storefront off GPLv3. It does not fit teams that need single sign-on, approvals, or contract pricing without a paid plan, or that need a generally available managed runtime now, since Vendure Cloud is in design-partner preview.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
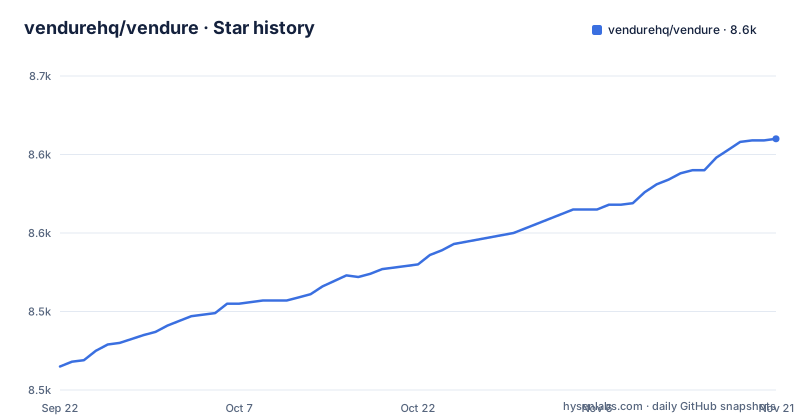
- vendurehq/vendure8,610 ★ · +145
| Repository | 2026-09-22 | 2026-11-21 |
|---|---|---|
| vendurehq/vendure | 8.5k | 8.6k |
145 Stars in the last 60 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
One npx command emits server, admin dashboard, and GraphQL API together
Getting a shop running is a single command, and it scaffolds the server, worker, admin dashboard and GraphQL APIs.
npx @vendure/create my-shopYou do not clone `vendurehq/vendure` to build a store, and you do not install the core and assemble NestJS modules by hand. The argument after the command becomes the project directory, and from that point the generated project is yours.
That boundary shapes how you debug. A stack trace from a scaffolded shop lands in files you generated, with the framework sitting behind a dependency boundary, so understanding framework internals still means reading `packages/` in the framework repository rather than your own tree. The repository says as much in a single line: build with `npx @vendure/create`, and clone only when you intend to contribute to Vendure itself.
The planning consequence is that the version you pin at scaffold time is the version you inherit. Upgrading later means moving a generated project forward, not re-running a generator against new inputs and getting fresh scaffolding for free.
The engines field pins Node 20.19 or 22.12 and the database is your pick
The runtime floor is declared rather than implied. The root `package.json` carries an engines constraint of `^20.19.0 || >=22.12.0`, and the README asks for Node.js 22.12+, adding that 20.19+ still runs but Node.js 20 is end-of-life. A CI image pinned to an earlier Node 20 patch will not satisfy that range, so the check belongs in your build setup before the first deploy, not after it.
Storage is your decision across four engines: PostgreSQL, MySQL, MariaDB, or SQLite. That spread covers a single-file local database and a managed cluster, but the choice is yours before the first order exists. SQLite removes a service from your local stack; PostgreSQL or MySQL puts connection handling, version upgrades, and backups on your operations list from day one.
What the getting started block does not contain matters as much. There is no migration command and no rollback path in the text, only a link to the getting started guide, which covers configuration, seed data and your first plugin. Budget time to read that guide before estimating the build, and treat your schema change procedure as a decision you still owe.
The compose file is a test rig where three databases claim port 3306
The compose file in the repository root is not a deployment recipe. Its own header comment says it holds the services required to develop and test Vendure locally, and the service list matches that claim: MariaDB, MySQL 8.0, MySQL 5.7, PostgreSQL 12.3, plus Elasticsearch and Redis.
Read the ports before borrowing any of it. `mariadb`, `mysql_8`, and `mysql_5` each publish `3306:3306`, so three services want the same host port. Only one of them binds at a time, and the failure surfaces as a port conflict rather than a database error. The PostgreSQL service is the only one carrying tuning, and the tuning is aimed at test observation: its command sets `shared_preload_libraries=pg_stat_statements` and `max_connections=200`.
Credentials are the user `vendure`, the password `password`, and the database `vendure-dev`. Copying this file into a deployed environment means shipping four database engines, developer logins, and a port collision to whatever host you point it at. If you scaffolded with `npx @vendure/create`, you do not have this file at all, and you still need to provide a database yourself.
The GPLv3 exception is scoped to plugins, and the core is not included
Licensing is where a self-hosted commerce core gets misjudged, so the split is worth reading closely. The project is open source under GPLv3. It also states that building against the GraphQL API does not make your storefront or your services subject to GPLv3. On top of that, a plugin license exception lets you release your own Vendure plugins under any license you choose, and a licensing FAQ is linked for the details.
The exception names plugins, and that word carries the weight. Plugin contracts and service overrides are the sanctioned route to changing pricing logic, adding entities, and altering workflows without patching the core, so the ordinary extension path stays inside the exception. A change that has to live in the core itself, or a fork, is a different question, and the FAQ linked from the license section is where to settle it instead of assuming the plugin answer generalizes.
What is not open: a commercial license comes with each of Vendure's paid plans, with pricing on the vendor site. The core you can read, extend, and self-host therefore arrives with license terms your legal team may still need to examine, and the project points at exactly one document for that question.
SSO, approval workflows, and B2B pricing are named as the paid Platform layer
Three capabilities teams tend to assume are in the box are named in the paid layer instead. Vendure's four paid plans (Starter, Growth, Scale and Enterprise) are built on top of the open-source core, and the list of what they add is specific: company accounts, quotes, contract pricing, account hierarchies, approvals, single sign-on and audit logs. B2B is the sharp edge, because B2B is advertised as a use case for the same core while contract pricing, approvals and single sign-on sit in the paid plans.
Your options are therefore three, not two. Budget for a paid plan, build SSO and approval flows yourself on the open core, or accept the gap and scope them out of the first release. The same split applies to operations. Self-hosting means you own the deployment, the data, and the stack, running anywhere Node.js runs, including Docker, Kubernetes, a single VM or any cloud provider. Vendure Cloud is the managed runtime: it deploys on git push and manages the database, queues, search, backups and scaling, it is included in every paid plan, and it is in design-partner preview with general availability planned for Q1 2027, so choosing it trades the deployment burden for a vendor dependency.
Every paid plan also includes direct support from the Vendure team.
The monorepo is a Bun and Lerna workspace built for contributors
Anyone opening this repository expecting a deployable application finds a contributor workspace instead. The lockfile is `bun.lock` alongside `bunfig.toml`, orchestration runs through `lerna.json`, and the test and e2e entries execute as `lerna run test --stream --no-bail` and `lerna run e2e --stream --no-bail`. Directories separate concerns a consumer never sees, including `packages/`, `e2e-common/`, `docs/`, `skills/`, and per-version changelog files.
The release script shows what maintenance actually costs. Its `version` step chains `bun install`, `check-imports`, `check-angular-versions`, `generate-platform-promotion-snapshot`, `build`, `check-core-type-defs`, and `generate-changelog`, then stages `CHANGELOG*`, `*/version.ts`, and `bun.lock`. A check named for Angular versions still gates releases, although the README describes the admin dashboard as React and TanStack.
For someone evaluating adoption, the practical consequence is that consuming and contributing are separate jobs with separate toolchains. Consuming needs Node, a database, and a generated project. Contributing adds Bun, Lerna, and the generator scripts behind `codegen` and `docs:build`, where GraphQL types for the shop and admin APIs are produced from the same schema files a consumer would only read.
Two introspectable schemas, shop and admin, are checked in as JSON
Vendure exposes two GraphQL surfaces rather than one, and the repository keeps both as committed artifacts. `schema-shop.json` and `schema-admin.json` sit at the root, and the docs generator is invoked twice with different flags, once with `--api=shop` and once with `--api=admin`. Client type generation is a separate step again, with `codegen:gql-tada` producing the types used against those endpoints.
That split has consequences for anything you automate. The project makes the point that the introspectable schema makes it straightforward to wire up LLM tool-calling, MCP servers, and agent frameworks. Introspection is a property of a schema rather than a permission boundary, so an agent attached to whichever surface answers first can end up on the administrative API rather than the storefront one. The shop API is the surface for public storefront traffic, and the two schemas are not interchangeable.
Having both files committed as JSON is useful for that reason. You can diff them, notice a removed or retyped field in a patch release, and keep a pinned copy of the contract your storefront client was written against. Nothing in the getting started path does that comparison for you.
Three patch releases in ten weeks with no stated support window
Maintenance signals here are concrete. Releases land on a steady cadence: v3.7.4 on 2026-10-05, v3.8.0 on 2026-10-12, and v3.8.1 on 2026-10-23, with the default branch last pushed on 2026-11-02. The project says patch releases ship regularly and points at the release notes, and the repository keeps four changelog files: `CHANGELOG.md`, `CHANGELOG_NEXT.md`, `CHANGELOG_v1.md`, and `CHANGELOG_v2.md`.
What is not written down is a support window. No compatibility range for plugins appears in the getting started text, and there is no rollback procedure, no stated policy for when breaking changes may land, and no list of versions still receiving fixes.
For a team taking real orders, the consequence is procedural. Pin exact versions instead of ranges, read the release notes before every patch bump, and re-run your own end-to-end suite, because the repository's `e2e` script protects the framework rather than your plugins. Patch-numbered releases also mean your custom plugins deserve the same review as your application code.
Editorial conclusion
Vendure fits teams that intend to change the commerce core and can own the deployment: the extension model is real, the commerce domain is built in, and the plugin license exception keeps your storefront off GPLv3. It does not fit teams that need single sign-on, approvals, or contract pricing without a paid plan, or that need a generally available managed runtime now, since Vendure Cloud is in design-partner preview. Before committing, read the plugin license exception against the specific changes you plan to make, confirm your database choice and Node version match what you already run, and read the release notes for the exact patch you would pin, since no support window is stated.
Frequently asked questions
What is a vendure?
Vendure is an open-source headless commerce platform: a Node.js, NestJS, and GraphQL backend paired with a React and TanStack admin dashboard, distributed under the GPLv3 license.
What is vendure used for?
It models catalog, orders, pricing, promotions, and customers on a single backend, and that same core is used to run D2C, B2B, marketplace, and omnichannel storefronts.
Is Vendure a good ecommerce platform?
It fits teams that need to change core behaviour, since plugins and service overrides remove the need to fork, while single sign-on, approvals, and contract pricing are part of the paid plans.
vendure vs medusa
The project draws no comparison with Medusa. What it states about itself is one TypeScript stack with an introspectable GraphQL schema, a GPLv3 core, and a plugin license exception covering your own plugins.
vendure alternative
The options beyond the open-source core that it names are commercial: Vendure Cloud, the managed runtime, and four paid plans (Starter, Growth, Scale and Enterprise) that add B2B features such as contract pricing, approvals and single sign-on.
Official sources
Where this project is recommended
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/vendurehq-vendure)Star history chart for your README
[](https://hysenlabs.com/projects/vendurehq-vendure)Was this useful?