Verus releases on date and commit hash tags, one of which is a rolling channel
Verified Rust for low-level systems code. Rather than adding run-time checks, Verus instead relies on powerful solvers to prove the code is correct.
At a glance
- What is it?
- A verifier for Rust that proves code correct for every possible execution using solvers rather than run-time checks, supporting a subset of the language while reaching past its type system for raw pointers. Its readme warns that features may be broken and the documentation is incomplete, its examples are proofs about bitvectors, locks and broadcast rather than applications, and it ships a best-practices guide for publishing verified code to a public registry.
- Who is it for?
- This suits someone working on low-level or concurrent Rust who wants proofs about invariants rather than tests about examples, and who is prepared to use a tool that covers only part of the language. It does not suit a team that needs the whole language covered today, or anyone who needs a stable release cadence, because the tags carry dates and commit hashes rather than semantic versions.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
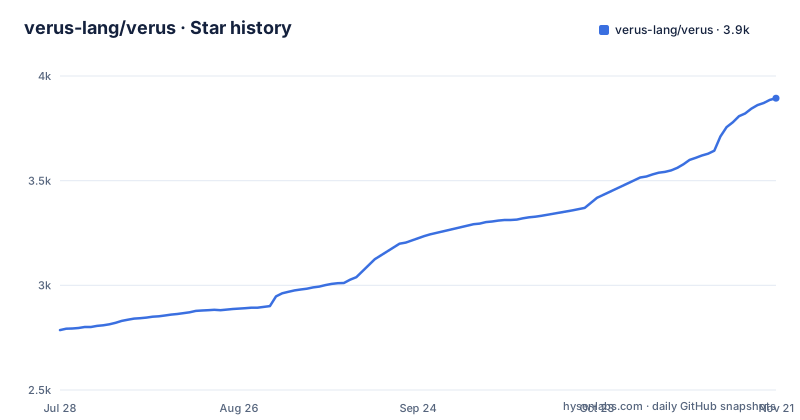
- verus-lang/verus3,894 ★ · +1,108
| Repository | 2026-07-28 | 2026-11-21 |
|---|---|---|
| verus-lang/verus | 2.8k | 3.9k |
1,108 Stars in the last 116 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Release tags are dates plus commit hashes, and one channel is rolling
The three most recent releases have version strings that look nothing like semantic versions, and they encode something useful.
Each one is a date, then a dot, then the first seven characters of a commit hash. One of the three has an extra path segment in its name, and that one is labelled a rolling release while the other two are not.
So there are at least two channels. The dated tags record a specific commit on a specific day, which makes it possible to say exactly what you verified against. The rolling tag moves, which is what a development channel is for.
This is a sensible scheme for a tool that sits between a compiler and a solver, where the exact solver version and the exact compiler version change what can be proved. A commit hash is a more honest version number than a semantic one for that situation.
It is also harder to depend on. There is nothing to say in a manifest that means today, because today is a different commit tomorrow, and the newest dated tag still encodes a build rather than a promise about behaviour.
For anyone evaluating the project, the practical point is that pinning means pinning a commit, not pinning a version.
It verifies a subset of Rust, and reaches past the type system
The central claim is in the first paragraph, and it is a strong one: you write specifications of what your code should do, and the tool statically checks that the executable code will satisfy them for all possible executions.
Two qualifications sit immediately after it, and they point in opposite directions.
The first is coverage. The tool currently supports a subset of the language, and the readme says the authors are working to expand it. There is no claim of completeness, so anything you write outside the subset is simply not checked.
The second is reach. In some cases it lets you go beyond the standard type system, and the example given is checking code that manipulates raw pointers, which the borrow checker will not accept in the first place.
So the honest description is not a drop-in replacement for the compiler. It is a verifier for the part of the language where verification is tractable, which happens to include code the type system refuses.
That combination is why the example set is the way it is, and it is also what tells you where the tool earns its keep.
The readme says features may be broken and the documentation is incomplete
The status section is four sentences and three of them are warnings.
It says the project is under active development. It says features may be broken or missing. It says the documentation is still incomplete. And it says that if you want to try the tool you should be prepared to ask for help in the project's chat.
That last sentence is doing real work. It is telling a prospective user that the first experience is expected to need hand-holding, and it is pointing at a specific chat rather than an issue tracker for it.
The distinction the project draws about where to ask which question is the other useful thing in that section. Feature requests and open conversations about upcoming work go to the discussions area. The issue tracker is reserved for actionable problems with existing features, bugs in things that already work. And it adds that either can be moved later if the maintainers disagree.
So the two channels are separated by what kind of thing you have, not by what you feel like, and the project will reclassify if it disagrees.
The readme also asks anyone using the tool to add their project to a publications page, which is how the adoption list is built.
The examples are proofs about bitvectors, locks and broadcast
The examples directory is the clearest statement of what this tool is for, because the names describe the shape of the problems.
There are three separate bitvector examples covering basics, an equivalence between two formulations, and a garbage collection pass. There is a hash table example in its own subdirectory. There are two atomics examples and two lock examples, numbered one and two. There is an atomic increment. There is a broadcast proof, which is a concurrency result. There are two doubly linked list examples, one of them proving a variant.
Two naming patterns repeat. Several come in pairs with a suffix meaning equivalence, and one linked list example is paired with a variant marked as such, which is the signature of a differential proof: two implementations, one property, shown to agree.
So the example set is about invariants of low-level and concurrent data structures, not about application code. That is deliberate and it matches what the tool claims to reach past the type system for.
There is also an example whose name is a failure, sitting in the same directory, and there are unit tests for the verifier itself that double as syntax examples. Both are what a verifier's repository should contain and few ordinary libraries have.
Publishing verified crates has its own best-practices document
One entry in the documentation list is more unusual than the rest, and it is worth reading as a signal about how far the project reaches.
Among the tutorial, the API reference, the guide for verifying concurrent code, the contributing guide, the licence and the logo page, there is a document of best practices for publishing code verified with this tool to a public package registry.
That is infrastructure beyond verification. It implies a workflow where proofs travel with the crate, where a downstream user can get a verified dependency from a registry, and where somebody has to write down how to do that correctly.
It also implies a constraint that shapes the tool. If code is to be published as verified, the subset it is written in has to be small enough that a consumer can build it, and the specifications have to be stable enough to mean something outside the repository they were written in.
That is a plausible explanation for why the supported subset is a subset, and for why the documentation describes the type of code being checked rather than promising the whole language.
The other research-flavoured entry points follow the same pattern: a publications and projects page, and a day-long tutorial held at a systems security conference whose slides and exercises are published.
The logo is CC-BY while the code is MIT
The licensing section of this readme is more careful than most, and it covers three different things.
The project itself is MIT, and the licence is linked as a documentation entry in its own right rather than being a line at the bottom.
The logo is different. It is credited to a named designer for the design contribution, the bitmap and vector logos are attributed to the project's contributors as a group, and they are licensed under a Creative Commons Attribution licence, version four, which is not the same terms as the code beside them.
Then there is a sponsorship note. A chat application the community uses provides free hosting for the project, and the readme explains what that application is in a sentence.
The logo split is the detail most likely to surprise someone reusing the assets, and getting it right is what the attribution paragraph is for.
The sponsorship note is also worth noticing for a different reason: for a formally verified systems tool, the project's chat is infrastructure someone else is paying for, and the readme says so on the front page rather than leaving it to a sponsorship page.
A blame-ignore file and an editor config sit at the root
The repository root is short, and two of its entries are statements about how the project is worked on.
The first is a blame-ignore configuration, the file that tells the version control system to exclude specific revisions from blame output. Its presence means somebody ran a change across the codebase, most likely a formatting pass, that would otherwise make every line look freshly touched. The project decided to hide that from anyone reading history.
The second is a configuration directory for a specific editor, alongside a configuration directory for a different one. Committing editor configuration is unusual, and it usually means the project wants its formatting to be the same regardless of what you use.
The rest of the root is three separate documents at the top level, one for building, one for installing and one for contributing, plus a file pinning the Rust toolchain, a dependencies directory, a source directory, a tools directory and the examples.
Pinning the toolchain at the root matters for this project specifically. Verifier behaviour depends on which compiler and which solver version you have, so a checked-in toolchain file is not a convenience here, it is part of making a proof reproducible.
Editorial conclusion
This suits someone working on low-level or concurrent Rust who wants proofs about invariants rather than tests about examples, and who is prepared to use a tool that covers only part of the language. It does not suit a team that needs the whole language covered today, or anyone who needs a stable release cadence, because the tags carry dates and commit hashes rather than semantic versions. Before you start, check three things: which of your files fall inside the supported subset, since code outside it is simply not checked; what happens at the boundary, because the readme does not claim completeness; and where your proofs live, since the project asks you to add your project to a publications page and there is a separate document on shipping verified code to a package registry.
Frequently asked questions
What is Verus in verus-lang/verus?
A tool for verifying the correctness of code written in Rust. You write specifications of what the code should do, and it statically checks that the executable code will satisfy those specifications for all possible executions, relying on solvers rather than adding run-time checks. It is MIT licensed, released under date and commit hash tags, and its readme says it is under active development with possibly incomplete documentation.
Does Verus support all of Rust?
No. It currently supports a subset of the language, which the project says it is working to expand, and it makes no claim of completeness, so code outside the subset is simply not checked. In the other direction it can go beyond the standard type system in some cases, and the example the readme gives is statically checking code that manipulates raw pointers, which the borrow checker rejects.
How do I try Verus?
Three routes. There is a browser playground for a quick look without installing anything. For real development the readme points at a separate installation document in the repository. And there is a documentation site with a tutorial and reference, API documentation for its standard library, and a guide for verifying concurrent code. An auto-formatter for the tool's own code lives in its own repository.
Can verified Rust code be published as a crate?
The project publishes a document of best practices for exactly that, covering how to publish code verified with the tool to a public package registry. It also maintains a publications and projects page listing academic papers and industry and academic projects using the tool, and asks anyone using it to add their own project there.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/verus-lang-verus)Star history chart for your README
[](https://hysenlabs.com/projects/verus-lang-verus)Was this useful?