The 1c_mcp proxy exists because 1C cannot speak OAuth2 or stdio
Инструмент для создания MCP-серверов в 1С:Предприятие путем разработки расширения конфигурации. Позволяет интегрировать данные и функциональность 1С с AI-ассистентами (Claude, Cursor и т.д.). Включает Python-прокси и пример расширения 1С с готовыми инструментами.
At a glance
- What is it?
- 1c_mcp builds Model Context Protocol servers on the 1C:Enterprise platform by way of a configuration extension, with an optional Python proxy in front. The proxy is the recommended path because it fixes the two things the direct path cannot do, and the same repository documents a URL case mismatch that silently turns POST requests into GET.
- Who is it for?
- The architecture is the story here: the protocol work lives in the ERP platform, and everything the platform cannot do lives in a thin proxy, which is why the recommended path is not the direct one. If you are deploying this, take the proxy.
- Can I use it commercially?
- Not without permission. GitHub finds no licence file in the repository, and without a licence all rights are reserved by default: you may read the code but not reuse it. Check the README, or ask the authors, before using it.
- Is it still maintained?
- Yes. The repository last received commits 12 days ago.
- What is it written in?
- Mainly 1C Enterprise, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
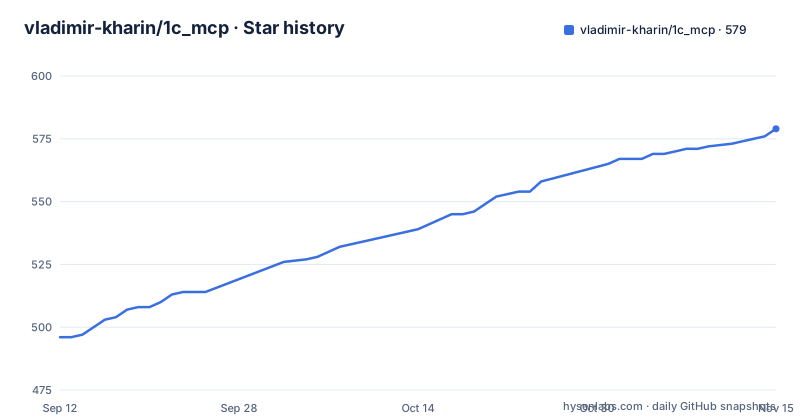
- vladimir-kharin/1c_mcp579 ★ · +83
| Repository | 2026-09-12 | 2026-11-15 |
|---|---|---|
| vladimir-kharin/1c_mcp | 496 | 579 |
83 Stars in the last 64 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The direct path is unsafe by design
There are three documented ways to connect an assistant to a 1C database, and the first one carries a warning before it carries an explanation. Connecting the AI client straight to the 1C HTTP service requires publishing the base with authentication turned off, with the access credentials embedded in the publication descriptor file, and the documentation calls that insecure before it goes on. The stated fix is not a better 1C configuration; it is a different architecture. The direct path also cannot serve clients that require the standard transport, because 1C publishes HTTP services and nothing speaks that transport natively, and it has limited compatibility with some HTTP clients because of protocol nuances. So the direct variant is presented as a way to see it work, and both of its limitations are exactly the two problems the proxy is built to solve.
The proxy is two fixes and a privilege decision
The recommended path puts a Python service between the client and 1C. It solves the transport problem by speaking the standard transport to the client, and it solves the authentication problem by implementing the OAuth2 flow that MCP standardises on and then forwarding the authorization to 1C as basic authentication. That is the part worth understanding: because 1C never sees the OAuth2 exchange, the web-published base can keep its own authentication switched on, which is exactly what the direct path could not offer. The proxy supports two modes, acting as one fixed service user, or passing each user's own credentials through to 1C under their own login. The second is the one to be careful with, because it means 1C enforces real per-user rights; the first means every assistant session shares whatever rights that one account has. The release history suggests this area has been the source of bugs, since two of the three recent version notes are about OAuth2 fixes and one is specifically about role rights.
A URL case mismatch turns POST into GET
One warning in the quick start is the most practically useful line in the documentation, and it is the kind of failure that costs an afternoon. The database name segment in the published URL has to match the publication name's letter case exactly, so a base published as a lowercase name must be requested in lowercase and not in title case. When the cases disagree, the web server issues a redirect, and a redirect following a POST is issued as a GET, which means the MCP request arrives at the database with the wrong method and the call fails in a way that looks like a protocol bug rather than a configuration typo. The path itself is otherwise unremarkable: publish the HTTP service that the extension provides, then point the client at the service URL under the base and service segments, with ready-made client configurations supplied in the repository for the common assistants.
The version that shipped two transports documents neither
The release notes are unusually descriptive, which makes the gap between them and the documentation easy to see. Version one-six is titled as MCP without a web server, offering file and reverse HTTP transports. Version one-five is about OAuth2 fixes and a redirect URI filter. Version one-six-one is about OAuth2 authorization and role rights fixes. The quick start and the three connection variants describe only the direct HTTP service, the Python proxy, and the proxy in a container. None of them mentions a file transport or a reverse HTTP transport, so the headline capability of the most recent major version is undocumented in the page you are most likely to read. The variable naming suggests one of them is configured through the proxy's own environment settings, and the proxy readme is the documented place for that detail, but as published the two documents disagree about what the software can do.
Tool containers are found by substring match
There are two ways to add your own tools, and the second one is worth reading carefully. The first is to create a new processing inside the shipped extension and register it in the tool containers subsystem, implementing two exported methods in that processing's manager module. The second is to build your own separate extension: copy the server subsystem into it and add your own extension's prefix to the subsystem's name, for example by prefixing it, and the engine will find it. The discovery rule is stated as the engine looking for subsystems whose name contains a specific marker string and connecting them the same way as its own. That is a loose contract. It means a subsystem is loaded as an MCP server container because of what its name happens to contain, so naming discipline inside a configuration becomes a security boundary, and anyone who can add an extension to the base can add tools that the engine will register.
Two exported methods with Cyrillic identifiers are the extension point
The entire contract for a custom tool is two procedures in one module, shown in the documentation as a code block: one that describes the available tools and their parameters, and one that executes the logic when the model calls a tool by name. There is no declarative schema, no registration file and no annotation; the extension point is a pair of method names that the engine looks for. Both are written in Cyrillic identifiers, which is normal for the platform's own code and awkward for a project whose development guide is explicitly meant to be fed to code generators, since a model reasoning about a Russian-language function signature is a different problem from one reasoning about an English one. The platform's data model vocabulary is Russian throughout, and the guide is linked as something to connect to an AI agent, so the convention is deliberate even if it costs something in reach.
The proxy container runs as root and declares its health check twice
The container side is small and mostly standard, with three details worth recording. The image is built from a slim Python base, installs dependencies from a copied requirements file with caching disabled, copies only the proxy source and exposes one port, and starts with a module invocation whose first argument selects the HTTP mode with a bind address and port. There is no user directive, so the proxy runs as root inside the container, which is a default worth changing if you deploy this yourself. The health check is declared twice, once as a HEALTHCHECK instruction in the image and once as a compose service health check, with the same command and the same interval, timeout and retry counts in both places; the command itself shells out to Python and makes an HTTP call, so the HTTP client library it uses has to be a runtime dependency rather than a development one. The compose file parameterises the published port from an environment variable, and the instructions warn that a proxy in a container talking to a database on the same host needs the host gateway address rather than the loopback one.
Editorial conclusion
The architecture is the story here: the protocol work lives in the ERP platform, and everything the platform cannot do lives in a thin proxy, which is why the recommended path is not the direct one. If you are deploying this, take the proxy. It keeps authentication switched on for the database and it serves clients that insist on the standard transport. Two things to check before you rely on the documented path. The release that advertises file and reverse HTTP transports does not have those transports explained anywhere in the documentation, so treat them as unverified until you read the proxy's own readme. And the engine discovers tool containers by substring-matching a subsystem name, which means anything you name similarly gets loaded, so control who can add extensions to the configuration.
Frequently asked questions
What is 1c_mcp?
A tool for building Model Context Protocol servers on the 1C:Enterprise platform by developing a configuration extension. The repository ships a ready extension that handles the protocol routine and provides tools for configuration metadata out of the box, plus an optional Python proxy for infrastructure problems, and the README states the project is MIT licensed.
Do I have to disable authentication on the 1C web server?
Not on the recommended path. The Python proxy implements the OAuth2 flow that MCP standardises on and forwards the authorization to 1C as basic authentication, so the published base keeps its own authentication. Only the direct-connection variant requires publishing without authentication, which the documentation describes as insecure.
How do I add my own tools to 1c_mcp?
Either create a processing inside the shipped extension and register it in the tool containers subsystem, or build a separate extension by copying the server subsystem and prefixing its name, which the engine then discovers. In both cases you implement two exported methods: one describing the tools and their parameters, and one executing the logic the model calls.
Which MCP primitives does 1c_mcp support?
Tools are the core, and the project also supports resources for providing static context such as files, and prompts for predefined message templates. The extension is what implements all three on the 1C side.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/vladimir-kharin-1c-mcp)Star history chart for your README
[](https://hysenlabs.com/projects/vladimir-kharin-1c-mcp)Was this useful?