VpnHood's open source part is the engine, the ads and billing interfaces are the product
Undetectable, Fast, Cross-Platform, Free VPN
At a glance
- What is it?
- A cross platform VPN client and server written in C# and .NET, claiming to be undetectable, with an independent security audit to its credit and a developer feature list that includes three ad networks and a billing interface. The default branch is develop, and the top changelog badge links to main.
- Who is it for?
- VpnHood suits someone who wants to run their own tunnel rather than rent one, or who wants to build a branded client on top of an engine. Five things to check before you install it.
- Can I use it commercially?
- Yes, with conditions. LGPL-2.1 is a weak copyleft licence: you can use it inside commercial and closed-source software, but if you distribute changes to its own files, you must publish those changes under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly C#, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
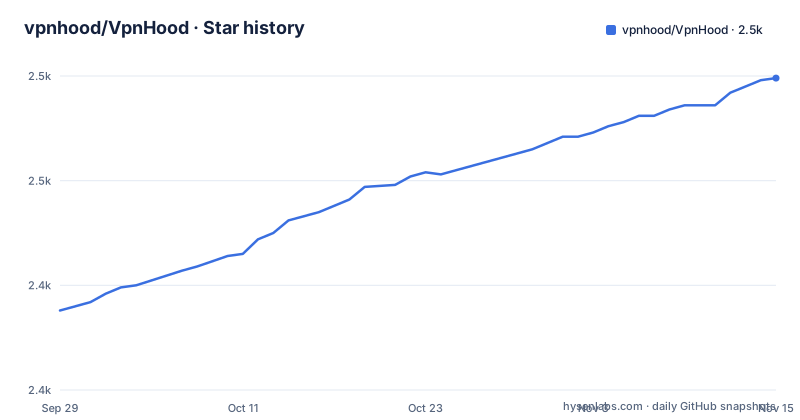
- vpnhood/VpnHood2,499 ★ · +111
| Repository | 2026-09-29 | 2026-11-15 |
|---|---|---|
| vpnhood/VpnHood | 2.4k | 2.5k |
111 Stars in the last 47 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The undetectability claim is asserted and never measured
The repository description is four adjectives and a promise: undetectable, fast, cross-platform, free. The readme opens with a sentence about being an alternative for circumvention and privacy, and then states the mechanism as a solution to bypass advanced firewalls and circumvent deep packet inspection, written from scratch in C#.
There is no evidence for the first word anywhere on the page. No packet capture, no test against a named firewall, no measurement, and no definition of what undetectable means here: whether a protocol analysis flags the tunnel, whether a blocklist catches it, or whether a specific appliance does.
The project does something better than ignoring the question, which is to link to it. Among its documents is a page titled with the question of whether a network provider can block it. That is the opposite of a marketing claim, and it is worth more than the adjective, because it tells you the authors consider blocking the expected outcome rather than a failure.
The same word appears once more in the client feature list, in a narrower form, as being undetectable on private addresses. That is a specific and much more modest claim than the one in the description, and it is the version worth believing, because a listener on a private network seeing a tunnel is a different problem from a national firewall seeing one.
The protocol list is where a reader can form their own view: user datagram, transmission control, QUIC, a mode named Cloaked, and a combination mode. Nobody on the page says which of those a given firewall sees as what.
An external audit is the strongest trust line on the page
There is one short section about a security audit, and it is the most load bearing paragraph in the readme.
It says the software underwent a comprehensive security audit by the Open Tech Fund, and it links to the full report published by that fund. That is a named third party, a named report and a public link, which is the standard of evidence a privacy project either meets or does not.
It is worth being precise about what an audit of this kind does and does not give you. It is a point in time assessment of a codebase, usually covering the client, the server and the update path, with findings and responses. It tells you that named people read the code and disagreed with the author in writing. It does not tell you the current build was audited, because software moves, and it does not tell you what the audit concluded about the proxy list behaviour or the ad interfaces, since those are operational features rather than cryptography.
So the right way to use the link is as a starting point for your own review rather than as a substitute for one. The two questions an auditor would not have answered for you are whether the relays your traffic passes through are trustworthy, and what the client does with the list of them. Both are described elsewhere on the page and both are operator decisions.
Given that the alternative to an audit is a claim in a repository description, the presence of a published third party report is a genuine differentiator for this project.
The relay list comes from a URL and rotates
One client feature is worth reading twice, because it changes the privacy picture more than anything else on the page.
It describes smart proxies: SOCKS4, SOCKS5, and HTTP and HTTPS relays, tested in parallel, rated, rotated, and automatically updated from a list URL.
Four properties there deserve separate attention. The list is fetched from a URL, which means the set of exit points is controlled by whoever controls that URL rather than by the person running the client. They are tested in parallel, which means several candidates are probed and the working one chosen, so a relay can change without the client being reinstalled. They are rated, so there is some notion of quality, and it is applied automatically. And they rotate.
Combined, that is a client whose egress is remote-controlled and changes over time. For a user whose reason for running a tunnel is to control who sees their traffic, that is a different guarantee from a tunnel that connects to a server they chose. It is also, to be fair, the design that makes the client free and small: the operator does not have to provision relays.
The rest of the client feature list is conventional and well chosen. One click connect, split tunnelling by application and by country, custom DNS, dual stack addressing, five protocols including the cloaked mode and a combination mode, and support for screen readers, which is rare enough in this category to be worth noting.
Ad interfaces, billing interfaces and a guide to publishing your own app
The developer feature list is where the business model becomes visible, and it deserves to be read rather than skimmed.
It lists an ads interface with three advertising networks integrated by name, a billing interface, a document on publishing your own app, distribution as modular packages on a package registry, an extendable user management layer with a REST interface, cross platform support for the mobile toolchain, a component based architecture described as highly customizable, and a simple build experience in a particular IDE.
Put those together and the picture is a white label product. The engine is open source and permissive enough to fork; the commercial layer is the brand, the ad integrations, the billing and the management console. The document on publishing your own app is the manual for that.
That is a legitimate and common shape for a free client backed by monetisation, and the licence is consistent with it, since it lets you redistribute a modified version. But it means the word free in the repository description describes the client, not the economics, and a reader who installs it is installing a build that is configured to show somebody else's advertising unless the operator changed that.
The server feature list reads more like something an operator would want: zero network configuration, no administrator privilege required, hot restart with sessions surviving it, built in user management, a feature named for protecting the server from network scanning, and compatibility with reserved proxies.
The privacy claim and the ad interfaces are not in conflict, but they describe two different products wearing one name, and a user is better served by knowing which one they have.
The default branch is develop and one changelog link points at main
A small inconsistency in the links is worth knowing about if you are following this project.
The default branch is develop. The changelog badge near the top of the readme links to the changelog file on the main branch. The changelog entry in the documents list, further down the same page, links to the changelog file on the develop branch. So one page points at two branches for the same document, and the branch that is not the default is the one in the badge.
That suggests a repository that was developed on one branch and moved, with a badge that was not updated, or a project where both branches are live and the distinction is not documented here.
There is a second change log in the tree as well, named for the server, so the client and the server are tracked separately. That is a reasonable arrangement for a project with two distinct deployment targets, and it is also one more place to look when you want to know whether a fix landed.
The release sequence has a shape worth noting. Three releases in a month, all in the same minor line, with the build counter climbing: 838, then 841, then a prerelease at 850. The prerelease carries the highest number, which is correct chronologically and slightly awkward for any tool that sorts versions and assumes a prerelease is behind the latest stable.
The last push is dated 29 September 2026 and the newest release is from 2 September, so the branch is ahead of the newest tag by about a month.
A committed build cache, two solution files and one text file of samples
The tree is a large one for a project whose readme is 339 words, and a few entries are worth naming.
There is a directory whose name is a frontend build tool's cache directory, sitting at the repository root rather than in an ignore list. That is a build artefact in version control, and it will conflict on every build for anyone who clones it.
There are two solution files: one in the newer solution format and one settings file for it. Alongside them are a shared build properties file and a shared build targets file, which is the standard way to keep compilation settings consistent across many projects in a repository, and a pinned SDK version file so every contributor builds against the same toolchain. There is also a submodules file, so parts of the build come from other repositories at pinned revisions.
The release tooling for the mobile client is at the root as well, which is unusual for a C# repository and tells you the iOS build is part of this tree rather than a separate one.
And then the samples. The examples listing for this repository contains exactly one file, a text file. So there is no runnable example in the tree, no sample configuration and no documented compose or command line invocation, and the two installer links on the page go to a prebuilt package and a wiki page rather than to anything a developer can read.
That is the honest gap in a project with this many features listed. To evaluate it you read the wiki; the repository gives you the source and the design, not the instructions.
Editorial conclusion
VpnHood suits someone who wants to run their own tunnel rather than rent one, or who wants to build a branded client on top of an engine. Five things to check before you install it. What the proxy rotation actually does, because the client fetches a list of relays from a URL and rotates through them, which means traffic can leave through third party infrastructure the operator does not control. What the undetectability claim rests on, since the page asserts it and links to its own document asking whether a provider can still block it. Where the money comes from, because a free client ships interfaces for three ad networks and a billing system, plus a document on publishing your own app. Which licence terms you are under, since LGPL covers the engine while the client is a mobile app on two stores. And which branch you are reading, because the default is develop and one of the two changelog links points at main.
Frequently asked questions
how to use vpnhood
The page links prebuilt clients rather than documenting a setup: a Windows installer package, a wiki page for installing the client on Linux, mobile apps on both app stores, and a wiki page for the general client install with alternative download links. The repository itself contains no runnable example and the samples listing holds a single text file, so the wiki is where the instructions are.
is vpnhood safe
The page states the software underwent a comprehensive security audit by the Open Tech Fund and links to the published report. It also describes client proxies that are tested in parallel, rated, rotated and updated automatically from a list URL, which means the set of relays your traffic can leave through is controlled by that URL rather than by you. Whether that trade is acceptable is the question the audit will not answer for you.
How do I get a server key for VpnHood?
The repository does not document key issuance. What the page does describe is the server side: built in user management, zero network configuration, no administrator privilege required, hot restart with sessions persisting, a feature for protecting the server from network scanning, and compatibility with reserved proxies. Setup details are routed to the project's wiki.
Is VpnHood really free?
The client is free and the engine is open source under the LGPL, which also allows redistribution of a modified version. The developer feature list includes an interface integrating three advertising networks and a billing interface, plus a document on publishing your own app, so the free client is configured to show an operator's advertising unless the operator changed that.
Which platforms does VpnHood support?
Clients for Windows on 10 and 11 at x64, Android on phones and TV, iOS on iPhone and iPad, and Linux. Servers run on Windows 10, 11 and Server, and on Linux. The project also supports split tunnelling by application and by country, custom DNS, both address families, and screen readers.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/vpnhood-vpnhood)Star history chart for your README
[](https://hysenlabs.com/projects/vpnhood-vpnhood)Was this useful?