Wangnov/Codex-App-Manager: a Tauri client that installs, delta-updates and cleanly uninstalls the Codex desktop app
Cross-platform installer & updater for the official Codex desktop app — incremental updates, clean uninstall, China-reachable self-update.
At a glance
- What is it?
- Codex App Manager does one job: it detects, plans and performs install, incremental update and clean uninstall of the official Codex desktop app, fetching payloads through a Cloudflare Worker that routes by country. macOS builds are signed and notarized; the Windows installers are not, and the README says so.
- Who is it for?
- Codex App Manager fits a Windows or macOS user who wants the official Codex desktop app installed, incrementally updated and cleanly uninstalled from one place, and who can reach a Cloudflare Worker that picks R2 or IHEP S3 by country. It is a poor fit if you need a signed Windows installer today, because there is none and the project states that plainly, or if your plan involves modifying the Codex installer itself, which is an explicit boundary.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
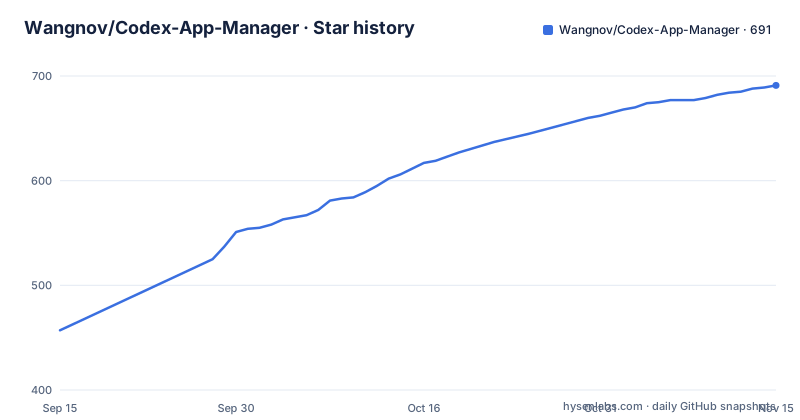
- Wangnov/Codex-App-Manager691 ★ · +234
| Repository | 2026-09-15 | 2026-11-15 |
|---|---|---|
| Wangnov/Codex-App-Manager | 457 | 691 |
234 Stars in the last 61 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
It installs Codex, never builds or patches it
Codex App Manager is a desktop client for the official OpenAI Codex desktop app. It detects an existing install on the machine, plans and performs install, incremental update and clean uninstall, and launches the app in one click. What it does not do is stated as firmly as what it does. It does not build or modify Codex, and the boundaries section rules out modifying or repackaging the Codex installer, bypassing OpenAI or Microsoft authorization or local install policy, and forging or recomputing Sparkle signatures.
The split with the upstream project is the key to reading this repository. codex-app-mirror distributes the official Codex installers unmodified and verifiably, and provides a China-reachable Sparkle incremental update source. Codex App Manager is the downstream client that turns those capabilities into a local install and update experience. Mirror upstream, client downstream, and neither rebuilds the payload.
Once the Manager is installed you do not download Codex separately. The Manager installs and updates the Codex app itself.
Detect, plan, confirm, then touch the disk
The operating model has three steps: detect, plan, execute. On launch the app probes the machine for the Codex install state and for what the platform is capable of, generates an install, update or uninstall plan, and asks for confirmation before running anything destructive.
The verification step is the part that matters during an update. Version and signature checks happen before the update is applied, and the stated reason is to avoid TOCTOU, the window in which what you verified is no longer what you install. Reading the plan before confirming is therefore not ceremony, since it is the only point at which a mismatch is visible.
The shell around that flow is Tauri v2 in a frameless popup window, with React 19, TypeScript, Vite and GSAP in the front end and a Rust command layer with application service, port and platform adapters behind it. The same tree builds locally in four commands:
npm install
npm run tauri:dev
npm run check
npm run tauri:build
The last one produces an unsigned local build. Linting is defined as eslint with max-warnings set to zero, and tests run through vitest.
macOS takes Sparkle deltas and rolls back on failure
On macOS the Manager reads the Sparkle appcast from the mirror, per architecture, arm64 or x64, and compares what the appcast offers against the version installed locally in order to plan the update. Where a delta package exists between the two versions it is preferred over the full download, the Sparkle signature is verified byte for byte using EdDSA, and the replacement happens in place. If it fails, the Manager rolls back.
When no matching delta exists for the jump you are making, it falls back to the complete package, so a wide version gap costs bandwidth but does not fail outright.
That path lives in its own crate, codex-mac-engine, kept separate from the Windows engine so two different update systems do not have to share one code path. macOS builds are Developer ID signed and Apple notarized, so a first launch is not stopped by Gatekeeper.
Windows stages MSIX or portable, then health checks the result
The Windows engine works differently. It fetches MSIX or the portable build from the mirror, stages the update, and supports a custom install directory. After installation it runs a health check, and on systems that have been trimmed it gives a hint rather than leaving a silent failure behind.
The crate split is the clearest statement of how far apart the two platforms are: codex-win-engine handles MSIX and portable, codex-mac-engine handles Sparkle, and neither tries to abstract the other away.
The download table spans four targets. CodexAppManager_aarch64.dmg serves Apple Silicon Macs and CodexAppManager_x86_64.dmg serves Intel Macs, while CodexAppManager_x64-setup.exe covers Windows x64 and CodexAppManager_arm64-setup.exe covers Windows ARM64. Each has a mirror direct link under a latest path that resolves to the current release without being edited per version.
One short link, two backends, routed by country
Self-update and payload downloads share a single short host, codexapp.agentsmirror.com, and a Cloudflare Worker in front of it does the routing. Outside China the file is served directly from R2. Inside mainland China the Worker reads CF-IPCountry and returns a presigned address pointing at IHEP S3. Same link, different node, and the switch is invisible to the user.
The Manager's own base URL is not buried in the application logic. It comes from VITE_MIRROR_BASE_URL, and the .env.example file in the repository sets that variable to the same host, so the routing decision lives in the Worker and in the release pipeline rather than in the client.
For the Manager's own binaries the path is /manager/latest/, which always resolves to whatever is currently published. That is what lets the four direct download links stay fixed across versions while the payload behind them changes.
The signature in latest.json covers bytes, not URLs
The Manager embeds a Tauri updater and checks two sources in order. First its own latest.json at codexapp.agentsmirror.com/manager/latest.json, served from R2 globally and split to IHEP S3 inside mainland China. Second, GitHub as a fallback, at the releases/latest/download/latest.json path.
The detail that makes the first source safe is that the signature in latest.json signs the installer bytes rather than the URL. The mirror only copies files byte for byte and rewrites the download address, so the signature stays valid wherever the file lands. The cache layout follows from that. Installers sit under a versioned path of the form /manager/version/ where long caching is safe, while latest.json sits at a fixed root path with short caching.
Every formal release has CI sync the artifacts and the rewritten latest.json to both mirrors, which is why self-update does not depend on GitHub reaching the client at all. Tagging v* triggers release.yml, which builds four platforms with retries on transient download failures, signs and notarizes the macOS app inside out, repackages the updater, signs the Windows updater artifact, publishes the GitHub Release, and finally syncs to R2 and IHEP. The version numbers line up at the moment: the newest tag is v0.5.11 from 2 October 2026, v0.5.10 and v0.5.9 both from 23 September, and package.json already reads 0.5.11.
The Windows installer carries no Authenticode signature
macOS builds are Developer ID signed and notarized, so Gatekeeper leaves them alone. Windows is the opposite, and the README says so rather than glossing over it: CodexAppManager_x64-setup.exe and CodexAppManager_arm64-setup.exe currently have no Authenticode code signature, so SmartScreen may prompt on first run. The Tauri updater signature used for self-update only verifies the downloaded bytes and does not represent Windows publisher trust.
The policy has also moved. A SignPath Foundation application is no longer being pursued, the project has switched to planning a paid cloud HSM certificate scheme, and until such a certificate is actually configured and verified the current downloads must not be described as signed. Both docs/code-signing-policy.md and docs/windows-signing.md hold the detail.
What you can verify today is a checksum. Each release ships SHA256SUMS, and on macOS you compare against it:
shasum -a 256 CodexAppManager_aarch64.dmgHomebrew is the recommended route on macOS instead:
brew install --cask wangnov/tap/codex-app-managerSkins are injected over CDP and leave Codex signed
The Manager also ships the runtime for awesome-codex-skins, a separate repository holding the .codexskin standard, its toolchain and a gallery. The theme page reads an online library at skins.agentsmirror.com/index.json and installs a skin in one click, verifying a sha256 after the download.
Three modes are offered, and the real distinction is persistence. Try-on hot-switches the running Codex within seconds, writes nothing to disk and can be reverted at any moment. Apply persists, and carries Codex's own accent and font configuration. Restore returns the native look in one click. A .codexskin file can be imported through a file picker or dragged onto the theme page.
The constraint that matters is how a skin is applied. Skins are injected over CDP, no application file is modified, and the signature stays intact, which is why a skin cannot invalidate Codex's own signing. Each preview in the gallery is a real-machine screenshot taken under a quality gate rather than a mockup.
Editorial conclusion
Codex App Manager fits a Windows or macOS user who wants the official Codex desktop app installed, incrementally updated and cleanly uninstalled from one place, and who can reach a Cloudflare Worker that picks R2 or IHEP S3 by country. It is a poor fit if you need a signed Windows installer today, because there is none and the project states that plainly, or if your plan involves modifying the Codex installer itself, which is an explicit boundary. Before you install, check four things: that SmartScreen will not stop you on Windows, whether verifying SHA256SUMS suits you better than a signature, what the plan and confirm step means for an update already in flight, and whether the v0.5.x cadence suits a tool you depend on daily.
Frequently asked questions
How does Codex App Manager remove the Codex desktop app?
Clean uninstall is one of the three operations it plans. The app detects the Codex install state and platform capabilities, generates an install, update or uninstall plan, and asks for confirmation before running the destructive part.
Is the Codex App Manager installer for Windows code signed?
No. The Windows x64 and ARM64 setup executables currently have no Authenticode code signature, so SmartScreen may prompt on first run. The Tauri updater signature only verifies downloaded bytes and is not Windows publisher trust. A SignPath Foundation application is no longer being pursued and a paid cloud HSM scheme is only being planned, so the current downloads must not be described as signed.
How does Codex App Manager update itself when GitHub is unreachable?
The Tauri updater checks its own latest.json at codexapp.agentsmirror.com first, served from R2 globally and split to IHEP S3 inside mainland China, with GitHub only as a fallback. CI syncs artifacts and the rewritten latest.json to both mirrors on every release, so the update path does not need GitHub.
After installing Codex App Manager, do I still download Codex myself?
No. The Manager installs and updates the Codex desktop app itself, taking macOS updates from the mirror's Sparkle appcast as deltas with rollback, and Windows updates by staging MSIX or portable builds with a custom install directory and a post-install health check.
Do Codex App Manager skins modify the Codex application files?
No. Skins are injected over CDP, so no application file is modified and the signature stays intact. Try-on changes the running app without writing to disk, apply persists along with Codex's own accent and font settings, and restore returns the native look.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/wangnov-codex-app-manager)Star history chart for your README
[](https://hysenlabs.com/projects/wangnov-codex-app-manager)Was this useful?