libwebsockets lets the TLS backend decide whether QUIC is possible
canonical libwebsockets.org networking library
At a glance
- What is it?
- libwebsockets is a pure C networking library covering http/1 through http/3, websockets, webtransport, and MQTT, and where you land depends on a TLS capability matrix that rules OpenSSL out of QUIC. Its pre-5.1 releases are called effectively deprecated, and the repository publishes no releases at all.
- Who is it for?
- libwebsockets suits C programs that want HTTP and WebSocket handling from one dependency and can commit to a TLS backend chosen for the protocol they actually need: GnuTLS or BoringSSL for QUIC and HTTP/3, OpenSSL or mbedTLS for JIT trust, BearSSL only when neither QUIC nor DTLS is wanted. It does not suit a project that must stay on OpenSSL and still wants HTTP/3, or a team that upgrades by patch release, since pre-5.1 releases do not carry many of the security fixes.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly C, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
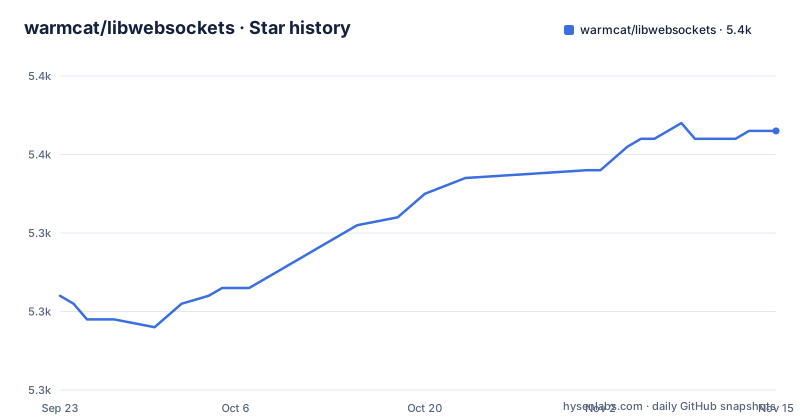
- warmcat/libwebsockets5,353 ★ · +21
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| warmcat/libwebsockets | 5.3k | 5.4k |
21 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
One C library, many protocol families, and a TLS backend you choose
libwebsockets is a pure C library with an MIT license that provides both client and server sides for http/1, http/2, http/3, websockets, webtransport, MQTT, and other protocols. It also carries lightweight ancillary implementations for JSON, CBOR, JOSE, and COSE, and it supports OpenSSL and MbedTLS v2, v3, and v4 out of the box. The stated range runs from embedded RTOS up to mass cloud serving. The combination table near the top of the README is the first thing to read, because the default TLS backend changes with the platform:
|LWS version|Platform|Protocols|Default TLS|
|---|---|---|---|
|<= 4.5|non-FreeRTOS|any|OpenSSL|
|<= 4.5|FreeRTOS|any|mbedTLS|
|5.0+|Windows|any|schannel|
|5.0+|*nix|h1, h2|OpenSSL|
|5.0+|*nix|quic/h3|GnuTLS|
|5.0+|FreeRTOS|any|mbedTLS|
Read the last three rows together. On v5.0 and later the same Linux build defaults to OpenSSL for h1 and h2 and to GnuTLS for quic and h3, which is the first hint that the backend is not one global setting in the way newcomers tend to assume.
quic/h3 is enabled by default and OpenSSL cannot carry it
QUIC and HTTP/3 in this library need a TLS stack that exposes the QUIC TLS API. Upstream OpenSSL does not provide SSL_set_quic_method, so it cannot act as the cryptographic engine for the QUIC transport, and the README directs anyone who needs QUIC or HTTP3 to BoringSSL or GnuTLS instead. openHiTLS has the same gap and simply does not provide the necessary QUIC TLS API. mbedTLS can do it, but only via a patch. Because quic/h3 is enabled for build by default, that requirement is why GnuTLS rather than OpenSSL is the default on *nix builds. The consequence is concrete for anyone reading this before choosing a stack: picking OpenSSL for its other properties means carrying a default build that expects a QUIC engine it cannot have, so you either turn that option off and lose HTTP/3, or move the project onto a different TLS library. BearSSL is listed with no QUIC transport at all.
The JIT Trust column rules out the two recommended QUIC backends
Read the capability matrix by column rather than by row and one entry stands out. JIT Trust is marked No for GnuTLS, LibreSSL, AWS-LC, BoringSSL, wolfSSL, and SChannel, and Yes for OpenSSL, mbedTLS, BearSSL, and openHiTLS. That matters because the two libraries recommended for QUIC, GnuTLS and BoringSSL, both lack it. A reader who needs QUIC on Linux is pushed toward a backend without JIT trust, and a reader who needs JIT trust is pushed back toward OpenSSL, which cannot do QUIC. Other columns narrow the field the same way. BearSSL has no QUIC transport and no DTLS, openHiTLS has no QUIC transport, and its DTLS cell reads Yes but not SRTP, which matters because WebRTC mixing is one of the features added in v5.0. There is no single row that satisfies every column, so the matrix is a negotiation rather than a recommendation.
Pre-5.0 branches are deprecated and no releases are published
The README is blunt about versions. v5.1 is available, and the advice is to upgrade to it or preferably to v5.1-stable or main, because many security fixes exist only on v5.1-stable and on main, and pre-5.1 releases are effectively deprecated. A continuous incremental security audit is described as running all the time, finding and fixing new problems. Against that, the repository publishes no releases, so there is no release list to choose a version from. Version information lives in branches instead, with main as the default branch, plus a changelog file, a SECURITY.md, and the READMEs directory at the top of the tree. The last push to main is dated 2026-11-02, so the work is current even though the release history is invisible. For a reader still on 4.x, the consequence is that fixes are reachable only by moving to v5.1-stable or main rather than by taking a patch release.
cmake is the stated build path and five others sit beside it
The library is described as easy to build and cross-build via cmake, and the tree supports that with CMakeLists.txt, CMakeLists-implied-options.txt and a cmake/ directory. Around it sit build paths for other worlds: Makefile.projbuild for the ESP-IDF style project build, component.mk for component based embedded builds, win32port/ for Windows, and Kconfig for kernel style configuration. Also in the tree are include/ and lib/, plugins/ and plugin-standalone/, contrib/, scripts/, and a fuzz/ directory. What the README does not do is hand you a command line. The one build option spelled out is DHT support, which is compiled in like this:
-DLWS_WITH_DHT=1Everything else is left to CMakeLists-implied-options.txt and the READMEs directory, so expect to read those before configuring anything beyond a default build on one platform.
The CC0 minimal-examples tree is the documented way in
The header documentation is one way to learn the API, but the project points at something more practical: more than 100 independent minimal examples, CC0 licensed so they sit in the public domain and are meant for cutting and pasting, covering various scenarios. Two directories hold them, minimal-examples/ for higher level cases and minimal-examples-lowlevel/ for lower level ones, with test-apps/ for the test applications and an lwsws/ directory. Alongside sit a READMEs directory described as a lot of READMEs on a variety of topics, Doxygen API documentation generated from libwebsockets.dox, and a page describing a large amount of CI testing per push. The tree also carries AGENTS.md and .clangd, which tells you the same codebase is expected to be worked on by writing assistants and by clangd aware editors.
Event loop sharing is the widest axis of choice
The library describes itself as gregarious about event loop sharing, and the list of integrations is long: libuv, libevent, libev, sdevent, glib, uloop, and custom event libraries. Any of those can sit underneath the same protocol code, which is unusual for a C networking library. That flexibility is also where the cost lands. Every loop you consider multiplies the configurations you have to build and test, and the README points at its CI page rather than promising that each combination is covered. The v5.0 additions widen the surface: WebRTC mixing, described as being like running your own zoom, HLS serving, and SChannel support that removes the need for an OpenSSL build on Windows, together with GnuTLS, openHiTLS, and BearSSL as new TLS options. Read the loop list as a menu of supported integrations, not as a statement about which pairings have been exercised.
Editorial conclusion
libwebsockets suits C programs that want HTTP and WebSocket handling from one dependency and can commit to a TLS backend chosen for the protocol they actually need: GnuTLS or BoringSSL for QUIC and HTTP/3, OpenSSL or mbedTLS for JIT trust, BearSSL only when neither QUIC nor DTLS is wanted. It does not suit a project that must stay on OpenSSL and still wants HTTP/3, or a team that upgrades by patch release, since pre-5.1 releases do not carry many of the security fixes. Before committing, read the capability matrix for your exact backend and version, and decide which branch you will track, because there are no releases to pin.
Frequently asked questions
how to use libwebsockets
Build it with cmake, then start from the minimal examples: more than 100 independent CC0 licensed examples sit in minimal-examples/ for higher level cases and minimal-examples-lowlevel/ for lower level ones, with READMEs/ and Doxygen API docs alongside them.
how to install libwebsockets
The README gives no package manager command and calls the library easy to build and cross-build via cmake. The tree carries CMakeLists.txt, cmake/, Makefile.projbuild, component.mk, win32port/, and Kconfig for other build systems, and the one documented option is -DLWS_WITH_DHT=1 for DHT support.
libwebsockets alternative
For TLS the listed alternatives are OpenSSL, MbedTLS v2, v3, and v4, GnuTLS, wolfSSL, BoringSSL, LibreSSL, AWS-LC, SChannel, BearSSL, and openHiTLS. For the event loop it supports libuv, libevent, libev, sdevent, glib, uloop, and custom event libraries.
Why use WebSockets instead of HTTP?
libwebsockets covers both sides in one pure C library: client and server for http/1, http/2, http/3, websockets, webtransport, and MQTT, plus lightweight implementations for JSON, CBOR, JOSE, and COSE. A service that speaks HTTP and WebSocket traffic can stay on that single dependency.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/warmcat-libwebsockets)Star history chart for your README
[](https://hysenlabs.com/projects/warmcat-libwebsockets)Was this useful?