Wazuh is three components, and the default branch carries a possible-bugs warning
Wazuh - The Open Source Security Platform. Unified XDR and SIEM protection for endpoints and cloud workloads.
At a glance
- What is it?
- Wazuh is an open-source platform for threat prevention, detection and response, built from an endpoint agent, a management server and a separate indexer for search and visualisation. It scans hosts directly and matches collected logs with a regular expression engine, and the file warns you that the default branch may contain bugs.
- Who is it for?
- Wazuh fits a team with a compliance obligation, most often around payment data, that wants file integrity monitoring, log analysis and vulnerability correlation in one place with an agent it controls. It does not fit a team that wants one binary, because the agent, the server and the indexer are three things with three version lines and the orchestration tooling lives in eight separate repositories.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly C++, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
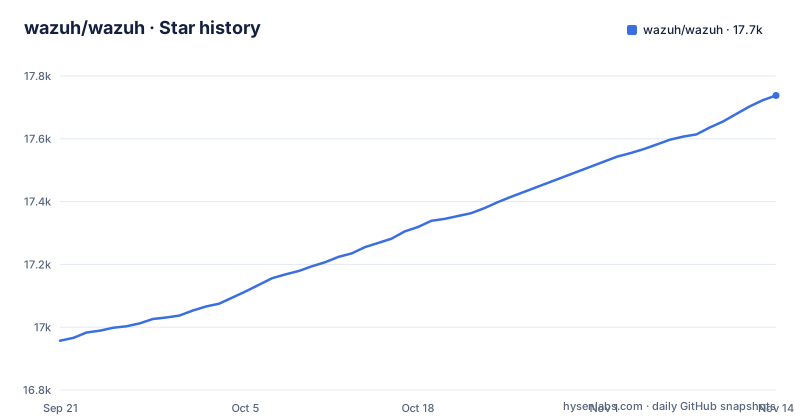
- wazuh/wazuh17,723 ★ · +766
| Repository | 2026-09-21 | 2026-11-13 |
|---|---|---|
| wazuh/wazuh | 17k | 17.7k |
766 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Three moving parts, and the search engine is a separate product
The architecture paragraph is short and load-bearing. A Wazuh deployment is an endpoint security agent on each monitored system, a management server that collects and analyses what the agents gather, and a separate component called the indexer, which the file describes as fully integrated and which provides the search engine and the data visualisation tool for navigating security alerts. So the alerting you search is not something this repository describes itself as implementing, it is something it integrates with. That is the first thing to internalise, because it turns one product into three version lines that have to agree, and because the piece most people picture when they think of a security information and event management tool, the search and the dashboards, is the one that lives elsewhere. The web interface in this project sits on top of that arrangement rather than replacing it.
The file itself warns you off the default branch
There is a branches section, and it has one line in it. It says the main branch contains the latest code and warns you to be aware of possible bugs on it. That is unusual to find stated so plainly, and it is the most useful sentence in the file for anyone about to build from a clone, which is what most people do without thinking. The tags tell you how much of a choice you have. The recent releases are v5.0.0-rc2 on 2026-10-30 and the 4.14.10 release candidates rc2 on 2026-10-28 and rc1 on 2026-10-21, which tells you two lines are in flight and they are not in step with each other. Pin a tag, and record which of the two lines you pinned.
Two detection philosophies with different false-positive profiles
The intrusion detection description is really two mechanisms, and the file keeps them apart. The agents scan the monitored system for malware, rootkits and suspicious anomalies, and specifically for hidden files, cloaked processes, unregistered network listeners and inconsistencies in system call responses. The server, separately, uses a signature-based approach with a regular expression engine to analyse collected log data for indicators of compromise. Both feed the same alert stream, and they fail differently. A host scan finds what is running now and is blind to anything it does not know to look for, while a log signature finds patterns in what was recorded and is blind to a machine that never logged the event. Tuning one does not tune the other, which is why a deployment that only ever adjusts the rules will be surprised by what the agent reports.
The log path works with no agent at all, which changes the deployment shape
One sentence in the log analysis section widens the scope considerably. Agents read operating system and application logs and forward them to a central manager for rule-based analysis and storage, and then it says that when no agent is deployed the server can also receive data over syslog from network devices or applications. So the platform has two operating modes that people conflate. With agents, it is an endpoint product that also analyses logs. Without agents, it is a log collector and analysis engine fed by whatever can speak syslog, including firewalls, switches and applications that were never part of your estate.
Active response is remote execution, and the trigger criteria are yours
The incident response section describes two capabilities that deserve to be read as one. There are out-of-the-box active responses that perform countermeasures against active threats, and the example given is blocking access to a system from the threat source when certain criteria are met. And separately, the platform can be used to run commands or system queries on agents remotely, to identify indicators of compromise and to do live forensics. The first is a response capability and the second is a remote execution capability. The criteria deciding when the first fires are configuration you write, which makes them the difference between a tool that contains an incident and a tool that causes one by blocking a source that turned out to be a false positive. This is the setting to design before you deploy, not after.
Compliance is the use case the file argues best, and it is not a bad one
The regulatory compliance section is the most specific argument in the document. It says the platform provides some of the necessary security controls to become compliant with industry standards, that it is widely used by payment processing companies and financial institutions to meet payment card industry data security standard requirements, and that the web interface produces reports and dashboards that help with that and with other regulations, naming GPG13 and the general data protection regulation. Anchoring all of this is file integrity monitoring, which watches content, permissions, ownership and attributes, identifies which user and which application made a change, combines with threat intelligence, and is required by several standards. Read that as an engineering fact rather than a marketing one: the rules are shaped for audit evidence, which is a different design pressure from detection quality.
The deployment story is eight separate repositories, none of them here
The orchestration section lists the automation tools the team maintains, and each one is its own repository: a CloudFormation template, a Docker repository, and modules for Ansible, Chef, Puppet, Kubernetes, Bosh and Salt. That is eight projects with eight release cadences; the file lists them as the automation tools maintained by the Wazuh team. Two consequences follow. Choosing an installation path is a real decision, because following one of these means pinning a second project. And a reader looking for a single answer to how to install this will not find it in the repository they cloned, which is why the documentation site is linked at the very top of the file and why the install and upgrade scripts at the top level are a starting point rather than a manual.
Editorial conclusion
Wazuh fits a team with a compliance obligation, most often around payment data, that wants file integrity monitoring, log analysis and vulnerability correlation in one place with an agent it controls. It does not fit a team that wants one binary, because the agent, the server and the indexer are three things with three version lines and the orchestration tooling lives in eight separate repositories. Before you install, read the branches note, which says the default branch may contain bugs, and build from a tag instead. Then decide how much authority the agent has, because active response is remote command execution on every monitored host and the criteria that trigger it are yours to write. And if compliance is the driver, read the rule content before you buy the story: the ruleset is a directory in this repository, and the quality of what it detects is that directory rather than the product description.
Frequently asked questions
What is Wazuh used for?
It is a free and open source platform for threat prevention, detection and response across on-premises, virtualised, containerised and cloud environments. Its documented capabilities include intrusion detection, log data analysis, file integrity monitoring, vulnerability detection against continuously updated CVE databases, configuration assessment, incident response, regulatory compliance, cloud security and container security.
Is Wazuh SIEM or edr?
The project's own description calls it unified extended detection and response and security information and event management protection for endpoints and cloud workloads. Mechanically it is an endpoint agent plus a management server, with a separate indexer providing the search engine and visualisation, and the file names payment processors and financial institutions as a principal user group for compliance work.
Is Wazuh free?
The project describes itself as a free and open source platform and the file states no price. The surrounding material is separate: the automation and deployment tooling is maintained as eight other repositories, and the file links the company site, documentation and community channels alongside the open source project.
how to install wazuh
The repository itself ships an install script and an upgrade script at its top level, and the documentation site is linked from the top of the file. The orchestration section points to eight separately maintained integration repositories, covering CloudFormation, Docker, Ansible, Chef, Puppet, Kubernetes, Bosh and Salt, so automated deployment means choosing between those projects.
how to use wazuh dashboard
The web interface provides data visualisation and analysis, and it can also be used to manage the Wazuh configuration and monitor the platform's status. The sections the file names are security events, integrity monitoring, vulnerability detection, regulatory compliance, an agents overview and an agent summary.
Is Wazuh a good security tool?
The project makes no comparative claim, so there is nothing here to quote. What the file does state is the scope, the three-component architecture, the warning that the main branch may contain bugs, and the fact that the detection logic is a ruleset you can read in the repository, which is the part worth evaluating before you deploy it.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/wazuh-wazuh)Star history chart for your README
[](https://hysenlabs.com/projects/wazuh-wazuh)Was this useful?