Scanners-Box is a link list that grew an AI agent section first
A powerful and open-source toolkit for hackers and security automation: a collection of self-developed open-source scanners by security professionals.
At a glance
- What is it?
- Scanners-Box collects open-source security scanners into a single README in three languages, with no code of its own to install. What the categories cover, which entries actually execute attacks rather than report them, and what the list cannot tell you about any project it links.
- Who is it for?
- Use Scanners-Box as a starting map when you are new to a category and need names to evaluate, then go read each repository before adopting anything from it. Do not treat it as a tool you can install, version, or hold responsible for a finding.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 9 days ago.
- What is it written in?
- GitHub does not report a main language for this repository.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
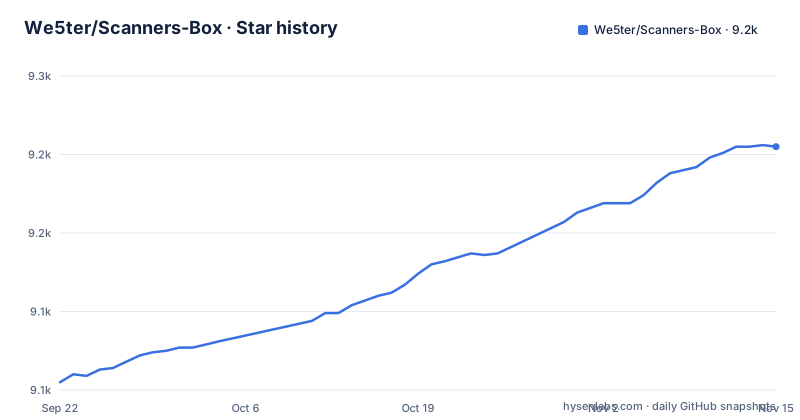
- We5ter/Scanners-Box9,205 ★ · +150
| Repository | 2026-09-22 | 2026-11-15 |
|---|---|---|
| We5ter/Scanners-Box | 9.1k | 9.2k |
150 Stars in the last 54 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The repository holds three READMEs and no code
Look at what is actually in the tree: .github/, LICENSE, README.md, README_CN.md, README_ES.md, badges/, logo.png. There is no source directory, no manifest, no Dockerfile, nothing to install and nothing to run. Scanners-Box is a curated link list, and the deliverable is the URL in each bullet. That has a direct consequence for anyone evaluating it: you cannot install it, you cannot audit its code, and you cannot pin a version, because the tool you end up using lives in a different repository under a different license with its own maintainers. What you get instead is a map of which category a class of tool belongs to, with one or two projects already collected under each heading.
Entries are bare links with a one-line pitch and no version
The format is uniform: a repository URL, a dash, then a single bolded sentence describing what the tool does. Nothing in that sentence gives you the license, the supported platforms, the last release, or whether the project still builds on your machine. A reader who treats the list as a recommendation inherits that gap, because a one-line description cannot tell you whether a scanner is kept alive, whether it needs a paid API key, or whether it will still install on your distro. The ordering is editorial too: within a heading there is no table, no tag system, and nothing to filter on, so deciding which entry in a given category suits you means opening every repository in that category yourself.
The AI agent heading sits first and is called the focus zone
The first heading in the table of contents is AI Red Teaming Frameworks & Agents, described as mature autonomous agents plus foundational frameworks to build your own. It holds the deepteam red teaming framework for LLM systems, pentagi, a fully autonomous multi-agent pentesting system in Go that runs whole engagements inside an isolated Docker sandbox with 20+ built-in tools including nmap, metasploit and sqlmap; Cairn, a state-space search engine with no predefined roles or workflows, purely goal-driven pathfinding; shannon, a white-box AI pentester for web apps and APIs; and CyberStrikeAI, a Go platform integrating 100+ tools with role-based testing and a skills system. Below that sit the LLM-powered scanners, then tools that audit AI applications themselves.
Several entries execute attacks instead of reporting them
Most of what is collected here reports; some of it acts. Dark-Moon is described as an autonomous AI pentesting engine performing continuous offensive security across web, cloud, AD and Kubernetes, using agentic reasoning, real exploit execution and attack path analysis to produce what it calls proof-based vulnerabilities. SickHackShark is built for CTF automation, covering recon, scanning, exploitation and flag capture end to end. CyberStrikeAI ships a built-in lightweight C2 framework, and shannon executes real exploits against pre-production web apps and APIs. In the entries shown, the only mention of authorization sits inside a single entry, CyberStrikeAI, which describes a C2 framework for authorized engagements. For a reader, that is the practical risk: a one-line description does not tell you which entries need a signed scope document first.
Runtime controls answer a question the scanners never ask
One category answers a problem the scanners do not: what an agent is allowed to touch while it works. NVIDIA OpenShell is a sandboxed runtime for autonomous agents where declarative YAML policies enforce boundaries across filesystem, network, process and provider access, block data exfiltration and unauthorized egress, and inject credentials only into policy-admitted endpoints; it runs Claude Code, Codex, OpenCode and Copilot CLI in isolated containers on Docker, Podman, MicroVM or Kubernetes. Microsoft's agent-governance-toolkit works from the other side, authorizing tools and actions through a policy engine, zero-trust agent identity with short-lived scoped credentials, OS-level execution sandboxing, circuit breakers, budget caps and audit trails, with reference policy packs mapped to all 10 OWASP Agentic Top 10 categories.
Audit tools read configuration, not traffic
A separate group inspects how an AI system is set up rather than what it sends over the wire. agentshield is a security auditor for agent configurations that scans Claude Code setups for hardcoded secrets, permission misconfigs, hook injection, MCP server risks and prompt injection vectors, carrying 268 rules across 15 modules, a 0 to 100 score, auto-fix, CI gating and compliance mapping to SOC 2, PCI DSS and ISO 27001. Tencent's AI-Infra-Guard covers AI infrastructure vulnerability scanning, MCP server risk detection and LLM security assessments, while garak probes models for hallucination, data leakage, prompt injection, misinformation, toxicity generation and jailbreaks, and LLMFuzzer fuzzes large language models directly. A scan of this kind tells you about the setup on disk, so it says nothing about a prompt a user types later.
The table of contents is generated and marks itself do not edit
Between the START and END doctoc markers the page carries an instruction not to edit that section and to re-run doctoc instead, which means the table of contents is derived from the headings below rather than curated by hand. That is a sensible convention for a page this size, and it has a visible cost: the contents describe what the collection intends to cover, while the entries under each heading move on their own schedule. Those headings also advertise a wide floor of traditional categories, covering smart contract scanners, red team and blue team tooling, mobile app package analysis, binary executable analysis, privacy compliance, subdomain enumeration or takeover, SQL injection and brute force, weak credential enumeration for the web, IoT hardware audit, cross-site scripting detection, enterprise sensitive information leak scanning, malware detection, middleware assessment, static and dynamic code analysis, and advanced persistent threat detection.
No releases, no changelog, and a license field reading NOASSERTION
The repository publishes no GitHub releases, so there is no version to pin and no changelog to read before you adopt anything from it, and the listing shows the license as NOASSERTION even though a LICENSE file sits at the top level. The terms for the list itself are therefore not summarized in any metadata a tool would read, and that ambiguity sits one click away from the license of each project it links, which is a separate decision you have to make per project. The page also ships README_CN.md in Simplified Chinese and README_ES.md in Spanish beside the English original, so a security decision taken from a translation can lag the English text. The last push to the repository was on 2 November 2026, which makes the index itself current even though nothing inside it is versioned.
Editorial conclusion
Use Scanners-Box as a starting map when you are new to a category and need names to evaluate, then go read each repository before adopting anything from it. Do not treat it as a tool you can install, version, or hold responsible for a finding. Before you run any entry, check its own authorization model, and before you paste a link from it into a report, open the project and confirm it still builds and still says what the one-line description claims.
Frequently asked questions
What is the Scanners-Box thing called?
The repository is Scanners-Box, and the collection inside it is titled the open-source security arsenal for hackers, enterprises, and AI agents. It lives at We5ter/Scanners-Box on GitHub, with a companion site at https://we5ter.github.io/ai-tools/, and it is written as a README in English, Simplified Chinese, and Spanish.
What is the best scanner in Scanners-Box to use?
The list does not rank anything. Entries are grouped under category headings and given a single sentence each, with no scores, no comparison table, and no ordering beyond editorial choice, so there is no best scanner to read off the page. Pick the category that matches your task, then open the projects listed under it and evaluate each on its own terms.
Where should I store documents I have scanned with Scanners-Box?
Scanners-Box has nothing to do with storing scanned documents, and it stores nothing. The repository contains only README.md, README_CN.md, README_ES.md, LICENSE, badges, and a logo, with no code, no service, and no file storage component of any kind.
What are the main types of scanners in Scanners-Box?
The categories cover AI red teaming frameworks and agents, LLM-powered vulnerability scanners, security auditing for AI agents and apps, AI agent runtime controls, security auditing for agent skills, scanners for smart contracts, mobile app package analysis, binary executable analysis, subdomain enumeration or takeover, SQL injection and brute force, weak credential enumeration, cross-site scripting detection, malware detection, middleware assessment, static and dynamic code analysis, and more.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/we5ter-scanners-box)Star history chart for your README
[](https://hysenlabs.com/projects/we5ter-scanners-box)Was this useful?