Weave router: an ONNX scorer in process, Postgres migrations, and a compose file that says dev only
Model router for agentic systems. Routes every prompt to the right model in <50ms. Cut costs 40-70% with just an endpoint change.
At a glance
- What is it?
- weave-os/router is a Go service that picks a model for each prompt and claims sub-50ms routing and 40 to 70 percent cost savings from an endpoint change. Underneath, it embeds its scorer in process with ONNX, keeps state in Postgres, and ships a local compose stack its own comments forbid you from exposing.
- Who is it for?
- Weave router fits a team already running agent workloads on several providers that wants routing decisions made in one place, with a scorer it can pin to a specific model commit and a database it can migrate. It does not fit a production deployment that starts from the bundled compose file, because that file names itself development only, ships default database credentials and a single-instance Postgres with no resource limits.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
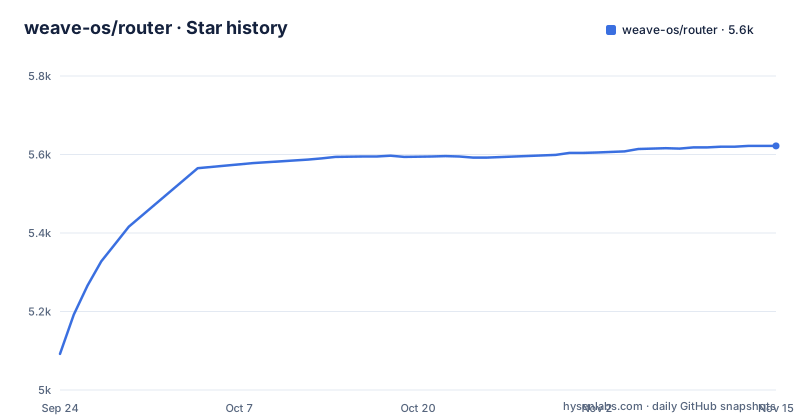
- weave-os/router5,622 ★ · +530
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| weave-os/router | 5.1k | 5.6k |
530 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
One Go binary, but the module reaches into Postgres, JWT and OpenTelemetry
The go.mod file is the fastest way to read the shape of this service. The module is weave-os/router, it declares go 1.26.0 with a toolchain line pinning go1.26.10, and its direct dependencies fall into recognisable groups. Serving and storage come from gin-gonic/gin and jackc/pgx/v5, with hashicorp/golang-lru/v2 for caching and google/uuid for identifiers. Security comes from golang-jwt/jwt/v5 and tink-crypto/tink-go/v2, and validation from santhosh-tekuri/jsonschema/v6 with tidwall gjson and sjson for reading and rewriting JSON. Telemetry is the largest block, with otelgin, otelhttp and runtime instrumentation plus OTLP metric and trace exporters over gRPC. Cloud pieces appear as cloud.google.com/go/auth and pubsub/v2. So the router is an HTTP service with a database, a token layer and a trace on every request, and the one dependency that explains its Docker image is hugot, the in-process inference runtime, which the Dockerfile takes further.
The scorer runs ONNX in process, which is why the base image is glibc
The Dockerfile comment at the top explains the build in one paragraph. The router uses hugot together with onnxruntime_go, which is CGO and dynamically links against libonnxruntime.so, to run the cluster scorer's embedders in process. Those embedders are named: Jina v2 and Qwen3-0.6B. Because the library is loaded into the running process, the base image has to be glibc, since Alpine and musl cannot load it out of the box. The builder is therefore bookworm-glibc and the runtime is distroless/cc-debian12, chosen to get the C runtime without the rest of Debian's userland. A third stage builds the mini UI as a Next.js static export with Node.js and copies it into assets/ui before the Go binary is assembled. In other words, this is not a pure Go deployment story: the binary dynamically links a native inference library and is assembled with a compiled web UI.
Model weights are pinned to a commit SHA so a build cannot silently drift
The cluster scorer model lives on the HuggingFace Hub, and the Dockerfile pins it hard. The repository is an argument, jinaai/jina-embeddings-v2-base-code, and the revision is a full commit SHA rather than a tag, with the comment spelling out the reason: pinning stops a deploy from quietly picking up a retrained model, and the note that Jina has not changed weights since April 2024 means the drift risk is low, so the pin is cheap insurance. You bump it deliberately, when scripts/upload_to_hf.py pushes a new version. A second embedder, Qwen3-Embedding-0.6B, is exported with last-token pooling baked into the graph by scripts/export_qwen3_onnx.py and uploaded to a public Weave-owned repo, an Apache-2.0 derivative pulled the same public way as Jina. Setting the Qwen repo argument to empty skips that pull, and because the runtime builds embedders lazily, a deploy that only serves Jina never needs the asset. Private repos authenticate with an HF_TOKEN build secret passed at build time, not baked into the image.
docker compose up is a smoke test, and the file refuses to be a deployment
The compose file is candid about its own limits in its opening comments. It brings up Postgres, applies migrations and starts the server end to end, which makes it suitable for a docker compose up smoke test, and then it says in capitals that it is development only, not tuned for production, because it is a single-instance Postgres with no resource limits and default credentials below, and it tells you not to deploy it to any environment exposed beyond localhost. The commands it documents are correspondingly small:
docker compose up --build
curl http://localhost:8080/health
docker compose run --rm seed
The database service is postgres:15-alpine with a health check that runs pg_isready every second, timing out after three seconds and retrying thirty times. Its host port is mapped to 5433 rather than 5432, specifically to avoid colliding with the Weave backend's own local Postgres, while the router inside the compose network still talks on the internal 5432. An init script mounted read-only creates the router schema on first database creation so the migrate sidecar can drop its schema_migrations table in the right place, and a named volume holds the data. There is also an optional traffic capture, with the output written to an ignored directory on the host.
The health endpoint is open, and the validate endpoint answers 401 to a bad key
Two of the documented checks in the compose file are worth reading as a security summary. The health check is a plain call to the health path on localhost port 8080, with no credential, which is normal for a liveness probe. The second is a deliberate negative test:
curl -H 'Authorization: Bearer rk_invalid' http://localhost:8080/validateThe comment beside it marks the expected result as 401. So the key format is a bearer token prefixed with rk_, and the validate endpoint is where you confirm a key before trusting it, and it rejects a bad one at the edge. The credentials in the compose file are the other half of that story: the Postgres user, password and database are all set to router as development defaults, and the .env template repeats the same warning to replace them in any deployment. Between the two files you get a fairly clear picture of the intended boundary, a permissive local loop for iterating and a validate path that is meant to be the first thing a real deployment exercises.
Postgres has two connection paths, and only one of them needs your certificates
The .env.example template is where the database configuration gets precise. You can either set a full DATABASE_URL connection string, which takes precedence, or you can set the four POSTGRES_ variables, and the template marks the whole database block as required for the router to boot. Beyond that basic set, the file separates two connection paths. The direct TCP path to a managed Postgres can demand mutual TLS, and when it does, four variables are set together: a server CA certificate, a client certificate, a client key, and a server name the server certificate has to carry, which matters when one CA signs for more than one database endpoint. The second path is the Cloud SQL Auth Proxy, which supplies its own certificates, so you leave those four unset and instead give the proxy instance name. The defaults are tuned for a local run, including an SSL mode of require with a note to set it to disable for local Docker, so the template is explicit about which values are placeholders you must replace.
A Pub/Sub emulator stands in for cross-replica cache invalidation locally
The compose file runs a Pub/Sub emulator alongside Postgres, and the comment says what it is for: cross-replica cache invalidation, with a note that in production this is GCP. That lines up with the dependency list, where cloud.google.com/go/pubsub/v2 sits in the direct requires. The design it implies is a horizontally scaled router where several replicas share a cache, and a message bus is what tells one replica that another has changed something the others are holding. Locally the emulator means you can exercise that path without a cloud project. It is a small detail in the compose file but a revealing one, because it shows the router is designed to run as more than one instance and to keep a shared view of its routing state, which is also why the single-instance Postgres in the same file is explicitly labelled as not for production.
Only one release exists, and it is a frozen model rather than a version
The release history is a single entry, a tag called hmm-model-v1, named HMM frozen model v1 and dated July 2026. That is not a software release in the usual sense, it is a frozen model artefact, which tells you something about how this project ships. The code moves on its own schedule, with the last commit on main recorded in November 2026, while the thing that gets a named tag is the model itself, frozen so a deployment can pin to a specific scorer. That is consistent with the Dockerfile pinning the embedder revision to a commit SHA and asking you to bump it deliberately. So the release discipline here is about the model, not the binary, and a team that wants reproducible routing should treat the frozen model tag and the pinned revisions as the versioned surface, while the Go code is the moving part around it.
Editorial conclusion
Weave router fits a team already running agent workloads on several providers that wants routing decisions made in one place, with a scorer it can pin to a specific model commit and a database it can migrate. It does not fit a production deployment that starts from the bundled compose file, because that file names itself development only, ships default database credentials and a single-instance Postgres with no resource limits. Before adopting it, separate the claims from the measurements: the sub-50ms routing and the 40 to 70 percent saving are the project's own numbers and the README cites no benchmark result for them, though bench/ holds an evaluation harness, so run your own before believing them. Then pin the embedder revisions, decide whether the Anthropic passthrough is acceptable for your keys, and read the docs directory for the routing and scoring model before you route production traffic through it.
Frequently asked questions
What is the weave-os router and what does it claim?
It is a model router for agentic systems that routes each prompt to a model. The project states it routes in under 50ms and cuts costs by 40 to 70 percent from an endpoint change alone, though the README cites no benchmark result for either number.
Can I run weave-os/router with its bundled docker compose file?
You can run it locally as a smoke test with docker compose up --build, but the file states it is development only, with a single-instance Postgres, no resource limits and default credentials, and it tells you not to deploy it beyond localhost.
What must be configured before the weave-os router boots?
The database block is required, either a full DATABASE_URL or all four POSTGRES_ variables, and at least one provider API key is recommended, with OpenRouter suggested as the baseline because it unlocks the open source model pool the cluster scorer is trained against.
How does the weave-os router handle model weights and updates?
The cluster scorer embedders are pulled from the HuggingFace Hub with the revision pinned to a specific commit SHA, so a deploy cannot silently pick up retrained weights, and the note asks you to bump that pin deliberately when a new version is uploaded.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/weave-os-router)Star history chart for your README
[](https://hysenlabs.com/projects/weave-os-router)Was this useful?