whisper-money carries a non-commercial badge on a self-hostable app
Understand your personal finances. Forget Excels, try Whisper Money.
At a glance
- What is it?
- A personal finance application on Laravel 12 and React 19 that can be self-hosted, whose readme badge is a Creative Commons non-commercial licence, whose environment example routes sessions, queue and cache to the database while the stack advertises Redis, and whose manual setup path depends on a command the page never installs.
- Who is it for?
- whisper-money is a real application rather than a demo, and the parts that show engineering judgement are worth naming. The environment example carries an unusually long comment on the OAuth server host, explaining that it must sit outside the progressive web app's manifest scope so that mobile sign-in links open in a browser rather than being swallowed by the installed app, and giving the production host.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly PHP, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
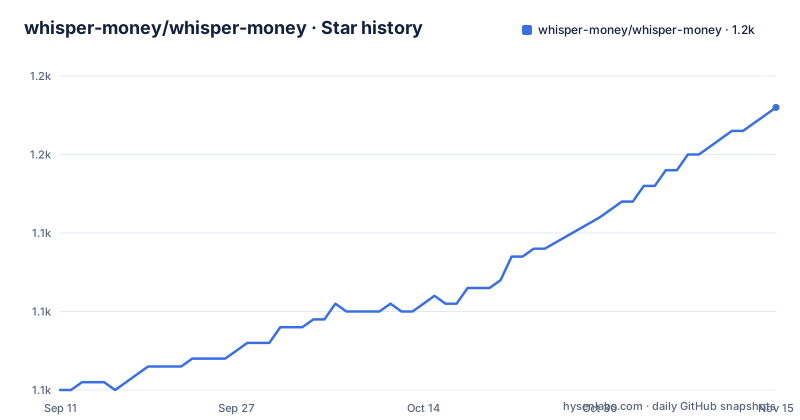
- whisper-money/whisper-money1,156 ★ · +36
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| whisper-money/whisper-money | 1.1k | 1.2k |
36 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Three licence signals and they do not agree
The readme leads with a Creative Commons badge for attribution and non-commercial use, version 4.0.
The hosting platform reports no recognised licence for the repository, and the root of the tree contains a single file named `LICENSE.md`, whose contents the file listing cannot confirm.
So there are three signals: a non-commercial Creative Commons mark on the page, no recognised licence in the metadata, and an unreadable file with the conventional name. Nothing on the page says which one governs.
The non-commercial part is the one with teeth, and it sits oddly against the rest of the project. This is a self-hostable web application with a Coolify deployment template, a Stripe subscription switch, and a feature list whose first item is that you own your data and that the whole codebase is public so you can check where it goes. The openness claim in that sentence is about visibility, not about terms of use.
There is also a localisation document at the repository root and eight translated versions of the readme on an external documentation service, so if the badge is deliberate it applies to translated copies too, and that is a separate question from the code.
The last push was 2026-10-02 and the newest tag is v0.2.11 from 2026-09-22, with the JavaScript manifest sitting at the same 0.2.11, so the version line is consistent even though the licence is not.
The manual setup depends on a command nobody installs
There are two documented install paths, and the second one has a gap in it.
The recommended path is a single line that runs a remote script through process substitution:
bash <(curl -fsSL https://whisper.money/setup.sh)After that you visit a wildcard localhost domain. The process substitution syntax is a shell feature rather than a POSIX one, so the line needs bash or something that implements the same syntax, and it executes a script that has just been downloaded.
The manual path is two steps. Clone the repository and change into it, then run `whispermoney install`.
Nothing on the page installs the `whispermoney` command. There is no global install line, no composer global require, and no reference to how the CLI ends up on your path after a clone. The page even warns you that you must run that command before any other, because commands like start will not work without it.
So the path that avoids downloading and running a script also avoids the one step that tells you how to get the script's own tooling. That is the kind of gap a reader discovers at the second command.
There is a third path for the production image, which copies an example environment file and brings up a compose file, and the port changes through a variable. After that comes a section on deploying to a hosting platform from a template, with an application key and application URL described as automatic, and the container generating an application key on first startup if none is provided.
Sessions, queue and cache go to the database, not to Redis
The tech stack section lists the cache and queue layer as Redis. The shipped environment example does not use it.
Three lines decide that. The session driver is the database, the queue connection is the database, and the cache store is the database. Redis is configured further down with a host, a port and a null password, so it is present and reachable but not selected.
The consequence is operational rather than theoretical. An operator sizing infrastructure from the stack table provisions a Redis instance and then watches it sit idle while MySQL absorbs session writes, queue inserts and cache entries. A framework's session driver also means every request that touches a session writes to the primary database.
The development compose file does run a Redis container, published on a non-standard host port, so a developer following the stack table sees the service and reasonably assumes it is in use.
Other defaults in the same file are worth knowing before you install. Debug output is on. The log level is debug. Session encryption is off while session lifetime is 120 minutes. The password hash cost is 12 rounds. The mail transport points at a local mail catcher on the SMTP port that the compose file publishes, and the sender address for automated sequences is a different address with a two-person name in the from field, which tells you the project is run by two people.
The application key is blank in the example, and the container fills it in on first boot, which is fine with a persistent volume and destructive without one.
The development database accepts an empty password from any host
The compose file that the development workflow uses contains four settings that together make it unsuitable for anything but a laptop.
The MySQL root password is taken from an environment variable, and the example environment file ships that variable blank. The compose file additionally sets the flag that permits an empty password, so a blank value does not fail loudly, it produces a database with no root password. Root is then allowed from any host rather than only from localhost. And the database port is published to the machine on a non-default port.
There are health checks on the database and on the cache, and the database volume also mounts a framework-provided script into the initialisation directory, so the file is a working development stack rather than a careless one.
The production compose file is a separate file with a hyphen in its name, and the deployment section on the page tells you to use that one instead. The header of the development file does not warn you the way the development compose file in some other projects does; it simply exists alongside a production file with a different naming convention, which is the only signal that they are not equivalent.
The development image also differs from the production one. It installs curl, git, zip, unzip, process and network tools, a command line database client and a network listener, and it ends by running the framework's built-in server on all interfaces with no process manager, no queue worker and no scheduler. Those are development conveniences, and they are all present in the file the development compose service builds from.
A postinstall script patches a dependency instead of pinning it
The JavaScript manifest has a postinstall hook, and it runs a Node script whose name describes exactly what it does: patching the string width behaviour of an interactive prompt library.
That is the honest way to deal with a dependency whose terminal rendering is wrong, but it is a heavier commitment than the alternatives. A postinstall hook runs on every install, including in CI and inside a container build, and it modifies files inside another package in the dependency tree. If the dependency fixes the problem in a later version, the patch stays and may now be applying to a file whose shape has changed, and nothing will tell you because a patched file looks like a normal installed file.
Two build inputs in the same area are also worth noting. The container image installs the JavaScript runtime by piping an install script from the vendor's site into a shell, and copies the PHP package manager binary from its own moving latest tag rather than a pinned version.
The scripts block has two other shapes worth knowing about. The lint command fixes files rather than only reporting them, so a lint invocation mutates the working tree. And the format command is scoped to a single directory, so the formatter covers a fraction of the JavaScript and TypeScript in the project while a formatter configuration and an ignore file sit at the root.
The test story is split in two, which is normal for a framework that renders on the server: one runner for the PHP side and one for the JavaScript side. A browser driver is a development dependency for the PHP browser tests, and the container file says in a comment that its browsers cannot be installed at build time because the dependency directory has to exist first, so it is deferred to runtime.
Six agent tool directories and an autoresearch log at the root
The repository root carries configuration for six different coding agents, which is more than any project needs and is worth listing as a fact.
There are directories for agents, for a general AI tool, for one commercial assistant, for an editor, for one open source harness, and for one other tool. Two instruction files sit beside them, one for the general agent convention and one for a specific assistant. There is also a model context protocol configuration at the root and a second one for the open source harness, plus three more loose configuration files whose purpose is not explained anywhere on the page.
The model context protocol configuration is not incidental. The page's environment example documents OAuth signing keys for a protocol server and an authorization server host, and the JavaScript manifest carries the protocol SDK as a development dependency. So the application exposes itself as a tool server, with an issuer, a key pair that can be shared across instances, and a deliberate decision about which host serves the authorization endpoints.
There is also a small research loop committed as four files: a shell script, two documents, one of which is named as a dashboard, and a JSON Lines data file. The data file being in the repository rather than in a results directory means the run history is reviewable, which is either deliberate or an accident that someone has kept.
Everything else at the root follows from the stack. There are two Dockerfiles and two compose files with different naming conventions, lock files for both package ecosystems, a code style configuration for PHP and two static analysis configurations one of which is a baseline file, and an experiments directory.
Open banking is off, and what is left is six brokers
The feature list leads with bank accounts that sync straight from your bank, and the section explaining how says the connection is optional, is a paid third-party service, and that a self-hosted install ships with it switched off.
That is unusually direct, and the rest of the section is specific. The aggregator is a licensed open-banking provider. Turning it on needs two things: an application identifier, and an RSA key pair whose public half is registered against that application, where every API call is a JSON web token signed with the private half using the RS256 algorithm and the application identifier carried as the key identifier.
What works without it is the second half of the account story. Accounts can be created by hand or filled from a delimited-file import, and six brokers and exchanges connect with their own API key and never touch the aggregator: two of them are European brokers, two are European or global exchanges, one is a global payments account, and one is a US brokerage.
Two things follow. The headline feature is a purchase, not a setting, so a privacy-first application has an unavoidable dependency on a third party for the feature that distinguishes it from a spreadsheet, and the page is upfront about it. And the fallback list is entirely European and international, with no domestic bank aggregator outside that set, so coverage outside those markets is limited to manual entry and file import.
The user interface does not offer the connection anywhere when the identifier is blank, which means the feature disappears rather than showing as disabled.
Editorial conclusion
whisper-money is a real application rather than a demo, and the parts that show engineering judgement are worth naming. The environment example carries an unusually long comment on the OAuth server host, explaining that it must sit outside the progressive web app's manifest scope so that mobile sign-in links open in a browser rather than being swallowed by the installed app, and giving the production host. The pool defaults are documented with reasons rather than bare numbers. The manual install works offline from a clone. And the readme says plainly that bank sync is a paid third party that ships switched off.
Three things to settle first. The licence position is genuinely unclear: the readme badge is a Creative Commons attribution and non-commercial mark, the platform reports no recognised licence, and the root carries a file named `LICENSE.md` whose contents the listing cannot confirm. Those are three different signals and non-commercial terms are not what most people expect from a self-hostable Laravel application, so get it in writing before you deploy one. Second, the headline bank connection is off unless you buy an aggregator subscription and generate an RSA key pair, while the broker integrations use their own keys and work regardless. Third, the default environment puts sessions, queue and cache in MySQL rather than in the Redis the stack line advertises, so an operator sizing Redis from the documentation would size it for nothing.
If you self-host, treat the development compose file as a local-only file. Its database accepts an empty root password from any host and publishes the port to your machine, and the shipped example environment has the password field blank.
Frequently asked questions
What is whisper-money built on?
A Laravel 12 backend on PHP 8.4 with a React 19, Inertia and TypeScript frontend styled with Tailwind v4, MySQL for storage, Redis for cache and queue according to the stack table, and the Pest test runner for PHP. The JavaScript side uses a second test runner.
How do I install whisper-money?
The quick path runs a remote script through bash process substitution and you then open a wildcard localhost domain. The manual path clones the repository and runs whispermoney install, though the page does not document how the whispermoney command itself gets installed.
Does whisper-money connect to my bank automatically?
Not out of the box. Bank connections go through a licensed open-banking aggregator that is a paid third-party service, so a self-hosted install ships with it switched off and the feature is not offered anywhere in the interface. Six brokers and exchanges work with their own API keys instead.
Where do whisper-money sessions and the queue go by default?
Into the database. The shipped environment example sets the session driver, the queue connection and the cache store to the database, even though the tech stack table lists Redis for cache and queue and the development compose file runs a Redis container.
What licence does whisper-money use?
The signals conflict. The readme carries a Creative Commons attribution and non-commercial badge, the repository platform reports no recognised licence, and the root holds a single file named LICENSE.md whose contents are not visible from the listing.
Can I turn off public sign-ups in whisper-money?
Yes. A registration switch defaults to true, and setting it to false closes public sign-ups so the register routes return a forbidden response and every registration call to action is hidden, while the login route stays open.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/whisper-money-whisper-money)Star history chart for your README
[](https://hysenlabs.com/projects/whisper-money-whisper-money)Was this useful?