wireguard-windows is a mirror whose go.mod replaces two dependencies with its own path
Download WireGuard for Windows at https://www.wireguard.com/install . This repo is a mirror only. Official repository is at https://git.zx2c4.com/wireguard-windows
At a glance
- What is it?
- The official WireGuard client for Windows, built on WireGuardNT, published on GitHub as a mirror only. The build downloads a pinned Go toolchain and the WireGuardNT archive with SHA-256 verification, targets three architectures, and the manifest satisfies two upstream dependencies from this module's own pseudo-versions.
- Who is it for?
- Read this repository as the mirror it declares itself to be, with the official source at git.zx2c4.com/wireguard-windows, and treat the client it builds as the one the README calls the only official and recommended way to run WireGuard on Windows. Take the installer route on a single machine, because it selects the right architecture, checks signatures and hashes, and installs for you; use the standalone MSIs only when you are deploying to many machines as an administrator.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 50 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
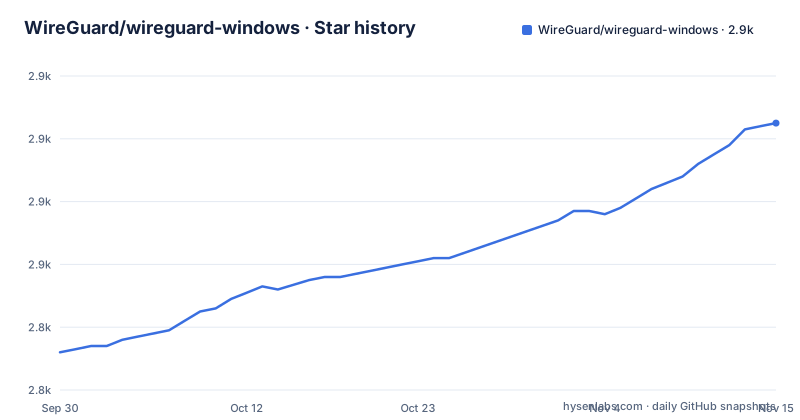
- WireGuard/wireguard-windows2,905 ★ · +73
| Repository | 2026-09-30 | 2026-11-15 |
|---|---|---|
| WireGuard/wireguard-windows | 2.8k | 2.9k |
73 Stars in the last 46 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The description says mirror only, and names the real repository
The repository description is two sentences and both matter. It points readers at the WireGuard for Windows download page, and then says this repo is a mirror only, with the official repository at git.zx2c4.com/wireguard-windows.
So the GitHub copy is a distribution convenience rather than the place work happens. There are no GitHub releases here either, so version history on this side is whatever the commit log holds. The last push was on 2026-09-26 and the repository is not archived.
What the README does claim is strong. It describes this as a fully-featured WireGuard client for Windows that uses WireGuardNT, and then states that it is the only official and recommended way of using WireGuard on Windows.
That second sentence is the one to hold on to. It is a statement about the client, not about the mirror, and it means the answer to whether there is another supported Windows client is in this page: there is not, by the project's own account. Everything else on this page is either the mirror's own build machinery or a set of documents aimed at administrators and auditors.
Two download routes, and only one of them verifies anything
If you came to run WireGuard rather than to read the source, the README sends you to the main download page and describes the two things there.
The first is the WireGuard Installer. Its stated behaviour, in full: it selects the most recent version for your architecture, downloads it, checks signatures and hashes, and installs it. Verification is part of the installer's job rather than something you arrange.
The second is a directory of standalone MSIs, described as being for system administrators who wish to deploy the MSIs directly, with the note that for most end users the ordinary installer takes care of downloading these automatically.
That split is the whole deployment story. One machine means one installer, and every integrity check happens inside it. A fleet means the MSIs, and from there the verification burden moves to whoever distributes them, which is why the same repository ships `docs/adminregistry.md`, a list of registry keys settable by the system administrator for changing the behaviour of the application.
Nothing in the README names a minimum Windows version, an architecture list beyond the installer's own selection, or an upgrade policy for an installed MSI.
Five documents ship with it, and one is written for auditors
Beyond the README there are five documents, each named with a one-line description, and the descriptions tell you what kind of project this is.
`adminregistry.md` is a list of registry keys settable by the system administrator for changing the behaviour of the application. `attacksurface.md` is a discussion of the various components from a security perspective, so that future auditors of the code have a head start in assessing its security design. `buildrun.md` covers building, localizing, running and developing for the repository. `enterprise.md` summarises features and tips for making the application usable in enterprise settings. `netquirk.md` describes various networking quirks and kill-switch semantics.
Three of those five exist because this is a client that sits inside the operating system. A registry key list is needed to change behaviour without repackaging. An attack surface document is needed because a VPN client holds keys and manipulates routes. And kill-switch semantics need writing down, since that is where a VPN's behaviour under failure is decided and where a reader auditing it will look first.
The build repository section links all five by path inside `docs/`, and the tree confirms that directory exists.
Two upstream dependencies are replaced by this module's own path
go.mod declares the module as golang.zx2c4.com/wireguard/windows with `go 1.26.0` as the language floor, and then does something that explains the mirror arrangement:
replace (
	github.com/lxn/walk => golang.zx2c4.com/wireguard/windows v0.0.0-20260420103851-857e549307fe
	github.com/lxn/win => golang.zx2c4.com/wireguard/windows v0.0.0-20210224134948-620c54ef6199
)
The two GUI dependencies, `github.com/lxn/walk` and `github.com/lxn/win`, are not resolved from their upstream at all. Both are redirected to pseudo-versions of this repository's own module path.
The effect is that the original import paths keep working while the code that satisfies them comes from this project. Anyone vendoring or auditing the dependency graph has to know that a `github.com/lxn` import in this build does not mean lxn's code.
The rest of the manifest is ordinary: golang.org/x/crypto, x/net, x/sys and x/text as direct requirements, x/mod, x/sync and x/tools as indirect. One detail is worth noting: x/text is pinned to a pseudo-version whose timestamp is 2026-09-18, three days before the last push, which is a pin to an untagged commit rather than a release.
There is also a `go.mod.master` next to `go.mod` in the root, which is a mirror-specific artefact rather than something a normal module would carry.
The build downloads Go 1.27.1 and checks its hash before extracting
The Makefile does not use the host's Go. It fetches its own toolchain and verifies it, using a download template that is careful about failure:
	if ! curl -L#o [email protected] $(2); then rm -f [email protected]; exit 1; fi
	if ! echo "$(3)  [email protected]" | sha256sum -c; then rm -f [email protected]; exit 1; fi
The sequence is fail-closed: download to an `.unverified` suffix, check the SHA-256 against the expected value, delete the file and exit non-zero on either failure, and only then move it into place. Nothing is extracted from an unverified archive.
Two downloads are wired to that template. The Go toolchain, as `go1.27.1.linux-amd64.tar.gz` from go.dev, expected hash beginning 63d339f0. And `wireguard-nt-1.1.zip` from download.wireguard.com, expected hash beginning dceb30a9.
The Linux archive is the notable one, because it means the Windows client is built on a Linux host and cross-compiled rather than built on Windows. The extracted toolchain is put ahead of PATH in the repository's own `.deps` directory, so a developer's installed Go version is irrelevant to the result.
The declared floor in go.mod is 1.26.0 and the pinned toolchain is 1.27.1, which is a minimum rather than a contradiction.
Three architectures, a GUI subsystem binary, and version stamping off
The build's target list is one line:
all: amd64/wireguard.exe x86/wireguard.exe arm64/wireguard.exeThree architectures, including 32-bit x86 alongside amd64 and arm64.
The compiler flags carry more information than the target list does. `-H windowsgui` links a GUI subsystem binary with no console window. `-s -w` strips the symbol table and DWARF information. `-trimpath` removes local filesystem paths from the binary. `-buildvcs=false` turns off Go's VCS stamping, which is the flag you would expect a mirror to need. `-overlay .overlay/overlay.json` is how the mirror substitutes files without editing the tree, and `-tags load_wgnt_from_rsrc` is what makes WireGuardNT load from the binary's own resources.
Version information is extracted from source rather than passed in. A sed expression pulls the Number field out of `version/version.go`, and that value is compiled into the resource file as `WIREGUARD_VERSION_STR`, with the array form alongside it, under `-O coff -c 65001`, where 65001 is the UTF-8 code page. The icon set enters the same way: `resources.rc` plus every `.svg` under `ui/icon/` converted to `.ico`.
There are also deployment defaults in the same file, a host named winvm, an architecture of amd64 and a path of Desktop, which is a convenience for whoever assembles the test machine.
MIT-licensed, with an All Rights Reserved line above the grant
The licence section is one sentence and then the notice itself. The sentence says this repository is MIT-licensed. The notice begins:
Copyright (C) 2018-2026 WireGuard LLC. All Rights Reserved.and continues into the standard MIT permission grant, which is cut off partway through the word "substant". So the header carries an All Rights Reserved line directly above an MIT grant, which is common boilerplate practice rather than a contradiction, but it is the kind of thing worth reading rather than assuming.
The root listing shows what the client is made of, as directories rather than as prose. `driver/` for the kernel component, `tunnel/` for the data path, `manager/` for the service, `services/`, `ui/` for the interface, `updater/`, `installer/`, `elevate/` for the privilege path, `conf/` for configuration, `l18n/` with `locales/` for translation, `ringlogger/` for buffered logging, and `embeddable-dll-service/` for the variant that runs as a library rather than an application.
Two Windows batch files sit at the root next to the Makefile, `build.bat` and `quickinstall.bat`, so the repository supports a Windows command line as well as the Linux cross-compile path. The last push was on 2026-09-26.
Editorial conclusion
Read this repository as the mirror it declares itself to be, with the official source at git.zx2c4.com/wireguard-windows, and treat the client it builds as the one the README calls the only official and recommended way to run WireGuard on Windows. Take the installer route on a single machine, because it selects the right architecture, checks signatures and hashes, and installs for you; use the standalone MSIs only when you are deploying to many machines as an administrator. Verify which repository you are building from first, since two go.mod replace directives resolve the lxn dependencies against this module's own path, and expect the build to fetch a pinned Go 1.27.1 toolchain and the WireGuardNT 1.1 archive with SHA-256 verification before anything is extracted.
Frequently asked questions
What is wireguard-windows?
It is a fully-featured WireGuard client for Windows that uses WireGuardNT, and the README states it is the only official and recommended way of using WireGuard on Windows. The GitHub repository is a mirror only; the official repository is at git.zx2c4.com/wireguard-windows.
How do you install WireGuard for Windows?
Use the WireGuard Installer from the main download page: it selects the most recent version for your architecture, downloads it, checks signatures and hashes, and installs it. Standalone MSIs are also published, described as being for system administrators who want to deploy them directly, with the installer handling that download automatically for most end users.
Which documents ship with the wireguard-windows repository?
Five besides the README: adminregistry.md with registry keys the system administrator can set, attacksurface.md written so future auditors have a head start on the security design, buildrun.md for building, localizing, running and developing, enterprise.md with enterprise features and tips, and netquirk.md covering networking quirks and kill-switch semantics.
How does the wireguard-windows build work?
The Makefile exports GOOS as windows, uses an overlay file for mirrored substitutions, and the build tag load_wgnt_from_rsrc to load WireGuardNT from the binary's resources. It downloads a pinned Go 1.27.1 toolchain and the wireguard-nt 1.1 archive, verifying both with sha256sum before extraction, and produces amd64, x86 and arm64 executables.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/wireguard-wireguard-windows)Star history chart for your README
[](https://hysenlabs.com/projects/wireguard-wireguard-windows)Was this useful?