wolfssl: the repository description still names 5.9.1, and neither SBOM path runs the check it targets
The wolfSSL library is a small, fast, portable implementation of TLS/SSL for embedded devices to the cloud. wolfSSL supports up to TLS 1.3 and DTLS 1.3! Update to wolfSSL 5.9.1 for the latest CVE fixes.
At a glance
- What is it?
- An ANSI C TLS library for embedded, RTOS and server targets, with an OpenSSL compatibility layer, hardware key handling, and recent additions for supply-chain compliance. Three things to read before trusting the file: the size and speed claims carry no numbers, the compliance tooling documents itself as not checking the standard it targets, and the compatibility layer that eases porting removes four enum names you may already be using.
- Who is it for?
- wolfssl is a defensible choice when footprint is the binding constraint, since the library states typical sizes of 20 to 100 kB and targets embedded and RTOS environments directly, and the hardware key handling is a genuine differentiator rather than a checkbox. Three checks first.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly C, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
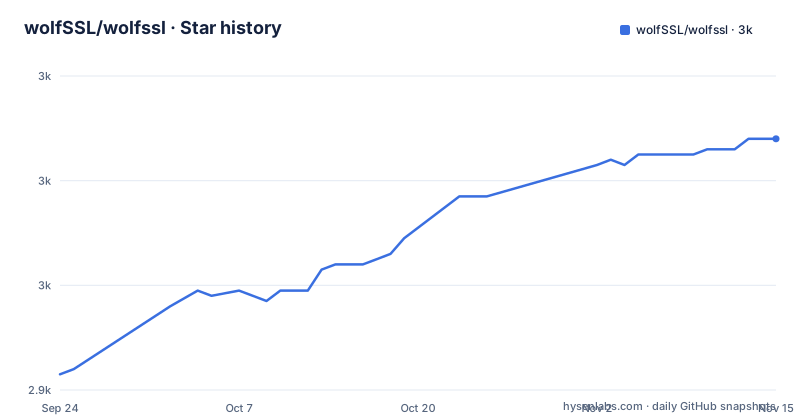
- wolfSSL/wolfssl2,988 ★ · +45
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| wolfSSL/wolfssl | 2.9k | 3k |
45 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The repository description pins a version two releases behind
The one-line description of the repository ends with an instruction to update to wolfSSL 5.9.1 for the latest CVE fixes. The releases tell a different story: v5.9.4-stable, named for September 25, 2026 and tagged on 2026-09-27, v5.9.2-stable from June 23, 2026, and v5.9.1-stable from April 8, 2026. So the advisory version named in the description is two releases behind the newest tag, and the sequence itself skips a number, going from 5.9.2 to 5.9.4 with no 5.9.3 among the recent releases. The last push to the repository is dated 2026-10-02. For a library whose description exists specifically to point people at security fixes, that string is the first thing a reader sees and the first thing that is out of date.
Neither SBOM path runs the check the section is written around
There are two entry points for bill of materials generation, and they are not equivalent. The embedded and IDE path is `python3 scripts/gen-sbom …`, configured through a hand-edited `user_settings.h` with no autotools required, and it covers Keil, IAR, STM32CubeIDE, ESP-IDF, Zephyr, plain CMake and custom Makefiles. The server path is `make sbom`, for Linux, Debian, RPM, Yocto and FIPS-ready builds that already use `./configure && make`. Both emit SPDX 2.3 and CycloneDX 1.6 JSON, and both are described as intended to satisfy the NTIA minimum elements. Then the file states the limit plainly: the `make sbom` path runs spec validation through `pyspdxtools` and gates the build on it, the standalone path validates only on demand as documented in `doc/SBOM.md`, and neither path runs an NTIA minimum elements checker by default. Two more targets sit alongside them. `make advisory` needs python3 and emits one CSAF 2.0 document and one CycloneDX 1.6 VEX document per CVE into `advisories/out/`, as `*.csaf.json` and `*.cdx.json`, built from records tracked under `advisories/` rather than from history at generation time. `make bomsh` produces an OmniBOR artifact dependency graph for cryptographic traceability from the installed library back to every source file that produced it.
Enabling the OpenSSL layer removes four enum names
The pitch for the library includes an OpenSSL compatibility API to ease porting into applications that previously used OpenSSL. The third note describes the cost. When wolfSSL is built with `--enable-opensslextra`, or with the macro `NO_OLD_SHA_NAMES`, the enum values `SHA`, `SHA256`, `SHA384` and `SHA512` are no longer available. Those names are mapped to the OpenSSL API for a single call hash function, and the replacement names are `WC_SHA`, `WC_SHA256`, `WC_SHA384` and `WC_SHA512`. So a build that turns on compatibility in order to port more easily also breaks source that used the older hash enumerators, which is exactly the code a porting project usually contains. The change is a rename rather than a removal of capability, but it is a compile error in code you did not write.
Disabling static cipher suites turns a configuration gap into a compile error
Since 3.6.6, SSLv3 is no longer enabled by default, and static key cipher suites using PSK, RSA or ECDH without ephemeral key exchange are disabled in favour of suites that provide perfect forward secrecy through ephemeral Diffie-Hellman or elliptic curve exchange. Three defines bring the old behaviour back: `WOLFSSL_STATIC_DH`, `WOLFSSL_STATIC_RSA` and `WOLFSSL_STATIC_PSK`. The file is clear about the trade, since those suites reuse one long-term private key for every session, so compromising that key decrypts past sessions. The build consequence is the part to plan for: compiling `ssl.c` now raises a compiler error when no cipher suites are available at all, removable by defining `WOLFSSL_ALLOW_NO_SUITES`. A narrow embedded configuration that previously built quietly will now stop, and the escape hatch is a macro that re-enables the old tolerance.
A single call disables server certificate verification
Certificate verification is where wolfSSL deliberately differs from OpenSSL, and the difference is safe by default. The client policy is to verify the server, so an application that does not load certificate authorities gets a connect failure rather than an unauthenticated session, reported as a connect error with no signer error to confirm failure, code -188. The file then documents how to get OpenSSL's more permissive behaviour, by making this call:
wolfSSL_CTX_set_verify(ctx, WOLFSSL_VERIFY_NONE, NULL);before calling `wolfSSL_new();`, and marks it as not recommended. Worth being explicit about the shape of this: the insecure option is one line, it is documented rather than hidden, and adopting it is a deliberate act with a name that says what it turns off. The same philosophy shows up elsewhere in the file, where re-enabling insecure cipher suites requires naming three separate defines rather than flipping one broad switch.
Three hardware key paths, and one of them keeps keys out of RAM
The file describes three separate mechanisms. CryptoCB key import, enabled with `CPPFLAGS="-DWOLF_CRYPTO_CB_AES_SETKEY -DWOLF_CRYPTO_CB_FREE"`, calls a callback during AES key setup and branches on its return: a success value imports the key to a secure element or HSM, does not copy it into wolfSSL memory, skips generating GCM tables, and routes every later AES operation through the callback, which is what makes TLS 1.3 traffic key protection possible where symmetric keys must never exist in main memory. An unavailable return falls back to the software path and copies the key to `devKey` for acceleration. Separately, device-unique keys can be derived from hardware entropy with `--enable-puf[=small|balanced|strong|strongest]`, choosing BCH error correction, and every raw SRAM readout is health tested so that all zeros, all ones, a repeating block or an implausible bit bias cannot silently yield a key shared across devices.
The size and speed claims arrive without measurements
Two comparative numbers lead the file: the library is stated to be up to 20 times smaller than OpenSSL, and user benchmarking and feedback are reported to show dramatically better performance. Neither is accompanied by a table, a configuration, a hardware list, or a link to a benchmark result. The one internally consistent figure is the footprint range, given as typical sizes from 20 to 100 kB, which is a range rather than a comparison. The tree does contain an `examples/benchmark/` directory, so the means of measuring exists inside the project even though no result appears in the documentation. Cryptographic validation is stated more concretely, with two wolfCrypt versions validated under FIPS 140-2 as certificates 2425 and 3389, and one under FIPS 140-3 as certificate 4718.
The top level holds two extensionless files with no obvious purpose
The repository root is wide, and a few entries stand out. Two bare files are named `input` and `quit`, with no extension and nothing else in the tree matching either name, so they read as leftovers from a scripted test rather than as source or configuration. Three readme files sit side by side, `README`, `README.md` and `README-async.md`, so a reader has to guess which one is current. Agent instruction files are present at the root as `AGENTS.md` and `CLAUDE.md`, alongside `SECURITY-POLICY.md`, `SECURITY-REPORT-TEMPLATE.md` and a `SCRIPTS-LIST`. Lint and editor configuration is explicit too, with a spell checker configuration and its exclusion list, a cypress ignore file, an editor config, and a file listing known macros for tooling. Build support is broad rather than tidy: CMake presets and settings, a Docker directory, a Vagrantfile with a helper script, `debian/` and `rpm/` packaging, kernel module directories for BSD and Linux, vendor trees for RTOS targets and IDEs, three FIPS-related shell scripts, a Perl certificate buffer generator, a commit test script, and a `sslSniffer/` tool.
Editorial conclusion
wolfssl is a defensible choice when footprint is the binding constraint, since the library states typical sizes of 20 to 100 kB and targets embedded and RTOS environments directly, and the hardware key handling is a genuine differentiator rather than a checkbox. Three checks first. Treat the comparative claims as positioning rather than measurement, since the file offers a twenty-fold size figure and reports of better performance with no benchmark behind either, even though a benchmark example directory exists in the tree. Decide early whether you want the OpenSSL compatibility layer, because enabling it renames four hash enums. And if you are adopting the SBOM tooling for a compliance deadline, read the note that neither entry point runs the minimum-elements checker by default, so the artifact you produce is not self-verifying.
Frequently asked questions
what is wolfssl
A lightweight SSL/TLS library written in ANSI C, formerly called CyaSSL, targeting embedded, RTOS and resource-constrained environments as well as standard operating systems. It supports up to TLS 1.3 and DTLS 1.3, and its cryptography comes from the wolfCrypt library inside it.
how to install wolfssl
The repository carries an INSTALL file at its root, and the documentation refers to section 21 of it for the advisory tooling. The compliance section names the build styles the project supports, including ./configure && make for Linux, Debian, RPM and Yocto, and a CMake path configured through a hand-edited user_settings.h. No single install command appears in the readme itself.
How much does a wolfSSL license cost?
The file states that wolfSSL is commonly used in standard operating environments because of royalty-free pricing, records the repository under GPL-3.0, and carries both a LICENSING file and a COPYING file at the top level. No price list or set of license tiers appears anywhere in the documentation.
Is wolfSSL FIPS validated?
Two versions of its wolfCrypt cryptography library are stated to be FIPS 140-2 validated under certificates 2425 and 3389, and one is FIPS 140-3 validated under certificate 4718. The file directs further questions to a FIPS FAQ page or to an email address.
How does wolfSSL compare to OpenSSL?
The file claims wolfSSL is up to 20 times smaller, reports that user benchmarking shows dramatically better performance, and offers an OpenSSL compatibility API to ease porting. It also documents a real behavioural difference: verification defaults to checking the server, and an application without certificate authorities gets a connect error with code -188 rather than an unauthenticated session.
What is the difference between wolfSSL and wolfCrypt?
They are not alternatives. The file states that wolfSSL is powered by the wolfCrypt cryptography library, so wolfCrypt supplies the cryptographic primitives and the FIPS validated builds, while wolfSSL is the TLS layer built on top of it.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/wolfssl-wolfssl)Star history chart for your README
[](https://hysenlabs.com/projects/wolfssl-wolfssl)Was this useful?