The panel ships with admin over plain HTTP
Deploy your own private zerotier-planet service in one minute.
At a glance
- What is it?
- This repository builds ZeroTier from source, patches its world generator to produce your own planet and moon files, and packages the result with a web management panel. The panel is documented with a fixed default username and password, over a port with no encryption unless you add a proxy yourself.
- Who is it for?
- This project suits someone who needs to remove a dependency on the public root server for a virtual network and is comfortable running a patched build they have read. Four things to check before you deploy it.
- Can I use it commercially?
- Not without permission. GitHub finds no licence file in the repository, and without a licence all rights are reserved by default: you may read the code but not reuse it. Check the README, or ask the authors, before using it.
- Is it still maintained?
- Yes. The repository last received commits 33 days ago.
- What is it written in?
- Mainly Shell, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
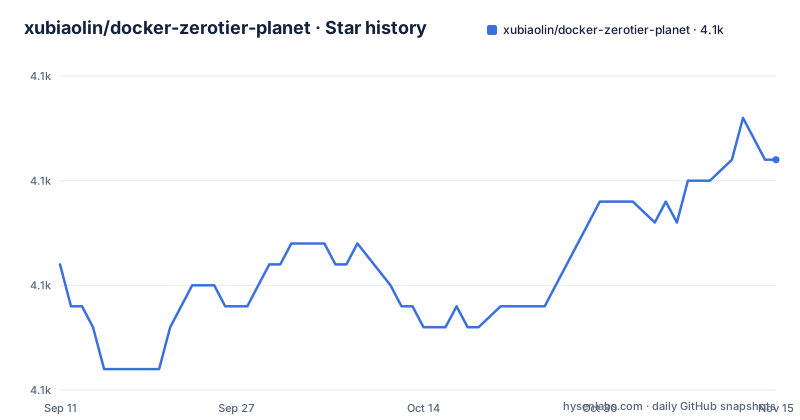
- xubiaolin/docker-zerotier-planet4,086 ★ · +5
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| xubiaolin/docker-zerotier-planet | 4.1k | 4.1k |
5 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The management panel is documented with a fixed default login and no encryption
The tutorial walks you to the panel by typing an address with a port into a browser, and immediately under that gives the default username and password. It is a password in capitals in the sense that matters: the same string for every installation on the internet. And the panel is reached over plain HTTP, because the TLS section comes later in the document and is written as something you set up yourself with your own certificate and your own domain. The ports you are told to open are the panel port over TCP and the VPN port over both TCP and UDP, so the panel is exposed to the same network reachability as the VPN itself. Put those together and the default state of a fresh install is an internet-reachable administrative interface with universal credentials and no transport security. That is survivable on a private network and unsafe anywhere else, and the fix is not difficult: change the credential during setup and put the panel behind a reverse proxy with a certificate, which the project does document. But nothing in the default configuration resists a scanner.
The image build checks out a branch, so two builds of the same tag differ
The container build takes a build argument for which upstream revision to compile, and its default value is the name of a branch rather than a version. The build clones the upstream source, checks out whatever that argument names, and compiles it. So the contents of your image are a function of when you built it, not of what you asked for, unless you override the argument with a specific revision. The same pattern appears at the network level: the build installs a toolchain by piping a remote script into a shell, with a protocol and TLS floor pinned, and then fetches a second project from another forge entirely to build the panel. That second project is cloned and its dependencies installed with the package registry switched to a regional mirror mid-build. Between the unpinned revision and the third-party mirrors, an image built today and an image built next month from the same tag are not the same artefact, and neither is reproducible from the repository alone.
The planet and moon files come from a patched world generator, not from the stock build
This is the actual mechanism of the project and it is worth stating plainly, because it is what distinguishes this from simply containerising the upstream product. The upstream build produces a network daemon. Separately, it produces a generator that emits the root server files describing your network. This repository replaces that generator: it copies its own version of the source file over the original, moves the original aside with a backup extension, and builds. The resulting binary is what creates your planet file and any moon files. The build also runs the daemon once briefly inside the image, waits, and then kills it, which is a way of making it initialise its own state so the generator has something to work from. So the trust question for anyone running this is not only what the container does, it is what a patched C++ source file does when it writes the files every client on your network will trust. You should read that patch. It is in the repository, under a patch directory, which is the right place for it.
The base image is old and the builder installs a toolchain larger than the project
Both stages of the build start from the same long-deployed Alpine release, which by now is far past the point where you would start a new image. On top of that base the builder stage installs a package set that reads as a complete development environment: a compiler collection, build tools, a JavaScript runtime and its native build tooling, Python, Go, OpenSSL headers, and a Rust toolchain installed from the network at build time. That is a lot of surface for what the project produces, and it exists because the upstream source has to be compiled rather than downloaded. The runtime stage is the same base with the daemon, the panel and the generator, so the shipped image is smaller than the build stage but still carries a compiler collection. Nothing in the file pins the base to a digest, so the same build tag resolves to whatever that tag points at on the registry's mirror. For a component whose job is to be the root of trust for a virtual network, the runtime base is worth choosing deliberately rather than inheriting.
There is no licence file, and the field for one is empty
The repository's top level is short: a readme in two languages, a container build file, two shell scripts, a patch directory, an assets directory and the automation directory. There is no licence file among them, and the repository's own metadata records nothing for one either, showing the value as unknown rather than a standard identifier. For most projects this is an oversight. For this one it is a specific problem, because the project distributes patched upstream source and builds an artefact whose whole purpose is to be trusted by every client on a network. You cannot tell from the repository whether you may modify it, redistribute the image, or run it commercially. The two shell scripts and the patch are the interesting parts from a legal standpoint and they are exactly the parts with no stated terms. Resolve this before deploying, and treat it as a blocker for anything beyond personal use.
Mobile clients need workarounds on both major platforms
The client configuration section covers six platforms and two need a workaround that tells you something about the design. The desktop procedure ends with a peer listing showing two roles:
fcbaeb9b6c 1.8.7  PLANET    52 DIRECT 16       8994     1.1.1.1/9993
fe92971aad 1.8.7  LEAF      14 DIRECT -1       4150     2.2.2.2/9993
Both connections read as direct, which is the state the whole project exists to produce. For desktop systems the procedure is consistent: find the daemon's data directory, replace the planet file in it, restart the service, join the network, approve the device in the panel, then check the peer list. On one router platform that means creating a symbolic link from the configuration directory to the daemon's expected data directory before it will look in the right place. On phones, the story changes. The Android section does not describe a procedure at all, it recommends an unofficial third-party client, because the official one will not let you replace the planet file. The iOS section offers two options, both indirect: a jailbroken device with the planet file replaced, or reaching the network through a different VPN tool entirely. So the population this project serves best is desktop and server users, and the two largest mobile platforms are effectively unsupported by the design.
The commercial service is described before the tutorial
The document opens with a hosted offering before it explains what the software does. A three-day trial, an annual price, a bandwidth figure, a monthly traffic allowance with peer-to-peer traffic exempt and a per-increment charge beyond it, a named datacenter, and a contact handle. A second listing points at a regional container provider's marketplace entry. After that come several chat groups, a messaging account, and only then the explanation of what a planet server is. The placement is a business decision, not a technical one, and it does not make the tutorial worse. But it is worth separating when you evaluate the project: the self-hosted path and the paid path share a name and a brand, the self-hosted path is the part under your control, and the paid path is what the document is steering you toward first. The last release tag in the history is from 2024 while the branch has been committed to more recently, so the tutorial describes something newer than anything tagged.
Editorial conclusion
This project suits someone who needs to remove a dependency on the public root server for a virtual network and is comfortable running a patched build they have read. Four things to check before you deploy it. Change the panel credential and put TLS in front of it, since the documented default is universal and the default transport is plain HTTP on an internet-reachable port. Read the patched generator source, because that file writes the planet data every client on your network will trust. Pin the build, because the image checks out a moving branch and configures third-party mirrors, so two builds of the same tag differ. And resolve the licence, which is absent from the repository entirely.
Frequently asked questions
What does docker-zerotier-planet do?
It builds a ZeroTier root server inside a container so you can run your own planet, and optionally moon, files instead of relying on the public ones. The repository compiles the upstream daemon from source, replaces its world generator with a patched version so it produces your files, adds a web management panel, and produces images for both AMD64 and ARM64.
What are the default credentials for the management panel?
The tutorial documents a fixed default username and password for the panel and tells you to log in and create a network straight away. Change them during setup. The panel is reached over plain HTTP on its own port unless you put a reverse proxy with a certificate in front of it, which the project documents as a separate later step.
Which ports does docker-zerotier-planet need open?
Two, both documented as adjustable: the management panel over TCP and the VPN port over both TCP and UDP. You also need a server with a public address, plus Git and Docker installed locally. The document recommends a reasonably current Linux distribution and lists a few.
Can I use docker-zerotier-planet on Android or iOS?
Not with the official mobile clients. The Android section recommends an unofficial third-party client, because the official one does not allow the planet file to be replaced. The iOS section offers only two indirect routes, a jailbroken device with the file replaced, or reaching the network through a different VPN tool. Desktop and server systems have full documented procedures.
Is docker-zerotier-planet licensed?
The repository has no licence file at the top level and its own metadata records the licence as unknown rather than naming a standard one. For a project that compiles patched upstream source and produces an artefact that clients trust, resolve the terms before deploying it anywhere beyond personal use.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/xubiaolin-docker-zerotier-planet)Star history chart for your README
[](https://hysenlabs.com/projects/xubiaolin-docker-zerotier-planet)Was this useful?