Spark: changing the salt regenerates every client, and nothing updates itself
Spark is a web-based, cross-platform and full-featured Remote Administration Tool (RAT) written in Go that lets you control all your devices anywhere.
At a glance
- What is it?
- A browser based remote administration tool in Go, made of a client, a server and a React front end whose build output is embedded into the binary. For operators managing devices they are authorized to manage, and worth reading the configuration and update model before deploying it anywhere else.
- Who is it for?
- Spark fits one job: administering devices you already own or are authorized to administer, from a browser, with no third party server in the path. Nothing in this article covers using it on hardware you do not control, and the project's own disclaimer restricts it to educational use and prohibits illegal usage.
- Can I use it commercially?
- Yes. BSD-2-Clause is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Activity is slowing. The repository last received commits 8 months ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
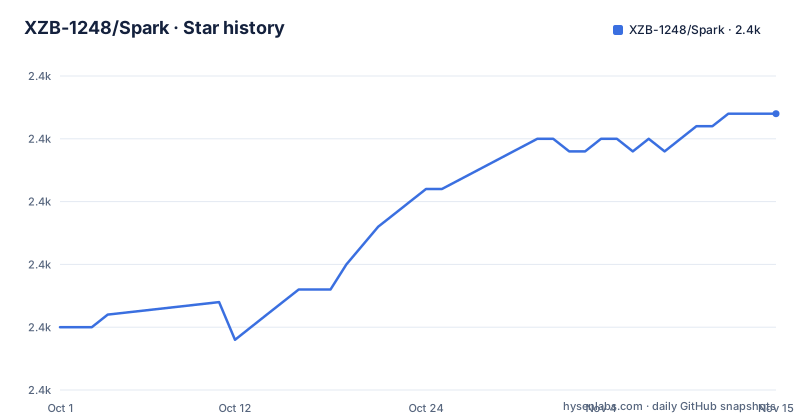
Star history
- XZB-1248/Spark2,412 ★ · +17
| Repository | 2026-10-01 | 2026-11-15 |
|---|---|---|
| XZB-1248/Spark | 2.4k | 2.4k |
17 Stars in the last 45 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
No auto-update means you distribute client fixes yourself
Three properties are claimed at the top of the README and the second one has a direct operational cost. Spark states that it collects no user information, that the server will not update itself, and that clients communicate exclusively with your server. That last property is the reason there is nothing else in the path: no vendor account, no relay, no callback service. The middle claim is what has to be planned around. A client binary installed on a fleet keeps running the code it was built with, so a server side fix, a protocol change or a patched dependency reaches the machines only when you rebuild and redistribute the client yourself. There is no update channel in the feature table and no version negotiation described anywhere, which means the fleet is as current as your last distribution run.
Changing the salt regenerates every client
The configuration is one JSON file that has to sit in the same directory as the executable:
{
    "listen": ":8000",
    "salt": "123456abcdef123456",
    "auth": {
        "username": "password"
    },
    "log": {
        "level": "info",
        "path": "./logs",
        "days": 7
    }
}
Two of those fields matter more than the rest. The salt is required, capped at 24 characters, and the README states plainly that after modification all clients need to be regenerated. So the salt is not a server secret that can be rotated quietly; it is embedded in every generated client, and rotating it is a rebuild of the entire fleet. That also makes it the value that binds a client to one server. Authentication is optional and separate: an auth object takes a username and a password, hashed passwords are recommended in the form $algorithm$hashed-password, and the listed algorithms are sha256, sha512 and bcrypt. Left unset, the web interface at the listen address has no credential check in front of it.
Four Linux gaps and two macOS gaps in the platform table
The feature table is seventeen rows by three systems, and it is mostly uniform until the bottom. Every row through remote terminal, including the process manager, kill process, network traffic, file explorer, file transfer, file editor, delete file, code highlighting, desktop monitor, screenshot and OS info, is marked available on Windows, Linux and macOS. The power rows diverge. Log Off and Sleep are marked unavailable on Linux. Hibernate and Lock Screen are marked unavailable on both Linux and macOS, so they exist on Windows only. Six rows are marked with an asterisk, and the note under the table says functions marked that way may require administrator or root privileges. The asterisk is a privilege warning rather than a portability one, so a Linux deployment of those six is a root deployment.
The newest release is from February 2023 and the last commit from March 2026
The release list holds three tags: v0.1.9 dated 2022-10-21, v0.2.0 dated 2022-11-01 and v0.2.1 dated 2023-02-01. The last recorded push is dated 2026-03-16. Those two dates are far enough apart to be worth stating plainly rather than characterising: work has continued to land on the branch since the last tag, and nothing in the tag list tells you what that work contains, since the changelog and the API documents are the only other sources and both live in the repository rather than on a release page. There are no prebuilt release notes per version to compare against, which is the practical reason to read CHANGELOG.md before assuming a tagged binary matches the branch you cloned.
The Go module is named Spark and declares go 1.18
The module line in go.mod is module Spark, a bare name rather than a repository path, and the language directive is go 1.18. The direct requirements mix current-looking and pinned-old entries: gin at v1.7.7, gorilla/websocket at v1.5.0, imroc/req/v3 at v3.8.2, gopsutil/v3 at v3.22.2, statik at v0.1.7, a June 2020 pseudo-version for golang.org/x/crypto, and two dependencies pinned to 2021 commits, kbinani/screenshot and lxn/win. The README's dependency list names six back-end projects and omits several that go.mod requires directly, including creack/pty for the terminal, denisbrodbeck/machineid, json-iterator, kataras/golog and kirides/go-d3d. The x/crypto pin is the one to look at first.
The web build is embedded into the server binary
There is no static asset directory to deploy, because the front end is compiled into the executable. The documented install route is to download the executable from the releases page, put the configuration file beside it, run it and open the web interface at http://IP:Port. Building from source starts with:
# Clone the repository
git clone https://github.com/XZB-1248/Spark
cd ./Spark

# Build the front-end
cd ./web
npm install
npm run build-prod
The static assets are then folded into the executable with statik, using statik -m -src="./web/dist" -f -dest="./server/embed" -p web -ns web. Only after that are the two binaries produced, by running ./scripts/build.client.sh into a ./built directory and ./scripts/build.server.sh into a ./releases directory, with go mod tidy and go mod download in between. So one build produces two artifacts from three sources, the Go server, the Go client and a React front end, and the client is the one you then have to place on every machine.
Three components, and extra C compilers off Windows and Linux
The project is split into a client, a server and a front end, which is why there are two build scripts and two binary outputs. Portability beyond Windows and Linux is not automatic: the README says additional C compilers may be required, and gives Android as the example, pointing at the Android NDK. The front end is React with Ant Design, axios, xterm.js for the terminal view and crypto-js for the client side cryptography, which lines up with the salt being something the client has to know. The back end is Go with gin as the HTTP layer, imroc/req for outbound calls, gopsutil for system information, gorilla/websocket for the live channel and kbinani/screenshot for the screenshot row in the table. Third-party license texts live in a licenses/ directory beside them.
Vulnerability reports and custom work both go to one inbox
The disclosure policy is unusual enough to state plainly: if you find a security vulnerability, do not open an issue, contact the author immediately by email at the address in the README. That keeps a private channel, and it also means there is no public tracker for the report. The same address is the route for custom features, where the README says to get in touch if you need some features customized, so anything beyond the seventeen rows in the table is arranged by private request rather than by a pull request. The documented contribution path is otherwise conventional: issues for bugs and enhancement ideas, forks and pull requests for code, with CONTRIBUTING.md holding the code of conduct. A Chinese README and Chinese API document sit beside the English ones.
Editorial conclusion
Spark fits one job: administering devices you already own or are authorized to administer, from a browser, with no third party server in the path. Nothing in this article covers using it on hardware you do not control, and the project's own disclaimer restricts it to educational use and prohibits illegal usage. Before deploying it, check four things. The client never auto-updates, so a fix on the server does nothing for an installed client until you redistribute the binary yourself. Changing the salt regenerates every client, which makes the salt a fleet-wide operation rather than a per host setting. The Go dependency set is pinned well behind current versions, including a 2020 cryptography pseudo-version, so treat the surface area as needing your own review. And the last recorded commit is dated 2026-03-16, with the newest listed release from 2023-02-01.
Frequently asked questions
What is XZB-1248/Spark?
A free, open source, web based cross-platform remote administration tool written in Go, made of a client, a server and a React front end, distributed under the BSD-2 license. The README restricts it to educational purposes and prohibits illegal usage.
What does the Spark config.json require?
A listen address in IP:Port form and a salt of at most 24 characters. The auth and log blocks are optional, and hashed passwords are recommended in the form $algorithm$hashed-password using sha256, sha512 or bcrypt.
What happens if I change the salt in Spark?
All clients need to be regenerated. The salt is capped at 24 characters and is what binds a generated client to one server, so rotating it is a fleet-wide operation.
Which Spark functions are not available on Linux?
Log Off, Sleep, Hibernate and Lock Screen are marked unsupported on Linux, and Hibernate and Lock Screen are also unsupported on macOS. The asterisked functions, which include shutdown and reboot, may require administrator or root privileges.
How do clients get updates in Spark?
They do not automatically. The README states that the server will not update itself, and no update channel is listed among the features, so client binaries stay as they were built until you redistribute them yourself.
How do I report a security issue in Spark?
The README says not to open an issue and to email the author immediately instead. Requests for custom features use the same email route, while ordinary bugs and enhancements go through issues and code through pull requests.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/xzb-1248-spark)Star history chart for your README
[](https://hysenlabs.com/projects/xzb-1248-spark)Was this useful?