hayabusa: the readme stopped documenting the tool, so the project kept its own history in two files
Hayabusa (falcon) is a Sigma-based threat hunting and fast forensics timeline generator for Windows event logs.
At a glance
- What is it?
- A Rust tool that consolidates Windows event logs into one timeline and hunts across them with Sigma rules, AGPL-licensed, with the rules under a separate licence. Its manifest documents a real TLS failure, parses event logs through an in-house fork pinned to a commit, and carries a readme that is now only a list of links.
- Who is it for?
- Use it for what it was built for, correlating Windows event records from one host or a fleet into a single timeline you can load into a timeline viewer, and keep the defensive frame in mind: this is a read and analyse tool, and nothing in it needs to touch the hosts it reads beyond pulling logs. Three things to check.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 5 days ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
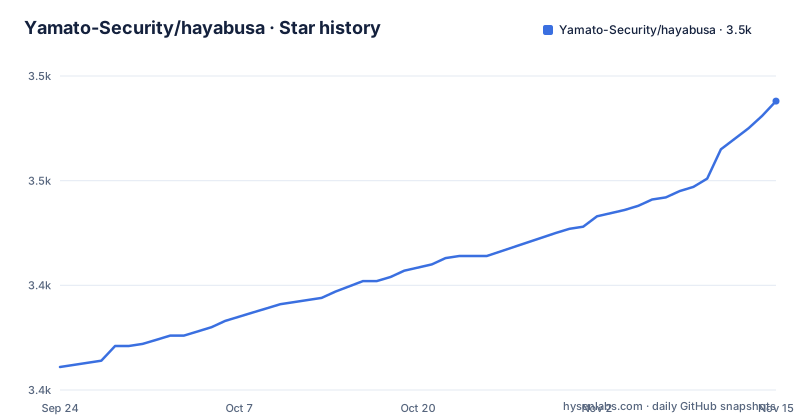
- Yamato-Security/hayabusa3,488 ★ · +127
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| Yamato-Security/hayabusa | 3.4k | 3.5k |
127 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The readme is a table of links, and the old ones are files in the tree
The current readme contains no commands. It states that all documentation now lives on a dedicated searchable site, and gives a five row table linking a getting started page, a command reference, a timeline output page, a rules page and an importing page, then links the releases for signed binaries. What it also does is keep the previous version rather than delete it, offering two preserved files, an English one and a Japanese one, described as unchanged. That is an unusual and defensible arrangement: a project that rewrites its documentation into a site keeps the old text in the repository so that existing citations, blog links and search results still resolve to something real. It also means the repository contains three readmes describing the same tool at three levels of detail, and only the two with OLD in the name are complete.
The event log parser is an in-house fork pinned to a commit hash
For a tool whose entire job is reading Windows event logs, the parser is the dependency that matters most, and it does not come from the ecosystem. It is required from a repository maintained by the same organisation, at a fixed commit hash rather than a version, with a feature flag for fast allocation enabled and an inline comment naming the upstream version and the date of the update. That is a deliberate choice with two consequences. The parser can carry fixes that upstream does not have, which for an event log format that Microsoft changes is the point. And an auditor reading the manifest sees a specific commit, so the build is reproducible, but that commit is not upstream and carries no independent review. Everything else in the manifest is a published crate.
A TLS failure is preserved as a comment above the fix
One dependency entry carries the most useful comment in the file, recording a failure and its repair:
# Enable the vendored-OpenSSL HTTPS/TLS backend for libgit2. The wildcard
# `0.*` resolved to a build of libgit2 with no TLS transport, so `update-rules`
# failed with `class=Ssl (16) - there is no TLS stream available`. The project
# already vendors OpenSSL (see `openssl` below), so this just links libgit2's
# TLS transport against it.
git2 = { version = "0.21", features = ["https", "vendored-openssl"] }
Three things are worth reading out of it. A wildcard version resolved to a build with no TLS transport, which is the exact failure mode an unpinned dependency produces. The rule download path was the thing that broke, so the tool that fetches detection rules could not reach the network. And the fix was not to pin a version but to switch on a feature that links the vendored TLS the project already ships. The error text is still in the repository, which is the right place for it.
Eight dependencies carry a wildcard version, and two allocators
The manifest mixes careful and careless pinning in one list. Numeric libraries are bounded, with byte sizes, hashes, the CLI parser, the CSV writer, the table renderer and the logger all on major version ranges. The regex engine used for rule matching is declared with a single star, and so are a concurrent map, the interactive prompt library, the progress bar, a type inference helper, an iteration helper, and both allocators. Two allocator crates appear side by side, a safe wrapper and its raw system bindings, the latter with an extended feature set. For a project that parses binary log files written by other software, a wildcard on the pattern matching engine is the least convenient line in the file, and the manifest does not attempt to argue otherwise.
The published crate ships source and no rules
The packaging list is short and deliberate:
include = ["src/**/*", "build.rs", "LICENSE.txt", "README.md", "CHANGELOG.md"]Five entries, and none of them is a detection rule, a default configuration, a test corpus, documentation, or the website. The tree holds all of those, including a rules entry, a config directory, test files, a documentation folder, artwork and screenshots, and there is a submodule file as well. So the crate published to the registry is the engine without its rule set, which is a defensible way to keep a binary distribution small and to let operators bring their own rules, but it means anyone installing from the registry rather than from a release binary has to supply the detection content separately. The Windows executable metadata is generated at build time instead, from a build script and a resource block naming the product, the company and the original file name.
Code and detection rules carry different licences
The licence paragraph splits the project in two. The tool itself is released under the GNU Affero General Public License version 3, which for a network service means a modified instance offered to users has to carry its source. The detection rules are released separately under the detection rule licence version 1.1 published by the Sigma project, and the file names that upstream repository as where the terms live. That split is the norm for a project consuming rules from a shared rule set, and it means the obligations on the code and on the content differ. The readme also claims to be the only open source tool with full Sigma support including version 2 correlation rules, a superlative with nothing behind it in the file. Whether that is true is a question for the reader to answer by looking at the alternatives.
Findings can leave the host, and addresses can be resolved to countries
The example environment file has two variables and both are empty:
WEBHOOK_URL=
CHANNEL=#
A webhook address and a channel reference, which together mean the tool can post a detection somewhere outside the machine when a rule fires. The defaults are inert, an empty address and a placeholder channel, so nothing leaves unless an operator fills the first line in, and that is the right way round. The other data-handling fact is in the dependency list rather than the documentation: a reader for the MaxMind GeoIP database format, which means the tool can turn addresses in the logs into geography. For a forensics workflow that is a normal enrichment step and also one worth knowing about before you share a resulting timeline, because the enrichment does not stay local either.
Releases are named after conferences and seasons
The version numbers follow a schedule, and the release names are not semantic. The newest is 4.1.0, named for the Suzumushi release, which is the Japanese name for the bell cricket that marks high summer, published in September 2026. Before it, 4.0.0 was named for the Black Hat Arsenal release in the United States, in August 2026, and 3.10.0 was named for a happy independence day release on 4 July 2026. The banner above the documentation carries a matching list of conference appearances going back to a 2022 arsenal talk in Asia, through a forensics summit, several Japanese conferences, and a 2026 arsenal slot. So the release titles double as a publication trail, which makes them pleasant to read and useless for deciding whether a version contains a particular fix.
Editorial conclusion
Use it for what it was built for, correlating Windows event records from one host or a fleet into a single timeline you can load into a timeline viewer, and keep the defensive frame in mind: this is a read and analyse tool, and nothing in it needs to touch the hosts it reads beyond pulling logs. Three things to check. Documentation now lives off the repository, so pin the version you read and expect the command surface to change between releases. The dependency manifest pins several crates with a wildcard version and pulls its event log parser from a fork at a fixed commit, which for a forensic tool is worth reviewing before you build it for an investigation. And detections can be posted to a webhook you configure, which means findings leave the machine unless you leave that variable empty.
Frequently asked questions
how to use hayabusa dfir
The repository no longer documents usage. It states that all documentation moved to a dedicated documentation site and links a getting started page, a command reference, a timeline output page, a rules page and an importing page. The previous single-page readme is still in the repository as a preserved file, in English and in Japanese, unchanged, so the commands can be read there.
how to use hayabusa forensics
It consolidates Windows event logs from one host or thousands of systems into a single CSV, JSON or JSONL timeline, ready for LibreOffice, Timeline Explorer, the Elastic Stack or Timesketch. It runs multi-threaded for speed, works live on one system or offline on collected logs, and hunts with Sigma rules including version 2 correlation rules.
What licence applies to Hayabusa and its detection rules?
Two licences. The tool is released under the GNU Affero General Public License version 3, with the terms in a licence file at the root, and the detection rules are released separately under the detection rule licence version 1.1 maintained by the Sigma project, which the readme links to that project's repository.
How do I get Hayabusa binaries?
Signed binaries are published on the releases page for each release, and the getting started page covers live response packages and building from source. The manifest pins a minimum Rust version at the patch level and uses the 2024 edition, so a source build needs a current toolchain, and the crate's published file list contains only source, the build script, the licence and two readme files.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/yamato-security-hayabusa)Star history chart for your README
[](https://hysenlabs.com/projects/yamato-security-hayabusa)Was this useful?