Yarn 1.x is a frozen hotfix line
GitHub describes it as The 1.x line is frozen - features and bugfixes now happen on https://github.com/yarnpkg/berry. The repository metadata lists JavaScript as its primary language. The metadata lists the NOASSERTION license. This article stays within the project description and details documented in the GitHub repository README.
At a glance
- What is it?
- The yarnpkg/yarn repository holds the frozen 1.x line: features and bugfixes moved to yarnpkg/berry, and this branch takes the occasional hotfix to make leaving easier. Its manifest still reads 1.23.0-0 while the newest release is 1.22.22.
- Who is it for?
- Adopt Yarn 1.x only if you are inheriting a repository that already has a yarn.lock and a 1.x-based CI image, because migrating is more work than staying and the migration guide is where the effort goes. Do not start a new project on 1.x, and do not read this branch as evidence of how Yarn works today, since the code here is kept for historical purposes.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Activity is slowing. The repository last received commits 6 months ago.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
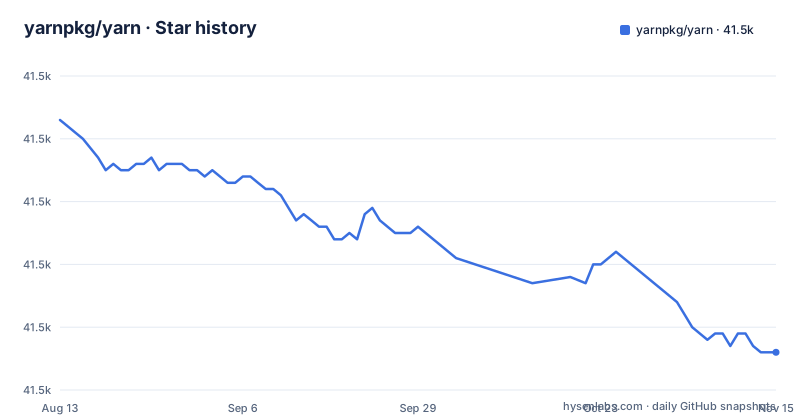
- yarnpkg/yarn41,456 ★ · -37
| Repository | 2026-08-13 | 2026-11-15 |
|---|---|---|
| yarnpkg/yarn | 41.5k | 41.5k |
-37 Stars in the last 94 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The branch exists to make leaving it easier
The first thing the README says is that this repository holds the sources for Yarn 1.x, that the latest version at the time of writing was 1.22, and that new releases are tracked on the berry repository, at 3.2.3 at that point, with a next major in progress. The stated purpose of keeping the branch is historical reference plus the occasional hotfix published to ease the migration path.
Contributing is closed the same way. The 1.x codebase is described as fairly old and accepting security fixes only, with new features and bugfixes directed to berry. The README goes further than that and recommends migrating outright, on the grounds that the later releases have been maintained longer than 1.x.
The dates agree. The last push was on 2026-05-12 and the newest release is v1.22.22 from 2024-03-09, with v1.22.21 and v1.22.20 both published on 2023-11-14. So the branch still takes commits, but a commit is a hotfix, not development.
The manifest reads 1.23.0-0 and no 1.23 was ever tagged
The version skew inside the repository is easy to miss and worth knowing before you file an issue against the wrong tree. The root package.json declares:
  "name": "yarn",
  "installationMethod": "unknown",
  "version": "1.23.0-0",
  "license": "BSD-2-Clause",
  "preferGlobal": true
A 1.23.0-0 is a prerelease marker, and there is no 1.23 release in the tag list. The highest published version is 1.22.22. So the code on master is a 1.23 that never shipped, and a `yarn --version` on a machine installed from npm will not match the version string in this manifest.
The same file also resolves a licensing question the repository metadata leaves open. The project's license field does not identify a license, while the manifest declares BSD-2-Clause. Two different files, two different levels of certainty, and the manifest is the one npm reads.
nodeLinker is the switch that decides what lands on disk
The migration guidance does not ask you to change your habits so much as to pick a layout. The `nodeLinker` setting chooses between node_modules like npm, symlinks like pnpm, and manifest files via Yarn PnP. One setting, three different on-disk arrangements.
Each arrangement has a different way of failing, which is why the choice cannot be deferred. node_modules duplicates packages and works with any tool that assumes a filesystem tree. A symlink layout breaks anything that walks the tree expecting real directories, and on Windows it depends on whether the account is allowed to create links. PnP removes node_modules entirely and resolves from generated manifests, which is fast and small but requires every tool in the chain to understand the resolution model.
The 1.x branch has no `nodeLinker` setting of its own. That option lives in the current documentation, which is the first sign that this repository is not where the current behaviour is defined.
There is no install command here, and there are two documentation sites
The installation section contains no command. It sends you to the Installation Guide on the project website, and the usage section sends you to a Usage Guide on the same site. The 1.x homepage is a different address, classic.yarnpkg.com, from the yarnpkg.com pages the README links to.
That split is the trap for anyone new to the project. classic.yarnpkg.com documents the line whose sources live in this repository. The README's Installation Guide and Usage Guide links point at yarnpkg.com rather than classic.yarnpkg.com, so check which line a page describes before copying a command from it.
The practical rule for a 1.x project is that the version has to be pinned explicitly, everywhere, because nothing in the documentation is going to stop a fresh install from landing on a different major.
Flat Mode trades npm's nesting for a single resolved version
Flat Mode resolves mismatched versions of dependencies to a single version to avoid creating duplicates.
The benefit is a tree without duplicates, which matters most for a project with a wide dependency tree.
The gap is that the documentation does not say which side of a version conflict gets the version it asked for. Two libraries pinned to incompatible majors of the same dependency is exactly the case where that matters, so test it before you trust Flat Mode with a tree that has one.
The checksums live in yarn.lock, so a rewritten lockfile loses them
The security claim is specific: Yarn uses checksums to verify the integrity of every installed package before its code is executed. The dependency list carries `ssri` and `hash-for-dep` alongside the tar handling packages, which is the integrity machinery sitting under that sentence.
The README does not say where the checksums are stored, so confirm that in the Yarn 1.x documentation before relying on the guarantee.
Two other guarantees sit in the same family. Offline Mode reuses packages already in the cache without a network connection, which makes air-gapped builds possible and makes a stale cache a silent source of old versions. Network Resilience means one failed request does not fail the install and requests are retried, so a flaky network slows an install instead of breaking it.
Babel 6, Flow types and `request` date the tree you would patch
The build stack is the fastest way to date this codebase. The root has a .babelrc, .flowconfig and a flow-typed/ directory, and the manifest pins babel-runtime at ^6.26.0, babel-core at ^6.26.0 and babel-loader at ^6.2.5. Alongside them sit commander at ^2.9.0, chalk at ^2.1.0, inquirer at ^6.2.0, mkdirp at ^0.5.1 and request at ^2.87.0, which is a dependency line most projects moved off years ago.
There is a test story here too. __tests__/ and end_to_end_tests/ sit beside four separate CI configurations, CircleCI, AppVeyor, Azure Pipelines and a Jenkins groovy job, plus a Dockerfile.dev. Four CI systems for a frozen branch is what happens when a project spans years without consolidating.
If you need a patch in 1.x, you are patching this tree, and this tree's own toolchain is what has to build and test it.
The npm name was donated, which matters if you fork and publish
Read the LICENSE file rather than the badge, and note that the manifest's BSD-2-Clause BSD-2-Clause is permissive enough for commercial use with a notice retained.
There is a second, smaller rights question in the credits. The npm package name `yarn` was donated by Sam Holmes, and the README thanks him for it. That is not a licence term, but it is the reason the name is not simply the project's to hand out, so a fork that publishes under the same package name is a different proposition from a fork that publishes under its own.
SECURITY.md sits at the root next to CODE_OF_CONDUCT.md and CONTRIBUTING.md. On a branch that accepts security fixes only, that file is the route to report a problem, and patching locally is the wrong first move.
Editorial conclusion
Adopt Yarn 1.x only if you are inheriting a repository that already has a yarn.lock and a 1.x-based CI image, because migrating is more work than staying and the migration guide is where the effort goes. Do not start a new project on 1.x, and do not read this branch as evidence of how Yarn works today, since the code here is kept for historical purposes. Verify two things: the exact 1.x version your lockfile and CI image expect and which of the two documentation sites, classic.yarnpkg.com or yarnpkg.com, the instructions you are following actually describe.
Frequently asked questions
What is yarn npm?
Yarn is a package manager for JavaScript projects and it is published to npm under the package name `yarn`, which the README credits to Sam Holmes for donating. npm is both the registry Yarn installs from and the CLI it is compared against, and it is named in the project's list of prior art alongside Bundler and Cargo.
How do I download yarn on my Mac?
The repository contains no install command and points to the Installation Guide at https://yarnpkg.com/en/docs/install. The larger decision is which line you install, because this branch is 1.x with v1.22.22 as its newest release, while current releases at 3.2.3 are tracked on the separate berry repository.
Is yarn still faster than npm?
The documentation states no timing comparison with npm. It describes caching every downloaded package and doing almost everything concurrently, and its stated guarantees are a lockfile with a deterministic install algorithm and checksums verified before any package's code runs, so treat the speed claim as a design description rather than a measurement.
How to install npm yarn?
Two documentation sites describe two different lines. This repository's homepage is https://classic.yarnpkg.com for 1.x, while the installation guide it links to sits on https://yarnpkg.com. The 1.x branch accepts security fixes only, and the README recommends migrating rather than installing it fresh.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/yarnpkg-yarn)Star history chart for your README
[](https://hysenlabs.com/projects/yarnpkg-yarn)Was this useful?