cpp-httplib states three limits before it lists a feature
A C++ header-only HTTP/HTTPS server and client library. [!NOTE] BoringSSL (best-effort): BoringSSL builds under CPPHTTPLIB_OPENSSL_SUPPORT and is exercised by CI against current upstream.
At a glance
- What is it?
- cpp-httplib is a single-header C++ HTTP and HTTPS server and client: you include one file and call listen. The file is unusually upfront about its boundaries, stating that it uses blocking socket I/O, that only HTTP/1.1 is implemented, and that 32-bit platforms are unsupported with no security review, plus three TLS backends.
- Who is it for?
- cpp-httplib fits a tool that needs an HTTP or HTTPS client or server inside a C++ program with no dependency tree, and that can live with blocking calls. It does not fit anything needing HTTP/2, non-blocking I/O or a supported 32-bit target, because the file rules out all three before it lists a feature.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly C++, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
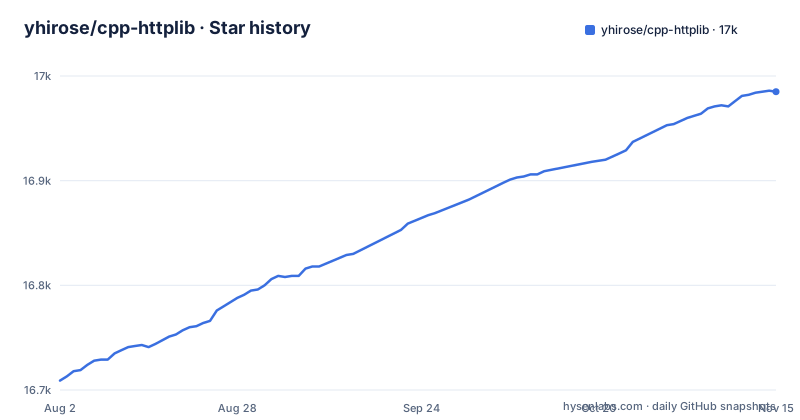
- yhirose/cpp-httplib16,985 ★ · +276
| Repository | 2026-08-02 | 2026-11-15 |
|---|---|---|
| yhirose/cpp-httplib | 16.7k | 17k |
276 Stars in the last 105 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Three of the first four paragraphs are about what it will not do
Before a single feature is listed, the file sets three boundaries, and they are the most useful paragraphs in it. The first says the library uses blocking socket I/O, and that if you want a library with non-blocking I/O this is not the one you want. The second says only HTTP/1.1 is supported and that HTTP/2 and HTTP/3 are not implemented. The third is a warning about 32-bit platforms: they are not supported, the library may compile there, no security review has been conducted for a 32-bit environment, integer truncation and other platform-specific problems may exist, and security reports that affect only 32-bit will be closed without action because the maintainer has no access to such environments. The same warning adds that continuous integration does basic compile checks only, not functional or security testing. If any of those three boundaries is one your project cannot accept, the answer is in the first screen and it is no.
One header today, and a script to split it when that stops working
The distribution is a single header file that you include, and the file's own claim is that setup is extremely easy because of it. The repository is organised around the consequences of that choice. There is a script for splitting the header into modules, a script for generating them, and a test directory with its own makefiles, and the command file in the repository root has a build target whose entire job is to run the split test once per TLS backend, one for each of the three. So the project treats the monolithic header as the default and the split layout as something it verifies rather than something it hopes works. That matters for adoption, because a single header that gets recompiled into every translation unit is the usual reason a C++ project abandons a library like this, and here the escape hatch is in the repository and covered by the tests.
The TLS backend is a compile-time define with a version floor each
Transport security is handled through an abstraction layer over three backends, and the table is the whole contract. OpenSSL is enabled by a define and needs version 3.0 or later, with its two libraries. Mbed TLS is another define, supports the 2, 3 and 4 series with auto-detection, and the table warns that version 4 renames one of its libraries. wolfSSL is the third, supports its 5 series, and the table notes it must be built with a specific option. The selection is one line before the include:
// Use either OpenSSL, Mbed TLS, or wolfSSL
#define CPPHTTPLIB_OPENSSL_SUPPORT   // or CPPHTTPLIB_MBEDTLS_SUPPORT or CPPHTTPLIB_WOLFSSL_SUPPORT
#include "path/to/httplib.h"

// Server
httplib::SSLServer svr("./cert.pem", "./key.pem");
So which TLS stack your binary uses is a build decision, not a runtime one, and two of the three carry a naming or build-option surprise you will meet the first time you compile against them.
BoringSSL builds, and it verifies hostnames from the SAN list only
One backend is documented separately and honestly. BoringSSL builds under the same define as OpenSSL and is exercised by continuous integration against the current upstream, but because it does not guarantee API stability the support is described as best-effort, with breakage expected to land occasionally. One known difference from OpenSSL is called out, and a separate note covers hostname verification on every backend. Its public headers require a newer language level than the library's own baseline, so your build has to move. And hostname verification, on every backend, is based on the subject alternative name list alone, with no fallback to the certificate's common name. The second one is the finding to act on. A certificate that carries only a common name will be rejected, and certificates of that shape are still in circulation, so if your internal endpoints use them, this is the paragraph that tells you before you find out in production.
The trust store you loaded from a file cannot be listed back
There is a small note about the wolfSSL backend that deserves more attention than it gets. The functions that return the loaded certificate authorities and their names only reflect certificates loaded through the store-loading call. Certificates added by pointing at a certificate path, or the system certificates, are not enumerable. So the API can tell you which roots came from the store you explicitly loaded and is silent about the ones that came from the system, which on a normal machine is most of your trust. That breaks any audit that reports what a client trusts, and it means a diagnostic that prints the trust store will under-report rather than fail. The file also documents a custom verification callback, which receives a context carrying the subject common name, the issuer, the depth and whether the certificate pre-verified.
Certificates can be passed in memory, for all three roles
The file notes that CA certificates are loaded when the client makes its first connection. Changing set_ca_cert_path() or enable_system_ca() after that has no effect, so make the settings before the first request, or use a new client; set_ca_cert_store() and load_ca_cert_store() take effect at once, and WebSocketClient works the same way.
The container is a stripped static binary on an empty base image
The Docker build in this repository is short and says something about how the author expects the library to be used. It compiles a single source file, docker/main.cc, with the compiler set to a recent language standard, statically linked and optimised, strips the result, and then puts that binary into an image with no base distribution at all, alongside one HTML file, exposing a port and passing the host, the port and a mount path as arguments. So the shipped image contains a binary and a file. The compose file builds it and mounts a directory of static content into the mount path. Paired with the test side, where every TLS backend has its own target and the tests run with a leak-sanitiser suppressions file, and there are separate targets for the fuzzer, a WebSocket heartbeat test, a thread pool test and a benchmark, the packaging and the testing are both aimed at the same thing: as little of this program as possible in the production path.
Editorial conclusion
cpp-httplib fits a tool that needs an HTTP or HTTPS client or server inside a C++ program with no dependency tree, and that can live with blocking calls. It does not fit anything needing HTTP/2, non-blocking I/O or a supported 32-bit target, because the file rules out all three before it lists a feature. Before you adopt it, decide which TLS backend you will compile against, since that is a define at compile time with its own version floor, and note that hostname verification is SAN-only on every backend, with no common-name fallback. Then plan certificate handling: CA certificates are loaded on the first connection, and on wolfSSL the trust-store enumeration functions cannot see certificates you loaded from a path. And if compile times become the problem, the project ships the script that splits the header and tests the split against every backend.
Frequently asked questions
What is cpp httplib?
It is a C++ HTTP and HTTPS server and client library distributed as a single header file that you include, with no dependencies to install unless you enable a TLS backend. It supports three TLS backends chosen at compile time, plus a stream API, server-sent events and WebSocket support, and the README describes it as cross platform.
how to install cpp httplib
There is nothing to install in the package manager sense: you download the single header and include it, and the file calls the setup extremely easy for that reason. You choose a TLS backend with a define before the include if you want transport security, and the repository also carries CMake, Meson and a command file if you would rather consume it as a build target.
how to use cpp httplib
For a server, construct one, register a handler per path, and call listen with a bind address and a port. For a client, construct one with a URL, call a verb such as Get, and check the returned result, which carries a status and a body. Server-sent events, WebSocket and a stream API each have their own example file in the example directory and their own document.
cpp httplib vs libcurl
The project makes no comparison. Its own shape is the difference: a single header you include, with TLS chosen by a define at compile time and no cpp-httplib library to build or link, where a system library is something you install and link against. Its limits are also stated, blocking socket I/O, HTTP/1.1 only, and no supported 32-bit target.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/yhirose-cpp-httplib)Star history chart for your README
[](https://hysenlabs.com/projects/yhirose-cpp-httplib)Was this useful?