WebCodex's workspace is at 0.5.0 and its newest release is 0.4.6
Give cloud AI agents a real development environment on your own machines.
At a glance
- What is it?
- yyjeqhc/webcodex gives a hosted AI client a development environment on your own machine by bridging the Model Context Protocol to a local server and runner. Its compose file is hardened in six specific ways, its installer is documented as unaccepted on real hardware, and its workspace version runs ahead of every tag.
- Who is it for?
- This suits someone who wants a hosted coding assistant to work on a repository that cannot leave the machine, and who already has that repository set up with its own toolchain. Three things to know first.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 22, 2026, and from our analysis. They are not legal advice.
Star history
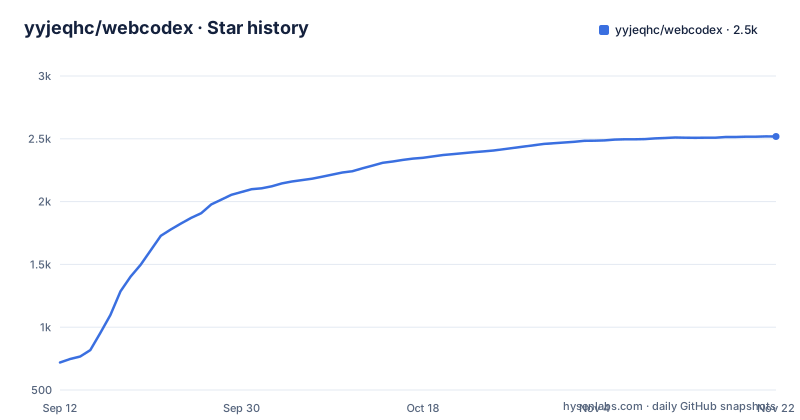
- yyjeqhc/webcodex2,518 ★ · +1,799
| Repository | 2026-09-12 | 2026-11-22 |
|---|---|---|
| yyjeqhc/webcodex | 719 | 2.5k |
1,799 Stars in the last 71 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The workspace version is ahead of every published tag
The manifest declares a workspace version of 0.5.0, and the newest published release is 0.4.6. So the source tree is a full minor version ahead of anything you can download, and the three most recent releases came out within two days, one of them on the day this branch was last pushed. That gap is normal for an active project but it changes how you read a version number: reporting 0.5.0 does not identify a release you can install, and a bug report against 0.4.6 and one against the current source are different things. The manifest also sets the licence, the edition and the dependency resolver once at the workspace level and has every crate inherit them, which is the tidy part; the untidy part is that the inherited version and the tags are tracked separately with nothing on the page reconciling them.
Six installer variants and none of them accepted on real hardware
The installer story is the part of the page that argues with itself most usefully. The unified workflow is described as under development, and the reader is pointed at a validation status document before choosing an artefact. Three platforms are targeted, a Windows installer, a macOS package and a Debian or Ubuntu package, each for two processor architectures, giving six variants. Then a sentence says the six still require native build and installation acceptance before release, and that real-machine installation, persistence across reboot, graphical behaviour and upgrades have not been accepted across all three platforms, with an explicit statement that the branch makes no claim of identical behaviour between them. So the branch defines the build pipeline and the download links still point at older release artefacts.
The compose file hardens six ways and expects a proxy in front
The server container is configured defensively in ways that are easy to read off the file. The root filesystem is marked read-only, with a small memory-backed temporary directory mounted writable. Every Linux capability is dropped and the no-new-privileges option is set. Two environment variables are declared as required, so the stack refuses to start rather than coming up without a token or without knowing its own public address:
environment:
  WEBCODEX_TOKEN: ${WEBCODEX_TOKEN:?set WEBCODEX_TOKEN in .env}
  WEBCODEX_ADDR: 0.0.0.0:8080
  WEBCODEX_PUBLIC_URL: ${WEBCODEX_PUBLIC_URL:?set WEBCODEX_PUBLIC_URL in .env}
The port mapping binds to the loopback interface by default, and the comment above it says only the existing reverse proxy on that host should be able to reach the service. A health check polls a health endpoint every fifteen seconds after a ten second grace period. The image tag is a moving one with an always-pull policy, which is a deliberate trade in the opposite direction from the hardening.
The image cannot see its own commit, so the caller passes it in
The container file contains a comment that explains a small design decision precisely. Git metadata is supplied as build arguments, a commit, a dirty flag and a build timestamp, because the version control directory is intentionally excluded from the build context. So a container build cannot discover what it was built from, and whoever builds it is responsible for passing those three values. Two other comments describe what is and is not in the image. The command line tool is included alongside the server so that pairing and administration can be run from inside the running container, and the component that runs jobs on a developer's machine is intentionally left out, which is the boundary between the machine holding the server and the machines holding the code.
Twenty crates, and the feature that is named experimental
The workspace lists twenty member crates and the names are the architecture. There are ones for the server and the command line, for the core and the environment, for a persistent shell and process control, for a runner and a registry of runners, for storage, for workflow sessions, and two contract crates that define what a tool is allowed to do. Then there are three capability crates whose names give the scope away: one for a language server, one for driving a computer, one for a browser. The default feature set is empty. One opt-in feature pulls in the code-mode crate with a specific JavaScript runtime and threads itself through both contract crates, and a second feature propagates across three others. Naming a feature experimental and gating it behind a default-off flag is the honest version of shipping it early.
The download directory is page source that is never deployed
One paragraph on the page is entirely about a directory that does not do what a download link implies. The directory holds static page source only. A workflow builds an artefact from the release manifest after a publication, and that artefact is not hosted or deployed by the workflow. So the visible surface is a page that was never published, and the actual files come from the releases list, which the same paragraph links to. It is a small detail in a way, and it is also the kind of thing that survives several releases because it breaks nobody: nobody clicks the link expecting an artefact and nobody notices that the page is missing.
Long-running work is answered with observability, not a queue
The capability list handles the hardest practical problem in agent tooling in one line: keep jobs observable rather than requiring one model turn to stay open indefinitely. The supporting sentence names what replaces the usual machinery: a runtime console, evidence attached to a workflow session, a jobs view, and Git and diff review, and it says this is done without a separate subsystem for accepting tasks and results. That is a design claim worth reading carefully, because a task queue with an acceptance step is what most agent platforms converged on, and the argument here is that an agent running commands in your own checkout does not need one because the checkout itself is the record. The temporary mode is the one-command sharing path for a single repository; the durable mode is a server on one machine and runners on each machine that owns code.
A dependency policy file at the root, and two example files
Two small things say how the project is policed rather than described. At the top level there is a workspace boundaries file, next to the manifest, which is a declaration of which crates are allowed to depend on which, enforced separately from the compiler's own rules. And the examples directory holds two files rather than a gallery: one project configuration in the tool's own format, and one plugin written in JavaScript that plugs in a native tool. That second file is the more revealing of the two. A Rust server that lets an external agent drive a local machine, and that supports plugins written in a scripting language, is extending its own authority by design, so the examples directory is where you should look first to see what that looks like in practice.
Editorial conclusion
This suits someone who wants a hosted coding assistant to work on a repository that cannot leave the machine, and who already has that repository set up with its own toolchain. Three things to know first. The workspace version is ahead of every published tag, so a version number in a bug report does not identify a release. The installer is described by its own documentation as under development, with six platform variants and none of them yet accepted on real hardware, so use the release artefacts rather than the unified package. And the container is hardened to the point where a reverse proxy in front is expected rather than optional, since the process runs with no capabilities and a read-only filesystem.
Frequently asked questions
What is yyjeqhc/webcodex?
It is an Apache-2.0 Rust project that gives a hosted AI assistant a real development environment on your own machines. An AI client connects to it over the Model Context Protocol or HTTPS, and it reaches the repository, its Git checkout and its compilers, tests and developer tools on the machine that owns them, so a project does not have to be copied into a hosted workspace.
How do I install WebCodex?
The unified installer is described as under development, and the page tells you to read a validation status document before choosing an artefact. For one computer you install the platform package on your workstation, which bundles the desktop app, the command line tool, the server and the runner; for several, you install it on the machine hosting the server and on each machine that owns repositories. Older release artefacts and the container path are documented separately as advanced options.
Is the WebCodex installer ready to use?
Not on its own terms. The branch defines installer targets for three platforms across two processor architectures, six variants in total, and the page says they still require native build and installation acceptance before release, with real-machine installation, persistence across reboot, graphical behaviour and upgrades not yet accepted across all three platforms, and no claim of identical behaviour between them.
How is the WebCodex server container hardened?
The root filesystem is read-only with a small memory-backed temporary directory, all Linux capabilities are dropped, the no-new-privileges option is set, two environment variables are declared as required so the stack refuses to start without them, and the published port binds to the loopback interface by default with a comment saying only the host's reverse proxy should reach it. A health endpoint is polled every fifteen seconds.
What is the current WebCodex version?
The workspace manifest declares 0.5.0 while the newest published release is 0.4.6, with three releases published within two days of the most recent push. The three most recent tags are v0.4.6, v0.4.5 and v0.4.4, so the source tree runs a full minor version ahead of anything you can download.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/yyjeqhc-webcodex)Star history chart for your README
[](https://hysenlabs.com/projects/yyjeqhc-webcodex)Was this useful?