FHEVM: the KMS interface, the async coprocessor, and the commercial licence line
FHEVM, a full-stack framework for integrating Fully Homomorphic Encryption (FHE) with blockchain applications
At a glance
- What is it?
- Zama's FHEVM lets you write confidential Solidity contracts on EVM compatible chains, runs the encrypted work in a Rust coprocessor off the host chain, and hands decryption to a key management service the repository only describes as an interface. A read of the directory layout, the test script, the toolchain claim, and the licensing terms before anyone adopts it.
- Who is it for?
- FHEVM fits a team that already writes Solidity, needs encrypted state sitting beside public state on an EVM chain, and is prepared to operate a key management service and a coprocessor deployment of its own.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
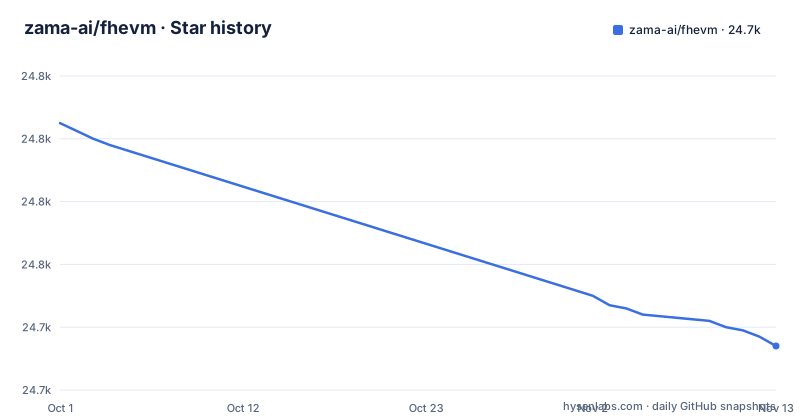
- zama-ai/fhevm24,734 ★ · -71
| Repository | 2026-10-01 | 2026-11-13 |
|---|---|---|
| zama-ai/fhevm | 24.8k | 24.7k |
-71 Stars in the last 43 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Free for research, licensed for anything commercial
The licensing story has two layers and they point in different directions. The project states the software is distributed under the BSD-3-Clause-Clear licence and points to the LICENSE file for details, but the FAQ entry on cost answers that Zama's libraries are free to use under BSD 3-Clause Clear only for development, research, prototyping, and experimentation purposes, and that companies must purchase Zama's commercial patent licence for any commercial use of the open source code. A repository index reads the licence field as unasserted rather than naming BSD-3-Clause, which is consistent with a code licence and a separate patent licence sitting next to each other. The consequence for a reader is that compliance here is not a checkbox: a team that prototypes with this code and then ships a product built on it crosses out of the free bucket and into a purchase decision, and the wording to read is the licence file plus that FAQ answer rather than the licence name alone.
Pull requests need an approved agreement, requested by email
Contribution is gated before any line of code gets reviewed. There are two ways in: open an issue through the repository's issue chooser to report bugs and typos or to suggest new ideas, or email [email protected] to request becoming an official contributor. Approval involves signing the Contributor License Agreement, and only approved contributors can send pull requests, so the project tells would-be contributors to get in touch first. For an outside maintainer that reshapes an ordinary bug fix. Filing an issue is cheap, but landing a patch needs an email round trip and a signed agreement before the work can even be opened as a pull request. The header of the README also links a bounty programme and an SLSA page, which are the paths for paid work and for supply chain provenance, and neither of those replaces the approval step for an ordinary patch.
The root test script runs bun in a folder that is not a workspace
The root package.json is thin, and the interesting parts are what it leaves out. The package is named fhevm, marked private, and declares exactly one script: test, whose body is below.
cd test-suite/fhevm && bun run testThe workspaces field beside it lists host-contracts, library-solidity, library-solidity/codegen, and test-suite/e2e, so the directory that script enters is not one of the declared workspaces while a sibling path, test-suite/e2e, is. The root carries package-lock.json rather than a pnpm or yarn lockfile, devDependencies hold only prettier with its import sorting plugin and prettier-plugin-solidity, and an overrides block pins @types/eslint-scope to 3.7.6 under webpack. There is no build or lint script at the root. A contributor who expects the workspace list to describe the whole stack meets the mismatch early, and the practical read is that end to end behaviour is exercised through docker-compose from the test-suite rather than from that one command.
Work is symbolic on chain and real in the coprocessor, asynchronously
The execution model is the piece to understand before writing a contract. All FHE operations are executed symbolically on the host chain, which the project says significantly reduces execution time, and the actual computations on encrypted data are offloaded asynchronously to the coprocessor, a Rust implementation living in the coprocessor directory. The halves are separated by directory on purpose: host-contracts holds the smart contracts deployed on the host chain for orchestrating FHE workflows, while gateway-contracts manages the gateway between the on-chain and off-chain components. The consequence for application code is that an encrypted computation does not resolve inside the transaction that asked for it, so a contract that submits an FHE operation and then needs its answer has to cope with an intermediate state. The root also holds relayer, relayer-http, and listener directories that the written project structure never mentions.
Integers cap at 256 bits and the operator list stops at arithmetic
The arithmetic surface is wide in one direction and bounded in another. The feature list promises up to 256 bits of precision for integers, and names the operators +, -, *, /, <, >, ==, ternary-if, and boolean operations, adding that consecutive FHE operations are not limited. Read as a contract about what you may write, integer precision has a 256 bit ceiling rather than being open ended. For further detail the README points at the documentation site at docs.zama.ai/protocol and at a whitepaper PDF, fhevm-whitepaper.pdf, for the cryptographic design.
Hardhat is the documented path and Foundry is marked coming soon
Toolchain support carries its own asterisk. The feature list says FHEVM contracts are written like any standard Solidity contract using Solidity, and that they are compatible with existing toolchains, naming Hardhat and Foundry with Foundry marked as coming soon. That one parenthetical decides which workflow a new project can follow today: a Hardhat based setup is the documented path, while a Foundry based one is described as intended and not delivered. The rest of the promise is that developers write confidential contracts without needing to learn cryptography, and the API shape is consistent with that, since you define exactly what data is encrypted and write the access control logic directly in your own smart contract. The trade is that Solidity fluency is assumed on day one and the cryptography ends up being a dependency you did not write.
Decryption points at a KMS the repository only ships an interface for
Key handling is delegated to something this repository does not contain. The kms-connector directory is described as an interface for integrating with Key Management Services to handle encryption keys securely, and decryption is managed through a key management system using multi-party computation, with the claim that this keeps the system secure even if some parties are compromised or misbehaving. An interface is not a key management service, so the guarantee made in the feature list is conditional on a deployment you have to supply and operate yourself. The operational side of that sits in charts, which holds Helm charts and deployment configurations for the stack, and the environments those charts expect are built from golden-container-images, Docker golden images for Node.js and Rust used as base images, with a .hadolint.yaml at the root to lint them. Treat the KMS as something to evaluate, not something that ships.
The structure section names seven directories and the root holds more
The written project structure covers seven directories, and the repository root carries considerably more. It names gateway-contracts, host-contracts, coprocessor, kms-connector, charts, golden-container-images, and test-suite, which between them cover the contract side, the compute side, and the deployment side. The root listing also includes library-solidity, protocol-contracts, listener, relayer, relayer-http, sdk, shared, ci, and docs, none of which appear in that section. For someone forming a picture of the architecture from the written description, the missing directories are the ones an application actually touches: the sdk a client would import, the relayer and listener directories, and protocol-contracts. The docs directory and the site at docs.zama.ai/protocol are where that gap closes, together with the examples index linked from the use cases section.
Editorial conclusion
FHEVM fits a team that already writes Solidity, needs encrypted state sitting beside public state on an EVM chain, and is prepared to operate a key management service and a coprocessor deployment of its own. It does not fit a team that needs Foundry support today, needs a key management service that ships in the box, or expects a permissive licence for a shipped product, because commercial use is tied to a purchased patent licence and pull requests need a signed agreement obtained by email. Before committing, read the LICENSE file and the cost answer in the FAQ, check that host-contracts and gateway-contracts match the chain you intend to target, and confirm that the toolchain your project already uses is the one named as supported.
Frequently asked questions
What is Fully homomorphic encryption (FHE) in zama-ai/fhevm?
It is the technique FHEVM is built on, letting encrypted data be processed directly onchain so that state can be updated while remaining encrypted at all times. The framework uses it to enable confidential smart contracts on EVM compatible blockchains.
What is considered the "Holy Grail" of cryptography in zama-ai/fhevm?
The README states that encrypted data is processed directly onchain, that states are updated while remaining encrypted, and that the underlying FHE crypto-scheme is quantum-resistant.
Is homomorphic encryption used today in zama-ai/fhevm?
The project presents it as running software rather than a proposal, with symbolic execution on the host chain, asynchronous offload to a Rust coprocessor, and a test-suite covering end to end stack behaviour through docker-compose.
What is partial homomorphic encryption in zama-ai/fhevm?
FHEVM is built on fully homomorphic encryption, and its README states that all typical operators are available, naming +, -, *, /, <, >, ==, ternary-if and boolean operations, and that consecutive FHE operations are not limited.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/zama-ai-fhevm)Star history chart for your README
[](https://hysenlabs.com/projects/zama-ai-fhevm)Was this useful?