afrog: a Go PoC scanner for targets you already own
A Security Tool for Bug Bounty, Pentest and Red Teaming.
At a glance
- What is it?
- afrog pairs built-in vulnerability checks with custom PoC authoring and a Go SDK, aimed at bug bounty hunters and pentesters who scan named targets. The mechanics are legible, the install is short, and the tuning surface the README exposes is narrow.
- Who is it for?
- Adopt afrog if you already hold written scope for the hosts you point it at and want PoC checks you can read and edit in the same repository as your scanning logic.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly HTML, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
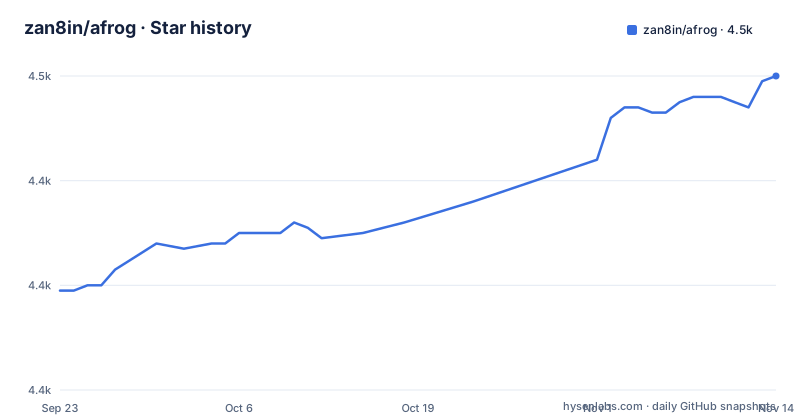
Star history
- zan8in/afrog4,460 ★ · +41
| Repository | 2026-09-23 | 2026-11-14 |
|---|---|---|
| zan8in/afrog | 4.4k | 4.5k |
41 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
afrog scans hosts you name, one URL or one file at a time
The scanner takes targets, not a discovery surface. A single host goes in with the -t flag, a list of them with -T, and the README quick start shows no crawl mode or subdomain enumeration. That constraint is the design. Bug bounty and pentest work arrives with a scope document, and afrog is built to run inside that scope rather than to find its edges.
The audience is a researcher who has already decided what to test and wants the per-host checks to be repeatable. The repository layout backs that reading: pocs/ holds the rule set, pkg/ holds the engine, cmd/afrog/main.go is the entry point, and proto/ sits alongside them. The examples/ directory breaks the same engine into ten subdirectories, including oob_scan/, port_scan/, vuln_scan/ and async_scan/, so the boundary between the command line tool and the library is easy to see.
Where it fits is narrow and worth naming plainly: this is a verification tool for a shortlist, not a survey tool for a subnet.
Every check is a PoC file, and yours live beside the built-ins
Checks are data. A rule in pocs/ describes what to send and what a confirming response looks like, which means a new check is a new file rather than a code change and a rebuild. That is the most useful single fact in the repository, because it is what lets a private rule set stay private: your PoCs never have to live in the upstream tree.
The engine consumes those rules and hands back findings, and the -S flag narrows a run by severity, which is the only selection mechanism the README shows. Output shaping is a separate concern, handled on the library side by examples/full_output/ and examples/progress_scan/ rather than by a documented command line flag.
There is a fifth handbook in the documentation table, Curated PoC, described as enabling curated PoCs under their own terms. The code itself carries an MIT licence and the curated set sits under separate licensing. Anyone planning to rely on those rules has to read the curated overview page before budgeting for them.
Building it takes Go 1.27 and a module path that ends in /v3
Two routes are documented. A prebuilt binary skips compilation entirely; the source route needs a recent toolchain and a build command that names the entry file directly rather than a package path.
git clone https://github.com/zan8in/afrog.git
cd afrog
go mod tidy
go build -o afrog cmd/afrog/main.go
./afrog -h
That leaves an afrog binary in the repository root, and the help flag is where you confirm what this build actually exposes. The toolchain route installs into your module path instead:
go install -v github.com/zan8in/afrog/v3/cmd/afrog@latestThe /v3 in that path is not optional. The module declares itself as github.com/zan8in/afrog/v3 and the latest releases are v3.5.8, v3.5.9 and v3.5.10, so an install written without the suffix fails to resolve against a v3 tree. The stated dependency is Go 1.27 or later.
First run: one target, then a file, then a severity filter
Start with a single host you are certain you may test.
afrog -t https://example.comMove to a list once that behaves. Targets are read from a file, and that file is how a scope list moves from a document into the scanner.
afrog -T targets.txtThen cut the noise. The severity flag takes a comma separated list, and running only the two upper bands is the documented way to keep a first pass short:
afrog -T targets.txt -S high,criticalWhat you should read off that first run is not the finding count but the coverage: which rules fired, whether the ones you expected stayed silent, and whether anything in the list timed out. No timeout flag and no concurrency flag appear in the README quick start; ./afrog -h is where to check what your build exposes.
The SDK path reaches further than the flags do
The ten directories under examples/ are the clearest statement of what the engine can do. basic_scan/ is the floor. async_scan/ and progress_scan/ exist because long runs need concurrency and feedback, and sdk_portscan/ shows the same engine driving port work rather than only HTTP checks. oob_scan/ is the entry that changes the security posture of the tool, because out-of-band checks need a listener you control and callbacks you can correlate back to a run.
That last point is the operational constraint nobody reads in a documentation table. Out-of-band detection is not self-contained. Your infrastructure becomes part of the measurement, and a firewall, an egress rule or a proxy that swallows the callback reports the vulnerability as absent. The dependency list reaches the same way into network services: the module pulls in drivers for SMB, MSSQL, MongoDB, PostgreSQL and Oracle, so a scan against a host with those ports open makes requests on your behalf that you are accountable for.
Embedding the SDK also means you own the Go dependency graph in the module file, roughly forty modules including a payload collection under the nu1r organisation.
Where afrog sits against a template-driven scanner
The nearest comparison is Nuclei, and the difference is in how checks are expressed rather than in what gets found. Nuclei is built around YAML templates that describe the request, the matchers and the workflow, which makes it easy to take a template from a public collection and run it unmodified. afrog's PoC authoring guide, at docs/en/poc/01-quickstart.md, treats a check as something you write, which suits a team with private detection logic and a rule format it intends to hold steady.
The second difference is what the binary wraps. afrog ships as a library first: afrog.go sits at the repository root beside afrog_test.go, and the SDK handbook is part of the same documentation table rather than a bolt-on. If your pipeline needs the scanner inside an existing Go service, that arrangement is the argument. If you need the largest body of community templates on day one, the template ecosystem is the other tool's advantage.
Do not pick between them on detection counts.
The repository reports HTML as its primary language, which is worth a look
The GitHub metadata for zan8in/afrog lists HTML as the primary language. Read the module file, the build command and the package tree and the reality is a Go project. The mismatch is a reminder that language statistics describe file counts rather than architecture.
What the layout does tell you is where the weight sits. A .goreleaser.yaml file drives the packaged builds, so the binary you download is cut from the same tree you clone. helper/ and pkg/ split low-level plumbing from engine logic,, and the README documents a built-in web console, started with afrog -web and opened at http://127.0.0.1:16868, so a web front end does ship with the scanner.
No changelog appears in the top-level listing, so upgrade notes live in the tagged version entries themselves. Read them before bumping a pinned install, because a module upgrade can move your dependency versions with it.
Editorial conclusion
Adopt afrog if you already hold written scope for the hosts you point it at and want PoC checks you can read and edit in the same repository as your scanning logic. Do not adopt it as a substitute for authenticated scanning, wide-protocol enumeration, or out-of-band infrastructure you have not stood up yourself, and verify your toolchain first: the module file pins go 1.27.0 with a toolchain line for go1.27.1, so the build does not start on anything older and the go install path needs the /v3 suffix.
Frequently asked questions
How do I install afrog on my machine?
The README documents three routes: download a prebuilt binary from the project's download page, build from source with a go build command after go mod tidy, or run go install against the v3 module path. Go 1.27 or later is the stated dependency.
How do I run afrog against multiple targets?
Pass a file of targets with the -T flag, or a single URL with -t. To limit a run to the two upper severity bands, add -S with the values high and critical.
Can I write my own PoC checks for afrog?
Yes. Built-in and custom PoC support are part of the design, the PoC Authoring Guide starts at docs/en/poc/01-quickstart.md, and the repository keeps its rule set in the pocs/ directory so private checks can be kept out of the upstream tree.
Does afrog support out-of-band detection?
The examples/ directory includes an oob_scan/ example alongside async_scan/, port_scan/, vuln_scan/ and vulnweb/, so out-of-band scanning is part of what the engine exposes.
Can I embed afrog in a Go program?
There is an SDK usage guide starting at docs/en/sdk/01-quickstart.md, and the module path is github.com/zan8in/afrog/v3, which is the same path the go install command uses.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/zan8in-afrog)Star history chart for your README
[](https://hysenlabs.com/projects/zan8in-afrog)Was this useful?