bootloader-unlock-wall-of-shame: a four tier index of 46 brands and the tools behind each workaround
Keeping track of companies that "care about your data 🥺"
At a glance
- What is it?
- The repository sorts phone makers into four unlock tiers, then links out to test point tools, MediaTek clients and a Snapdragon 8 Elite entry marked patched in February/March 2026. It is a map, not a manual, and it rarely dates an entry.
- Who is it for?
- Treat the wall of shame as triage, not as a procedure. If your brand is on the list you get a verdict and a first link, which is exactly what you need before you spend a weekend on it.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- GitHub does not report a main language for this repository.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
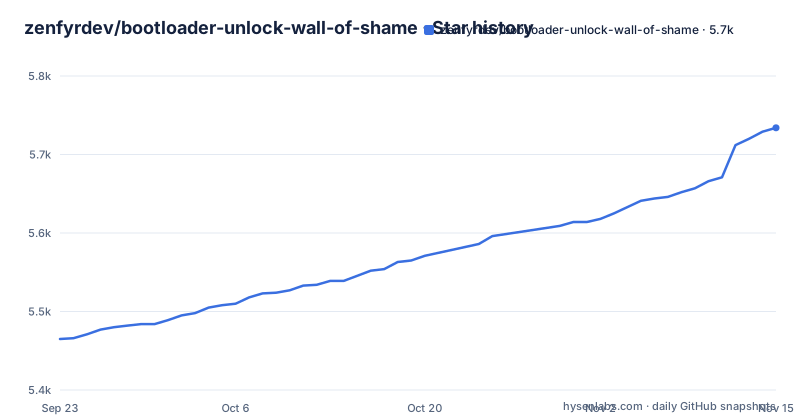
- zenfyrdev/bootloader-unlock-wall-of-shame5,734 ★ · +269
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| zenfyrdev/bootloader-unlock-wall-of-shame | 5.5k | 5.7k |
269 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Four tiers and forty-six brand links
The index sorts manufacturers into four groups and gives each one a verdict, with a link to a page under brands/ for the detail. The first group, the one the project tells you to avoid at all costs, has seventeen entries: Alcatel, Amazon, Apple, Asus, Cat, Coolpad, Doogee, Energizer, Huawei, Meizu, Panasonic, Samsung, Sharp, TCL with BlackBerry, Vivo with IQOO, Vsmart, and Windows phones. They share one sentence: unlocking is completely impossible without a workaround. The second group has ten, and here the wording changes, because these vendors do unlock, just under conditions such as region, model, or SOC, or they ask for a sacrifice to unlock. That is Hisense, HMD with Nokia, Honor, HTC, LG, Motorola with Lenovo and NEC, OPPO with Realme, Oukitel, Xiaomi with Redmi and POCO, and ZTE with nubia and Redmagic. The third group has seven, Fairphone, Google with Nexus, Infinix, itel, OnePlus, Sony, and Tecno, and they share the condition of needing an internet connection, a waiting period, or both. The last group has twelve under a label that reads safe for now, followed by a troll face, which is the author telling you the label expires. Blackview, Cubot, Micromax, Microsoft, Nothing, Shift, Teclast, Teracube, TP-Link with Neffos, Ulefone, Umidigi, and Volla sit there.
The offline rule that sits above the whole list
Before the tiers, one callout sets the standard everything is judged against: no matter how nice a company is, you should not trust them unless their unlock process is 100 percent offline. That sentence is the sharpest thing here, and it is also the one with nothing behind it. An unlock that runs on a vendor server can be changed without notice, can be withdrawn, and leaves a record that you asked for it. An unlock that runs offline cannot. The third tier exists because of that test, since those seven vendors are described as requiring a connection or a wait. The carrier section applies the same logic from the other end. A carrier locked phone is one you took on commitment from a carrier, which the page calls common in North America, and almost all of them refuse the unlock outright, because unlocking would let you bypass the contract entirely. The sentence worth reading twice is the one after that: many devices still refuse the unlock after the carrier lock has been lifted. Nothing here explains what a lifted carrier lock changes inside the bootloader, and the advice for this whole category is to check the device manual or contact support, with the longer version on the linked carriers page.
Mirrors that read fine but take no issues
There is nothing to install here. The deliverable is a set of Markdown files, so setup means getting a copy and knowing where the parts sit.
git clone https://github.com/zenfyrdev/bootloader-unlock-wall-of-shame.git
cd bootloader-unlock-wall-of-shame
The top level shows the whole shape of the work: brands/ holds one folder and one README per vendor, carriers/ deals with contract locked phones, and ru/ is a Russian translation of the index. Copies are mirrored on Codeberg and on tangled, and the page is explicit that issues, pull requests, and discussions on those two are not monitored, so GitHub is where they go. That split has a real cost: a correction filed on a mirror goes nowhere. There are no releases, so there is no tag to pin and no changelog to read, and the default branch is main with its last push dated 2026-11-02. A LICENSE file sits next to README.md and CONTRIBUTING.md, yet the repository's license field reads NOASSERTION, so open the file before you reuse a line from it.
Chip level routes that ignore the tiers
Below the brands sits a second layer organised by silicon instead of by policy, and it is the layer that can actually open a phone. Kirin is the cleanest case: models 620, 650, 655, 658, 659, 925, 935, 950, and 960 can be unlocked with test points and a tool called PotatoNV, and the project's whole instruction is to read that tool's own README. MediaTek hardware that answers to mtkclient or to Penumbra can be unlocked with either one, and bootloader (LK) patches can be applied via lkpatcher, which also has a web version, or via kaeru for ARMv7 boards; booting with patched LKs requires an already unlocked bootloader or may not be supported at all. Qualcomm has an entry for Snapdragon 8 Elite Gen 5 and Snapdragon 8 Elite, marked as patched in February/March 2026.
One brand, three OPPO MediaTek fallbacks
OPPO and Realme sit in the second tier, and the MediaTek notes list several tools for that chip family. mtkclient or Penumbra handles the unlock itself. lkpatcher, which has a web version, or kaeru for ARMv7 boards, applies bootloader (LK) patches, and the notes warn that booting with patched LKs requires an already unlocked bootloader or may not be supported at all. The README also tells you to check OEM-specific pages first, as there are often exceptions, but gives no test for telling you which tool applies to your device. That is the structural gap in the project. The tier tells you what a vendor's policy is, the chip notes tell you what the community reaches for, and nothing joins the two layers together.
The Snapdragon 8 Elite window shut in March 2026
One entry in the whole index carries a date, and it happens to be the newest and most consequential one. It covers Snapdragon 8 Elite Gen 5 and Snapdragon 8 Elite, and the note marks it as patched in February/March 2026. The value of that entry is therefore already spent, and it is still worth reading, because it tells you exactly which chip generation had the gap and that the gap closed. Maintenance here looks like this. Entries are lines in Markdown files, the repository has no releases and no changelog, and the last push to main is dated 2026-11-02, so a chip getting patched or a vendor changing policy arrives as one edited line with no public record of when anyone last checked. The safe for now tier has the same flaw in a worse form, because nothing says when those twelve brands were last looked at.
Nothing on the page covers data, warranty, or firmware build
Here is what a reader cannot get from this index however carefully they read it. The index itself does not say whether a workaround wipes the phone or mention warranty, not even for the seventeen brands the project tells you to avoid. The third tier names its condition, an internet connection or a waiting period, without giving a number of days or saying whether the requirement moved. The second tier fails in a different way, because it merges several unrelated situations under one label: conditions based on region, conditions based on model, conditions based on SOC, and unlocks that ask for a sacrifice. From the index alone you cannot tell whether you are looking at a settings toggle, a wait, or something you are going to lose. And none of it is checked. Corrections arrive as pull requests and discussion posts, so a brand page is only as good as whoever wrote it.
Editorial conclusion
Treat the wall of shame as triage, not as a procedure. If your brand is on the list you get a verdict and a first link, which is exactly what you need before you spend a weekend on it. Before running any of the linked tools, read the tool's own documentation, check what your firmware build does, and confirm that the entry you are relying on has not quietly gone stale, because almost nothing in the repository dates a claim and every page is one person's pull request away from changing.
Frequently asked questions
What does unlocking your bootloader do on a device the wall of shame flags?
It is the step that lets a phone run software the vendor did not ship on it. The project also points at custom Android Verified Boot keys as a narrower route: they allow a custom OS with the bootloader left locked, and the page notes that devices supporting them are rare.
Is unlocking a bootloader risky, according to the wall of shame tiers?
The caution it leads with is about trust rather than breakage: do not trust a vendor unless the unlock process is 100 percent offline. Some of the routes it links rely on test points or tools such as mtkclient, and it notes that booting with patched LKs requires an already unlocked bootloader or may not be supported at all.
Does unlocking the bootloader delete everything, does the wall of shame say?
The main list does not say. It gives a tier per brand and a link to that brand's page, and its own stated test is whether the vendor's unlock process is 100 percent offline. Check the specific brand page and the vendor's own instructions before you start anything.
Why did Samsung lock the bootloader?
Samsung sits in the top tier, grouped with vendors that have made it completely impossible to unlock their devices without a workaround. No reason is given per brand. The README's broader worry is companies dismantling user choice and open platforms, citing Google's Android developer verification program aimed at installing 'unauthorized' software.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/zenfyrdev-bootloader-unlock-wall-of-shame)Star history chart for your README
[](https://hysenlabs.com/projects/zenfyrdev-bootloader-unlock-wall-of-shame)Was this useful?