hcxtools converts WiFi captures to hash files and stops there, on Linux with kernel 5.15 or newer
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
At a glance
- What is it?
- Ten standalone C tools that turn capture files into hash files for Hashcat and John the Ripper, with every unwanted record left in the output for you to filter. This is network auditing territory: the set excludes Windows, macOS and Android, refuses to crack or decrypt anything, and warns that merging dump files destroys the hash values custom blocks carry.
- Who is it for?
- hcxtools fits a specific job: you hold captures from a network you own or are authorised to test, and you want them in a shape Hashcat or John the Ripper will read. It is not a general cracking toolkit and does not pretend to be one.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 15 days ago.
- What is it written in?
- Mainly C, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
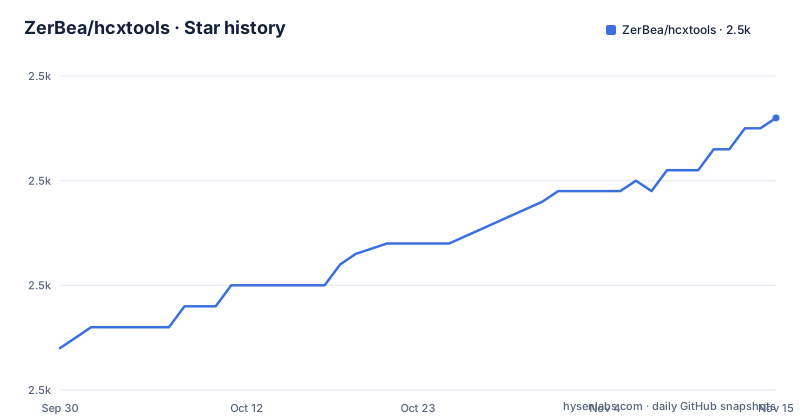
- ZerBea/hcxtools2,476 ★ · +22
| Repository | 2026-09-30 | 2026-11-15 |
|---|---|---|
| ZerBea/hcxtools | 2.5k | 2.5k |
22 Stars in the last 46 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Ten standalone C binaries, linked one dependency set at a time
The tree is flat and the naming is systematic. Ten `.c` files sit at the top level: `hcxpcapngtool.c`, `hcxhashtool.c`, `hcxpmktool.c`, `hcxpottool.c`, `hcxpsktool.c`, `hcxeiutool.c`, `hcxwltool.c`, `hcxhash2cap.c`, `whoismac.c` and `wlancap2wpasec.c`, alongside `include/`, `man/`, `changelog` and a `usefulscripts/` directory. There is no shared library to link against. Each program is built on its own and installed on its own.
The Makefile's `TOOLS` list carries a per-binary dependency split that is worth reading before you build. `hcxpcapngtool` gets OpenSSL and zlib. `hcxhashtool`, `wlancap2wpasec` and `whoismac` get OpenSSL and libcurl. `hcxpsktool`, `hcxpmktool` and `hcxpottool` get OpenSSL, with pthread added for the pot file tool. Three of them, `hcxeiutool`, `hcxwltool` and `hcxhash2cap`, pick up nothing beyond the base flags. Because it is one target list, a full `make` pulls curl and zlib development files onto the machine even if you only ever intended to run the capture converter.
The pipeline ends at hashcat or JtR, by design
The workflow is written out as a single line: hcxdumptool -> hcxpcapngtool -> hcxhashtool (additional hcxpsktool/hcxeiutool) -> hashcat or JtR. hcxtools occupies the middle. It sits downstream of a capture tool and upstream of a cracking tool, and it does nothing that either neighbour does not already do.
The project is explicit about the four things it will not do. It does not crack WPA PSK related hashes, and points you at Hashcat or John the Ripper to recover the PSK. It does not crack WEP, pointing at the aircrack-ng suite. It does not crack WPS, pointing at Reaver or Bully. It does not decrypt encrypted traffic, pointing at tshark or Wireshark. That list is unusually clean for a repository in this space, and it is also why the tree carries no wordlists, no candidate generation for other targets, and no attack loop. `hcxwltool` mixes wordlists and `hcxpsktool` produces weak PSK candidates, both of which are inputs for the neighbours rather than substitutes for them.
Building means a clone, a parallel make, and a make install as super user
Package managers cover most distributions. The documented source route is three steps.
git clone https://github.com/ZerBea/hcxtools.git
cd hcxtoolsmake -j $(nproc)make install (as super user)For a different prefix, the same target takes a variable:
make install PREFIX=/usr/local (as super user)`PREFIX` defaults to `/usr` and `BINDIR` resolves to `$(DESTDIR)$(PREFIX)/bin`, so the first form lands in `/usr/bin` and the second in `/usr/local/bin`. Both install as root. A third build definition sits next to the Makefile: `meson.build` with `meson_options.txt`, so the project carries two independent build systems, and the documentation only walks through one of them.
Kernel 5.15 is mandatory, gcc 16 is advised, and newbies are told to leave
The platform list is short. Windows OS, macOS, Android, emulators and wrappers are all marked unsupported in one line, and the operating system requirement reads Linux latest longterm or stable, kernel 5.15 mandatory. The recommended distributions are Arch Linux for notebooks and desktops and OpenWRT for small systems such as the Raspberry Pi.
The dependency list is specific about versions: gcc 16 recommended with deprecated versions not supported, libopenssl 3.0 or newer plus openssl-dev, librt and librt-dev, zlib and zlib-dev for gzip compressed capture files, libcurl 7.56 or newer plus curl-dev used by `whoismac` and `wlancap2wpasec`, and pkg-config. Compiler flags default to `-O3 -Wall -Wextra -Wpedantic` with `-std=gnu99` appended.
Then there is the knowledge list, which is unusual to see stated plainly: radio technology, electromagnetic-wave engineering, detailed 802.11 protocol, detailed key derivation functions, NMEA 0183 protocol, and detailed Linux. The README also says outright that the tools are not recommended for unexperienced users or newbies. Whether that advice is calibrated is your call, but it is at least on the page.
The Makefile still reports 7.1.2 while the branch has moved to 2026-09-29
The version string is not derived at build time in the usual way. `PRODUCTION_VERSION := 7.1.2` and `PRODUCTION_YEAR := 2026` are hardcoded, and `VERSION_TAG` is computed from `git describe --tags`, falling back to the hardcoded production version when that command fails. A tree without tags therefore builds something that claims to be 7.1.2 whether or not it is.
The released tags run 7.0.1 on 2025-08-17, 7.1.0 on 2026-02-01 and 7.1.2 on 2026-02-08. The last push recorded for this branch is 2026-09-29, roughly seven months past the newest tag, so what you clone from git head is ahead of the newest release by a wide margin while the binary still identifies itself as 7.1.2. If a bug report needs a version string, the one the tool prints will not distinguish your build from the February release.
A `.travis.yml` also sits at the top level next to `.github/`, so continuous integration history is split across two configurations.
Conversion keeps everything, so filtering is left to hcxhashtool
The notice says it plainly: hcxtools are designed to be analysis tools, which means that everything is converted by default and unwanted information must be filtered out. There is no selective conversion flag to reach for. Whatever was in your capture file arrives in the hash file, and cleaning it afterwards is a separate step.
That step exists. `hcxhashtool` filters hashes from HC22000 files based on user input, and `hcxeiutool` prepares the `-E`, `-I` and `-U` output of `hcxpcapngtool` for use by Hashcat plus a rule or JtR plus a rule. `hcxpottool` handles the ASCII format and several UTF formats of Hashcat's pot file, which matters as soon as candidate sets carry non-ASCII passwords.
Format coverage is broad: Hashcat modes 4800, 5500, 2200x and 16100, with 250x and 1680x marked deprecated, plus John the Ripper modes WPAPSK-PMK, PBKDF2-HMAC-SHA1, chap, netntlm and tacacs-plus. Single file gzip compression is supported for capture input. The guidance is to use mode 22000, and 22001, in preference to the deprecated 2500, 2501, 16800 and 16801 modes.
Merging dump files destroys custom block hash values, and output is appended
Three data handling facts sit in the notice block, and all three can cost you a run.
The loudest is a warning in capitals: do not merge dump files, because doing so will destroy hash values assigned by custom blocks. The custom block is how a capture carries the identifiers that let a hash be tied back to a specific access point and client, so a merged file produces hashes that cannot be traced and cannot be checked.
Second, most output files are appended to existing files rather than replaced. pcapng, pcap and cap files are the stated exception. A pot file or an output hash file therefore accumulates across invocations, and re-running the same input twice silently doubles your candidate set rather than replacing it.
Third, the tools do not perform nonce error correction. A packet loss produces a wrong PTK rather than a flagged record, so a capture with gaps can yield hashes that look valid and are not. All three are reasons to work on copies of a capture and to keep one capture per run.
Two tools move your captures off the machine
Not every binary in this set is a local file converter. `wlancap2wpasec` uploads multiple gzip compressed pcapng, pcap and cap files to https://wpa-sec.stanev.org, and the Makefile links it against OpenSSL and libcurl. `whoismac` shows vendor information and downloads an oui reference list, also against OpenSSL and libcurl. Those two entries are the entire reason the project needs a network client library at all.
The upload path is also mentioned in the introductory section, which suggests sending an uncleaned dump file to the same site so that common wordlists or a weak password generation algorithm can be tried against it. That is a public submission of your network's frames. Whether a given capture is appropriate to publish is a decision about your own infrastructure and your neighbours' traffic, and it should be made before the command runs rather than after.
For anyone working on networks they own or are authorised to assess, the rest of the set stays local: nine of the ten tools read and write files, and the tenth is the one that talks to the internet.
Editorial conclusion
hcxtools fits a specific job: you hold captures from a network you own or are authorised to test, and you want them in a shape Hashcat or John the Ripper will read. It is not a general cracking toolkit and does not pretend to be one. Before a first run, confirm four things. Your kernel is 5.15 or newer and your gcc is 16 or newer, since older compilers are called out as unsupported. Your hcxdumptool and hcxpcapngtool versions match each other, because mismatched versions produce garbage rather than an error. You have disk space and a habit of moving old output aside, since most tools append instead of overwriting and a stale pot file will quietly blend into your results. And you know exactly which of your captures are about to leave the machine through wlancap2wpasec. Anyone who wants a GUI, a Windows build, or a one command answer does not want this.
Frequently asked questions
How do I install hcxtools on Kali Linux?
The README does not mention Kali at all. It says that on most distributions the tools are available through the package manager, and it recommends Arch Linux for notebooks and desktops and OpenWRT for small systems. The source route it does spell out is a git clone, then `make -j $(nproc)`, then `make install` as super user.
Which platforms does hcxtools support?
Linux only. Windows OS, macOS, Android, emulators and wrappers are all marked unsupported, and the stated operating system requirement is a Linux longterm or stable kernel with 5.15 mandatory.
Does hcxtools crack WiFi passwords itself?
No. It converts capture files into hash files for Hashcat or John the Ripper and explicitly leaves PSK recovery to them. WEP is pointed at aircrack-ng, WPS at Reaver or Bully, and traffic decryption at tshark or Wireshark.
Why should I not merge capture files before running hcxtools?
The README warns that merging dump files will destroy hash values assigned by custom blocks, which is what ties a hash back to a specific access point and client. It also notes that most output files are appended to existing files, and that no nonce error correction is done, so packet loss yields a wrong PTK.
Which hash formats does hcxtools produce?
For Hashcat it covers modes 4800, 5500, 2200x and 16100, with 250x and 1680x deprecated. For John the Ripper it covers WPAPSK-PMK, PBKDF2-HMAC-SHA1, chap, netntlm and tacacs-plus, and mode 22000 or 22001 is recommended over the deprecated 2500 and 16800 modes.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/zerbea-hcxtools)Star history chart for your README
[](https://hysenlabs.com/projects/zerbea-hcxtools)Was this useful?