rtty's C client dials out to rttys, so a device behind NAT needs no open port
🐛 Access your device from anywhere via the web.
At a glance
- What is it?
- rtty is the C client half of a remote access system: devices call out to a central Go server, which relays a browser terminal, file transfers, batch commands, an HTTP proxy and TCP forwarding back to them. The repository holds the small embedded client, not the server, and the tree makes that split visible.
- Who is it for?
- rtty is worth a look if you maintain devices you cannot reach directly, because the outbound connection model removes the port forwarding problem that makes remote access on embedded hardware tedious, and the C client is small enough for the routers and gateways it targets.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 8 days ago.
- What is it written in?
- Mainly C, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
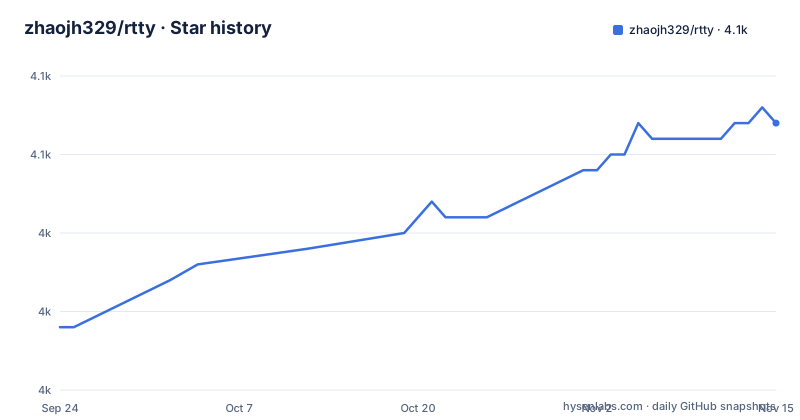
- zhaojh329/rtty4,052 ★ · +13
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| zhaojh329/rtty | 4k | 4.1k |
13 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Clients dial out, so a device behind NAT needs no open port
The architecture is a relay with connections pointing one way only. A central server, rttys, accepts connections from browsers and from devices, and a device is identified by a device ID and placed in a group. Both the browser and the device client have to be able to reach the server, and because the device initiates the connection, a device behind NAT does not need a public IP address or inbound port forwarding.
That single decision is what makes the system usable on a home router, and it is also what dictates the deployment. The server has to be reachable from wherever the device is, which in practice means either a public host or something a tunnel makes public. What the browser gets in return is a terminal, file transfer and access to device services, all through the same relay, with no inbound hole punched in the device itself.
This repository is the client, and the other two pieces live elsewhere
The split is stated in the overview and it is worth repeating because it is the most common source of confusion. This repository contains the C client. The server, rttys, is a separate repository and provides the web interface and relays connections to devices. The server is written in Go with a frontend built using Vue.
A third repository exists for the Go client, and it is presented as an alternative implementation rather than a rewrite: easy cross-platform compilation for rapid integration, dependencies managed by the Go toolchain, and a connection to the same rttys server as the C client. So the choice a project makes is between two client languages against one server, and the C side is described as ultra-lightweight and designed for embedded Linux and resource-constrained devices.
TLS is available three ways and mutual authentication is optional
Traffic between a device client and rttys is encrypted with TLS, and the SSL implementation is a build-time choice rather than a bundled one. Three backends are named: mbedtls, previously known as polarssl, described as a lightweight SSL and TLS library; wolfssl, offered under its commercial name CyaSSl and described as embedded; and OpenSSL, described as the full-featured toolkit. All three are optional dependencies, so a build with no SSL at all is a valid configuration.
On top of that sits optional mutual TLS, certificate-based client authentication, which means the server can require a client certificate rather than trusting the network path. That is the setting to think about first for fleet deployments, since device IDs are otherwise the only thing identifying a caller, and a stolen ID is not a secret.
Two required dependencies: an event loop and an INI parser
The C client needs libev, a high-performance event loop library, and inih, a lightweight INI parser used specifically for loading the rtty configuration file. Everything else is conditional on features. There is no JSON parser in the list, no HTTP library and no terminal emulator, which is consistent with a client whose job is to maintain a connection and relay bytes.
The build reflects that shape as well. The root holds `CMakeLists.txt` with a `cmake/` directory beside it, a `src/` directory for the code, and `tools/` for whatever else the project keeps there. There is a `.gitmodules` file, so at least one dependency arrives as a submodule rather than through a package manager, and the configuration file itself, `rtty.ini`, is committed at the root, which means the shipped defaults are visible before anything is built.
The browser becomes a network hop for HTTP and TCP traffic
Beyond the terminal, the feature list includes two forms of tunnelling. HTTP proxy support lets you reach a device's own web interface through the relay, which is the common case for a router administration page that has no other route in. TCP port forwarding covers everything else, exposing a TCP service on a connected device through the server.
Both features move the same trust decision as the terminal. A device reachable through a relay is a device whose services are reachable by anyone who can reach the server and knows the device ID, so the questions worth asking are whether the relay authenticates sessions before it proxies anything and whether group membership is enforced on the proxy path as well as the terminal path. The README describes the features and does not describe an authorisation model, so that part has to come from the server side.
Batch commands and file transfer are the two features aimed at fleets
Device management is organised around identification and grouping: devices carry IDs, devices belong to groups, and batch command execution runs a command across multiple devices at once. File management is handled by upload and download through the web interface rather than by a command line tool, which is the point of having a browser in the loop.
The terminal itself is a full-featured one powered by Xterm.js, with window splitting for multi-session work, a virtual keyboard for touch devices, and serial terminal forwarding for talking to a serial line. That last item is the one that distinguishes rtty from a plain SSH gateway: a router or gateway whose console is a serial port rather than a network service can still be reached, which is a common situation on embedded hardware that has no SSH daemon at all.
One sponsor and five named production users
The project states at the top that it is officially supported by GL.iNet, a router vendor, and the production users section names GL.iNet alongside Yunlianxin Technology, One IOT World, bitswrt Communication Technology and Guangzhou Lingpai Technology, then trails off with an ellipsis.
The sponsorship and the user list point the same direction as the design. The stated uses are maintaining OpenWrt routers, troubleshooting embedded Linux gateways and managing distributed Linux devices remotely, and the clients are described as targeting Linux and OpenWrt environments. A vendor-backer and a hardware-shaped feature set are consistent with each other, and both are also the reason to check the release history before relying on it: v9.2.0 shipped on 2 October 2026, v9.1.0 in May 2026 and v9.0.4 in December 2025, a minor release roughly every four to six months.
Documentation in two languages and an agents directory
The repository carries parallel Chinese and English material: `README_ZH.md` is linked from the title, and there is a `CONTRIBUTING_ZH.md` next to `CONTRIBUTING.md`. The contribution guidelines are therefore available in both languages, though the English file is the one the README points newcomers to, and it does not summarise them, so the expectations for a pull request live one click away.
The rest of the root is small and mostly explanatory. There is an `img/` directory for the images the README uses, the `cmake/`, `src/` and `tools/` directories for the build, and an `.agents/` directory whose purpose the README does not describe, alongside `.github/` and a `.gitmodules`. The project also links a star history page, which is the sort of thing that tells you the audience is arriving from repository listings rather than from a documentation trail.
Editorial conclusion
rtty is worth a look if you maintain devices you cannot reach directly, because the outbound connection model removes the port forwarding problem that makes remote access on embedded hardware tedious, and the C client is small enough for the routers and gateways it targets. Before you commit, be clear about which half you are installing: this repository is the device client, and the web interface and relay live in the separate rttys repository, with a second Go client in a third. Then decide on transport security early, because the three SSL backends are optional dependencies and mutual authentication is off unless you configure certificates on both ends. And read the configuration file before your first run, since the client loads an INI file and the sample of it sits in the repository root.
Frequently asked questions
What does rtty actually do?
It is a remote access solution made of device clients and a central rttys server. You open a terminal in the browser, transfer files and reach device services through that server, and because the device initiates the connection, devices behind NAT need no public IP address or inbound port forwarding. This repository holds the C client.
What does the rtty client need to compile?
Two required dependencies: libev as the event loop, and inih as a lightweight INI parser used to load the rtty configuration file. SSL is optional and comes from OpenSSL, mbedtls or wolfssl. The build itself is CMake, with CMakeLists.txt, a cmake directory and a src directory at the root, plus at least one submodule.
Does rtty support mutual TLS between a device and the server?
Yes, as an option. Connections between device clients and rttys are encrypted with TLS, and mutual TLS adds certificate-based client authentication on top. Which library implements the TLS is a build choice among mbedtls, wolfssl and OpenSSL, all listed as optional dependencies.
Can rtty reach a device's own web interface or a serial console?
Both are listed features. HTTP proxy support exposes a device's web interface through the relay, TCP port forwarding covers other TCP services, and serial terminal forwarding covers devices whose console is a serial line rather than a network service. The web terminal itself is powered by Xterm.js, with window splitting and a virtual keyboard for touch devices.
Is rtty only for routers and OpenWrt devices?
The stated uses are maintaining OpenWrt routers, troubleshooting embedded Linux gateways and managing distributed Linux devices remotely, and the clients are described as targeting Linux and OpenWrt environments. Devices are organised by ID and group, and batch command execution runs a command across several devices at once.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/zhaojh329-rtty)Star history chart for your README
[](https://hysenlabs.com/projects/zhaojh329-rtty)Was this useful?