SubnetDesk: RustDesk with the rendezvous server taken out
LAN-only remote desktop based on RustDesk
At a glance
- What is it?
- SubnetDesk is an independently maintained RustDesk fork for networks where both machines can already reach each other. It removes the public device ID, rendezvous, relay, cloud account, proxy and automatic update paths, and replaces them with direct endpoint connections, mDNS discovery and a CIDR allowlist. The cost is that it does nothing for cross-NAT access.
- Who is it for?
- Use SubnetDesk in a home lab, an office LAN, a classroom, on-site support, or any private network joined by WireGuard, Tailscale or OpenVPN, where direct reachability is a given. It will not help you reach a machine behind a corporate NAT, because that is exactly the problem the removed rendezvous and relay solved.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 3 days ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
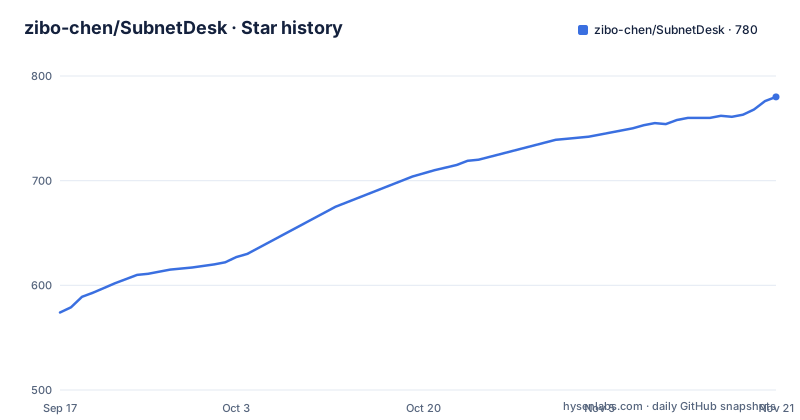
- zibo-chen/SubnetDesk780 ★ · +206
| Repository | 2026-09-17 | 2026-11-21 |
|---|---|---|
| zibo-chen/SubnetDesk | 574 | 780 |
206 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
A RustDesk fork with the coordination paths removed
The premise is narrow on purpose. SubnetDesk targets remote control between devices that can already reach each other, and everything else about RustDesk's topology is deleted rather than optional: the public device ID, rendezvous, relay, cloud account, proxy, and automatic public-update paths. What replaces them is direct endpoint connections plus local device discovery.
The comparison table in the README is the clearest statement of the trade. Connection becomes a direct IP address or hostname instead of a device ID routed through rendezvous with an optional relay. Discovery becomes automatic mDNS on the LAN instead of a device ID or an address book. Server dependency drops to none, where the usual deployment needs a public or self-hosted rendezvous and relay. Best suited for becomes LANs, routed private networks and VPNs, rather than internet and cross-NAT access.
The README states the limitation as a warning rather than a caveat: SubnetDesk does not provide internet rendezvous or relay services, and the two devices must be reachable through the same LAN, a routed private network or a VPN.
Discovery is mDNS, and the default port is 21118
Setting up takes four steps. Install and open SubnetDesk on both machines. On the controlled machine, open LAN settings, set a username and password, and enable LAN discovery. On the controller, either pick the device that appears or type an address in the form `hostname:port` or `IP:port`. Then verify the fingerprint on first connection and connect.
The default port is `21118` and it is configurable, which means the port is part of the configuration surface rather than a constant. The network checklist that follows is the part people skip: both devices must be able to route to each other, TCP port 21118 or whatever you configured must be allowed by the host firewall, and the controlled device's CIDR allowlist has to include the controller's network.
mDNS is only needed for the automatic path. Direct address entry works without it, which is the fallback when a network blocks multicast. On Linux there is a separate readiness document covering SELinux, Wayland and the login screen, since those three are what stop a capture daemon from starting on a freshly installed distribution.
Passwords are Argon2id hashes and fingerprints are trust on first use
The security model has four parts and they are all local. Traffic stays on the network path between your two devices because there is no coordination service to route it through. Passwords are persisted as Argon2id hashes rather than plaintext. Device fingerprints provide trust-on-first-use verification and help detect an unexpected change of endpoint identity. CIDR allowlists let the controlled machine limit which source networks may connect at all.
That last item is the one that changes how the tool should be deployed. A username and password restrict who knows a credential; a CIDR allowlist restricts where a connection can originate, which is the control that matters when the machine sits on a network you do not fully own.
The README adds the ordinary advice on top: expose the listening port only to trusted networks, use a strong unique password, and verify fingerprints through a separate trusted channel when you can. Capability-wise the fork keeps what people use RustDesk for: remote control, clipboard, audio and file transfer.
The Cargo package is still called rustdesk
The manifest is worth opening before you build anything. The package name is `rustdesk`, not `subnetdesk`, and it carries `default-run = "rustdesk"`. The version is 1.3.0, the edition is 2021, and the minimum Rust version is 1.75. The description string is the one place the fork names itself, reading as a LAN and VPN remote desktop.
The library is `librustdesk` and it builds as a cdylib, a staticlib and an rlib, which is what lets the same core serve the Flutter UI, a service binary and any embedding host. That binary exists: a `service` target built from `src/service.rs`, separate from the desktop app.
The dependencies are the upstream RustDesk shape rather than something rewritten. `scrap`, `hbb_common` and `base` are path dependencies into `libs/`, with `scrap` already enabling the wayland feature. The workspace also carries `build.rs`, a `Dockerfile`, an `entrypoint.sh`, a `vcpkg.json`, and directories for `appimage/`, `fastlane/`, `flatpak/`, `flutter/` and `web/`.
There is a feature named `software-update` that pulls in reqwest and ring. Its presence next to a product decision to remove automatic public updates is the kind of thing to check before you assume a build has no update path compiled into it.
drm-wake is a compile gate, not a preference
Most feature flags in this manifest are one line. `drm-wake` has a paragraph of explanation above it, and the reason is a good illustration of how a capture feature can have two different kinds of side effect.
The distinction the comment draws is between reading and writing. Everything else in the DRM backend reads, because capture takes a scanout image. The wake writes: it injects a single synthetic pointer event from the root service so that a compositor which has idle-disabled its outputs turns them back on. That is a different class of operation, so it gets its own switch.
The practical result is that `--features drm` builds the capture path with no wake code compiled in at all, rather than behind a runtime flag. If you are packaging this for an environment where you do not want the service moving a pointer, you can remove the behaviour from the binary rather than trusting a setting.
Other flags follow the same pattern: `flutter` pulls in flutter_rust_bridge, `hwcodec` and `vram` forward to scrap, `screencapturekit` forwards to cpal, and `unix-file-copy-paste` gathers x11-clipboard, x11rb, percent-encoding and once_cell.
Four platforms, a nightly tag, and a recommendation to skip it
Packages come from GitHub Releases, with a nightly release and GitHub Actions artifacts for the newest changes. Windows ships x86_64 and ARM64, as an `.msi` installer that is recommended plus a portable `.exe`. macOS ships Intel and Apple Silicon as a `.dmg`. Linux covers x86_64 and ARM64 with `.deb`, `.rpm`, `.AppImage` and `.flatpak`, plus an Arch package on x86_64. Android covers ARM64, ARMv7, x86_64 and universal as `.apk`.
The README's note on nightly builds is explicit that they are development builds and that the latest stable release is preferable for daily use, which is the advice to follow given the software grants you remote control of a machine.
The release record has an oddity worth knowing. The nightly tag is dated 2026-07-17 while v1.3.0 is dated 2026-08-27 and v1.2.3 is dated 2026-08-17, so a continuously rebuilt tag is older than the stable releases it sits beside. The last push to master is dated 2026-10-01, and the default branch is master with the licence file spelled LICENCE.
Building means Flutter, submodules, and a pinned native package workflow
The build is a clone with submodules and one script:
git clone --recurse-submodules https://github.com/zibo-chen/SubnetDesk.git
cd SubnetDesk
./build.py --flutter --hwcodec
The `--flutter` flag selects the Flutter desktop build and `--hwcodec` enables hardware codec support, which is the same feature the manifest forwards to scrap. The README says the build requires Rust, Flutter and platform-specific native dependencies, and then names the file that actually settles the question: the native package workflow under `.github/workflows/` is described as the source of truth for pinned tool versions, target architectures and packaging steps.
That is a sensible division. `build.py` is the entry point, and the workflow file is where the versions are pinned, so reading the workflow tells you what a release was actually built with.
For contributors the scope rule is stated just as plainly: check the existing issues first, and keep changes focused on the LAN and VPN first product direction.
The container build compiles CMake and vcpkg from source
The `Dockerfile` is a Debian bullseye slim image that assembles a full native toolchain before Rust is even installed. It installs the C and C++ compilers, nasm and yasm, GTK 3 development headers, clang, the XCB libraries for screen capture and shape, ALSA and PulseAudio development packages, PAM, GStreamer 1.0 and its base plugin set, OpenSSL headers, make, wget and ninja.
Two steps build tools rather than install them. CMake is downloaded as a 3.30.6 release tarball, configured, made and installed into `/usr/local`. vcpkg is cloned at tag 2023.04.15 with depth one, and four libraries are installed through it: libvpx, libyuv, opus and aom.
The image also creates an unprivileged user with passwordless sudo, fetches the Sciter GTK shared library from the c-smile SDK repository, and installs Rust through rustup with TLS 1.2 enforced. The entrypoint is copied in from `entrypoint.sh`. It is a heavy image, but it is heavy for a reason: a remote desktop has to compile against every codec and capture backend it intends to support.
Editorial conclusion
Use SubnetDesk in a home lab, an office LAN, a classroom, on-site support, or any private network joined by WireGuard, Tailscale or OpenVPN, where direct reachability is a given. It will not help you reach a machine behind a corporate NAT, because that is exactly the problem the removed rendezvous and relay solved. Before you deploy it, open the firewall for port 21118, set the CIDR allowlist on the controlled side, verify the fingerprint out of band on first contact, and read the AGPL terms if you intend to offer it as a service.
Frequently asked questions
What is SubnetDesk?
An independently maintained RustDesk fork for LANs, routed private networks and VPNs. It keeps remote control, clipboard, audio and file transfer, and is licensed AGPL-3.0. It is not an official RustDesk release.
What does SubnetDesk remove from RustDesk?
The public device ID path, rendezvous, relay, cloud account, proxy and automatic public-update paths. In their place it uses direct connections by IP address or hostname and automatic mDNS discovery on the LAN. It provides no internet rendezvous or relay service.
How do I connect to a machine with SubnetDesk?
On the controlled machine open LAN settings, set a username and password, and enable LAN discovery, with a default port of 21118. On the controller pick a discovered device or enter hostname:port or IP:port, then verify the fingerprint on first connection and connect.
What has to be true on the network for SubnetDesk to work?
Both devices must be able to route to each other, TCP port 21118 or your configured port must be allowed by the host firewall, and the controlled device's CIDR allowlist must include the controller's network. mDNS is only needed for automatic discovery; direct address entry works without it.
How does SubnetDesk protect the connection?
Passwords are persisted as Argon2id hashes rather than plaintext, device fingerprints give trust-on-first-use verification and reveal an unexpected endpoint change, and CIDR allowlists limit which source networks may connect. Traffic stays on the path between your two devices because no coordination service is involved.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/zibo-chen-subnetdesk)Star history chart for your README
[](https://hysenlabs.com/projects/zibo-chen-subnetdesk)Was this useful?