The default branch is develop, the README says take master
Go implementation of Ethereum proof of stake
At a glance
- What is it?
- Prysm is a Go implementation of the Ethereum consensus specification, built with Bazel and the Go module toolchain together and packaged with a distroless image. Its README asks coding agents to load a shared instruction file, and its Dockerfile says outright that it is not the image you should deploy.
- Who is it for?
- Prysm is the right project to read if you want to see a consensus client built the way a chain team builds one, with an action graph of generated code, a fake crypto mode for tests, and a build that fails on unknown make variables. Three things to know before you build it.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
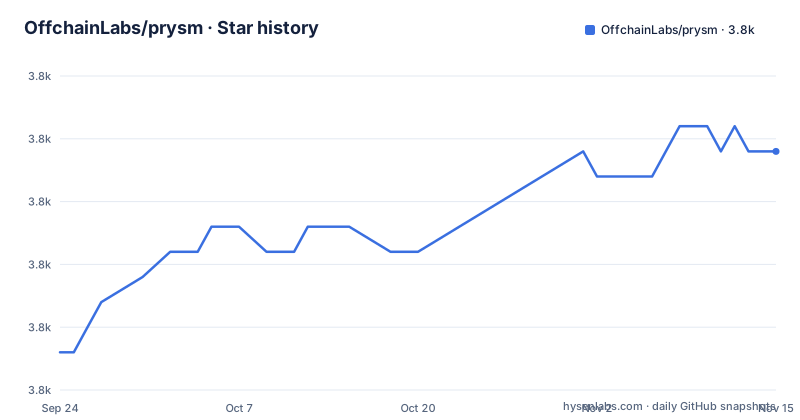
Star history
- OffchainLabs/prysm3,792 ★ · +8
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| OffchainLabs/prysm | 3.8k | 3.8k |
8 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The default branch is develop while users are told to take master
The contributing section says Prysm maintains two permanent branches and describes each in one line. master points to the latest stable release and is described as ideal for most users. develop is used for development, contains the latest pull requests, and is the branch developers should base their work on. The repository's default branch, in the metadata, is develop. So a clone with no branch specification gets the development branch, while the README's own recommendation for an ordinary user is the other one. That gap is deliberate in most projects with this layout, and it is worth stating out loud because it is the difference between running a released consensus client and running whatever landed most recently on a proof-of-stake chain.
The Dockerfile says it is not suitable for releases
The container file opens with a comment that answers the question most people have about a Dockerfile. It says this docker file builds a FAST, non-hermetic image for local iteration, naming Kurtosis and devnets as the cases, and that it is NOT suitable for releases. For a hermetic, reproducible image for releases, use make dist. Two details make that warning concrete. The whole source tree is copied before anything is built, with no dependency layer split, so any change to any file invalidates the compile. And the version is injected at link time from an ARG whose default is the literal dev:
  RUN --mount=type=cache,target=/go/pkg/mod --mount=type=cache,target=/root/.cache/go-build \
  CGO_ENABLED=1 CGO_CFLAGS="-D__BLST_PORTABLE__" \
  go build \
  -ldflags "-X github.com/OffchainLabs/prysm/v7/runtime/version.gitTag=$TAG" \
  -o "/out/$BIN" "./cmd/$BIN"
The module path in that flag ends in v7, matching the v7 release line.
Three binaries share one build argument
The usage comment gives the shape of the build: docker build with a BIN build argument taking beacon-chain, validator or prysmctl, and it states the default is beacon-chain. So one Dockerfile produces three different programs, and the selection is a positional path into the source tree at build time rather than a compile-time feature. The final image is gcr.io/distroless/cc-debian12, which is the C-enabled distroless variant rather than the static one, with the binary copied in as /entrypoint and set as the entrypoint directly. There is no shell, no package manager and no configuration file in the runtime image, so every setting the process needs has to arrive as an argument or an environment variable from outside.
Two KZG libraries and a C BLS binding explain CGO
The module file explains the build flags better than the build flags explain themselves. The requirements include both crate-crypto/go-kzg-4844 at version 1.1.0 and ethereum/c-kzg-4844/v2 at 2.1.8, so two implementations of the same proof system sit in one dependency graph. The BLS signature library is herumi/bls-eth-go-binary at 1.31.0, which is a binding to a C implementation rather than a pure Go one, and that is what makes CGO_ENABLED=1 necessary and what the -D__BLST_PORTABLE__ define is for. There is also consensys/gnark-crypto at 0.18.1, which is a proving system rather than a consensus dependency, and ethereum/go-ethereum at 1.17.4, the execution client, pulled in as a library. A consensus node that links all three of those is not a small binary.
The Makefile refuses variables it does not recognise
Build systems rarely validate their own input, and this one does. An ALLOWED_VARS list names the variables a caller may set: GO, DIST, TAGS, flags, mode, bls, platform, SOURCE_DATE_EPOCH, DOCKER_REGISTRY and DOCKER_TAG. Everything else that arrives from the command line is collected into BAD_VARS, and if that list is not empty the build stops with an error naming the offending variables and printing the allowed set. The same pattern guards the enum-like options: gen mode is checked against force and no-force, test mode against no-race and race, and the BLS backend against real and fake. A typo in a flag therefore fails immediately instead of silently selecting a default.
Tests can run against a fake BLS backend
The test variables show how wide the test matrix is. There are four test kinds, mainnet, mainnet-spectest, minimal and minimal-spectest, and eleven end-to-end scenarios: minimal, builder, web3signer, slasher, slashing, scenario, scenario-multiclient, postmerge, statediff, mainnet and multiclient. Those scenarios are grouped into three suites, and the mapping is written out by hand in the Makefile with a comment telling the reader to keep it in sync with the suites map in build/e2e/main.go. Two of the variables matter for how fast a change can be checked. Test mode defaults to no-race with race available, and the BLS variable defaults to real, with fake as the alternative, so signature-heavy tests have a path that skips the cryptography.
Bazel and the Go module toolchain sit in one tree
The top level mixes two build worlds without comment. There is go.mod, go.sum, a Makefile and a Dockerfile, and beside them WORKSPACE, BUILD.bazel, MODULE.bazel, MODULE.bazel.lock, deps.bzl, distroless_deps.bzl, .bazelrc, .bazelversion and .buildkite-bazelrc. The module path is versioned as github.com/OffchainLabs/prysm/v7, which is the Go convention for a project whose releases are v7.x, and the same convention appears in the link flag that stamps the version. Around them are three launcher scripts for different shells, prysm.sh, prysm.bat and prysm.ps1, a changelog/ directory alongside CHANGELOG.md, and documents for the two things a consensus client cannot skip: DEPENDENCIES.md and INTEROP.md.
The repository tells coding agents how to load its rules
One section of this README is addressed to tools rather than to people. Shared agent instructions live in .agents/AGENTS.md, and to use them the reader is told to point the agent's config file at it from the repository root, with this command:
echo '@.agents/AGENTS.md' > ./AGENTS.md # or ./CLAUDE.mdThat writes a single line containing an at-reference into a file at the root, either AGENTS.md or CLAUDE.md, rather than copying the instructions. Alongside it the tree holds .ethspecify.yml for specification annotations, fuzzbuzz.yaml for fuzzing configuration, nogo_config.json for a static analysis pass, a .well-known directory, and CI configuration spread across Buildkite, a GitHub Actions workflow for Go, a .travis.yml from the era before either, Codecov, DeepSource and golangci. The legal section is equally short: the licence is GPL-3.0 with LICENSE.md at the root, and the legal disclaimer is a link to TERMS_OF_SERVICE.md.
Editorial conclusion
Prysm is the right project to read if you want to see a consensus client built the way a chain team builds one, with an action graph of generated code, a fake crypto mode for tests, and a build that fails on unknown make variables. Three things to know before you build it. The Dockerfile is explicitly a fast non-hermetic image for local iteration and says to use make dist for releases. The default branch is develop, so a plain clone is not what the README calls the stable release. And the dependency list carries two KZG libraries and a C BLS binding, which is why the image needs CGO enabled and a portable define.
Frequently asked questions
What is Prysm?
A Golang implementation of the Ethereum consensus specification, developed by Offchain Labs. Its README calls it the core repository for Prysm, an Ethereum consensus implementation written in Go, and the project is licensed under the GNU General Public License v3.0 with the text in LICENSE.md.
How do you install Prysm?
The README contains no install command. It states that a detailed set of installation and usage instructions, plus breakdowns of each individual component, is available in the official documentation portal at prysm.offchainlabs.com/docs, and points at the releases page for the latest releases and upcoming breaking changes.
Which branches does Prysm maintain?
Two permanent branches. master points to the latest stable release and is described as ideal for most users, while develop is used for development, contains the latest pull requests, and is where developers should base their work. The repository's default branch is develop.
Which programs does the Prysm build produce?
beacon-chain, validator and prysmctl, chosen through the Dockerfile's BIN build argument, which defaults to beacon-chain. The build stamps the version through a linker flag on the runtime version package, and the file states it is not suitable for releases, directing release builds to make dist.
Does Prysm publish a changelog?
Yes. The README points at the releases page for details of the latest releases and upcoming breaking changes, the tree carries both a CHANGELOG.md file and a changelog/ directory, and the three most recent tags are v7.2.0, v7.1.8 and v7.1.7.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/offchainlabs-prysm)Star history chart for your README
[](https://hysenlabs.com/projects/offchainlabs-prysm)Was this useful?