ContextMenuMgr: intercept first, review second, three logs for a bug
Context Menu Manager Plus is a powerful utility that helps you manage the Windows right-click context menu and keep third-party apps from cluttering it with junk entries.
At a glance
- What is it?
- ContextMenuMgr manages the Windows right-click menu by defaulting newly detected third-party entries to disabled and queueing them for review, while optionally restricting registry writes so other software cannot add more. It discloses that a substantial part of its code is AI-assisted, runs as five separate processes including a Windows service, and acknowledges three projects it draws heavily on as bare URLs.
- Who is it for?
- ContextMenuMgr fits a Windows user annoyed by software adding menu entries without asking and who wants the additions reviewed rather than silently permitted, and it does not fit anyone who installs drivers frequently or who needs its metadata parsing to be exhaustive. Verify four things before you install it.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly C#, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
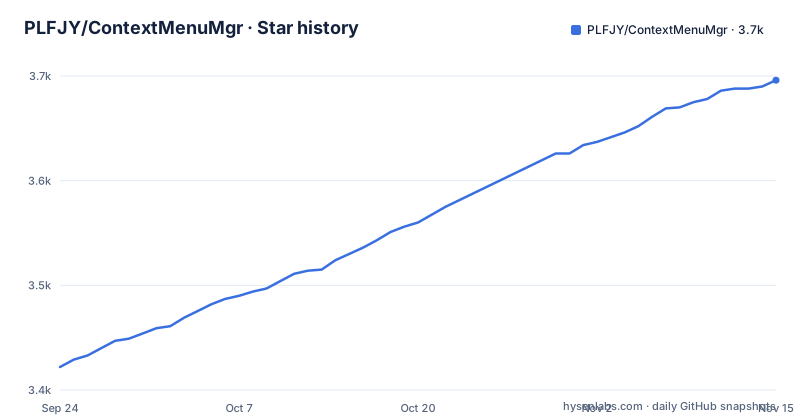
- PLFJY/ContextMenuMgr3,696 ★ · +274
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| PLFJY/ContextMenuMgr | 3.4k | 3.7k |
274 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
New entries are disabled by default, with a hedge attached
The design goal the file calls its most important is to intercept first and hand the decision to the user afterwards. When a new menu entry is detected it is not left to take effect: the project tries to disable or block it first and then places it on a pending review page. The user then picks one of three outcomes, which is where the design becomes interesting. One allows the entry and enables it. One keeps it registered but keeps it disabled, so the entry survives in a third state that is neither present nor active. One removes it, from the registry or from the review queue. Two observations sit underneath. The description of the central goal uses the word for best-effort twice, so even default-deny is a target rather than a guarantee. And the file is explicit that this is the difference between itself and an ordinary menu manager.
Registry protection will break some installers, and the features list says so
One feature restricts third-party software from writing the registry keys behind context menu entries, and the recommendation attached to it is to turn the restriction off temporarily before installing a driver or any software that writes menu items. That is an unusual thing to advertise inside a feature list, and it reframes the feature: it is interference, and interference has a cost that the operator pays. The notes section then gives nine separate reasons an expectation may fail, and they are specific rather than generic. Deletion, disabling and access-control changes can be blocked by system permissions, security software or Windows protection mechanisms. Some protected registry roots cannot have their access control lists modified by ordinary means, which the file attributes to Windows itself. Metadata parsing of icons, display names, command text and class identifiers is best-effort and does not claim full coverage, and the deep shell-extension analysis is best-effort too, where the file says failure is normal behaviour.
Five processes, and a bug report needs logs from three of them
The architecture is a set of cooperating processes rather than one program: a Windows service that does the scanning and the registry work, a desktop interface for interaction, a native tray host for notifications and the tray entry, and a separate analysis process whose whole purpose is to probe third-party shell extensions in isolation so that a failure there does not affect ordinary menu management. That last one is the interesting design decision, because probing a shell extension means loading someone else's code, and doing it in a process you can throw away is the sensible way to contain that. Inter-process communication is named-pipe based, and the repository adds a sixth project holding the contracts those processes share, which the README never mentions. The feedback section then asks for logs from the interface, the service and the tray host separately, plus the Windows version, the offending entry, reproduction steps and a screenshot.
Three build entry points and a solution format only the newest tooling reads
The root carries two Windows batch files and one PowerShell script as build entry points, one of the batch files named for the beta channel, and the release list shows the beta tag coming from that channel with a metadata segment and a commit hash pasted into the version name. The two documented package-manager installs are equally concrete:
winget install PLFJY.ContextMenuMgrPlusscoop install PLFJY/ContextMenuMgrPlusA stable release tag in the same list is named with a plain suffix instead, so the same version number appears twice in two naming styles. The solution file uses the newer XML-based solution format rather than the long-standing text one, which is the right choice for a project on the newest .NET and also means older toolchains cannot open the solution at all. Centralising build properties in one shared file is done properly. Everything about the build is Windows-only in practice, and the file that would explain how to run any of it is a link away.
One page is installation and one file is everything else
The README is an install page. Architecture, the development guide, build and release procedure and troubleshooting all live in a single document under the documentation directory, linked once and never summarised. That is a defensible split, but it means the page a reader lands on says nothing about how the thing works, and the page that would has to be fetched separately. Two smaller things about the front page. Its own contents list contains one anchor that differs from the others in a way that will not resolve, carrying an invisible variation character that its heading happens to include while the other headings lose their emoji entirely. And in place of a build or test badge there is a link to a third-party trending-repository service with a hardcoded numeric identifier.
Heavily derived from three projects, credited as three bare URLs
The acknowledgements say the project's code draws heavily on the following projects, and then list three URLs with no names, no descriptions and no prose of any kind. Two of the three are themselves context menu managers for the same operating system, including the one this project's name is a variation on, and the third is a desktop interface library. So the lineage of a general-purpose licence project that describes itself as heavily based on three others is expressed as a list of links. Nothing about that is unlawful, and a permissively licensed codebase assembled from permissively licensed code is ordinary. It does mean that anyone reasoning about where a line of code came from has three links to follow rather than an account of what was taken and adapted from where, which is a sharper question than a reader of the file can answer.
The file discloses AI-assisted code and then invites agents to contribute
The second thing on the page is a warning box, and it is unusual enough to quote its substance. It says a substantial part of the code was generated with AI assistance and has since had continuing manual work, integration and refactoring, but may still contain omissions, insufficient handling of edge cases, or behaviour that does not fully match expectations, and it invites issues with reproduction steps, logs, screenshots and system versions if you find any. Three sections later, the contribution section says the project ships development documentation alongside two agent instruction files and that mainstream agent tools can be used directly to contribute to it. Those two positions are consistent, and almost nothing else in the ecosystem states them in that order. The repository root also carries an IDE's project directory, which is per-developer local state rather than shared source.
Five names for one program, and a video as the homepage
The same program carries several identifiers. The repository has one name, the product calls itself a third thing in its display name, the package managers use a fourth form with their own separators, the solution file uses a fifth, and the recorded homepage is a link to a video on a video-sharing site rather than to any documentation. The two package manager routes also differ in where they get their package from: one resolves a published listing, while the other requires adding a bucket that lives in a separate repository the user must trust before installing. The file also lists a mirror of the repository twice, once as a link and once as plain text, which is the kind of duplication that appears when a section is assembled rather than written. None of it blocks an install; all of it makes finding the right artefact take a moment.
Editorial conclusion
ContextMenuMgr fits a Windows user annoyed by software adding menu entries without asking and who wants the additions reviewed rather than silently permitted, and it does not fit anyone who installs drivers frequently or who needs its metadata parsing to be exhaustive. Verify four things before you install it. Read the notes section rather than the feature list, because the file lists nine separate reasons your expectation may not hold and says outright that failure is normal in one of them. Turn the registry protection off while installing software, since the same file recommends that. Expect to supply logs from three processes when reporting a problem, and expect to be told the logs are more useful than the interface. And check what the install scope is on the executable route, since the settings page can also install, repair or remove the Windows service itself.
Frequently asked questions
What is PLFJY/ContextMenuMgr?
A Windows tool for managing the right-click menu, described as more than a toggle switcher. It manages the classic menu entries and the newer Windows 11 menu entries side by side, detects entries added by third-party software, can restrict third parties from writing the menu-related registry keys, and offers search, per-page filtering and deeper analysis of individual entries. It runs as a set of cooperating processes, including a Windows service.
How does ContextMenuMgr handle new context menu entries?
By defaulting to no. When a new entry is detected the tool tries to disable or block it first and queues it for review rather than letting it take effect. The user then allows and enables it, keeps it registered but disabled, or removes it from the registry or the queue. The file describes the interception itself as best-effort, so the default-deny behaviour is a target rather than a guarantee.
How do I restore the old context menu in Windows 11?
This tool does not replace the newer menu with the older one. It manages both systems side by side, and the file lists special entry points such as the new-item menu, the send-to menu and the shortcut-key menu separately because they live in different registry locations. It also notes that user-level, system-level, packaged and class-identifier entries do not all behave the same way.
Can I install ContextMenuMgr with WinGet or Scoop?
Both, with separate identifiers for the stable and beta channels on each. The Scoop route needs one extra step first: adding a bucket, which lives in a different repository from this one. The executable route instead points you at the assets attached to a release and tells you to pick the file matching your processor architecture and install scope, naming the self-contained 64-bit build as the usual choice.
What are the known limitations of ContextMenuMgr?
The file lists nine. Operations can be blocked by permissions, security software or Windows protection, and some protected registry roots cannot have their access lists modified at all. Metadata parsing is best-effort and does not claim full coverage, the deeper shell-extension analysis is best-effort where failure is described as normal, and the different categories of menu entry do not behave identically. Enabling the registry restriction can stop installers from writing menu entries, and in edge cases the logs are said to be more useful than the interface.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/plfjy-contextmenumgr)Star history chart for your README
[](https://hysenlabs.com/projects/plfjy-contextmenumgr)Was this useful?