laravel-log-viewer: the one route you add is the only door, and it has no lock
:dromedary_camel: Laravel log viewer
At a glance
- What is it?
- rap2hpoutre's Laravel log viewer is a small composer package that renders your application's log file as a web page. It registers no routes of its own, so the entire access model is one line you write, at a guessable path, with no middleware attached and no authentication mentioned anywhere in the file.
- Who is it for?
- laravel-log-viewer fits a developer who wants to read an application log in a browser during development, and it fits an application whose log file is something you would be content to publish. Verify four things before you add the route.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Activity is slowing. The repository last received commits 6 months ago.
- What is it written in?
- Mainly PHP, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
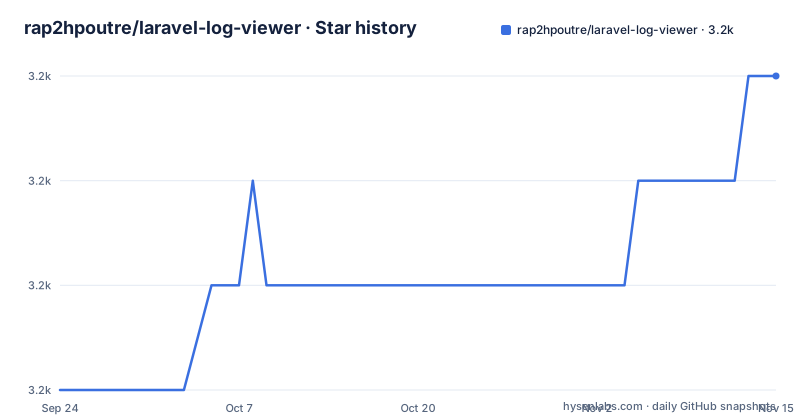
- rap2hpoutre/laravel-log-viewer3,195 ★ · +3
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| rap2hpoutre/laravel-log-viewer | 3.2k | 3.2k |
3 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The install is one GET route with no middleware attached
After the composer command there is exactly one step, and it is the step that decides everything about who can read your logs:
Route::get('logs', [\Rap2hpoutre\LaravelLogViewer\LogViewerController::class, 'index']);A plain GET, at a path made of one common word, with no middleware group and no authentication of any kind. The file does not mention authentication, does not show an alternative with a middleware call, and does not say what happens when the request is unauthenticated. What the page renders is your framework's log file, which in most applications accumulates request paths, identifiers, query values and exception detail. None of that is the package's fault; it is the consequence of the documented install. The reason the line is yours to write is stated deliberately in the summary, which says the package registers no vendor routes of its own. That is the right default for a package like this, and it puts the access decision entirely in the hands of whoever pastes the line in.
No public assets and no vendor routes, both in a single line
Four claims appear in one sentence and two of them are architectural. No public assets means nothing is written into your public directory, so there is no asset path to guess and no publish step for styling. No vendor routes means the package does not silently mount itself anywhere, which is why the install is a manual route rather than a service-provider side effect. Both are good choices for a package whose whole job is exposing internal state, and together they mean the attack surface is exactly the route you add and nothing else. The other two claims are that it works with or without log rotation, and that it is private in the sense of not phoning anywhere, though the file does not expand on either. What it does not say is where rotated files end up, which channel it reads, or what the page shows when the log is empty.
The configuration file is publishable and no option is described
The advanced section has two recipes and both use the framework's vendor publish command. The first publishes the view file using a views tag. The second publishes the configuration file and omits the tag entirely, so what it publishes is whatever that provider has tagged rather than one named file. The destinations are stated for both, one under a vendor views directory and one under the configuration directory. What is missing is the part that would make publishing useful: not a single option is described. No environment variable, no key, no default value, no statement of what the file can change. If your log is in a non-default place, or you want a different date format, or you want to bound how much is read, the file gives you no way to find out short of reading the published file yourself.
One troubleshooting entry, and it is about the framework's view cache
There is a single thing that can go wrong according to the file: an argument exception thrown from the framework's own view finder, attributed to configuration caching, fixed by clearing the configuration cache. That is a useful entry and it is the only one. Nothing is said about the log file not existing yet on a fresh application, about the storage directory not being readable by the web user, about using a log channel other than the default one, about what happens after rotation has moved the current file, about a log large enough to be slow to read, or about the log being empty. A viewer whose failure modes are all upstream of it may reasonably document only its own, and this is a case where the failure modes are almost entirely upstream.
Three identical badges, one continuous integration service, and no changelog
The badge row opens with three links to the same package page. They were presumably three different badges whose image references were flattened, so what renders is three links to one destination. The fourth points at a hosted analysis service on the master branch, and the fifth at a social account. There is no badge for a workflow-based continuous integration service, and the tree contains a test configuration and a test directory, so tests exist and are not advertised. The tree also has no changelog file. That matters more here than it would elsewhere, because the summary explicitly sends readers to the releases page for guidance on which version suits their framework version. The version history is therefore only in the tags, and the one piece of context in the tags is a release note on a single old tag about framework compatibility.
A new major and a patch release seventeen hours apart
The three newest tags are a major, a patch, and an older compatibility release. The major went out on 2026-05-11 and the patch on 2026-05-12, seventeen hours later, with the patch sharing its exact timestamp with the last push. Before that, the compatibility tag is dated 2025-03-10 and carries a note naming the framework version it added support for. So framework support moved from one release to two inside a single major version, and the version number does not track the framework version at all. The practical consequence for an installer is that an unconstrained require pulls the current major, which needs a recent framework, and the only guidance on which release suits which version is a sentence pointing at the tag list.
A heading that ends in a colon with nothing after it
The file has a section headed with a partial question, followed by one sentence describing the package as a small log viewer for the framework, followed by a sentence ending in a colon and nothing after it, where an image would be. That is the whole visual demonstration of what the tool produces. Elsewhere the prose has similar looseness: the project it credits as its inspiration is named with a misspelled first name while the link points at a different spelling of that name, and the parenthetical notes that the inspiration worked only with one framework version from many years ago. Neither is a defect. Together with the empty image slot and the section heading that is a fragment, they describe a front page maintained in a hurry by someone who cares about the code.
Editorial conclusion
laravel-log-viewer fits a developer who wants to read an application log in a browser during development, and it fits an application whose log file is something you would be content to publish. Verify four things before you add the route. Decide who can reach it, because the documented line carries no middleware and the package deliberately registers none of its own, so that single line is the whole access model. Read the log first, because what the page renders is your framework's log and that file routinely contains request paths, identifiers and exception detail. Confirm the configuration options yourself by publishing them, since the file tells you the file exists and nothing about what any option does. And check what happens when rotation has run, because the file says it works with rotation and does not say where rotated files appear.
Frequently asked questions
How do I install the laravel log viewer?
With composer, then one line added to your web routes file pointing a GET route at the package's controller. The file calls that the whole install: there are no public assets to publish and the package registers no routes of its own. For older framework versions and for Lumen it directs you to earlier releases and states that those are no longer maintained.
Does rap2hpoutre/laravel-log-viewer ship with authentication?
Nothing in the file mentions authentication. The documented route is a plain GET with no middleware group, and the package deliberately registers no routes of its own, so that single line is the only access point and whoever writes it decides who can reach it.
Which Laravel versions does rap2hpoutre/laravel-log-viewer support?
Laravel 12 and 13 on the current line. An older release carries a note naming the framework version it added support for, and the file states that earlier framework versions and Lumen are no longer maintained and directs users to the older releases for those.
What can I configure in rap2hpoutre/laravel-log-viewer?
The file tells you a configuration file exists and can be published into the configuration directory with a vendor publish command, and that a view file can be published for styling. It does not name a single option, so the contents of the published file are the only documentation of what can be changed.
What should I do when the Laravel log viewer shows an error?
There is one troubleshooting entry in the file: an argument exception from the framework's view finder, attributed to configuration caching, fixed by clearing the configuration cache. Nothing is said about missing log files, permissions, a non-default log channel, rotated files or very large logs.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/rap2hpoutre-laravel-log-viewer)Star history chart for your README
[](https://hysenlabs.com/projects/rap2hpoutre-laravel-log-viewer)Was this useful?