overcommit's install backs up your hooks, its force flag overwrites them, and required beats both skip variables
A fully configurable and extendable Git hook manager
At a glance
- What is it?
- A Ruby gem that installs Git hooks into every repository you create or clone, with hooks configurable per repository and stored in source control. Four environment variables control skipping, disabling and colour, and one configuration option makes all of them stop working.
- Who is it for?
- Overcommit is worth adopting if your team commits from several machines and wants the same checks everywhere, because it solves the two problems that stop people doing that: a hook that is easy to install per machine is easy to forget, and a hook whose configuration lives only on one developer's laptop does not travel. Four things to know.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 4 days ago.
- What is it written in?
- Mainly Ruby, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
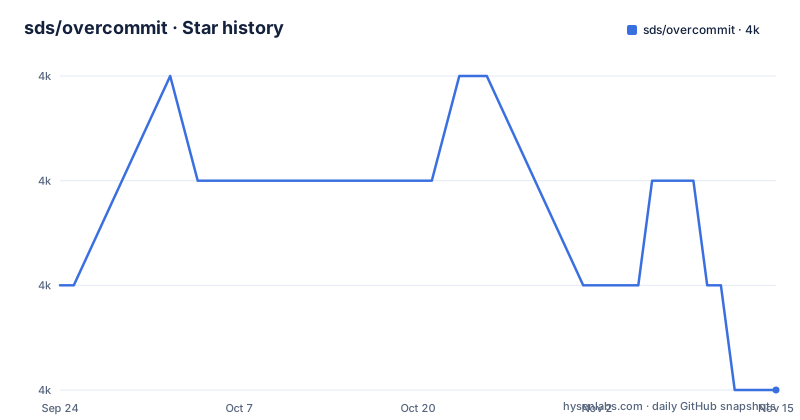
- sds/overcommit4,003 ★ · -1
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| sds/overcommit | 4k | 4k |
-1 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Four environment variables, and one option that beats two of them
The escape hatches are all in the environment and all documented. One names hooks to ignore. Another names the only hooks you want to run, for people who prefer a whitelist. A third turns the whole tool off, for scripts of your own that invoke version control internally and should not trigger anything. The fourth forces colourised output on or off independently of whether the output is going to a terminal, which is what you want in a continuous integration log. Then there is the escape hatch for the escape hatches: mark a hook as required in its configuration and the first two stop working, you get a warning saying so, and the hook runs anyway. For a tool whose entire purpose is to be inconvenient when a check fails, that is the right control to hand a team, and it lives in a configuration file rather than on a command line.
Signature verification exists, and so does a switch to turn it off
The table of contents lists signature verification among the configuration options, and it also carries a security section whose visible entry is how to disable signature checking. That pairing is the security story of the whole project in miniature. The hooks are plugin code that the tool loads and runs on your commits, so the question of whether that code can be trusted is the question of who gets to put code on your machine at commit time, and a signing check is the answer to it. Disabling the check is a documented and supported operation, which is the right thing to do on a machine with no network and the wrong thing to do on a laptop that clones all day. Reading those two entries next to each other tells you more about how the project thinks about trust than either entry does alone, and it is unusual to find either one written down at all.
Installing backs up your hooks, and the force flag overwrites them
By default installation stops when existing hooks would conflict. The `--force` option permits installation to proceed and overwrite them. The README says hooks that Overcommit replaces are backed up and can be restored with `overcommit --uninstall`. If the existing hooks are important, keep a separate copy and verify restoration in a test repository before changing a shared workflow.
The automatic setup is one exported variable you have to remember
To get hooks into every repository you create or clone from then on, the documented approach is to export the tool's template directory into an environment variable, and the file says to add that to your shell environment. Git then uses that directory as a template when it populates a new clone, which is a neat trick: it means no per-repository setup step at all. If the variable is not set, or if the shell you happen to be using does not read the file you put it in, every new repository arrives with no hooks and nothing reports an error. The section also handles the case where you already have a template directory of your own, and the advice there is to copy the contents across rather than replace the variable, which is the more careful of the two instructions in that part of the file. The two commands are short, and the export is the one people forget:
export GIT_TEMPLATE_DIR="$(overcommit --template-dir)"A Ruby floor of 2.6 and best effort on Windows
The requirements section is one line: the project aims to support a Ruby runtime floor on Unix-like systems, with best effort on Windows. The word aims is doing quiet work there. A gem whose hooks run on every commit is exactly the kind of software where the platform you develop on is the platform that matters, and the project says so rather than implying parity. The dependency model is the other half of the same story. Hooks call out to third-party tools, so the machine where you commit has to already have whatever you configured, for example the stylesheet linter named as the example, whose gem is maintained by the same author. Most hooks print a warning when a required executable is missing rather than failing, which is friendly and also means a misconfigured machine silently checks less than you think it does.
The project runs its own hooks, committed to the tree
The repository carries a directory of hook scripts and a template directory beside them, plus its own hook configuration file at the root. That last one is the repository-specific configuration the README describes as living in source control, so the project dogfoods the thing it ships: its own commits go through the hook manager, configured by a file anybody can read in the tree. That is a stronger demonstration than documentation, and it has a practical side effect. The configuration file at the root is the worked example a new user will actually read, rather than one written for a manual, and it doubles as the answer to what a sensible starting configuration looks like. It also means the tool's own hook code is visible in the repository rather than hidden in a gem, which is what makes the signature question above answerable by inspection.
Two executable directories and a record of unfixed lint
The layout has a scripts directory and a second one beside it, which is more structure than a project this size usually needs, and suggests the split between commands and helpers was decided once and then kept. There is a configuration directory for the built-in hook definitions, a specification directory, a gemspec, a rake file, a gemfile and a changelog. Two small things from the root. The licence file is named with the word licence in it, which is a habit rather than a convention. And there is a lint tolerance file beside the lint configuration, which is the usual way a project records what it has decided not to fix yet. One of the four badges at the top of the README links over plain http to a documentation-coverage service while the other three point at the package index, the test workflow and the coverage service.
Editorial conclusion
Overcommit is worth adopting if your team commits from several machines and wants the same checks everywhere, because it solves the two problems that stop people doing that: a hook that is easy to install per machine is easy to forget, and a hook whose configuration lives only on one developer's laptop does not travel. Four things to know. Read the interaction between the install flag, the force flag and the uninstall flag before you run it in a repository that already has hand-written hooks. Decide where the trust boundary sits, because the hooks are plugin code that runs on every commit and the tool has both a signature check and a documented switch to disable it. Mark hooks you care about as required, because that single option is what makes the skip variables stop working. And remember the automatic installation path is an exported environment variable in your shell profile, so a repository cloned from a shell that does not read that file will have no hooks at all. Licence terms are MIT, the Ruby floor is 2.6, and the last push is dated 2026-09-06.
Frequently asked questions
What does overcommit do?
It manages and configures Git hooks. Beyond the standard hook types you can define hooks specific to a repository and store them in source control, and add existing hook scripts without writing Ruby. Installing it replaces a repository's hooks, backing up whatever it replaces.
How do I install overcommit?
With the gem installer from RubyGems. The file strongly recommends an environment where installing a gem does not need root privileges, and suggests a Ruby version manager. You then run the install flag in a repository, which backs up any existing hooks and can be reversed with the uninstall flag.
How do I skip an overcommit hook?
Name it in a skip environment variable before committing, or name the only hooks you want in an alternative variable. A hook can also be marked as required in its configuration, in which case both mechanisms stop working, a warning appears, and the hook still runs.
What do the OVERCOMMIT_DISABLE and OVERCOMMIT_COLOR variables do?
The first turns the hook manager off entirely, for a command of your own that runs version control internally and should not trigger hooks. The second forces colourised output on or off independently of whether the output is going to a terminal, which is what you want in a CI log.
Does overcommit check the code of its hooks?
The README lists signature verification among the configuration options and also documents how to disable signature checking in its security section. That pairing is the relevant part: hook code runs on your commits, and a signing check is what determines whether it should be trusted in the first place.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sds-overcommit)Star history chart for your README
[](https://hysenlabs.com/projects/sds-overcommit)Was this useful?