searx is unmaintained: pinned 2022 dependencies and a privacy-first stance on bug reports
Privacy-respecting metasearch engine
At a glance
- What is it?
- searx is a Python metasearch engine under AGPL-3.0 whose own README now announces that its author has moved on to a different tool and that searx is no longer maintained. What the repository still documents is a stable, fully pinned codebase, and what it no longer offers is anyone to fix a broken upstream engine.
- Who is it for?
- searx makes sense for someone who wants to read a frozen, well documented Python codebase, run it locally on their own machine, and accept that every upstream engine problem is theirs. It does not make sense as a base for a public instance that needs current engines, security patches or issue response, because the project has said it is no longer maintained and its newest tag is v1.1.0 from August 2022.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Activity is slowing. The repository last received commits 6 months ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
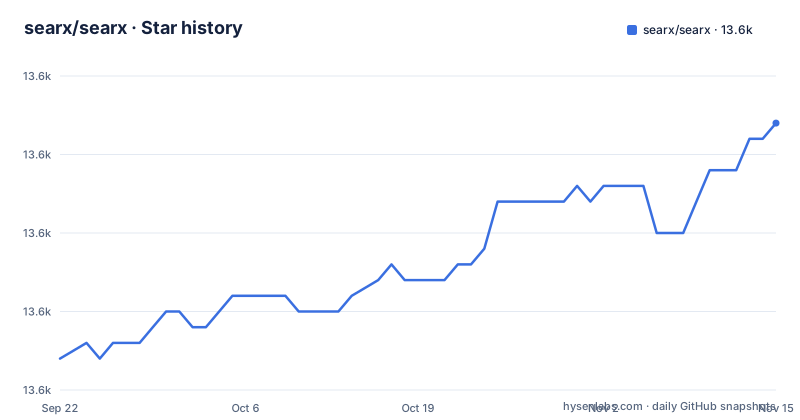
- searx/searx13,567 ★ · +15
| Repository | 2026-09-22 | 2026-11-15 |
|---|---|---|
| searx/searx | 13.6k | 13.6k |
15 Stars in the last 54 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The README opens with a handover notice instead of an install guide
The first block of text in README.rst is an announcement titled IMPORTANT ANNOUNCEMENT, and it is the project's current status. The author says he has shifted his active development focus away from searx to a new search tool he has been building, called Hister, and closes with the flat statement that searx is no longer maintained, followed by thanks to everyone who contributed and used it. His reasons are architectural rather than personal. Results are only as good as what upstream engines expose, privacy guarantees are partial because requests still leave your machine, relevance ranking is limited to what scraped results provide, and there is no persistent memory of what you have already read or found useful. The repository metadata agrees with the notice: the declared homepage is hister.org rather than searx, while the logo in the file still points at the older searx.github.io address.
Maintenance mode was the wrong question, and the file answers it
The FAQ section handles the status question head on. Under is searx in maintenance mode, the answer given is no, immediately followed by the line that searx is no longer maintained. Those are different states, and the difference decides how you plan an install. A project in maintenance mode still triages issues and still ships fixes, while an unmaintained one does not. The dates back the second reading. The three most recent releases are v1.1.0 from 7 August 2022, 1.0.0 from 27 March 2021 and v0.18.0 from 14 December 2020, while the last commit on the default branch master is dated 14 May 2026. setup.py still advertises Development Status :: 4 - Beta, which described the project when written and says nothing about who handles an engine that upstream changes tomorrow.
Two console scripts ship, and only one of them serves requests
setup.py registers two console scripts. The first maps to the web application entry point, and the second maps to the engine checker:
searx-run = searx.webapp:run
searx-checker = searx.search.checker.__main__:main
The checker is the half that matters for a self-hosted install, because every result searx shows comes from a third-party engine that can change its markup, throttle an address or start returning something unrelated. The Makefile exposes it as a target you invoke yourself, with a verbose flag and a per-engine form that takes an engine name with underscores turned into spaces:
./manage pyenv.cmd searx-checker -vFor an operator the consequence is plain. With no release train, the moment your instance starts returning empty or wrong results is a moment only you are watching for.
Every dependency is pinned and none of them moved after 2022
requirements.txt is a list of exact pins rather than ranges: Brotli==1.0.9, babel==2.11.0, certifi==2022.12.7, flask-babel==2.0.0, flask==2.2.2, jinja2==3.1.2, langdetect==1.0.9, lxml==4.9.2, pygments==2.12.0, python-dateutil==2.8.2, pyyaml==6.0, requests[socks]==2.28.2 and setproctitle==1.3.2. setup.py reads that file for install_requires and requirements-dev.txt for the test extra, so those pins are the install contract rather than a suggestion. The Dockerfile pins the operating system the same way, building from alpine:3.15 and installing that same requirements file. Pinning buys you reproducibility, and with nobody bumping versions upstream it is the only reproducibility on offer. It also means a pinned package that no longer builds on your Python version or your architecture is your problem to solve, with no patch to wait for and no guidance in the file about how to move the pins forward.
Configuration lives in volumes the image deliberately never bakes in
The Dockerfile declares VOLUME /etc/searx and VOLUME /var/log/uwsgi, then points the environment at files inside the first one: SEARX_SETTINGS_PATH=/etc/searx/settings.yml and UWSGI_SETTINGS_PATH=/etc/searx/uwsgi.ini. The entrypoint runs under tini as /sbin/tini -- /usr/local/searx/dockerfiles/docker-entrypoint.sh, and the service listens on 8080. Build arguments named TIMESTAMP_SETTINGS, TIMESTAMP_UWSGI and VERSION_GITCOMMIT set the modification times of searx/settings.yml and dockerfiles/uwsgi.ini via touch and stamp a git revision into searx/version.py, and the build pre-compresses every html, css, js, svg and font file under searx/static with gzip -9. searx/settings.yml is listed in the package data, and the README points administrators to the admin handbook.
The bug report you will never file is a deliberate privacy decision
The file explains why fewer bug reports reach the issue tracker, and the reason is design rather than neglect. It says users rather not report bugs, because reporting one publicly would reveal which engines they use and what search query triggered the problem. The project states that it accepted this challenge, that users must come first rather than the software, and that it is willing to compromise on the number of issue reports to avoid violating user privacy. The disagreement with the fork grows out of the same position: SearxNG added engine metrics that collect more information to make engine maintenance easier, while searx declines engine detailed monitoring and declines a new user interface that relies on Javascript. The consequence for you is that a broken engine in your own instance has no route through the tracker, because the design makes the most detailed bug report the one nobody wants to write.
The fork gets a comparison, and both positions sit in the same file
SearxNG receives its own section rather than a dismissal. It is a fork of searx created by a former maintainer, and the stated cause is that the majority of maintainers at the time did not consider the new proposed features privacy respecting enough, with engine metrics called out as the most significant issue. The fork's side of the ledger: rolling releases, dependencies updated more frequently, engines fixed faster, an easy path to running your own public instance with performance and metrics monitoring, and a simpler maintenance story for an instance administrator. searx's side: the fork is under heavy refactoring with dependencies updated even where unnecessary, which raises the risk of regressions, and this project prefers stability to moving fast and breaking things. No measurement appears in either column, so treat this as stated preference rather than result. Choose by asking whether you need fixes faster or a codebase that stops changing.
make run opens a browser on port 8888 and that is the whole developer loop
The Makefile routes everything through a wrapper, with MTOOLS set to ./manage at the top. The developer loop is two targets: install performs a developer install of searx into a virtualenv, and run depends on it. The run target opens http://127.0.0.1:8888/ in your browser and starts the application with debugging enabled:
SEARX_DEBUG=1 ./manage pyenv.cmd python ./searx/webapp.pyThat debug flag is a local developer convenience the shipped container does not set, so do not carry it into a deployed instance. The test side is thorough for a repository of this size: ci.test chains test.pep8, test.pylint, test.unit and test.robot, and test.sh shellchecks a fixed list of scripts including utils/brand.env, utils/lib.sh, utils/filtron.sh, utils/searx.sh, utils/morty.sh, utils/lxc.sh and utils/lxc-searx.env. A green local run tells you your checkout is internally coherent. It tells you nothing about whether the engines your queries reach still answer, which is the failure nobody is left to report.
Editorial conclusion
searx makes sense for someone who wants to read a frozen, well documented Python codebase, run it locally on their own machine, and accept that every upstream engine problem is theirs. It does not make sense as a base for a public instance that needs current engines, security patches or issue response, because the project has said it is no longer maintained and its newest tag is v1.1.0 from August 2022. Before you install, read the announcement at the top of the file, check the pins in requirements.txt against your Python version, and decide whether you want a system you own or the rolling releases and engine metrics the fork offers.
Frequently asked questions
What happened to searX?
Its author shifted active development to a new tool called Hister, and the README states that searx is no longer maintained. The last commit on master is dated 14 May 2026, while the newest release tag is v1.1.0 from 7 August 2022.
How does searX work?
It is a metasearch engine, which the announcement says makes it fundamentally dependent on third-party search engines. Results are only as good as what upstream engines expose, and privacy guarantees remain partial because requests still leave your machine.
how to install searx
Installation instructions live in the admin handbook linked from the file rather than in the file itself. The repository ships a Dockerfile built from alpine:3.15 on port 8080, and the Makefile offers install as a developer install into a virtualenv.
how to use searx
For ready to use instances the file points at searx.space, and for everything else it links user, admin and developer handbooks on the project homepage. It also says searx targets privacy conscious users who run their own instances locally instead of using public ones.
searx vs searxng
SearxNG is a fork of searx made by a former maintainer because the maintainers at the time rejected the proposed features as not privacy respectful enough, engine metrics being the most significant issue. The fork ships rolling releases and faster engine fixes; searx argues for stability and refuses engine detailed monitoring.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/searx-searx)Star history chart for your README
[](https://hysenlabs.com/projects/searx-searx)Was this useful?