Hermes Agent Control Room is a folder of runbooks that installs nothing by itself
Control Room-first template for managing Hermes agents from one VPS agent to specialist teams and orchestrated workflows
At a glance
- What is it?
- A public template for running Hermes agents off one VPS, organised as four levels from a single agent to an orchestrated team. Its whole installation story is three English sentences aimed at an agent, and its own folder tree disagrees with the skills it promises.
- Who is it for?
- Treat hermes-agent-control-room as a document to argue with rather than a system to install: it hands an agent a structure, and the structure is only as good as what you put in the runbooks.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Activity is slowing. The repository last received commits 6 months ago.
- What is it written in?
- Mainly Shell, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
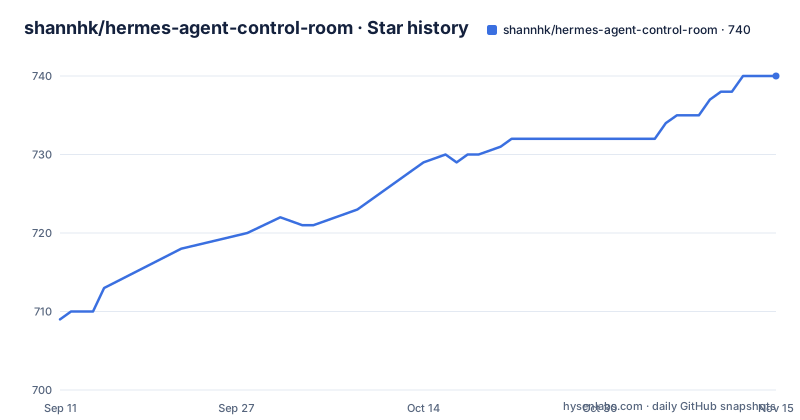
- shannhk/hermes-agent-control-room740 ★ · +31
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| shannhk/hermes-agent-control-room | 709 | 740 |
31 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The Control Room is a sidecar of documents, not an agent
The premise is a deliberate narrowing. What you build first is a control plane, described as a sidecar repository or folder that documents and governs your Hermes agents, and the text is explicit that it is not an agent itself. Instead it is the system map, the operating manual, the registry, a runbook library and a recovery notebook. The growth path it proposes is one line:
one agent -> direct specialists -> orchestrator -> automated agent teamWhat ships is folders: agents/ with a single .gitkeep, docs/, shared/, templates/, skills/, examples/ and assets/. That matches how the repository is classified, since it is recorded as primarily Shell while nothing at the top level is a script or a binary, only .gitignore, LICENSE, README.md and those directories. The templates directory is the concrete part: inventory.md, docker.md, env-map.md, runbook.md and backup.md per agent, plus docker-compose files for an agent and for an orchestrator, and agents.yaml with task and result templates for the bus.
Four levels, and the ordering is the whole opinion
Level 1 is a Control Room plus one registered agent, aimed at one personal agent, VPS setup documentation, Docker migration planning and keeping runbooks tidy, and the text says plainly that you do not need an orchestrator or a task bus yet. Level 2 adds role-specific specialists that you talk to directly, with hermes-life, hermes-seo, hermes-dev, hermes-cmo and hermes-ops as the named examples, while the Control Room documents all of them. Level 3 adds hermes-orchestrator as an optional front door that can route and synthesise, and carries the one hard warning in the document: it should not become a giant agent holding every credential. Level 4 adds recurring workflows, audits, backup checks, task routing and optional gateway calls. The same rule is stated twice, once in the core idea as automate only after the manual system works and again in Level 4, which is either emphasis or an admission that the order gets skipped.
Seven skills are described and three skill folders appear in the tree
The bundled skills section names seven: create-vps, which creates a fresh Hetzner VPS with an SSH key, an SSH alias and a local provisioning folder; setup-control-room, which bootstraps an SSH-accessible VPS with Node, Claude Code, Codex, Docker, Hermes Agent and this template; agent-control-room for managing the docs and agent folders; agent-task-router for handing work from an orchestrator to specialists through a bus; agent-registry-manager for the registry; agent-backup-manager, which is designed to audit per-agent backups without committing secrets; and agent-security-auditor, whose description stops in the middle of a word at Check ports, dashboards, SSH, Do. The suggested folder structure disagrees with that list. Its skills/ directory shows exactly three entries, create-vps/, setup-control-room/ and agent-control-room/, so the four skills that make delegation, registry upkeep, backup and security work are absent from the tree a newcomer is told to copy.
Setting it up means saying three English sentences to a model
There is no installer here, and the document is upfront about it: the repo does not run code when opened, it gives your agent the instructions, templates and skills, and you still have to ask the agent to run the setup flow. Option A is built entirely on prompts meant to be pasted into a chat with an agent that can read GitHub or a local clone:
Read this repo and help me set up an Agent Control Room.
Start with docs/starter-guide.md and the setup-control-room skill.
or the shorter version, Use setup-control-room to bootstrap my VPS, and for a fresh machine the chain Use create-vps, then chain into setup-control-room. Option B assumes you already have an Ubuntu or Debian VPS you can reach. The two access styles are kept deliberately separate as well, since the Control Room path, the direct path to a named specialist, and the orchestrated path through the task bus are all drawn as first class, and you are told you are never locked into one workflow.
The manual route is five commands and five files you fill in yourself
Option B is the only path written as shell. You connect as root, clone the repository to a fixed path, read the guide, then create an agent folder and drop the templates into it:
ssh root@YOUR_SERVERgit clone https://github.com/shannhk/hermes-agent-control-room.git /root/agent-control-room
cd /root/agent-control-roomcat docs/starter-guide.mdmkdir -p agents/hermes-life
cp templates/agent/*.md agents/hermes-life/What happens next is typing. Five files under agents/hermes-life/ have to be filled in: inventory.md, docker.md, env-map.md, runbook.md and backup.md. The last line visible in the document is an instruction to keep raw secrets out of those files, which is a policy, not a filter. Notice also that two paths are fixed by convention rather than configuration: the control plane lives at /root/agent-control-room, and the task bus, drawn as inbox, working, outbox and archive, lives at /srv/agent-bus.
Secret handling is a written rule in three places and nowhere else
The rule about secrets appears in the file list as an instruction, again in the shared/ folder as an api-keys-sop.md alongside commands.md and security.md, and a third time as the stated purpose of agent-backup-manager, which is to design and audit per-agent backups without committing secrets. The architecture carries the same intent: the control plane node is described as holding docs, rules, registry, ports and env maps, runbooks and backups, and the security auditor exists to check ports, dashboards and SSH. What is absent is any mechanism. Nothing in the repository prevents a runbook from containing a token, nothing rotates anything, and the env-map.md file invites exactly the inventory a secret map would hold. For a template whose selling point is governance, the governance is a set of headings you are expected to respect. Anyone treating it as a security control is reading more into the file names than they carry.
The diagram and the folder tree both stop short of the repository
Two documents inside this repository are incomplete in ways that matter for orientation. The system diagram is a mermaid flowchart whose last specialist node, hermes-ops, ends mid-label after VPS / ba, so the one node describing the operations role is cut off while the other four, hermes-life as a personal agent, hermes-seo as the SEO specialist, hermes-dev for code and site work and hermes-cmo for marketing, are complete. And the suggested folder structure omits two directories that do exist at the top level, assets/ and examples/. The examples directory is the more interesting omission, because it mirrors the four levels exactly, with level-1-control-room-one-agent, level-2-direct-specialists, level-3-orchestrator-specialists and level-4-automated-team. So the worked examples for all four stages exist on disk, and the tree meant to get you started does not point at any of them.
The first step assumes Hetzner, root access and one fixed server
Everything converges on a single VPS. The core idea opens with creating a VPS or choosing an existing one, the first skill on the list creates a Hetzner server, and the manual route begins with an SSH session to root on an Ubuntu or Debian box, cloning into a root-owned path. There is no configuration file in the top level listing, so the paths, the provider and the SSH identity are conventions the template assumes rather than options it exposes, and the provider in the first skill is named outright. That matters when you compare it to the general shape it is selling: a control plane, an optional orchestrator, specialists behind a task bus, and automation last. The mechanism is sound and portable in principle, but the entry point quietly commits you to one hosting vendor and root-level access, which is a larger concession than a documentation template usually names out loud.
Editorial conclusion
Treat hermes-agent-control-room as a document to argue with rather than a system to install: it hands an agent a structure, and the structure is only as good as what you put in the runbooks. Read the starter guide and the seven skill descriptions before you let any model act on them, fill inventory, docker, env-map, runbook and backup by hand for your first agent, and keep raw secrets out of the tracked files since the protection here is a written rule rather than a mechanism. Skip Level 4 until the manual path works, and expect to fight the vendor lock-in to Hetzner if your server lives anywhere else.
Frequently asked questions
What does hermes-agent-control-room actually install?
Nothing runs by itself. The repository gives an agent instructions, templates and skills, and the text says you still have to ask the agent to run the setup flow. The manual route is an SSH session, a clone into /root/agent-control-room, and copying the five template files into a new agent folder.
How many skills does hermes-agent-control-room bundle?
Seven are described: create-vps, setup-control-room, agent-control-room, agent-task-router, agent-registry-manager, agent-backup-manager and agent-security-auditor. The suggested folder structure shows only the first three skill folders, so the remaining four are not in the tree it tells you to copy.
Do I need a Hetzner VPS to use the Hermes Control Room?
Not strictly. The create-vps skill makes a Hetzner VPS with an SSH key and alias, but the manual option is for any existing Ubuntu or Debian server you can SSH into as root. Both routes are given, and neither makes the provider configurable.
Where do the control plane and the task bus live on the server?
The control plane is placed at /root/agent-control-room, and the Agent Task Bus at /srv/agent-bus, holding inbox, working, outbox and archive. Templates for the bus are agents.yaml, task-template.md and result-template.md.
Should I add an orchestrator before hiring specialist agents?
The level order puts direct specialists at Level 2 and the orchestrator at Level 3, as an optional front door. At that level the text warns it should not become a giant agent holding every credential, and automation at Level 4 comes only after the manual workflow works.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/shannhk-hermes-agent-control-room)Star history chart for your README
[](https://hysenlabs.com/projects/shannhk-hermes-agent-control-room)Was this useful?