solidtime: unvouched pull requests over 50 changed lines are closed
Modern open-source time-tracking app
At a glance
- What is it?
- An AGPL time tracker for freelancers and agencies whose contribution gate is a conversation rather than a code review, where frontend API types are generated from the application's own OpenAPI document, the example environment runs FrankenPHP against PostgreSQL with Gotenberg for documents, and the example environment file ships literal keys that must be replaced before deployment.
- Who is it for?
- solidtime suits a freelancer or agency that wants time tracking with billable rates, clients and tasks on infrastructure it controls, and that is willing to read a self-hosting guide. It does not suit a contributor expecting to open a pull request and have it judged on its merits, because unvouched authors are gated by a conversation before any code.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly PHP, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
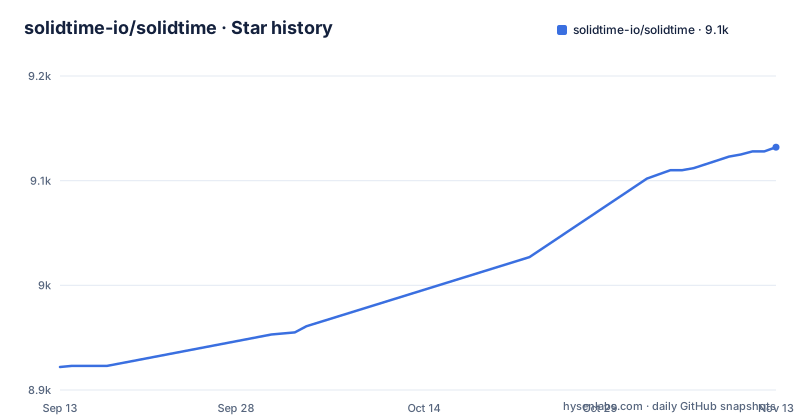
- solidtime-io/solidtime9,132 ★ · +210
| Repository | 2026-09-13 | 2026-11-13 |
|---|---|---|
| solidtime-io/solidtime | 8.9k | 9.1k |
210 Stars in the last 61 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Unvouched pull requests close themselves at fifty lines
The contribution policy is the most unusual thing about this repository, and it is enforced by automation rather than by review. The instruction is to open an issue or start a discussion and wait for approval before submitting a pull request, with an exception for tiny fixes or changes, and a candid note that pull requests might not be merged for various reasons. The mechanism is stated next: to keep that manageable, pull requests from authors who are not vouched are closed automatically unless they change fifty lines or fewer. To become vouched you open an issue or a discussion, explain how you intend to implement the change, and once the approach is agreed you are vouched. So the gate is not code quality, it is whether a conversation happened first, and the automatic-close threshold is a line count rather than a judgement.
Machine-generated pull requests are called out by name
One sentence in the contributing section is unusually blunt and worth quoting rather than paraphrasing: if you submit an AI slop pull request, especially without following the proper procedure, you will be banned from future contributions to solidtime. That is a written policy about machine-generated contributions, stated before anyone submits one rather than after. It sits alongside the vouching rule rather than replacing it, and the two together are a coherent position. The vouching system already assumes a human who has agreed an approach, so a generated diff is not merely unwelcome, it is out of process. The same section also points out that documentation contributions are handled separately, in the documentation repository, for example to add new self-hosting guides, which is the low-friction route in if your contribution is prose rather than code.
Bugs go to issues and features go to discussions
The two intake channels are split by kind, and the split is the point rather than an accident of tooling. For bugs you are asked to open an issue in the repository with instructions on how to reproduce the bug. For a feature request you are asked to create a discussion instead. That arrangement does two things at once. A bug report with reproduction steps is the artefact a maintainer can act on directly, while a feature request is a discussion because the outcome is a decision about whether and how, not a fix. For someone considering a contribution it also tells you where your message belongs before you have written any code. Vulnerabilities are handled apart from both, with the security document given as the place to report them rather than the public issue tracker.
Frontend types are generated from the app's own API document
The contract between the two halves of the codebase is machine-generated, and the script that does it is worth knowing about. The zod:generate script runs a client generator against the application's own documentation endpoint, reading the API description served at localhost on the docs path, and writes the result into the API workspace as a generated TypeScript client with a base URL of /api. The repository carries an openapi.json document at the root, and the frontend is split into two npm workspaces, one for the user interface and one for the API. The consequence is that a backend change to an endpoint regenerates the frontend type rather than being transcribed by hand, which removes a whole class of drift. The cost is that generation needs a running instance of the application, and the generated file is something you should read rather than edit.
FrankenPHP, PostgreSQL and a Gotenberg sidecar
The example environment file pins a specific stack rather than offering a menu. The database connection is set to pgsql on the standard PostgreSQL port, with a separate host and credential block for the test database. The server is not php-fpm: the Octane server variable is set to FrankenPHP. Document rendering is handled by an external service, with a Gotenberg URL pointing at a container on its own port. API access is token based through Laravel Passport, with a personal access client id and secret configured alongside everything else, and files go to S3-compatible object storage using path-style endpoints. Local mail goes through Mailpit. So the deployment shape is opinionated in a way that saves you decisions and costs you flexibility, and anything that produces a document needs that extra service running.
The example environment ships literal keys that must be replaced
The environment example is not a skeleton of empty values, and that is worth flagging before anyone deploys from a copy. It contains an application key as a literal base64 string, a Passport personal access client id and secret, and credentials for object storage. It also points the application URL at a .test hostname and sets a default pagination size of five hundred. The consequence is that these placeholders are shaped like real values, so someone who copies the file and runs it without regenerating the key material is running an instance with publicly known secrets. For a self-hosted deployment that is the first thing to change.
Registration can be open, off, or invite-only
One configuration value decides whether your instance is open to the internet, and it is a string with three meaningful settings. Registration supports on, off and invite-only, with true and false still accepted for backwards compatibility, and the default in the example file is on. Alongside it there is a super administrators variable that takes an email address. The consequence for anyone self-hosting is that the sensible order of operations is to set registration to off or invite-only before exposing the instance, create the administrator, and only then decide whether to open signups. It is a configuration value rather than a code change, which is what makes it a genuinely cheap thing to get wrong and a cheap thing to fix.
Editorial conclusion
solidtime suits a freelancer or agency that wants time tracking with billable rates, clients and tasks on infrastructure it controls, and that is willing to read a self-hosting guide. It does not suit a contributor expecting to open a pull request and have it judged on its merits, because unvouched authors are gated by a conversation before any code. Before deploying it, replace the application key and the Passport credentials that ship in the example environment, decide whether registration is open or invite-only, and note that self-hosting guides belong in the separate documentation repository.
Frequently asked questions
What is solidtime?
A modern open-source time tracking application for freelancers and agencies, licensed under the GNU Affero General Public License v3.0. It covers time tracking, projects, tasks, clients, billable rates set at several levels, multiple organizations under one account, roles and permissions, and import from other trackers.
What is the best self-hosted time tracking software?
The project describes itself as an open-source time tracker that can be self-hosted, with guides at docs.solidtime.io under self-hosting and a separate repository of self-hosting examples. You can also sign up for a hosted version instead.
How does solidtime compare with Toggl?
The repository does not frame the two as competitors. Toggl appears as one of the supported import sources, alongside Clockify and a Timeentry CSV, for bringing existing time tracking data into solidtime. Choosing between them as products is outside what this repository states.
What are the alternatives to solidtime?
The repository does not list alternatives. What it names are import sources rather than substitutes, namely Toggl, Clockify and Timeentry CSV, which tells you where data can come from rather than where you could otherwise go.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/solidtime-io-solidtime)Star history chart for your README
[](https://hysenlabs.com/projects/solidtime-io-solidtime)Was this useful?