gocryptotrader: 22 exchanges, a FIX column with no Yes, and a 386 container
A cryptocurrency trading bot and framework supporting multiple exchanges written in Golang.
At a glance
- What is it?
- thrasher-corp/gocryptotrader is a Go trading framework for twenty-two exchanges whose own README says it is not ready for production, whose build tag silently changes decimal rounding, whose container cross-compiles to 32-bit x86 and so loses its SQLite backend, and whose exchange table marks FIX unavailable for every row.
- Who is it for?
- Use it as a framework to study or to build on, and read it as what its README says it is: under development and not ready for production. Three things to check before you point it at an account.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 4 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 22, 2026, and from our analysis. They are not legal advice.
Star history
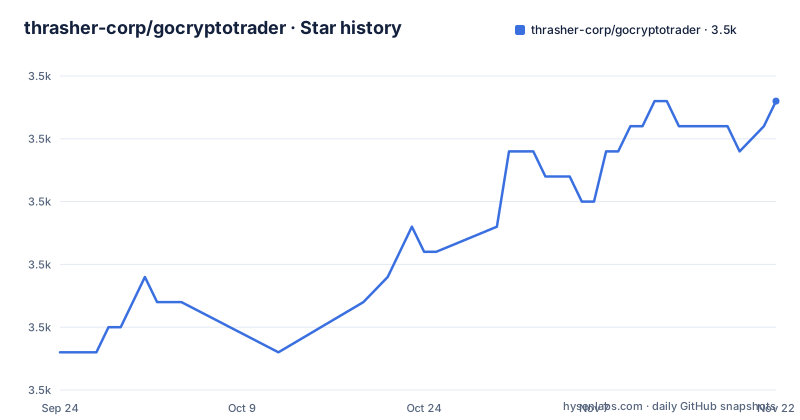
- thrasher-corp/gocryptotrader3,469 ★ · +10
| Repository | 2026-09-24 | 2026-11-22 |
|---|---|---|
| thrasher-corp/gocryptotrader | 3.5k | 3.5k |
10 Stars in the last 59 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The FIX column has no Yes in twenty-two rows
The exchange support table has three capability columns and twenty-two rows. Twenty-two, not the thirty the text above it promises as a target.
The REST column is Yes twenty-two times out of twenty-two. That is a complete row.
The websocket column is Yes nineteen times, No twice for Bitflyer and Lbank, and not-applicable once for Yobit. So the table uses two different words for absence in the same column, and the legend underneath explains only one of them. It says not-applicable means the exchange does not support the feature. It never says what No means, so a reader cannot tell whether No means this project has not implemented it or the exchange genuinely lacks it. That is the same question for every other column, where No appears five times.
The FIX column is where the table stops being informative. There is not one Yes in it. Five rows say No, and seventeen say not-applicable. Whatever FIX support the project has, this table does not claim it for any exchange.
Two rows are the same venue under two names, Binance.US and Binance, which brings the distinct count to twenty-one.
The target is stated as the top thirty exchanges sorted by average liquidity, as ranked by CoinMarketCap, with the ranking given as a link to a live page. So the goal is a moving target defined by a URL, the table is eight rows short of it, and the third of its three capability columns is empty.
For a framework whose pitch is breadth across venues, the column that documents institutional connectivity reads as a stub.
A build tag changes your arithmetic without telling you at runtime
This project documents its decimal behaviour more carefully than anything else in its README, and what it documents is a build-time switch that changes what your numbers are.
By default, Decimal is an alias for a third-party arbitrary-precision decimal library. Build with a tag and it is backed by a different library instead, and the README enumerates five differences.
Arithmetic and float conversion truncate beyond nineteen fractional digits and return no error, so a non-zero result below a very small threshold becomes zero. Parsing behaves differently and rejects such inputs outright.
Division truncates to nineteen digits under the tag, where the default build rounds to sixteen. The last three digits of any division differ between the two builds.
The struct grows from sixteen bytes to thirty-two. In a program holding orderbooks, tickers and balances, that is a doubling of a per-value memory cost.
The binary encoding is not compatible, and it rejects values whose native encoding would exceed a one-byte length field. So a value the default build handles can be refused by the tagged build at runtime.
And fractional power exponents are rejected, so an expression that compiles and runs under the default build can fail under the tag.
None of this is a defect. The README does something most projects do not: it enumerates the behavioural differences and ships a benchmark so you can measure them yourself. The suite runs with make decimal_bench, and the count and duration are overridable through two environment variables.
The risk is structural rather than local. A trading bot that compiles two ways produces two different sets of numbers, with nothing in the running binary recording which implementation is in it.
The container cross-compiles to 386, which turns off cgo and with it SQLite
The Dockerfile has a builder stage and a small Alpine runtime. The builder copies the source in, vendors the modules, and then builds two binaries with an explicit architecture and operating system set in the environment on the command line.
The architecture is 386. That is 32-bit x86, an architecture from before this project existed, and the builder image is the amd64 build of Go. So the two binaries are cross-compiled, not built natively.
Go disables cgo by default when you cross-compile. It cannot know what C compiler to use for a target it is not building on, so it turns the feature off unless you point it at a cross toolchain explicitly, and this Dockerfile does not.
That matters because the module's SQLite driver is a cgo package. It is a binding to the C library, and it does not build without a C compiler. So the published container, built this way, has no working SQLite backend.
The README lists database support as Postgres and SQLite3, and points at a database directory for details. From a clone with a local Go toolchain, both work. From the container, the Postgres driver is pure Go and the SQLite one is not available.
The same 386 choice has a second cost in a program like this. A 32-bit address space halves the memory ceiling, and this bot holds orderbooks and processes trades.
There is no comment in the Dockerfile explaining the architecture, and the README's build instructions use a plain go build with no architecture set, so a reader building locally gets the host architecture and a reader using the image gets 386.
The config lands in an anonymous volume, so redeploying never refreshes it
Start from what the README tells a Linux or macOS user to do, because that is where the config file comes from:
git clone https://github.com/thrasher-corp/gocryptotrader.git
cd gocryptotrader
go build
mkdir ~/.gocryptotrader
cp config_example.json ~/.gocryptotrader/config.json
Five commands. Clone, enter, build, make the directory, copy the checked-in example into it as config.json. The Windows variant is the same shape with a different directory, and both instructions then say, in one line, to make any necessary changes to config.json.
That is the entire configuration workflow, for a program whose config is where exchange API keys live. No key names, no testnet, no paper-trading option.
Now the runtime stage of the Dockerfile. It declares a volume at the configuration directory. It copies two binaries into the application directory. And it copies a config file into the configuration directory.
The config file it copies is not a real config. In the builder stage the image renames the checked-in example config to config.json with a no-clobber move. So what lands in the image is the project's example file, unmodified, with whatever placeholder values it ships with.
Then the volume declaration does something at runtime that is easy to miss. Docker creates a volume at that path when the container starts, and because the path has content in the image, that content is copied into the new volume. So the example config appears in the volume on first run, which is convenient.
It is also anonymous. Nobody named it, so there is no compose or command line reference to it, and it is tied to the container rather than to the image. Two consequences follow, and both are the kind you discover months later.
Edit the config in the volume and it survives an image upgrade, because the upgrade brings a new image but the volume is not part of it. Your API keys stay where you put them, which is good.
But the reverse is also true: a new image's config.json never replaces what is already in the volume. So if the project changes the example config in a way you need, pulling the new image and recreating the container changes nothing, and there is no signal that anything was skipped.
The compose file makes it worse by omission. It declares no volumes at all, so the only configuration path is the anonymous one, and it passes no environment variables either.
The image exposes four ports, compose publishes two, and the default is neither
Three documents in this repository name ports, and no two of them agree.
The Dockerfile exposes a range, four consecutive ports from 9050 to 9053. The compose file publishes two of them, 9052 and 9053, host to container. The Makefile sets a default listen port variable of 9050, which is the bottom of the image's exposed range and is not one of the two the compose file publishes.
So if you run the daemon with its defaults inside the compose file, the port it listens on is not forwarded to the host. If you publish 9052 expecting the daemon to be there, it is not, unless you have also configured the daemon to use it.
The Makefile is where the answer actually lives. It defines a listen port variable and a separate profiler listen port, and the configuration flag is built conditionally so the binary accepts a config path only when one is passed. So the daemon is configurable and the documentation never shows any of it.
The profiler port is 8085, which is not inside the image's exposed range at all. So the profiler the Makefile knows about cannot be reached from outside a container built from this Dockerfile without a port that the image does not declare.
The compose file is three services long in effect, because it is a single service: build from the current directory, map two ports, and stop. There is no environment section, no volume, no restart policy, and a version key of 3, which the current Compose specification no longer needs.
Four forked modules are pinned to 2017 through 2020, two of them database tooling
The module file is mostly ordinary: a Postgres driver, a SQLite driver, a websocket library, a gRPC stack, an argument parser, a configuration library, an error library, a testing library, and two decimal implementations, one of which is the default and the other the tagged alternative.
Four entries are not ordinary. They are forks, and every one is pinned to a pseudo-version, which is how the tooling records a specific commit rather than a tag.
A migration tool pinned to an October 2019 commit, and marked incompatible. A model generator pinned to a January 2019 commit. A trading library pinned to a June 2020 commit. And a fourth-party fork pinned to a February 2017 commit.
Two of those four are the database toolchain. The migration tool is what runs your schema changes and the model generator is what produces your database model structs. Both are forks, both are six or seven years behind anything upstream would be today, and the repository carries the output of the generator as committed files, which is why there is a models directory excluded from formatting.
There is a second example file at the top level for the generator, alongside the example config, which tells you the generated models are treated as a reviewed artefact rather than a build step.
None of this blocks a build, and a fork pinned to a known-good commit is a legitimate choice. It does mean the migration path for your own database runs through a fork whose relationship to upstream is invisible from this repository.
make check means different things on a laptop and in CI
The aggregate target runs four steps: lint, a script of miscellaneous checks, a Markdown lint, and the test suite. The intent is obvious and the implementation has one asymmetry.
The Markdown step begins by checking whether a Node package runner is installed. If it is not, the script tests whether it is running in CI. In CI it prints a message and exits non-zero. Outside CI it prints a message and exits zero.
So locally, a missing Node runner silently downgrades one of the four steps of make check into a no-op that reports success. The aggregate still passes. Nothing in the local output tells you that a quarter of the gate did not run, except a line of prose saying it was skipped.
That is a defensible choice for a developer who does not have Node installed, and the message is honest about it. The cost is that a green local check and a green CI check are not the same assertion, which matters most for a Markdown linter whose output depends on a version pinned in the same line that was skipped.
The lint step has a related cost. It installs the linter at a pinned version on every invocation, then runs the installed binary. Since the aggregate target depends on lint, every full check re-resolves and re-installs the linter rather than reusing what is already in the Go bin directory.
Two other details. Tests run with the race detector on by default and can be turned off through one variable, which is the right default for code handling concurrent exchange connections. And the generated code, the vendored tree and the protobuf output are all excluded from the formatting target, which is how you keep a formatter from fighting a code generator.
An encrypted config and an OTP generator with no documented workflow
Two features in the current list point in the same direction and neither is explained anywhere.
The first is an AES256 encrypted config file, listed among the current features. That matters for this project in a way it does not for most, because the config is where exchange API keys and secret keys live, and a trading bot's config is a high-value file.
The second is an OTP generation tool, with its own command directory linked from the same list, and a one-time-password library as a direct dependency in the module file.
So the design is: the config is encrypted, and there is a command to generate a one-time password. What the README never says is how those two fit together. Whether the one-time password is the encryption key, whether it wraps the key, whether it is requested at every start, how many are supported, or what happens when you lose it.
That last question is the one that matters. For an encrypted config holding exchange credentials, losing the key means losing access to the config, and the README gives no recovery path. It also gives no procedure for the ordinary case: how do you actually encrypt config.json, and with what.
The build instructions treat the config as an ordinary JSON file. Clone, build, copy the example to your configuration directory, and make any necessary changes. No key generation step, no encryption step, nothing about the one-time password.
Also worth noting in the same list, because it is the line with the most consequence per word: the features include exchange deposits and withdrawals for specific exchanges. That is the one capability here that moves funds out of an account, and it sits in a list of twenty-two bullets alongside websocket support and candle retrieval, with no note about testnet use, limits, or confirmation.
Editorial conclusion
Use it as a framework to study or to build on, and read it as what its README says it is: under development and not ready for production. Three things to check before you point it at an account. It publishes no releases, so there is nothing to pin. Its container cross-compiles to 32-bit x86, which turns off cgo and takes the SQLite backend with it, so plan on Postgres. And its build tag changes decimal rounding from sixteen fractional digits to nineteen while doubling the size of every decimal value, with nothing in the running binary recording which build you have. The feature list also includes deposits and withdrawals for specific exchanges, which deserves its own review before you enable it.
Frequently asked questions
Which exchanges does gocryptotrader support?
Twenty-two rows in the support table, all with a REST API. Nineteen also have websocket support, Bitflyer and Lbank are marked No, and Yobit is marked not applicable. Five rows mark FIX as No and the rest not applicable, so no exchange in the table has a working FIX API. The stated target is the top thirty by liquidity.
Is gocryptotrader ready to use with real money?
The README's own second line says the bot is under development and is not ready for production. The repository also publishes no GitHub releases, so there is no tagged build to pin, and the manifest declares a specific Go version the install instructions never mention.
How do I give gocryptotrader my exchange API keys?
Copy config_example.json to ~/.gocryptotrader/config.json on Linux and macOS, or to the GoCryptoTrader directory under your roaming application data on Windows, and then make any necessary changes to config.json. The README does not name the keys, and does not mention a testnet or a paper-trading option.
What does the udecimal_on build tag change?
It swaps the default decimal implementation for another one. The README documents five differences: arithmetic truncates past nineteen fractional digits without an error, division truncates to nineteen digits where the default build rounds to sixteen, the Decimal type grows from sixteen to thirty-two bytes, the binary encoding is not compatible, and fractional power exponents are rejected.
Does gocryptotrader have a backtester?
Yes, an event-driven backtesting tool that uses historical or custom data, with its own top-level directory and README. There is also a benchmark suite for comparing the two decimal implementations, run with make decimal_bench, with the sample count and duration overridable through environment variables.
Can gocryptotrader use SQLite?
From a local build, yes; the README lists database support for Postgres and SQLite3. From the published container, probably not: the Dockerfile cross-compiles for GOARCH=386, which disables cgo by default, and the module's SQLite driver is a cgo package.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/thrasher-corp-gocryptotrader)Star history chart for your README
[](https://hysenlabs.com/projects/thrasher-corp-gocryptotrader)Was this useful?