Zeron is local by default, and signing in trusts every device with your files
A native control plane for Claude Code, Codex, Cursor, Devin and other coding agents.
At a glance
- What is it?
- A Rust control plane that runs coding agents on your own machine, with multi-device sync as an opt-in second mode. The readme states the trust model plainly, including that one display option makes your gitignored environment files readable from another device, and it ships a headless install that still needs the desktop audio library.
- Who is it for?
- Zeron fits someone running several coding agents who wants one local place to see and drive them, and who will keep the sync mode switched off until they have a second machine they actually trust. Three things to know before you sign in anywhere.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
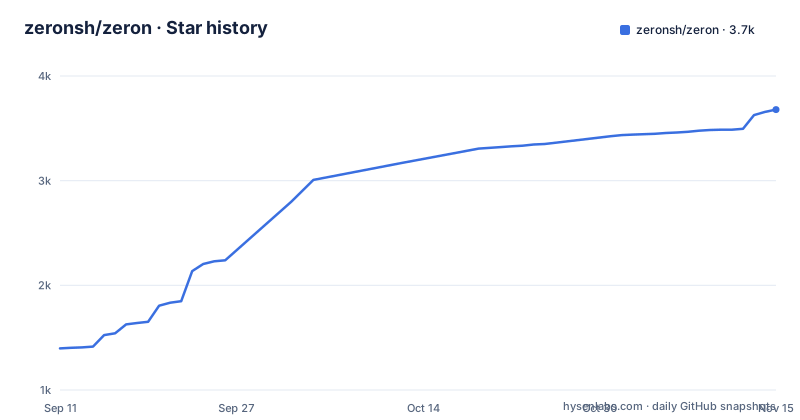
Star history
- zeronsh/zeron3,679 ★ · +2,282
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| zeronsh/zeron | 1.4k | 3.7k |
2,282 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Three releases in a day, and the patch number is in the hundreds
The three newest tags are separated by about thirty two hours: 0.2.100 and 0.2.101 on the same day, and 0.2.102 the next morning, with the patch component incrementing by one each time and sitting above a hundred. That is a project shipping several times a day, and it has a consequence for anyone pinning: the difference between two consecutive versions is small and frequent, so a version number is a timestamp rather than a set of features. The workspace manifest agrees with the newest tag, so there is no drift between the source and the release. It is worth setting against the issue tracker size as well, which is in the hundreds, because a tool that releases this often and carries that many open issues is a fast moving target rather than a settled one.
A headless install needs the desktop audio library
The Linux install is one line.
curl -fsSL https://zeron.sh/install.sh | sh
zeron status
What that script does is spelled out, and two of the details matter on a server. It starts the daemon immediately and arranges for it to keep running across reboots. And Linux requires the system audio runtime library, explicitly including in headless mode, because the headless build shares the desktop executable rather than being a separate binary. So a machine with no sound card and no desktop still needs that library present, which is the kind of dependency that shows up as a startup failure on a stripped down image rather than as a clear message. The script handles it by starting the binary and checking that it runs before activating it, and reports which runtime libraries are missing if it does not. It also rewrites a desktop launcher entry and icon on every run, so the install is not idempotent in the filesystem sense.
The trust model is stated, and one toggle makes your .env readable
This is the paragraph a reader should not skip, because it defines what the sync feature actually grants.
> Devices signed in to the same synced account are trusted with remote workspace access. A device controlling a workspace on another device can list, read, and write its files; enabling `Show ignored files` also makes gitignored files such as `.env` available remotely. `.git` is always excluded.
So there is no per-file permission model and no read only remote mode. Trust is granted at the account level, any signed-in device can write another device's files, and a display option that exists to let you see ignored files in a project also turns your environment files into remote readable files. The readme's own instruction is to sign in only devices you trust with the full contents of your workspaces. The version control directory is the single hard exclusion. That is a defensible model for a tool whose purpose is driving an agent across machines, and it is a sharp edge for anyone who signs in a shared or borrowed machine.
Local sessions never leave, and credentials freeze while the engine is running
Two more rules make the mode boundary precise. The first is that signing in does not upload, move or import anything you already have: local sessions and their attachments stay under the local profile and reappear when you go back. That is a strong privacy property for a product whose headline mode is network sync, and it is stated plainly rather than buried. The second is about timing. Signing in or out changes the profile that the next engine start will use, so it refuses to touch credentials at all while an engine owns the data directory, and the working sequence is stop, change, start. The desktop application honours the same boundary, meaning a user who logs in through the interface will not see the change until a restart. It is a slightly awkward dance, and it exists because two engines sharing one data directory would be a much worse outcome.
Updates download in the background and apply when you quit
The update behaviour is described in more detail than most projects bother with. The desktop application checks for a new release when it starts, then every hour while it runs, and again when you return to it after the machine has slept. A new version downloads in the background, the sidebar then offers a restart prompt, and if you ignore it the update installs the next time you quit. There is a manual check in the menu, named differently on macOS and on the other two platforms. And there is an environment variable that disables the background download while keeping the notification, which is the right way round: the option is about bandwidth, not about whether you find out. Service installs follow a further rule, restarting into the newer version only once no agent run or terminal is active, so an update never interrupts work in progress.
Windows ships one architecture in two shapes, macOS in two ways
The platform section is uneven in an instructive way. Windows gets a single architecture installer, an executable named for a version and one architecture, which installs for the current user without administrator rights, adds itself to the start menu, and registers itself for uninstall through the settings application. A portable archive is published as well, and the update manifest has to sit beside the executable for in application updates to work at all, which is a small operational detail with no documentation discipline of its own. There is no mention of an ARM64 Windows build. macOS is handled differently again: take the desktop release, or build the binary from source and run the install command for the launch agent, which is the route for anyone who wants a service without the application. The Linux path is the most automated of the three and the only one where the installer manages the launcher entry itself.
Sync is a CRDT with a byte-identical TypeScript twin
The workspace has seventeen members, a voice crate, a theme crate, a syntax crate and a mobile crate among them, and it publishes nothing to any registry, so every dependency between them is a path. The interesting one is the sync layer, which is built on a conflict free replicated data type library, plus a companion package for its wire protocol. The comment on that second dependency explains the arrangement: it is the protocol for the session rooms on the edge, and it is the official Rust twin of the equivalent TypeScript package that the edge component speaks, in the same monorepo, with byte identical frames, cross checked by snapshot tests. So the sync format has two implementations that cannot drift silently, which is the right way to run a mixed language edge. Another comment records the provenance of the interface toolkit: a fork extracted from another editor project at a specific commit, with bounded blur passes and shared weights added, tracing components removed, and fork history preserved.
Editorial conclusion
Zeron fits someone running several coding agents who wants one local place to see and drive them, and who will keep the sync mode switched off until they have a second machine they actually trust. Three things to know before you sign in anywhere. Trust is granted per account rather than per file, any signed-in device can write another device's workspace, and one display option makes gitignored files such as your environment files remotely readable. Releases arrive several times a day with a patch number above a hundred, so pin rather than track. And a headless Linux box still needs the desktop audio library present, because the same executable serves both modes.
Frequently asked questions
What does Zeron actually control?
It is a native control plane for coding agents, named for a list that includes Claude Code, Codex, Cursor, Devin, Grok, Hermes, Pi and Antigravity. Every device runs its own small engine that stores sessions on that device, and multi-device sync is an optional second mode.
Does Zeron need an account or a network connection to start?
No. A new installation starts in local only mode with no account and no network connection, and no sign in or sync configuration is required. Signing in is only for opening the account's synced workspace, and it does not upload or move any existing local sessions.
What can a signed-in device do to another device's workspace?
Devices signed in to the same account are trusted with remote workspace access: one can list, read and write another device's files. Turning on the display option for ignored files also makes gitignored files such as .env available remotely, while the version control directory is always excluded. The readme says to sign in only devices you trust with your workspace contents.
How do I install Zeron on a Linux machine?
Pipe the install script into a shell and then check the status. The installer starts the daemon and keeps it running across reboots. Linux needs the system audio runtime library present even in headless mode, because the headless build shares the desktop executable, and the installer verifies the binary starts before activating it.
How do Zeron updates work?
The desktop application checks at startup, hourly while running, and after the machine wakes, downloads a new version in the background, and offers a restart to apply it, installing on the next quit if you ignore the prompt. An environment variable keeps the notification but disables the download, and a service install restarts into the newer version only once no agent run or terminal is active.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/zeronsh-zeron)Star history chart for your README
[](https://hysenlabs.com/projects/zeronsh-zeron)Was this useful?