GreenWall fakes a contribution graph by pushing a real repository
customizing the GitHub contribution graph, allowing you to draw various patterns on it. GitHub .
At a glance
- What is it?
- A desktop application that renders an image into GitHub's contribution grid, then creates a real repository and commits to it so the squares light up. The engineering is small and the consequence is large, and the project says so in its own disclaimer.
- Who is it for?
- GreenWall is a good tool for practising GitHub contribution mechanics, for demoing the mechanics of the grid, or for experimenting with how GitHub counts and displays contributions. It is a poor foundation for anything else.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Activity is slowing. The repository last received commits 6 months ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
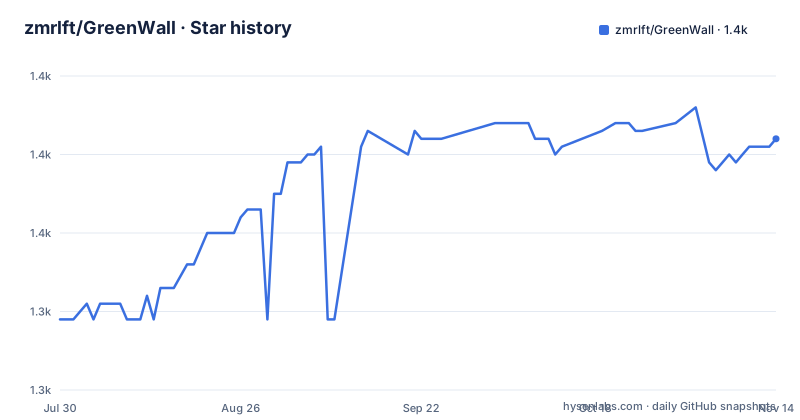
- zmrlft/GreenWall1,362 ★ · +23
| Repository | 2026-07-30 | 2026-11-14 |
|---|---|---|
| zmrlft/GreenWall | 1.3k | 1.4k |
23 Stars in the last 107 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The grid is filled by pushing a generated repository, not by drawing in the browser
The mechanism is the part worth understanding before anything else. GreenWall does not overlay or restyle your contribution graph. It asks you for a personal access token so it can sign in to GitHub, gives you a calendar to paint on, and then, when you are satisfied, creates a real repository under your account and pushes generated commits into it.
The buttons are named for what they do. You press Create Remote Repo, edit the repository name and description, choose whether it is public or private, then press Generate & Push and the application does the rest. GitHub counts contributions from commits in a repository you own, so the commits have to be real, on a server, under your account. There is no client-side trick available here.
That is also the whole risk profile in one sentence. The tool needs write access to your account to do its job, and the thing it produces is a commit history that did not correspond to work. The project's own disclaimer names falsifying job applications as an example of misuse and puts the responsibility on the user.
The canvas is seven rows by fifty-two columns, so shape is the hard part
You can set rows from 1 to 7 and columns from 1 to 52, which is the size of GitHub's own grid. That constraint is why the guidance is mostly about not distorting images rather than about picking colours. Target rows exists specifically to stop a tall image being flattened into a week, and the guide also recommends cropping a noisy background before raising the threshold rather than trying to smooth everything away.
Two rendering modes cover most inputs. Auto handles photographs and grayscale images. Binary handles black on white text and line art. Around them sit four controls: brightness invert, threshold, a scaling filter with Nearest and Bilinear options, and stroke recovery with dilation.
The documentation then gets specific, which is the most useful part of the README. Four input types are matched to exact settings:
| 1 | Black text on white background | Mode: Binary; Invert: on; Smoothing: Nearest; Threshold: 0–10; Recovery 1: 12–24; Dilation: 0–1 |
| 2 | Low‑contrast photo or drawing | Mode: Auto; Smoothing: Bilinear; Threshold: 0–15 |
Line three of that table raises recovery to 20-28 and dilation to 1-2 for lines of two pixels or thinner, which is the specific case where a stroke disappears entirely.
A private repository still counts, so the pattern can stay hidden
The most useful piece of advice in the documentation is not about rendering at all. After pushing, the README notes that GitHub may take anywhere from five minutes to two days to show the contributions on a profile, and then points out that you can keep the repository private and enable Include private contributions in your profile settings.
That combination is what makes the tool survivable to use. The repository is a wall of empty commits with no source code in it, so its content reveals nothing. With it private and private contributions enabled, the squares appear on your profile while the repository itself stays invisible to anyone who visits it. A visitor does not learn that the green is manufactured.
The delay is worth internalising too. Five minutes to two days is the difference between an afternoon project and an afternoon project you check tomorrow. Nothing in the application can shorten it, because the counting and the rendering both happen on GitHub's side after the push. If you care about the timing of a profile update, plan for the long end of that range rather than refreshing the page.
The right mouse button is bound to three different actions
Painting has two tools, a brush and an eraser, and the right mouse button toggles between them. The same button also cancels a paste preview. And during ordinary painting it cancels the current stroke. Three behaviours share one binding, which is workable once you internalise it and confusing the first time you right-click while a paste preview is following the cursor.
There is a clipboard as well, entered through a Copy Mode button. You drag a region on the calendar, press Ctrl+C, and the application reports a copy. From then on the copied pattern follows the pointer as a preview until you left-click to drop it, right-click to abandon the preview, or press Ctrl+V again to restore the last copied pattern in place.
Brush intensity is what gives you the shades of green, so a design that needs four distinct tones means stepping through intensity levels rather than painting flat colour. For a 364-cell grid at most, that is a workable amount of manual work, which is why the copy and paste feature exists at all.
The macOS build is unsigned and the documented fix strips the quarantine attribute
On Windows and Linux you download the application and run it. On macOS the README explains that the application is not yet signed, so the system will restrict it on first launch, and offers three commands:
cd the-directory-where-green-wall.app-is-located
sudo xattr -cr ./green-wall.app
sudo xattr -r -d com.apple.quarantine ./green-wall.app
The documentation is honest about how to use them. Try them in order and stop once one works. They will not launch the application, because they only modify file attributes, so you still have to double-click it yourself.
What the documentation does not dwell on is that this is a trust decision. The quarantine attribute is what macOS uses to warn you about an application it has not verified, and removing it with sudo, twice, on a binary whose signature you cannot check, is exactly the sequence that legitimate-looking malware asks users to run. The commands work, which is why they are here. Anyone adopting this on macOS should download from the release page, compare against the published checksums if there are any, and understand that they are asserting the application is safe rather than verifying it.
The documented Wails version is older than the one go.mod requires
The development guide asks for Go 1.24 or newer, Node.js 22 or newer, Git, and the Wails command line tool:
go install github.com/wailsapp/wails/v2/cmd/[email protected]The module file requires a newer library than that:
require github.com/wailsapp/wails/v2 v2.11.0So following the guide installs a 2.10.2 command line tool against a project that wants the 2.11.0 library. That combination usually works, since the CLI and the library are versioned together but not locked together, and it is the kind of drift that only shows up as an odd error message much later.
The module file also carries a commented-out line that was left in by someone:
// replace github.com/wailsapp/wails/v2 v2.10.2 => C:\Users\admin\go\pkg\modIt points a replacement at a module cache on a specific Windows user profile, which is harmless while commented out and would break the build for anyone who uncommented it. The rest of the workflow is short: clone, install the frontend dependencies with npm inside the frontend directory, then run wails dev for development or wails build for a binary, which lands in build/bin/.
The project calls itself a demonstration and tracks a 0.x version line
The disclaimer is short and specific. GreenWall is provided for educational, demonstration and research purposes related to GitHub contribution mechanics, and misuse, with falsifying job applications given as the example, is the user's responsibility. That sentence is the correct ethical framing for the project, and it is worth reading before anything else here.
The version line supports the same reading. Releases are v0.7.3 in December 2025, v0.7.4 in January 2026 and v0.7.5 in March 2026, so this is pre-1.0 software with no stability promise. The last push to the repository is dated 12 May 2026, which leaves a gap of roughly six weeks since the newest release, and there are 27 open issues.
Visibility has arrived faster than the versioning. The README records a recommendation in a Chinese developer newsletter in November 2025, a feature in a video channel in the same month, and selection as an interesting project by a Chinese open-source community in December. The licence is MIT and there is no project homepage beyond the repository, which for a desktop application with this much attention is unusual and leaves the repository as the only place any of this is documented.
Editorial conclusion
GreenWall is a good tool for practising GitHub contribution mechanics, for demoing the mechanics of the grid, or for experimenting with how GitHub counts and displays contributions. It is a poor foundation for anything else. The square root of the design is that it manufactures history rather than recording it, which is what its own disclaimer is about, and if that is your intended use the tool cannot help with that. If you are still evaluating it, check the unsigned macOS build first, since stripping the quarantine attribute on a binary you have not verified is the step most likely to cause trouble.
Frequently asked questions
How does GreenWall make the contribution graph light up?
It creates a real repository under your GitHub account and pushes generated commits to it, so the squares come from real commits on GitHub's side. You sign in with a personal access token, paint on the calendar, then press Create Remote Repo and Generate & Push.
Can the repository GreenWall creates stay private?
Yes. Keep it private and enable Include private contributions in your GitHub profile settings, so the contribution streak counts while the repository content stays invisible. The README notes GitHub may take anywhere from five minutes to two days to display the contributions.
Why does GreenWall not open on my Mac?
The application is not signed, so macOS restricts it on first launch. The README offers sudo xattr commands run from the folder containing the app, to be tried in order until one works, and notes that they only modify file attributes so you still have to launch it manually.
What image formats can GreenWall use, and which mode should I pick?
PNG, JPG and SVG are all accepted, with rows from 1 to 7 and columns from 1 to 52. Auto mode suits photographs and grayscale images, while Binary mode suits black on white text and line art, where invert, stroke recovery and dilation matter most.
How do I build GreenWall from source?
You need Go 1.24 or newer, Node.js 22 or newer and Git, plus the Wails command line tool installed with go install. Then clone the repository, run npm install inside the frontend directory, and use wails dev for development or wails build for a binary in build/bin/.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/zmrlft-greenwall)Star history chart for your README
[](https://hysenlabs.com/projects/zmrlft-greenwall)Was this useful?