openteams: a shared room for 16 coding agents, two lockfiles, and two patched crates
Plan, Build, and Ship — with a team of AI agents instead of one
At a glance
- What is it?
- openteams is a local-first desktop app that puts the coding agents you already run into one shared session, with a developer-owned issue list, per-session git worktrees and build statistics that connect output to cost. Its packaging is where the detail lives: an unsigned macOS build, two lockfiles in one root, and two crates.io dependencies redirected to forks.
- Who is it for?
- openteams suits an indie developer already running several coding agents in separate terminals who wants one session, one issue list and one cost record, rather than anyone looking for a new model or a project management suite.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 12 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 19, 2026, and from our analysis. They are not legal advice.
Star history
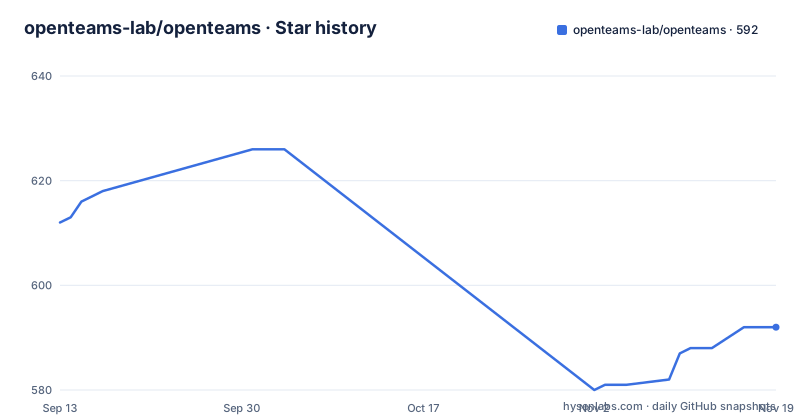
- openteams-lab/openteams592 ★ · -20
| Repository | 2026-09-13 | 2026-11-19 |
|---|---|---|
| openteams-lab/openteams | 612 | 592 |
-20 Stars in the last 67 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Sixteen agents, and four different ways to install them
The connected-agent table is the most useful part of the install section, and it is a list of other people's installers as much as openteams's own. The rows split into four shapes. Seven are global npm packages: Claude Code, Codex, Gemini CLI, Qwen Code, OpenCode, Amp and GitHub Copilot. Five pipe a remote script straight into a shell, with Cursor, Droid, Kimi Code, Qoder CLI and Kiro CLI each using a curl command. One is a Python package installed with pip, which is Hermes. One needs nothing at all, since Pi runs through npx. The readme states that sixteen agents are supported and names a bundled one as well, so openteams ships an agent of its own rather than only orchestrating other people's. Model providers are configured separately, in the app under Settings, Provider Config and Add Provider, which keeps the agent list about executables and the provider list about credentials. Two routes install openteams itself rather than an agent: the desktop build, which the readme marks as recommended and points at the release downloads for a Windows installer, a macOS disk image and a Debian package, and a one-line runner:
npx openteams-webThe macOS build is unsigned, and the workaround is one command
The macOS distribution has a documented caveat rather than a fix. The current release is not signed or notarized by Apple, so the browser adds a quarantine attribute when the disk image is downloaded, and Gatekeeper can then report the application as damaged even when the file is intact. The readme's instruction is explicit about ordering: drag the application into Applications first, confirm the download came from the official release, and only then run this:
xattr -dr com.apple.quarantine /Applications/openteams.appThe readme is careful about what that command does, which is worth repeating here because the phrasing matters. It removes the quarantine attribute from openteams alone and does not disable Gatekeeper globally. That is the narrow version of the workaround, and it is the version you should use: a user who follows it clears one application, while a user who reaches for a global Gatekeeper bypass has weakened every future download as well. Windows and Linux builds are published as an installer and a Debian package respectively, with no comparable caveat recorded.
Two lockfiles sit in one root, and the manifest is private
The root of the repository carries both a pnpm lockfile and an npm lockfile, which is the kind of pairing that eventually produces two dependency trees. The package manifest itself is marked private and publishes almost nothing: its file list covers only the payload directory for the npx package, its manifest file and that package's build output. A single binary is registered, mapping the openteams command to a JavaScript entry point inside that payload. Script names are organised around the two halves of the application, with frontend tasks delegated into the frontend directory through pnpm and backend tasks delegated to cargo. Two of those tasks set up their own environment first, resolving a backend port from a setup script before the watch process starts, and the combined quality check runs the frontend lint, the frontend tests and a cargo check in sequence.
Two crates.io dependencies are redirected to forks
The Rust workspace is not a plain dependency list. Two crates are redirected away from the registry entirely: the websocket crate and its async companion are patched to forks maintained under an OpenAI-affiliated organisation, each pinned to an exact commit rather than a branch. That is a defensible choice for a fork carrying fixes you need, and an expensive one to inherit, because every future build depends on two external repositories staying reachable at those commits. A third dependency, the type-export library, comes from a fork under an individual account and is taken from a non-default branch rather than a release. The workspace also declares what it excludes: the desktop shell directory and a remote crate sit outside the workspace members list even though both are present in the tree, so the app you install is not built by the same command that builds the library.
Types are generated from Rust and checked for drift
The interface between the two languages is generated rather than hand-written, and the drift check has its own script. One task runs a Rust binary named for type generation, and its companion runs the same binary with a check flag, so a stale type file fails a check instead of being noticed later. The Rust side carries the schema machinery for that, including a schema library with derived output for date and identifier types and an ordered representation so generated JSON keeps its field order. On the lint side, the backend is treated as blocking: clippy runs across the workspace and all targets with a feature flag for the test mode enabled, and warnings are promoted to errors. Formatting is checked separately. There is also a translation check run as a shell script, which pairs with the seven language versions of the readme kept under a translations directory.
Build statistics answer the question a token counter cannot
The project's argument is about bookkeeping rather than capability, and the readme states the boundary in a table of what it is and is not. It is not another model, not a replacement for the agents you run, not a pile of chat windows, not a project management suite, and not one large prompt that disappears until it finishes. What it adds is a layer of records. Chat sessions hold the shared context. Issues are owned by the developer and link work to the sessions that carry it out, and agents do the plan rewriting. Parallel work goes into separate git worktrees so unfinished changes stay separate until you merge or discard them. Workflow mode shows the steps and their dependencies before and during execution, which is what makes retrying a single step possible instead of restarting. The build statistics then attach tokens and cost to what was delivered.
Tags embed a build timestamp the manifest does not have
Version identification is inconsistent across the release feed and the source. The newest published tag is a release whose version string carries a date and time, and the one before it is a pre-release whose string contains both a build counter and a timestamp. The package manifest, by contrast, carries a plain semantic version with no timestamp, one step ahead of the newest release tag. So there is no arithmetic that maps a tag to the manifest version, and a script that derives a build from the newest tag will not reproduce the manifest number. The release cadence itself is regular, with tags roughly a week apart across the three most recent. One more detail explains the environment variables in the development scripts: the combined development mode sets an allowed-origins variable from the frontend port before starting both halves, so the local backend only accepts requests from the local frontend.
Editorial conclusion
openteams suits an indie developer already running several coding agents in separate terminals who wants one session, one issue list and one cost record, rather than anyone looking for a new model or a project management suite. Before you install, know that the macOS build is unsigned, that clearing the quarantine attribute is a step you have to take yourself and only after you trust the download, and that each connected agent brings its own installer, from a global npm package to a shell script piped into curl. If you plan to build from source, read the workspace file first: two dependencies are patched to forks at pinned revisions and the desktop shell sits outside the workspace.
Frequently asked questions
How do I install openteams on macOS without Gatekeeper blocking it?
Drag openteams.app into Applications from the official release, confirm you trust the download, then run xattr -dr com.apple.quarantine /Applications/openteams.app. That clears the attribute for openteams only and does not disable Gatekeeper globally.
Which coding agents can openteams connect to?
Sixteen are supported, including Claude Code, Codex, Gemini CLI, Qwen Code, OpenCode, Copilot, Cursor and a bundled openteams CLI agent. The visible rows install in four shapes: global npm packages, curl scripts piped to a shell, one pip package, and one agent that runs through npx.
Does openteams rewrite the project plan?
No. Issues are developer-owned and link work to the sessions that execute it. The readme is explicit that agents do the work but do not rewrite the plan, and that the app is not a project management suite.
How does openteams keep parallel agent sessions from colliding?
Each session can use its own git worktree, so unfinished changes stay separate until you merge or discard them. Workflow mode also shows the steps and their dependencies before and during execution, which lets you retry one step.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/openteams-lab-openteams)Star history chart for your README
[](https://hysenlabs.com/projects/openteams-lab-openteams)Was this useful?