SLF4J ships six bindings and three bridges, and names them backwards
Simple Logging Facade for Java
At a glance
- What is it?
- A facade that lets an application log through one API and lets the deployment choose the framework. The repository shows the shape clearly: bindings for six targets, bridges that redirect three other logging APIs into the facade, a module that only builds on JDK 25, and an escalation path that runs through a sponsorship tier.
- Who is it for?
- SLF4J is one of the few Java libraries whose module layout tells you the whole design, and this repository is worth reading as that layout rather than as documentation. Two rules decide whether a change here is easy.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 42 days ago.
- What is it written in?
- Mainly Java, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
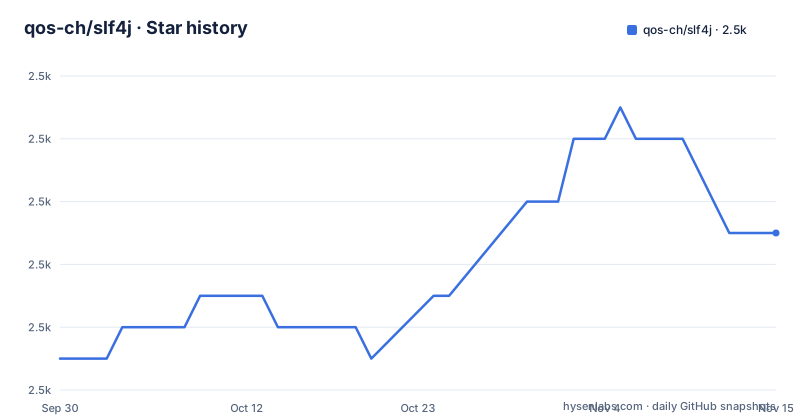
- qos-ch/slf4j2,533 ★ · +4
| Repository | 2026-09-30 | 2026-11-15 |
|---|---|---|
| qos-ch/slf4j | 2.5k | 2.5k |
4 Stars in the last 46 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
A facade naming eight frameworks and shipping six bindings
The whole idea fits in the opening paragraph: SLF4J is a facade or abstraction over logging frameworks, and the end user plugs in the desired framework at deployment time. The frameworks named there are java.util.logging, logback, reload4j, log4j 2.x, logevents, penna, rainbowgum and tinylog.
The module list at the root is where the design becomes concrete, and it splits cleanly in two. Bindings live in slf4j-simple, slf4j-nop, slf4j-jdk14, slf4j-jdk-platform-logging, slf4j-log4j12 and slf4j-reload4j. That is six, against eight frameworks in the introduction, and the two that have no binding here at all are logback and the four smaller frameworks.
That absence is not an omission. A binding is SLF4J handing its API to someone else's implementation, and the frameworks that implement the SLF4J provider interface ship that code themselves. So the repository ships the adapters it must maintain and leaves the rest to their own projects.
The bridges are named the other way round from the bindings
Seven root directories are bridges rather than bindings, and three of them have a blackbox twin. There is jcl-over-slf4j, jul-to-slf4j, log4j-over-slf4j and osgi-over-slf4j, plus jcl-over-slf4j-blackbox, jul-to-slf4j-blackbox and log4j-over-slf4j-blackbox.
The naming carries the direction. A binding is named for the framework it plugs into slf4j, and a bridge is named for the API it redirects into slf4j, which is why log4j-over-slf4j and slf4j-log4j12 sit side by side and do opposite jobs: one sends log4j 1.2 style calls into SLF4J, the other sends SLF4J calls out to a log4j 1.2 binding. The distinction trips people up regularly, and having both modules in one tree is the clearest possible illustration of why.
The blackbox variants are the test half of the same pair, and their presence as separate modules says the project treats bridge behaviour as something that has to be verified against a real logging implementation rather than assumed.
Three JDK rules in five lines of the build section
The build section is the densest part of the page and it carries three separate toolchain rules. SLF4J 2.0.x runs under Java 8. Building it requires Java 9 or later. And the slf4j-scoped-mdc module requires JDK 25 or later, because it uses java.lang.ScopedValue, and it joins the reactor only when the build runs on JDK 25 or newer.
That last rule is the one worth pausing on. A module that silently drops out of the build depending on the JDK you happen to use is a real hazard for a library with this many downstream users, and it is exactly the sort of thing that turns into a surprise on a contributor's machine rather than in CI. The page states the condition without saying what a consumer who wants that module on an older JDK should do.
Maven is the build tool throughout, with a parent directory and a root pom.xml, so the reactor is assembled from those two entries and the module list that follows.
Urgent issues are routed through a sponsorship tier
Support has two documented channels and both are unusual. For problems, the page asks you to open a discussion on GitHub and states plainly that you should not email the developers directly. For urgent issues, it points at a GitHub Sponsors link with a specific tier id, using the phrase champion a release.
So the escalation path for a production problem is a paid sponsorship tier rather than a public tracker label, and the page attaches a service level to it: in principle, most championed issues are solved within 3 business days, ensued by a release. The grammar is awkward but the claim is specific enough to hold the project to.
For an organization depending on SLF4J in production, that is worth reading as a policy statement. The public route is discussions, the fast route is funded, and there is no third option described.
Six contribution steps, and the fourth one is a machine check
The contribution process is a numbered list of six steps, and two of them are unusual for a Java library of this age. Step one is to file a bug report to start the discussion, before any code exists. Step two is to fork, and the page asks you to create a new branch in your fork so the change is easy to merge back.
Step four is the one that catches people: all commits must be signed off by the contributor attesting to a Developer Certificate of Origin, and commits without that sign off are rejected automatically by the DCO GitHub check application. Nobody has to read a licence clause to find out, because a bot reads the commits.
Step five carries an exclamation point and a warning in the source text: push to your fork and branch, not to your master, since pushing to master makes later submissions harder. Step six is submitting the pull request from the commit page. Between them the steps ask for a written issue, a signed off history and a clean branch, which is a stricter path than most projects of this size would set.
Two CI configurations, a committed IDE folder and a root src directory
The top level listing carries thirty entries and a few of them do not belong to a library's public surface. There is a .travis.yml next to a .github directory, so two continuous integration configurations sit in the tree at the same time. There is a .idea directory, which is IDE state rather than project configuration. There is a src directory at the root of a project whose real code lives in twenty module directories.
Alongside those sit the files a maintainer would expect: a parent directory and root pom.xml for Maven, release.sh, codeStyle.xml, LICENSE.txt rather than a file named LICENSE, SECURITY.md, FUNDING.yml and AGENTS.md. The presence of an agent instruction file at the root of a project of this age is itself a small signal about how the repository is worked on now.
None of it is harmful, and none of it is explained on the page. For a contributor the practical question is which of the two CI systems is authoritative, and the answer is not on the README.
Three releases in 2026, and a tag format that breaks scripts
Recent releases show a tight patch cadence in the second half of 2026. Version 2.0.18 shipped on 2026-05-12, 2.0.19 on 2026-09-04 and 2.0.20 on 2026-09-22, so two releases landed five weeks apart after a four month gap. The last push to the default branch, master, is dated 2026-09-25.
The tag format is the other thing to copy carefully. The leading v is joined straight to the version, so the tag reads v_2.0.20 where a conventional one would read v2.0.20. That is not cosmetic if you pin a dependency or write a release script from the tag list, and it is the kind of detail worth checking before you automate against this repository.
The modules the page never explains are as interesting as the ones it does. slf4j-ext, slf4j-migrator, slf4j-testing, the integration directory and src at the root all appear in the listing with no description anywhere in the visible text, so a reader has to take them on trust or go read the source. The named set, the bridges and the bindings, tells a much clearer story than the ones left unexplained.
Editorial conclusion
SLF4J is one of the few Java libraries whose module layout tells you the whole design, and this repository is worth reading as that layout rather than as documentation. Two rules decide whether a change here is easy. The first is the JDK matrix: the runtime stays on Java 8, the build needs Java 9 or later, and one module only joins the reactor on JDK 25, so a contributor without a recent JDK silently produces a smaller build. The second is process, since a pull request needs a filed bug report first and a Developer Certificate of Origin sign off that a GitHub application checks automatically. Before you adopt it, confirm which binding your deployment will actually use, because the six here do not cover the frameworks the introduction names.
Frequently asked questions
Is SLF4J the same as Log4j?
No, they occupy different roles. SLF4J is a facade over logging frameworks, and its own tree contains both a binding named slf4j-log4j12 and a bridge named log4j-over-slf4j, which send calls in opposite directions. The introduction names log4j 2.x among the frameworks a deployment can plug in.
What is SLF4J used for?
It serves as a simple facade or abstraction for logging frameworks, allowing the end user to plug in the desired logging framework at deployment time. Named examples include java.util.logging, logback, reload4j, log4j 2.x, logevents, penna, rainbowgum and tinylog.
How do I install SLF4J?
Add the org.slf4j:slf4j-api dependency to your build, then add one compatible SLF4J provider at runtime, such as slf4j-simple or Logback. Select versions compatible with your application and consult the SLF4J manual; without a provider SLF4J falls back to no-operation logging.
What Java version does SLF4J need?
SLF4J 2.0.x runs under Java 8, but building it requires Java 9 or later. The slf4j-scoped-mdc module requires JDK 25 or later because it uses java.lang.ScopedValue, and it is part of the reactor only when the build runs on JDK 25 or newer.
Which logging bindings ship in the SLF4J repository?
Six: slf4j-simple, slf4j-nop, slf4j-jdk14, slf4j-jdk-platform-logging, slf4j-log4j12 and slf4j-reload4j. Frameworks such as logback, logevents, penna, rainbowgum and tinylog are named in the introduction but ship their SLF4J integration elsewhere.
How do I report a problem with SLF4J?
Open a discussion on GitHub; the page asks that you do not email the developers directly. For urgent issues it points at championing a release through a sponsorship tier, and states that most championed issues are solved within 3 business days, ensued by a release.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/qos-ch-slf4j)Star history chart for your README
[](https://hysenlabs.com/projects/qos-ch-slf4j)Was this useful?