ReVanced Patcher rewrites other people's signed Android apps, and its README says so in two tenses
💉 ReVanced Patcher used to patch Android applications
At a glance
- What is it?
- ReVanced Patcher is a Kotlin library that disassembles and reassembles Dalvik bytecode, decodes and rebuilds APK resources and reads and writes arbitrary files inside an APK. Its dependency snippet still carries an unreplaced version placeholder, its recent release feed is mostly pre-releases, and a Gradle library ships npm release tooling to cut them.
- Who is it for?
- ReVanced Patcher is a tool for people who write patches, not an application, and that distinction decides how you should read it. Before using it on anything, settle two questions the repository does not answer for you.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 159 days ago.
- What is it written in?
- Mainly Kotlin, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
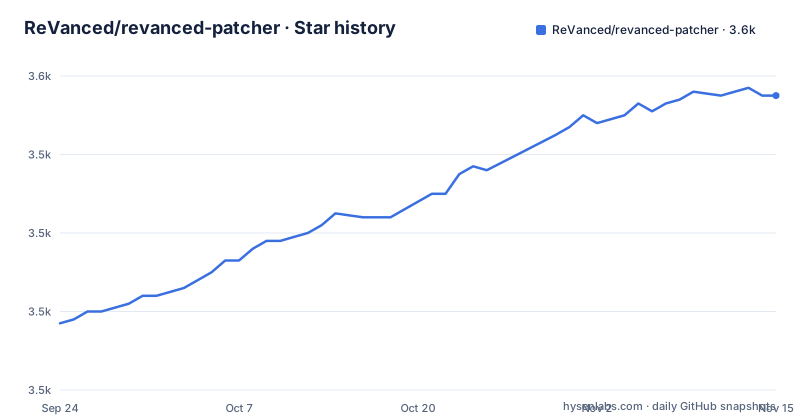
- ReVanced/revanced-patcher3,555 ★ · +58
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| ReVanced/revanced-patcher | 3.5k | 3.6k |
58 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
It rewrites other people's signed applications
The four capabilities in the feature list are all write access to an application you did not build. The first disassembles and assembles Dalvik VM bytecode, which is the executable content of an Android app. The second decodes and builds APK resources, which is the non-code half. The third reads and writes arbitrary files directly from and to APK files, so anything inside the archive is reachable. The fourth is an API for writing modular patches that can do all three. The project describes itself as continuing the legacy of Vanced, and it states that it powers ReVanced Manager, ReVanced CLI and ReVanced Library, with the patches themselves developed in a separate repository. So the library is the mechanism and the patches are elsewhere, which is the right place to draw the line when judging what this codebase is for.
The README describes it in two different tenses
There is a small inconsistency in the opening lines that tells you how the file is assembled. The heading block and the first level one heading both say ReVanced Patcher used to patch Android applications, in the past tense. A few lines later, the About section says ReVanced Patcher is a library that is used to patch Android applications, in the present. One of the two is a leftover from an earlier version of the project, and the past tense is the one that ended up on the title line and in the repository description. It is a small thing, but it is the kind of drift that matters here, because whether the project still does this is exactly the question a reader of the title line is trying to answer, and the About section contradicts it four lines further down.
The dependency snippet still has an unreplaced placeholder
The getting started section has two steps. The first is to add a repository to your project, and the link points at the GitHub documentation for a GitHub Packages registry, which means the library is distributed through GitHub Packages rather than a public Maven repository, so consumers need access to that registry. The second step is the dependency line:
    dependencies {
        implementation("app.revanced:revanced-patcher:{$version}")
    }
The version is a template placeholder that was never substituted, so the coordinate in the published file cannot be pasted into a build as it stands. The group is app.revanced and the artifact is revanced-patcher. The README then points at a separate template repository for a minimal project configuration, which is where a reader would find the working form of this line.
Fifty lines of image markup come before the first sentence
The top of the file is markup rather than prose. Roughly fifty lines are picture elements wrapping logo and badge images, each with a dark and a light variant selected by a colour scheme media query, wrapped in links to the project site, GitHub, Discord, Reddit, a Telegram channel, X and YouTube. Several of those images are not in the repository: they are fetched from a general image host and from a user-content host, so the header depends on third parties staying up and on those URLs not disappearing. One of the links, the Discord one, is written over plain HTTP while the rest use HTTPS. The only prose in that block is the line about continuing the legacy of Vanced, which sits below the images as an unlinked sentence.
What the four capabilities mean mechanically
Set out plainly, the library offers bytecode level work, resource level work, arbitrary file access inside the archive, and an API that composes them into patches. Each of those is a distinct capability with a distinct failure mode. Bytecode work requires the disassembler and assembler to round-trip instructions exactly, since a mismatch changes the program's meaning. Resource work requires the resource table to be decoded and rebuilt consistently with the manifest that references it. Arbitrary file access is the broadest and the least constrained, since it can replace anything in the archive including the files the other two operate on. The modular patch API is what lets a patch be written once and applied by a host application, which is why the same library appears behind a manager, a command line tool and a separate patches repository.
The recent release feed is mostly pre-releases
Of the three most recent releases, two carry a development suffix. The newest is v22.1.0-dev.1, published 2026-06-09, and the last push to the default branch is dated the same day. Before it comes v22.0.2-dev.1 from 2026-03-17, and before that a plain v22.0.1 from 2026-03-13. So a consumer pinning from the release list is as likely to land on a pre-release as on a finished version, and the version line itself is at 22 while the patches repository that consumes this library moves on its own schedule. The changelog at the root and the release configuration at the root are the places to look for what actually changed, and the library's own documentation directory is where the API is described.
A Gradle library that ships npm release tooling
The repository contains both a Gradle build and a Node manifest, and the Node manifest exists only to cut releases. package.json has no dependencies and no scripts; its entire content is a devDependencies block listing semantic-release, its changelog and git plugins, a Gradle plugin for the same purpose, and a community plugin whose job is to back-merge release branches. A package-lock.json sits beside it, and a .releaserc file sits beside that, so the release process is configured in two places for a project whose build is Gradle. The source itself is one module in a single patcher directory, with build.gradle.kts and settings.gradle.kts at the root, wrapper scripts for Unix and Windows, and the documentation in a docs directory.
The GPL terms ask you to publish what you change
The licence section gives the short version and then the long one. The library is under GPLv3, and the summary says you may copy, distribute and modify it as long as you track changes and dates in the source files. Any modifications must also be made available under the same licence, along with build and install instructions. That second sentence is the one with teeth for a patch author, because a patch is a modification and the README asks for the build and install steps to be published with it. What the licence does not do is speak to the applications a patch is applied to. Those carry their own terms, and rewriting them is a separate question from the licence of the tool that does the rewriting.
Editorial conclusion
ReVanced Patcher is a tool for people who write patches, not an application, and that distinction decides how you should read it. Before using it on anything, settle two questions the repository does not answer for you. First, scope: it can rewrite bytecode, rebuild resources and replace arbitrary files inside an APK that someone else shipped and signed, which changes that application's behaviour and invalidates its signature, so patching it is a decision about that application's terms rather than a technical one. Second, provenance: the library is GPLv3 and the README asks you to publish modifications under the same licence with build and install instructions, but that obligation covers the library and your patches, not the apps you point them at. If you want the mechanics of an Android patching tool, this is a good place to read; if you want a modified app, none of this makes that a good idea.
Frequently asked questions
What does ReVanced Patcher do?
It is a Kotlin library for patching Android applications. It disassembles and assembles Dalvik VM bytecode, decodes and builds APK resources, reads and writes arbitrary files directly from and to APK files, and provides an API for writing modular patches that can use all three.
How do I add ReVanced Patcher to a project?
Add the GitHub Packages registry to your project, then add the dependency using the coordinate app.revanced with the artifact revanced-patcher. The README's version field is still an unsubstituted placeholder, and the distribution is through GitHub Packages rather than a public Maven repository, so registry access is part of the setup.
Is ReVanced legal to use?
The repository does not address that question. It states the licence of its own code, GPLv3, including the requirement to track changes and to publish modifications with build and install instructions. Whether modifying a particular third-party application is permitted comes from that application's terms, not from this library's licence.
Is ReVanced Patcher safe, and can a patched app be detected?
The repository says nothing about either. Its documentation covers the fundamentals of the library and how to write patches with it, and the rest of the README covers contributing, building and licensing. Any question about detection or about the safety of a resulting application has to be answered from the application being modified, not from this codebase.
What are the recent ReVanced Patcher releases?
v22.1.0-dev.1 published 2026-06-09, v22.0.2-dev.1 published 2026-03-17 and v22.0.1 published 2026-03-13, so two of the three are development pre-releases. The last push to the main branch is dated 2026-06-09, the same day as the newest tag.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/revanced-revanced-patcher)Star history chart for your README
[](https://hysenlabs.com/projects/revanced-revanced-patcher)Was this useful?