Rocket.Chat's React Native app: the readme documents continuous integration, and the store upload is the gated step
The Secure CommsOS™ for mission-critical operations
At a glance
- What is it?
- The mobile client for a team chat product, and a repository whose front page is a map of its own pipelines rather than a description of the app. What is there is unusually honest about how the build works: four entry workflows, two of which write back to the branch, four manual approval gates, and a rule that a diff touching no end-to-end flow skips the end-to-end stage entirely.
- Who is it for?
- Read this repository as build documentation rather than product documentation, because that is what it is, and it is good documentation: the triggers are named, the call graph is drawn, and the approval points are listed with the condition that fires each one. Two things to know if you are contributing.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
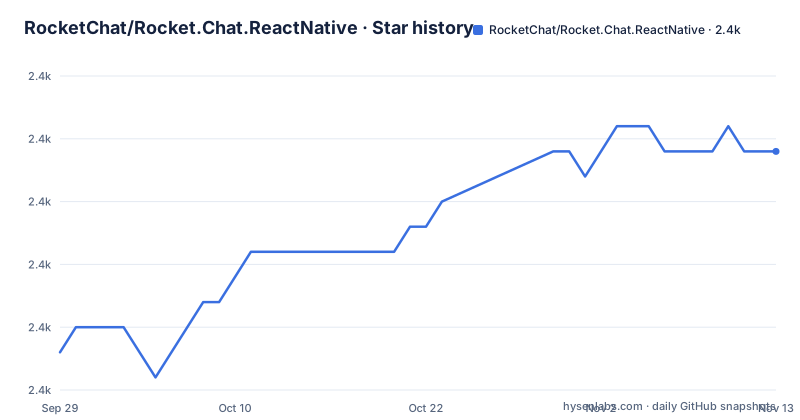
Star history
- RocketChat/Rocket.Chat.ReactNative2,422 ★ · +8
| Repository | 2026-09-29 | 2026-11-13 |
|---|---|---|
| RocketChat/Rocket.Chat.ReactNative | 2.4k | 2.4k |
8 Stars in the last 45 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The readme is a pipeline map, and the repository blurb is marketing
The repository's short description is a product slogan about mission-critical operations. The readme is a document titled continuous integration workflows, and its first line says what it does: it maps which event triggers which workflow and how those workflows call each other.
So the front page of the repository is an engineering map. There is no feature list, no screenshot, no installation instructions for an end user, and no architecture overview. What there is, is four entrypoint workflows in a table, a diagram of how they call one another, and a table of manual gates. For anyone deciding whether to work on this codebase that is arguably the more useful page, because the pipeline is where mobile work is actually lost, and for anyone evaluating the project as a product it is the wrong page entirely.
The four entrypoints are worth reading in full, because the difference between them is the whole design. One runs on any pull request and does linting, tests, a changelog, gated store builds, and gated end-to-end work. One runs on pushes to the development branch and does the same minus the gates, plus seeding the emulator caches the end-to-end shards need. One auto-formats and commits back. One sorts translation keys and commits back. Two of the four write to the branch that triggered them.
Two workflows commit their own fixes back to the branch
Automatic formatting is a design choice, not a convenience, and this repository has committed to it twice.
The formatting workflow triggers on any push except three named branches, and what it does is run two tools and commit the result back to the branch that triggered it. The two tools are a formatter and a linter, both from the same family of Rust-based JavaScript tooling, and the same pair appears in the manifest: one command formats and then lints, and the lint command itself is the linter followed by the TypeScript compiler. So the same three checks a contributor runs locally are the three a push runs, except the push version also fixes what it finds and writes the fix.
The second is narrower and arguably more interesting. A workflow triggers on any push that touches the translation files, and its whole job is to sort the JSON keys and commit the result. Machine-sorted translation files are a real convention: they turn a merge conflict over an alphabet of strings into a non-conflict, at the cost of a commit that exists only to reorder keys.
Both of these mean a contributor's branch can change after they push. Neither is controversial, but both change the mental model: you are not pushing to a branch and waiting, you are pushing to a branch that will push back, and the second commit is as legitimate as the first.
The store upload is gated, the build is not
The manual gates table is the most useful thing on the page, and reading it closely tells you where the project's real control points are.
Four environments gate four steps. An Android build job holds when it is called from a pull request rather than from a branch push. A separate Android upload job holds under the same condition and runs after the build finishes. An iOS build job holds the same way. And an end-to-end approval holds when a pull request's diff affects at least one end-to-end flow.
Three of those four gates exist so a store upload cannot happen from a pull request without a human. That is the important one, and it is worth stating plainly: building the app is automated, publishing it is not. The upload job is a separate gated job that runs after the build completes, which means the artefact that reaches a store is produced inside a pipeline and released outside it. That is the shape you want, and it is visible only because the page lists the environment names.
The fourth gate is different in kind. It does not protect anything from a stranger; it protects the queue from itself. The end-to-end stage runs Maestro flows on emulators, which is the slowest and flakiest part of a mobile pipeline, so the gate fires only when the diff touches at least one flow, and a diff that touches none skips the stage entirely rather than waiting for an approval nobody needs to give.
A diff is mapped to the end-to-end flows it affects
That last mechanism has a name and a directory. The repository root holds a directory for a tool the page calls sniffler, and the pull request workflow uses it twice.
Once to narrow the end-to-end work: the shards variable selects the subset of flows that a change could plausibly break, so a one-file change does not run the entire Maestro suite. And once to decide whether the approval gate fires at all, on the same question of whether the diff impacts any flow. A diff the tool is confident cannot affect any flow skips the whole end-to-end stage, and because the stage never starts, no approval is requested.
The confidence qualifier is doing real work in that sentence. A tool that says a change affects nothing might be right, or might be missing a path; the pipeline treats the second case as acceptable, which means the safety net is coverage analysis rather than proof. For a project whose end-to-end suite runs on emulators on both platforms, that is the trade that keeps pull requests moving.
The same repository carries the flows themselves in a directory at the root, so the mapping is between a diff and a set of files that are in the tree and readable by anyone reviewing the gate decision. The script that computes it is also in the tree, invoked from the manifest by name, which means a reviewer can run it locally and get the same answer the pipeline got.
The manifest version is one ahead of the newest tag
The repository publishes releases on a monthly cadence and the manifest sits one version beyond the last of them.
The three newest tags are all in the same series, a few weeks apart, with the latest published at the end of September. The manifest declares the version one increment higher, dated a few days later than the tag. The default branch is a development branch rather than a release branch, so that is not surprising on its own; what is worth flagging is that a version comparison between the manifest and the tag list tells you nothing about which release the code is.
Two other version surfaces exist and neither is the manifest. The pipeline stamps nothing visible in the files on display, and the release notes for each tag are generated by a workflow that takes a pull-request run and a branch run as separate inputs, which means the two paths produce different changelogs for the same code.
The practical consequence is small and predictable. If you are pinning a dependency or writing a build script, pin a tag. If you are reporting a bug, give the tag and the commit. The manifest number is a private field in a private package, and it is the one number in the repository that will not match anything you can download.
An encrypted keystore and a push key are both in the tree
Two credential-shaped files sit at the root of the repository, and they are handled differently, which tells you something about how the project treats each.
The Android signing key is present in encrypted form, with an encryption suffix on the filename, so the private material is in the tree but not in the clear. The iOS push notification key is present as a plain file with the conventional name for that role. Neither is surprising in a mobile application repository: a team that ships to two stores needs both keys to exist somewhere a build can reach them, and encrypting one and not the other is a decision someone made rather than an oversight nobody noticed.
What is worth checking before you build anything is where the decryption happens and who holds the passphrase, because that is not documented on the page this repository ships. A dependency scanner will flag an encrypted keystore and a plain push key with different confidence, and a reviewer reading the tree will have to work out which is which from the filenames alone.
Also present are the expected mobile companions: a Gradle wrapper for Android, CocoaPods configuration for iOS, a Ruby version file and a dependency manifest for the pod tooling, a Metro bundler configuration, Babel and Jest configurations with a shared preset and a setup file, and a patches directory.
Patches on every install, and a second application id
Two details in the script table describe a build that is not stock, and both are easy to miss.
The first is a postinstall hook that runs a patch application tool, against a patches directory checked into the repository. That means every install, including a fresh clone on a new machine and every continuous integration run, applies patches to installed dependencies before anything builds. It is a common and legitimate practice for a project that needs a fix upstream has not released, and it is also the kind of thing that makes a build non-reproducible for anyone who does not know about it, because the dependency versions your machine resolves are not the ones upstream publishes.
The second is a second application id. The ordinary Android run command passes a fixed package name; a separate whitelabel run command passes an application id as a bare flag with no default, which is the shape a white-label build takes, where one codebase ships under different package names for different customers.
Two other switches are worth noting because they change what the bundler does rather than what it builds. One starts the development server with an environment variable set and the cache reset, for end-to-end runs. Another does the same for component stories. And the test command pins the timezone to UTC explicitly, which is the kind of detail that only exists because a snapshot test failed somewhere else.
Editorial conclusion
Read this repository as build documentation rather than product documentation, because that is what it is, and it is good documentation: the triggers are named, the call graph is drawn, and the approval points are listed with the condition that fires each one. Two things to know if you are contributing. The default branch is a development branch rather than a release branch, and the manifest version sits one ahead of the newest tag, so neither is a reliable answer to where the code stands. And the store upload is the guarded step, which means a release is a human decision on this repository rather than a consequence of a green pipeline.
Frequently asked questions
What does the Rocket.Chat React Native repository document?
Its continuous integration. The page maps which event triggers which workflow and how those workflows call each other, lists four entrypoint workflows, draws the call graph, and tabulates four manual approval gates. It contains no feature list or user-facing setup instructions.
Can a pull request in Rocket.Chat React Native publish to an app store?
Not without a human. The Android upload is a separate job behind an approval environment that holds when the pipeline is triggered by a pull request rather than a branch push, and it runs after the build completes. The same holds for the iOS build job.
When does the Rocket.Chat React Native end-to-end suite run?
Only when a diff affects at least one of the Maestro flows, according to a tool in the repository that maps changes to impacted shards. A diff judged to affect none skips the stage entirely, so no approval is requested for it.
Do pushes to Rocket.Chat React Native change the branch automatically?
Yes. One workflow auto-formats and commits fixes back to the triggering branch, and another sorts translation JSON keys and commits the result when a push touches the translation files.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/rocketchat-rocket-chat-reactnative)Star history chart for your README
[](https://hysenlabs.com/projects/rocketchat-rocket-chat-reactnative)Was this useful?