Brunch's install instructions live in three other documents
Boot ChromeOS on x86_64 PC - Supports Intel CPU/GPU from 10th gen or AMD Ryzen
At a glance
- What is it?
- Brunch builds a generic ChromeOS image for an x86_64 machine from an official recovery image, using a one gigabyte partition holding a custom kernel and a separate EFI partition to boot it. The root readme is a landing page: it names the hardware gates, states a serious data loss warning in its own words, and hands the actual install steps to other files and another project.
- Who is it for?
- Brunch fits someone with a recent Intel or Ryzen machine, no sensitive data on it, and a tolerance for an unofficial boot path that the project's own warning describes as something ChromeOS could break at any time. It does not fit a laptop you depend on, and it does not fit anyone with a discrete GPU, a virtual machine or an ARM processor, all three of which are excluded by name.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 36 days ago.
- What is it written in?
- GitHub does not report a main language for this repository.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
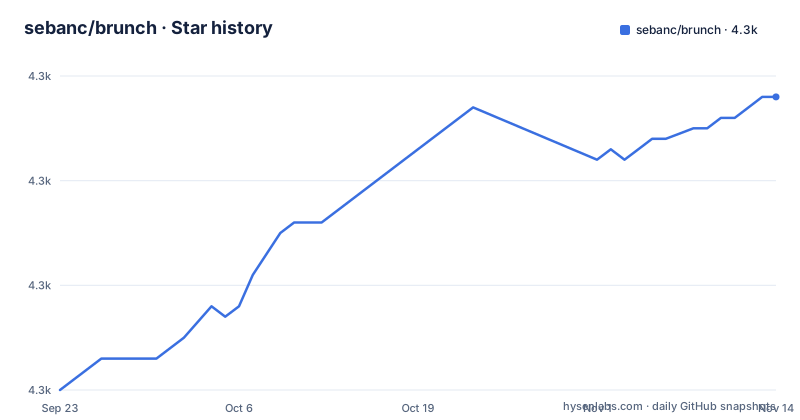
- sebanc/brunch4,288 ★ · +28
| Repository | 2026-09-23 | 2026-11-14 |
|---|---|---|
| sebanc/brunch | 4.3k | 4.3k |
28 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The root readme contains no install steps at all
The page a visitor lands on is an index. It says the guide has been split into separate sections and to follow one of the links for a guide suitable to your current operating system.
Then it offers two choices under the manual heading, one for Linux and one for Windows, and each is a link into a separate document in a subdirectory.
Above that sits a third route, labelled as the simplified install, which points at another project by the same author: a graphical tool that handles the installation instead of a terminal. That project's own instructions are where you are sent once you have picked a recovery image.
So the chain is four documents long. This page decides whether your hardware qualifies and names your recovery image, the graphical tool's page covers the automated path, and two further documents cover the manual path per operating system. A fourth document holds troubleshooting and answers.
None of the commands are here, and the page does not pretend otherwise. Knowing how a terminal works is listed as a base requirement, with a note that the guide tries to make this easy but expects the basics.
Release tags carry the upstream milestone and a build date
The release tags are not version numbers for this project.
The three most recent are a milestone number, the word stable, and a date.
That shape tells you the important thing about this repository's relationship to its upstream: a release corresponds to a particular ChromiumOS milestone, and the tag records which one along with the day it was cut.
The three recent tags are r151, r152 and r154, roughly three to four weeks apart in date. That is a fast cadence for something that patches an operating system image, and it is explained by the project's design rather than by the amount of code in it.
The last of those tags and the most recent push carry the same day, and the tags are named after what they are: a stable channel build for a milestone, not a release of the framework's own code.
For anyone tracking what they are running, the milestone number in the tag is the meaningful part, since that is what determines how closely the image tracks ChromeOS itself.
A one gigabyte partition and a custom kernel is the mechanism
The technical description is one sentence long and it is the whole design.
The framework creates a generic ChromeOS image for x86_64 from an official recovery image, and it does so using a one gigabyte ROOTC partition containing a custom kernel, an initramfs, binaries for a software TPM implementation, userspace patches and configuration files, together with a specific EFI partition to boot from it.
Two things follow from that. The source material is Google's own recovery image for the platform, so the base is official rather than a community rebuild. And what the project adds is confined to one small partition plus a boot partition.
Hardware support is therefore delegated to the general Linux kernel's hardware compatibility, which the page states plainly rather than as a caveat.
The page's own warning says data can be deleted on other partitions
The warning paragraph is the most important text on the page and it is worth taking apart.
It says this is not the intended way for ChromeOS to work. It says that at some point ChromeOS could become incompatible with the framework and delete data unexpectedly, including on partitions that are not running ChromeOS. It says that installing it means agreeing to take those risks, and that the author cannot be held responsible for anything bad that happens, data loss included.
The recommendation that follows is specific rather than general: use it only on a device containing no sensitive data, and keep that data synchronised with a cloud service.
The clause about other partitions is the part that changes the scope. A user who installs this expecting to affect only a test partition is being warned about writes outside it, which is a stronger statement than an ordinary stability caveat.
Taken together with the fact that this is an unofficial boot path, the warning is the reason to read the rest of the documentation on a machine you can afford to lose, and the reason to keep a backup that does not live on that machine.
Recovery images are chosen by CPU generation
The one decision the landing page does make for you is which recovery image to download, and it makes it by CPU generation rather than by a hardware model.
For Intel, there are three names: jinlon for tenth generation, voxel for eleventh to thirteenth generation, and kanix for fourteenth generation and Core Ultra.
For AMD, there is a single name, and it is used for all Ryzen parts.
That is a three-way split for Intel and a one-way split for AMD, which means the failure mode of guessing wrong is asymmetric: on an Intel machine there is a real chance of picking the wrong one, and on an AMD machine there is no choice to make.
The page gives no diagnostic for telling which generation a processor is. It links out to encyclopaedia pages for Intel Core and AMD Ryzen processors instead.
The page's reference block also defines links to the official update service and to third-party repositories for a toolkit and an update utility.
Discrete GPUs, virtual machines and ARM are excluded by name
The hardware section lists three base requirements and four exclusions, and the exclusions are the more useful half.
The requirements are an x86_64 computer with UEFI boot support, administrative privileges on the device, and an entry-level understanding of the terminal.
The supported processors are Intel from the tenth generation and AMD Ryzen. The exclusions are older Intel and AMD processors, discrete GPUs, virtual machines, and ARM processors.
Four exclusions for four different reasons, and only one of them is about the processor generation. A discrete GPU being unsupported is the one that surprises people, because it is not a CPU limit at all.
Virtual machines are excluded outright, which rules out the obvious safe way to try this. The page also names three features that may not work or may need troubleshooting on otherwise supported machines: the camera, the microphone and the touchpad.
The page defines badge links it never uses and one reference that is just http
The bottom of the page is a reference block of link definitions, and it is longer than the visible badge row needs.
Only three badges are rendered at the top: one for the licence, one for open issues, and one for the chat server. The block also defines badges for stars, forks and pull requests, with their own image URLs, and none of those three is displayed.
Seven image references are defined as well, and the visible body uses three of them: the troubleshooting icon and the Linux and Windows icons.
None of this breaks anything. It does mean the page carries link definitions for resources that were added at different times and never tidied, which is the normal residue of a long-lived readme, and it is a reason to trust the visible body of the page rather than the footer.
A directory and a file differ by one capital letter
Two things at the root of the repository will confuse anyone scripting against it.
The documentation file is named with an extension, and the directory holding the other documentation is the same word with a capital letter.
The reference block uses both forms.
The other thing is a single file with a certificate-style extension sitting at the root next to the licence and the images directory, with no explanation of its purpose anywhere on the page.
The acknowledgements section, for its part, names four projects and says they were used while building this one: a ChromeOS-on-PC project, the maintainer of the software TPM implementation, a Linux kernel patch collection for specific hardware, and a package manager framework for ChromeOS.
Editorial conclusion
Brunch fits someone with a recent Intel or Ryzen machine, no sensitive data on it, and a tolerance for an unofficial boot path that the project's own warning describes as something ChromeOS could break at any time. It does not fit a laptop you depend on, and it does not fit anyone with a discrete GPU, a virtual machine or an ARM processor, all three of which are excluded by name. Before you start, check four things. Whether your machine is on the supported CPU list at all. That you have read the data loss warning rather than skipped past it. Which recovery image your CPU generation needs. And where the steps actually are, since the page you land on contains none of them.
Frequently asked questions
How do I install the brunch framework?
First identify the recovery image for your CPU: jinlon for tenth generation Intel, voxel for eleventh to thirteenth generation, kanix for fourteenth generation and Core Ultra, and gumboz for Ryzen. Then either use the graphical installer from the author's separate project, or follow the manual guide for your operating system, both of which are separate documents rather than part of the main page.
What hardware does Brunch support?
An x86_64 computer with UEFI boot support, running an Intel processor from the tenth generation or newer, or an AMD Ryzen processor. Older Intel and AMD processors, discrete GPUs, virtual machines and ARM processors are all listed as unsupported. The camera, microphone and touchpad are named as features that may not work.
What are the risks of installing Brunch?
The project states that this is not the intended way for ChromeOS to work, that ChromeOS could at some point become incompatible with it and delete data unexpectedly, including on partitions not running ChromeOS, and that installing means accepting that risk. It recommends using it only on a device with no sensitive data, with data kept in sync elsewhere.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sebanc-brunch)Star history chart for your README
[](https://hysenlabs.com/projects/sebanc-brunch)Was this useful?