dailycheckin: the versions are dates and four rows of the service table are stale
A daily check-in script based on Docker / QingLong panel / Synology, supporting multiple accounts. Check-in list includes iQiyi, Quanmin K Song, Youdao Cloud Note, Baidu Tieba, Bilibili, V2EX, AcFun, SMZDM, Alipan, Moutai purchase, Mi Fit, Baidu Search Resource Platform, Enshan Forum, Aola Star and more.
At a glance
- What is it?
- dailycheckin is a scheduled script that signs in to about fifteen consumer services every day and reports the result through eleven notification relays. Its own bookkeeping is the interesting part. The version number is a calendar date rather than a semantic version, the service table records a per-row check date and four of its rows have not been checked since February 2024, one row is marked with a state the legend glosses as depending on luck, and the documented release target has a mistyped flag.
- Who is it for?
- dailycheckin fits someone who wants a single scheduled job signing in to a pile of small consumer accounts, running unattended on a NAS or a container host, and who treats the whole thing as best-effort rather than as infrastructure. It does not fit a team that needs to know a service's check-in still works without looking at the status column.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 128 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
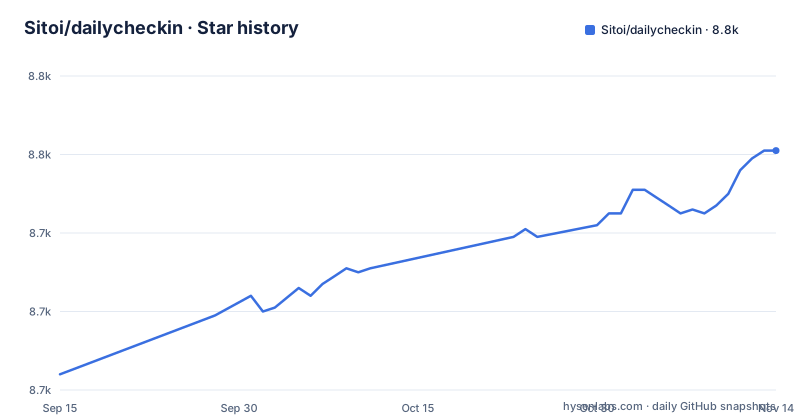
- Sitoi/dailycheckin8,761 ★ · +57
| Repository | 2026-09-15 | 2026-11-14 |
|---|---|---|
| Sitoi/dailycheckin | 8.7k | 8.8k |
57 Stars in the last 60 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The version number is a date
The three most recent releases are numbered as year, month and day, and the newest, 25.12.9, is the ninth of December 2025 (published on 2025-12-24). Consequence: there is no semantic version here, so the usual meanings do not exist. There is no minor to upgrade within. For a project you deploy rather than depend on, that is a workable convention. For anything that installs it, it means you can only take latest or pin an exact date-shaped string, and a rollback is another date-shaped string you have to have kept. The newest release also carries the same date-shaped string as its title, so even the feed does not add a second scheme you could sort on. There is no branch scheme described either, so a deployment that tracks the default branch is tracking whatever the newest date-shaped build happens to be, and a deployment that pins a version has pinned a day rather than a release.
Four service rows have not been checked since February 2024
The service table carries a check-date column, and it holds three values across the whole table. Most rows were last checked on 2025-09-28, four were last checked on 2024-02-20, and one (FNNASCLUB) on 2025-12-09. The legend above the table defines five states, from running normally through temporarily unavailable, executable but needing an update, pending test, and a fifth whose gloss is that it depends on luck. Consequence: the freshness of the table is per row and the layout does not distinguish the two dates, so a reader scanning for a green cell finds one last checked in February 2024. And the fifth state is the project saying, in its own legend, that one row is not reliably working. The table is the project's only status reporting, so it is where a maintainer signals that a service's sign-in flow has changed, and it is also where a reader decides whether to bother.
The lint configuration ignores the two things a linter is usually wanted for
The lint configuration selects eight rule families and then ignores thirteen rules by name, two of which are the unused-import check and the line-length check. A line length is set anyway, one hundred and twenty columns. Consequence: unused imports and over-long lines accumulate without complaint, in a project whose whole structure is a directory of small per-service modules where an unused import is usually the residue of a half-finished check-in. The rest of the ignore list is coherent for this shape of code, with too-many-branches, too-many-statements and magic-value checks all switched off, which suggests the rules were tuned until the codebase passed rather than chosen in advance. The tool targets py39, which matches the >=3.9.0 floor in setup.py. The ignore list also switches off the rule that catches a function whose name does not follow the casing convention, which in a project of fifteen service modules named after their services is the rule you would most want.
The HTTP stack is held a major version behind
Four dependencies are declared. One cryptographic library is pinned to an exact version, one key library floats within a major, and the two that matter for a script that makes network calls are held on compatible-release ranges, requests within 2.25.x and urllib3 within 1.26.x:
    requests~=2.25.1
    urllib3~=1.26.2
Consequence: the request path runs on old releases of both libraries, and because one is exact while two float on compatible-release ranges, a fresh resolve can produce a combination the maintainer never ran against. That is the shape where dependency updates become manual work rather than a version bump, and it is worth knowing before you file an issue about a failure that turns out to be a library version. The same four lines appear in a second file, so the constraint that pins the request stack is written down twice. Those two are the only runtime dependencies doing any real work, so the project runs on a two-library core and a pinned crypto helper, which is why the dependency surface looks small on the manifest and is not small in the resolved tree.
The release target has a mistyped flag and an old-style command
The build file's packaging target is one line, and it invokes the legacy setup command to build both a source distribution and a wheel, with a trailing flag that stops mid-word:
python3 setup.py sdist bdist_wheel --universaConsequence: the flag is misspelled as written. The release target next to it uses the legacy upload command, which those tools removed years ago. So both halves of the release path in the repository need attention, and anyone who wants to build or publish from source has to work around the only route the project documents. That is worth knowing at the point you pick it up rather than the point you try to release it. A separate target handles the pre-commit hooks and another is declared for the documentation build, so the parts of the build file that still work are the ones nobody publishes from. The clean target removes the build directory, the egg information and the distribution directory, so re-running the packaging step after a failed build starts from nothing each time rather than from a partial one.
Three manifests and a lock file describe the same four dependencies
The repository holds a project manifest, a legacy setup script, a requirements file and a lock file. The two manifests also split the metadata: the project manifest hard-codes version 25.12.9, while the legacy setup script records a personal site as the project URL, the documentation site as a separate link, and produces the version by reading and executing a file inside the package during the build. Consequence: a dependency change is a change in up to three places, and a build runs code out of the tree before it runs any of that code deliberately. For a project of this size that is more configuration than the code needs, and it is the configuration rather than the fifteen service modules that a new contributor will have questions about. The requirements file is read by the legacy setup script at build time, which is how the duplicate stays in step in one direction and drifts in the other. The project manifest delegates seven fields to files elsewhere, so the authoritative source for the readme, the interpreter floor, the licence and the entry points is not the manifest you are looking at.
One service's login script lives at the repository root
The top level holds the package directory, the container directory, a start script, documentation and a single file named for one service's login flow. Consequence: that script is outside the package, so it is not installed with it, not covered by the package data and not reachable from an installed copy. It is a small inconsistency in a tree that is otherwise carefully laid out, and it is the kind of thing that only shows up after someone has already installed the tool and found the command missing. Everything else in the tree is either the package, the container definition or documentation, so this one file is the outlier in a layout that is otherwise predictable.
Reporting goes through eleven relays and most of them need an account elsewhere
The notification list names eleven channels: DingTalk, two WeCom (enterprise WeChat) channels and Feishu, Telegram, the iOS push application Bark, and WeChat or QQ relays (server 酱, server 酱 TURBO, pushplus, Cool Push and qmsg 酱). Consequence: the notification layer is the integration surface and almost none of it is self-hosted, so setting it up means registering with a third party and holding a key,.
Editorial conclusion
dailycheckin fits someone who wants a single scheduled job signing in to a pile of small consumer accounts, running unattended on a NAS or a container host, and who treats the whole thing as best-effort rather than as infrastructure. It does not fit a team that needs to know a service's check-in still works without looking at the status column. Before adopting it, read the check-date column rather than the status colour, confirm which of the eleven notification relays you already have an account with, and decide whether the one service marked as depending on luck (MIMOTION) is one you care about.
Frequently asked questions
What is dailycheckin?
A scheduled script that signs in to a list of consumer services every day, supports multiple accounts per service, and reports the result through a choice of notification channels. It installs from the package index and can be deployed as a container, through a panel that runs scheduled tasks, on a NAS, or locally, and it can update itself.
how to use dailycheckin
Install it, configure the accounts for the services you want, and schedule it through whichever deployment you chose. The project keeps a status table of the services it supports with a per-row last-checked date and a five-state legend, so the current state of a given service is in that table rather than in the documentation, and four of its rows were last verified many months before the rest.
Does dailycheckin work on a NAS or in a container?
Yes, both are named as first-class deployment targets alongside a scheduled-task panel and running locally. The repository carries a container directory and a start script for that route, and the project publishes to a container registry as well as to the package index, with the readme carrying badges for both.
How often is dailycheckin updated?
The version numbers are calendar dates rather than semantic versions. The project describes itself as supporting automatic updating, and the release cadence in the feed is irregular, with two releases on consecutive days followed by a gap of several months.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sitoi-dailycheckin)Star history chart for your README
[](https://hysenlabs.com/projects/sitoi-dailycheckin)Was this useful?