XXMI Launcher: model importer setup and account considerations
Modding platform for GI, HSR, WW and ZZZ
At a glance
- What is it?
- XXMI Launcher installs and manages model importers for several games. The project warns that antivirus products may flag its unsigned files; users should assess download, game-rule and account risks before installation.
- Who is it for?
- XXMI Launcher provides a shared interface for installing and updating supported game model importers. Download from the official release page, verify the game version, and review the game's current rules before use.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 3 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
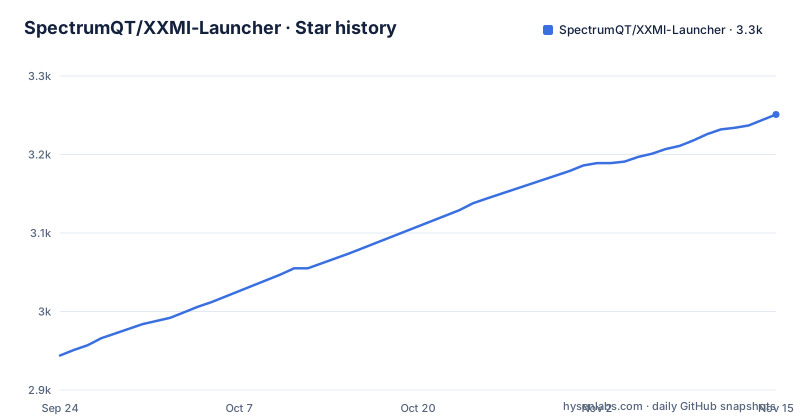
- SpectrumQT/XXMI-Launcher3,251 ★ · +307
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| SpectrumQT/XXMI-Launcher | 2.9k | 3.3k |
307 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The Paranoia Warning comes before the feature list
The first section of the README is not about the project. It is a warning, and it is the most direct thing on the page.
Some picky antivirus products may trigger false positives for XXMI .exe or .dll files. The project has no funds to satisfy what it calls Microsoft's endless greed, so it says, in its own words, that it is up to you to use them as is, build yourself or go by. Three Microsoft and community links back that up: the Defender documentation on false positives and false negatives, the Smart App Control documentation on code signing, and a Reddit thread about what code signing certificates cost.
So the shipped binaries are unsigned, the project expects them to be quarantined, and it offers three responses: accept them, compile your own, or walk away. That is an honest position to take about a tool that injects libraries into another program, and it is also the reason the requirements file pins a Python-to-C compiler.
What the warning does not do is mention accounts. There is no statement anywhere on the page about competitive rules, moderation, or what happens if the games detect the modification. For a tool that changes what a game client loads, that absence is the first thing a careful reader will notice.
Safe to Use means authenticity, and it sits beside the warning
The feature list has five entries, and four of them are about convenience.
One Ring launches and manages all the supported model importers in a unified way. Plug-and-Play configures any supported game and installs its XXMI instance automatically. Custom Launch can be configured to start the game in almost every possible way through advanced settings. Automatic Updates keeps the XXMI instances and the launcher itself up to date.
The fifth is Safe to Use, described as verifying the authenticity of XXMI libraries and of the launcher's own downloads.
The README does not explain the verification mechanism or establish that every download is safe. Treat authenticity verification as a project claim, obtain binaries from the official release page, and assess antivirus alerts rather than assuming they are false positives.
There is also an exclusion stated up front: the Google Play Games version of Wuthering Waves is not supported currently. One of the advertised games has a variant the launcher will not touch.
Six importers live in four accounts, and one is in a repository named TEST
The importer list is where the project's shape becomes visible, because nothing is in one place.
EFMI, the Endfield importer, and WWMI, the Wuthering Waves importer, are both under SpectrumQT, who also maintains the launcher. SRMI, the Star Rail importer, is nominally under SpectrumQT too, but its link points at a repository named SRMI-TEST.
ZZMI, the Zenless Zone Zero importer, and HIMI, the Honkai Impact importer, are under a different account, leotorrez. GIMI, the Genshin Impact importer, is under a third, SilentNightSound.
Three of the six carry a parenthetical link to an old repository, so those importers have been moved at least once and the page keeps the old addresses for people who still have them.
Now put that next to the authenticity feature. The launcher claims to verify the authenticity of XXMI libraries, and the set it is verifying spans six artefacts across four accounts, one of which is a repository whose name says it is a test. Nothing on the page describes what the check covers, whether the signature is checked against a key shipped in the launcher or fetched at runtime, or what happens when it fails.
The repository description names four games, GI, HSR, WW and ZZZ. The importer list has six entries, because Endfield and Honkai Impact are separate from Star Rail and Genshin Impact.
Thirty-one exact pins, and three of them are Windows-only
The requirements file is the most informative document in the repository, and it is a flat list of exact pins, `==` for all thirty-one of them.
Four entries explain the platform. `pywin32`, `winshell` and `WMI` are Windows integration libraries with no platform markers, and `pywin32` in particular cannot install on Linux. So `pip install -r requirements.txt` is a Windows operation, unconditionally, even though the launcher ships a portable build advertised for Linux through WINE.
Two entries explain the build. `Nuitka` compiles Python to C, which is how a Tk application becomes a native executable, and it is the same answer the Paranoia Warning gives when it offers to let you build the binaries yourself. A compiled Python binary looks unfamiliar to heuristic scanners, so the AV warning and the compiler choice are the same fact seen from two sides.
Two explain the interface. `customtkinter` is the widget toolkit, and `tkinterweb` with `tkinterweb-tkhtml` and `tkinterweb-tkhtml-extras` renders HTML inside the window. `Markdown` and `py-gfm` supply that content, and `darkdetect` picks the theme.
One is the clue to what the launcher does. `vdf` is the Valve Data Format library, which is how a Windows program reads Steam application manifests to find an installed game. Alongside `psutil` for process handling and `winshell` for shortcuts, that is the whole shape: find the game, start it with injected libraries, watch the process.
And the credentials for the authenticity check are visible too, in `cryptography`, `cffi` and `certifi`. The repository root also carries `Locale/` and `Themes/` directories, so the interface text and appearance live in the tree rather than inside the binary.
v2.4.1 follows v2.2.1 and no 2.3 tag is in sight
Three releases are visible, and their version numbers do not form a sequence.
v2.2.0 on 2026-06-08, v2.2.1 on 2026-06-11, and then v2.4.1 on 2026-10-03. The minor version steps from 2 to 4 with no 2.3.0 among them, and the gap between the second and third release is almost four months.
The last push to the branch shares its timestamp with the newest tag to the second, 2026-10-03, so the release was cut from the tip rather than from a branch. That is the healthy pattern, and it is the only thing about the release line that is.
The tree itself is short. `.github/`, `.gitignore`, LICENSE, README.md, requirements.txt and `src/`, plus the two content directories, `Locale/` and `Themes/`, and `public-media/` for images. There is no test directory, no build configuration, no continuous integration configuration and no issue template in that listing, in a repository whose whole purpose is distributing signed-or-not binaries to end users.
So the release cadence is verifiable and the build is not. The two things a security-conscious reader would look for are the two things the tree does not show.
Game rules and account risk
The project README does not promise that modifying a particular game is permitted or that an account cannot be penalized. Game publishers set their own rules and may change enforcement. Check the current terms and official support for the exact game and distribution before use, and decide whether the account risk is acceptable.
The license link points at a repository with a different name
The License section is one sentence: XXMI Launcher is licensed under the GPLv3 License. The link on the word licence points at `github.com/SpectrumQT/WWMI-Launcher/blob/main/LICENSE`.
That is a different repository name from the one this README lives in. This repository is XXMI-Launcher; the link goes to WWMI-Launcher.
The likely explanation is a rename, since the launcher and the Wuthering Waves importer share an author and a lineage, and the release artefacts have likely been renamed alongside. But the consequence stands either way: the licence a reader is sent to verify is not in the repository they are reading, and a project whose first section is a warning about unverified binaries is not a project that should route its own licence through a path that may no longer exist.
The rest of the page is symmetrical in the same way. The navigation links are Features, Installation, Included Model Importers, Support This Project and License, and four of those five are covered above. Installation is the section with the most detail and the least about how the thing works internally: two routes, an MSI for Windows and a portable archive for Windows and Linux through WINE 9.22 or newer, with the Visual C++ redistributable as a prerequisite for the portable one and a default location of `%AppData%\XXMI Launcher`.
What is absent is as informative as what is present. There is no architecture note, no description of how a model importer attaches to a running game, no uninstall procedure and no troubleshooting section.
Editorial conclusion
XXMI Launcher provides a shared interface for installing and updating supported game model importers. Download from the official release page, verify the game version, and review the game's current rules before use. The project's authenticity claim and an antivirus warning do not independently establish that a binary is safe or that a modification is permitted.
Frequently asked questions
What is XXMI Launcher?
It is a Python desktop application that installs and manages per-game model importers. The repository describes it as a modding platform for GI, HSR, WW and ZZZ, and the importer list runs to six entries across Endfield, Wuthering Waves, Zenless Zone Zero, Star Rail, Genshin Impact and Honkai Impact.
Is XXMI Launcher safe?
The project says it verifies the authenticity of its libraries and downloads, and warns that some antivirus tools may flag its unsigned files. These statements do not independently establish safety. Obtain releases from the official source, review the files and permissions, and assess the risks for your system.
Can XXMI Launcher get you banned?
The launcher README does not guarantee account safety. Game rules and enforcement vary and can change; consult the current terms and official support for the specific game before installing modifications. A lack of a warning is not evidence that a modification is permitted.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/spectrumqt-xxmi-launcher)Star history chart for your README
[](https://hysenlabs.com/projects/spectrumqt-xxmi-launcher)Was this useful?