Swizzin's install pipes a remote script into bash, and its unattended examples use a retired link
A simple, modular seedbox solution
At a glance
- What is it?
- Swizzin is a modular seedbox solution for Debian and Ubuntu, and the whole install is two lines that fetch a script from a short domain and run it as root. The project is unusually honest about the two things that catch people out, which are that escalating with the wrong form of the switch-user command silently breaks the installer's password check, and that it is a port of another commercial seedbox panel. It also ends by asking you to install a cryptocurrency miner.
- Who is it for?
- Swizzin is a sensible answer for someone who has outgrown a one-off seedbox script and wants a package manager for a box, with a single command set, on-call add-on packages during the run, and unattended installs for fleets. Three things to weigh before you use it on a machine you care about.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 69 days ago.
- What is it written in?
- Mainly Shell, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
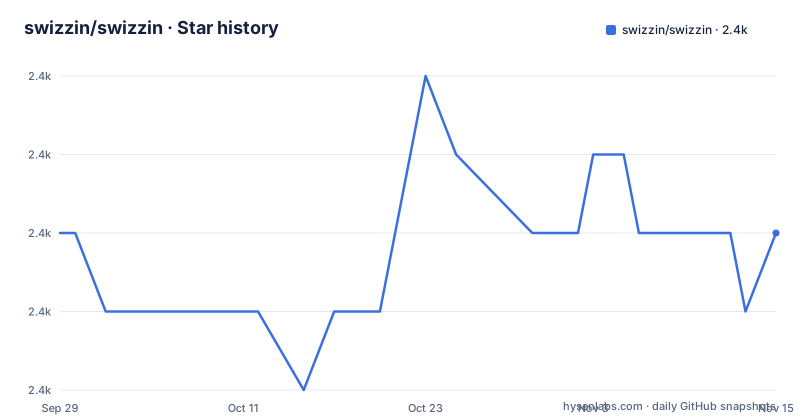
- swizzin/swizzin2,387 ★ · +0
| Repository | 2026-09-29 | 2026-11-15 |
|---|---|---|
| swizzin/swizzin | 2.4k | 2.4k |
0 Stars in the last 47 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The install is a piped script from a short domain, run as root
There are two ways to install and they differ only in the fetch tool:
bash <(wget -qO - s5n.sh) && . ~/.bashrcbash <(curl -sL s5n.sh) && . ~/.bashrcEach one pipes a remote script straight into a shell as root and then reloads your profile. There is no checksum to verify, no signature, no version flag and no way to read the script before it runs, and the domain is a short alias rather than the project host. That is the standard shape for this category of installer and the project is not unusual in choosing it, but it is worth stating plainly that you are trusting whatever that domain serves at the moment you press enter. The installer itself is interactive, navigated with the arrow keys, tab to move between fields, space to select and enter to confirm, so a first run asks its questions rather than assuming defaults.
The wrong switch-user form breaks the password check
One whole section of the page is devoted to a detail most installers would leave alone: the difference between the two forms of the switch-user command. The project requires you to be a full root login, either directly or by elevating with the login form, and explicitly says not to use the bare form or the shell form that is the default under one of the supported distributions. The stated symptom is concrete. The installer runs a password strength check, the binary is installed, and the check cannot find it, because the system binary directory and its derivative paths were never set properly by the escalation method. The explanation given is that the bare form changes the user while the login form goes through the whole login process and resets the environment as if you had logged in as root directly. It is a small failure that would otherwise cost an afternoon.
The unattended examples use a flag the page never explains
Four flags are described for custom and unattended setups, and three of them have a worked example. A local flag installs from a clone of your own fork rather than upstream. A user flag and a password flag take a username and a password, with packages as bare arguments, which is the most useful one for a fleet. An environment flag points at a file, and the repository ships an example environment file for it. The fourth flag, the one the example that demonstrates the whole feature actually uses, is never explained anywhere on the page. So the copy-and-paste case for unattended installs is the one you cannot verify from the documentation, and the password in that same example is passed as a command line argument, where it lands in the shell history. The other two examples also route through a short link domain that no longer resolves.
QuickBox's package repository is the ancestor, panel included
The page answers the lineage question directly and without hedging: the QuickBox package repository has been ported over, including the panel, so the web control panel people associate with the commercial product is part of what you get here. What changed is the shape of the interface. The project describes itself as revamping its own command set to reduce and consolidate the number of commands needed to manage a box, and it adds two capabilities the original does not describe: add-on packages can be installed while the installer is still running, and that run can be unattended. So the difference from QuickBox is not the catalogue but the ergonomics and the automation. For anyone choosing between the two, that is the axis to compare on, along with the operating system list, which is restricted to long-term-support branches of two distributions and does not include the containers the original is often deployed alongside.
Ten commands, one of them for a single hosting provider
The command list is short enough to read in a minute and it is the clearest statement of what the project is. There is a command to list every package in the repository with its description, commands to install and remove packages accepting several at once, commands to add and delete a user, a command to change a user's password, a command to update the box itself from the project host, and a command to upgrade one installed package. The last two are the interesting ones. One removes hardened kernels installed by a single hosting provider, which is a cleanup for a very specific environment and tells you the project carries provider-specific knowledge. The other starts a management interface for extra plugins of a particular torrent client, and can be invoked under its own short name as well as through the main command. The user management examples use joke usernames, which is a small indication of tone.
The page ends by asking you to install a miner
The donations section asks for money in two ways and then adds a third. Money goes through the project's sponsorship programme, and the page is explicit that a vendor profiting from running the project commercially should sponsor it. Individual contributions are welcome too. Then the last request on the page: if you have nothing to spare, donate your idle processor cycles to the maintainer's mining pool, which it says is easy to set up and costs you nothing, and gives you the command. It is opt-in and it is the maintainer's own pool, so it is not a red flag, but it is an unusual closing line for a licence-licensed infrastructure project and it tells you something real about who this is for. The other detail in that section is an ownership one: the sponsorship link points at a different account from the repository's own namespace, and so does the code quality badge at the top of the page.
Four commit gates for a shell codebase, and three support channels
The repository is small and entirely shell, and its root is mostly the machinery that keeps it that way: an editor configuration, attributes, a pre-commit configuration, a shell analysis configuration, a commit message linter and a commit message convention file. That is four separate gates between a commit and the repository, which is a lot of ceremony for a few hundred scripts, and it explains why the contributing guide asks you to read it first. Support is spread across three channels with instructions that do not quite agree. The header sends you to chat for community matters and to GitHub discussions for feature requests and to raise issues. A later section says the opposite about the issue tracker: not for technical support, not for feature requests, only for bugs. And the contributing section routes code discussion back to the chat. No releases are published, so the version number lives in the page heading and the changelog rather than in a tag.
Editorial conclusion
Swizzin is a sensible answer for someone who has outgrown a one-off seedbox script and wants a package manager for a box, with a single command set, on-call add-on packages during the run, and unattended installs for fleets. Three things to weigh before you use it on a machine you care about. That the install is a remote script fetched over a short domain and executed as root with no checksum, no signature and no tag to pin, which is the same trust model every seedbox script has and is worth weighing explicitly. That it manages the host rather than a container, so a mistake in one of its package scripts is a mistake on the box. And that the unattended examples as written will not run, because they use a link domain that no longer exists, so read the documentation site for the current form rather than copying from the page. For anything beyond a throwaway box, treat the shell scripts as the thing to review, since that is the entire codebase.
Frequently asked questions
how to install swizzin
As root, paste one of two one-line commands: one fetches a script with wget and the other with curl, each pipes it into bash, and each then reloads your shell profile. The installer asks its questions interactively, and a separate set of flags supports unattended installs.
swizzin vs quickbox
Swizzin is a port of the QuickBox package repository, panel included, restructured around a single command. What it adds is the ability to install add-on packages while the installer is still running, and unattended installs with flags for user, password and packages.
swizzin vs docker
The page does not compare the two. It states that Swizzin installs directly on Debian 11 and 12 or Ubuntu 20.04, 22.04 and 24.04, as root, with its own package scripts managing the host, rather than running inside a container.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/swizzin-swizzin)Star history chart for your README
[](https://hysenlabs.com/projects/swizzin-swizzin)Was this useful?