Taiga UI's compatibility table leaves its last column empty and its ranges contradict its labels
Angular components library for awesome people
At a glance
- What is it?
- An Angular component library publishing two major versions from one branch seconds apart, whose readme badges point at its development kit package rather than its components package, whose fifty-project adoption figure is internal to one company, and whose Figma files exist only for the two majors that no longer get support.
- Who is it for?
- Taiga UI suits an Angular team on the current major who wants per-component imports and a design system that is actively automated, and it is a poor fit if you need a published migration path from an older major, because the line you would come from is already out of support. Check six things first.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
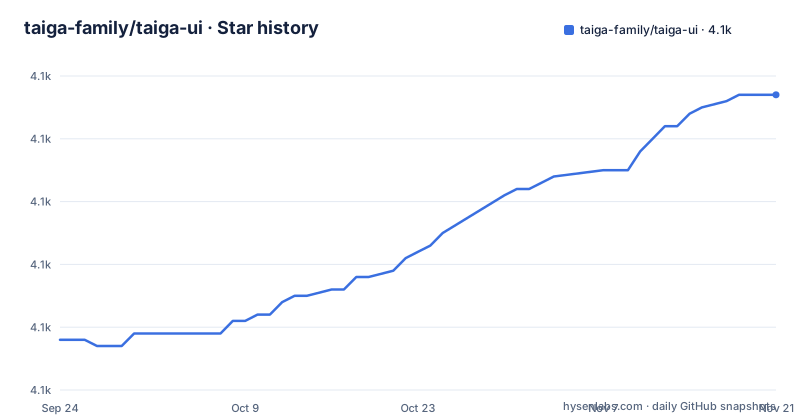
- taiga-family/taiga-ui4,097 ★ · +39
| Repository | 2026-09-24 | 2026-11-21 |
|---|---|---|
| taiga-family/taiga-ui | 4.1k | 4.1k |
39 Stars in the last 58 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The compatibility table's last column is empty in every row
The version compatibility table has four columns and one of them delivers nothing. The headers are the library version, the Angular range, a support status, and a column headed latest version. All four data rows leave that fourth cell blank. So the table's most directly useful piece of information, which exact release of the library is current on each line, is present as a heading and absent as content, and a reader has to go to the registry to get it. The remaining three columns also disagree with each other. The current line covers Angular 19 and later, the previous line covers 16 and later, and the two lines below those are marked as no longer supported. But the third line, already unsupported, claims compatibility from Angular 12 all the way to 21, which is a wider and newer range than the supported current line claims. So the compatibility range does not track the support status: the widest Angular coverage in the table belongs to a version nobody should adopt. Two lines also both run to the newest Angular, so a project on the newest framework has two candidate library majors. One date in the table is written in day-month-year order in an otherwise English document.
Two major versions were published seconds apart from a branch the file calls v5 only
The release record shows the two supported lines being cut together. The newest release of the current major was published at ten past ten in the morning, and a release of the previous major was published thirty-seven seconds earlier the same day. A third release of the current major is a week before that. So the project maintains two majors in parallel and publishes to both, which is a genuine service and not something to criticise. The awkward part is the file's own description of where the work happens. The versions section says the main branch is all of the current work and is against v5, and that previous majors live on their own branches, listing a branch for each older version. A v4 release was nevertheless cut from the same tree that minute before the v5 one. So either a script cherry-picks into the older branch, or the older branch only receives patches, and nothing in the file says which. One more detail makes the cadence concrete: the previous major's release number carries a patch component above one hundred, so that line has shipped over a hundred patch releases. The branch itself was last pushed three days before those releases were cut, so publishing runs from a pipeline rather than from the most recent commit.
Both npm badges point at the development kit, and the root package is private
The readme opens with a row of badges, and two of them are package registry links. Both point at the component development kit package, and they do so under two different hostnames, one of which is the canonical registry host and the other an alias. There is no badge for the components package at all, which is the package most people looking at this file want. The reason is visible in the manifest. The root manifest is named for the components package, carries the same version number as the newest release, and is marked private, so it is never published. What is published are the workspace packages under a projects directory. So the root version field is a single number that has to be kept in step across every published package, and it is the number a reader sees on the repository page while the packages they will actually install are somewhere else. The two descriptions in the repository do not match either: the one-line summary calls it a component library for awesome people, which is a joke, while the manifest describes components, services, directives and tools for building high quality interfaces with a modern Angular framework.
The fifty project figure counts one company's own work
One of the readme's selling points is headed as a claim about staying power, and it deserves reading closely. It says the library started as an internal product in the company's own codebase, that it is used by more than fifty projects in production now, and that it is here to stay. The fifty is real usage, but it is usage inside one organisation, which is a very different thing from ecosystem adoption, and the readme does not claim otherwise. What it does do is present internal adoption plus a promise as the answer to whether the project will survive, and a promise is not a fact a reader can check. There is corroborating evidence in the repository, which is worth more than the sentence: an automated dependency update service is wired in, a task runner orchestrates the builds, a dead-code detector and a spell checker run alongside the linter, and two major lines are still receiving releases. The other bullet in that group is the one to weigh against the library's headline claim. It says the library is big, counts a hundred and thirty or more components and a hundred or more directives plus dozens of tokens, and then adds that it is not over yet. A library that is still growing is in tension with a library whose main pitch is that you can import one entity and carry nothing redundant, because the surface you audit today is not the surface you inherit later.
The design files exist only for the two versions nobody should adopt
There is a line about Figma in the getting-started section, and it is the only place the design side of the project is mentioned. It says the Figma library is available only for the 2.x and 3.x versions, links a community file, and adds that the next version of the Figma library is in progress for the latest version of Taiga UI. Put that next to the compatibility table and the position is clear. The two versions with published design files are the two the table marks as no longer supported, and the version the table marks as current has no design file yet. So a designer or a front-end developer picking this library for a new project today is working from a component API whose visual source does not exist, while the visual source that does exist describes an API two majors old. The link is also to a community file rather than a library published by the team, which is a reasonable way to share one and a less reliable thing to build a design system on. The file does not say what in progress means or when the current version's library is expected, and it is the only sentence about design tooling in the whole readme.
Two release tools, and the plain one skips the commit hook
The manifest has four release scripts and they use two different tools. One invokes a conventional release tool directly, and it passes a flag that skips verification. The other three invoke a TypeScript script in the repository's scripts directory, passing a mode argument of major, minor or patch. So a maintainer has one command that cuts a release the conventional way with verification disabled, and three commands that cut one through a script, and the file does not say which is the live path or whether the two produce the same artefacts. The verification flag is the part worth noticing in context. The repository installs a git hook manager automatically on install, and it carries both an agent instruction file and a contributor file, so commit conventions are clearly enforced somewhere. The release path that bypasses verification is the one with the shortest name and no mode argument, which is the one a tired maintainer reaches for. Alongside the release scripts sit the everyday quality gates: a linter invoked over the whole tree, a formatter, a spell checker, and a dead-code detector, each with its own configuration file at the root, with the linter's configuration itself written in TypeScript. There is also an editor spell-check dictionary at the root, which tells you the project expects people to contribute prose as well as code.
A task runner, four quality tools, and a format command that names the lockfile on the command line
The build is orchestrated by a task runner configured at the root, and the scripts show what it is doing. Building the libraries runs the target across every project and excludes the demo application; building the demo has its own target and a variant configured for a different build mode. So the workspace is at least a demo application plus the published libraries, and the library build deliberately skips the app. A browser test project sits alongside them, opened with an explicit project path. The formatter is the interesting one: it is invoked with the package lockfile negated as a leading path argument, and with an instruction to take its ignore list from the git ignore file rather than from a formatter config. Excluding one file on the command line while sourcing the rest of the scope from version control is a defensible choice, and it is also a choice that will not survive someone reformatting the script. The spell checker is pointed at dotfiles as well and takes the same ignore file. Three separate TypeScript configs sit at the root, one for building, one general and one for specs, which is the usual arrangement for a project that compiles its own sources. Everything is npm workspaces under a projects directory with a package lock file, not a task-runner-native lock.
The root holds a committed environment file and three hosted service configurations
Look at what is tracked at the top level and the infrastructure becomes visible. There is a coverage service configuration, and the badge row links that service, so coverage is measured and reported. There is a pair of Firebase configuration files, so a hosting or database project is attached to this repository. There is a documentation-context configuration for a third-party service that serves documentation to language models, which is a recent addition and an interesting thing to find in a component library. There is a deploy workflow for GitHub Pages in the badge row, so the documentation site is published from the repository. And there is an environment file, committed, with no example file beside it, which is the reverse of the usual convention and the single item here worth acting on before contributing anything. The badge row also includes a third-party visitor counter, so viewing the readme on the forge causes a request to an external counting service. Two editor directories, a dev container definition, a spell-check dictionary and two agent instruction files complete the picture. The positive reading is that the maintenance story is heavily automated, and the caution is that a repository this heavily wired to external services has more places to change than a component library strictly needs.
Editorial conclusion
Taiga UI suits an Angular team on the current major who wants per-component imports and a design system that is actively automated, and it is a poor fit if you need a published migration path from an older major, because the line you would come from is already out of support. Check six things first. Two major versions ship from the same branch, so the version you get depends on which line a release script targets. Both readme badges point at the development kit package, not the components package. The table meant to tell you which Angular versions work leaves its most useful column blank and its ranges do not track its own support labels. The adoption figure counts projects inside one company. The design files are published only for the two unsupported majors. And the library states it is still growing, which means the bundle you audit this quarter is not the bundle you will have next quarter.
Frequently asked questions
what is taiga ui
A fully tree-shakable Angular component library made of several base libraries and add-ons, published as multiple packages rather than one, using Angular's secondary entry points so a single component can be imported on its own. It is written in TypeScript in strict mode, and every component uses OnPush change detection.
is taiga ui free
It is released under the Apache 2.0 licence, declared in the workspace manifest and linked from the readme's licence badge, with a licence file at the repository root. The readme also points at a getting started page and a browser-based starter, both free to use.
Which Angular versions does Taiga UI support?
The readme's compatibility table maps four library majors to Angular ranges. The current line targets Angular 19 and later, the previous line targets 16 and later with long term support ending on 01.01.2027, and the two below are marked no longer supported even though one of them claims a wider range. The table's final column is empty in every row.
How do I install Taiga UI?
The readme contains no install command. It points at a getting started page on the project website and at a browser-based starter, and the two registry badges at the top of the file both point at the component development kit package rather than the components package.
How large is the Taiga UI component library?
The readme states a hundred and thirty or more components, a hundred or more directives, and dozens of tokens, utilities and tools, and adds that the library is not finished growing. It also says the library began as an internal product and is used by more than fifty projects in production inside that one company.
Does Taiga UI have a Figma component library?
A Figma file is linked for the 2.x and 3.x versions only, both of which the compatibility table marks as no longer supported, and the readme says the library for the latest version is in progress. The link points at a community file rather than one published by the team.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/taiga-family-taiga-ui)Star history chart for your README
[](https://hysenlabs.com/projects/taiga-family-taiga-ui)Was this useful?