Verify's source is MIT and its binaries carry a maintenance fee from September 2026, checked at build time against a sponsor list frozen when the package was packed
Verify is a snapshot testing tool that simplifies the assertion of complex data models and documents.
At a glance
- What is it?
- Verify is a .NET snapshot testing tool that serialises each test result to a file named after the test and compares on the next run. Its README is a generated file, its source is open, and a maintenance fee now applies to the official builds and published packages used by revenue-generating organisations and government agencies, verified during the consuming project's own build from a sponsor list bundled at pack time.
- Who is it for?
- Use Verify if you want to assert on complex objects and generated documents by reviewing a diff rather than by writing assertions, and if the cost model suits you. Seven documented routes for accepting a snapshot mean the workflow fits whatever your review process is, including a plain diff tool and a file rename.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly C#, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
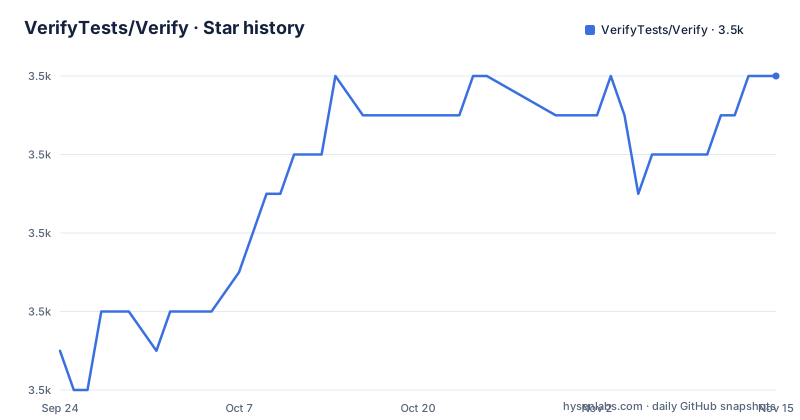
- VerifyTests/Verify3,474 ★ · +7
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| VerifyTests/Verify | 3.5k | 3.5k |
7 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The README is a generated file, and its source sits beside it
The first thing in the README is an instruction not to edit it.
A comment at the very top says the file is generated, names the tool that generates it, names the source file, and says to edit the source and then run the tool.
The root listing shows both files. There is a readme file and a readme source file, both in lower case, and the generated one is the lowercase readme rather than the conventional uppercase name. So a reader arriving at the repository sees two prose files with almost identical names and one of them is generated from the other.
The generation marks are still visible further down the file. The introduction paragraph is wrapped in a comment naming an include path and an end marker, and the supporters section is wrapped the same way. So the content has been spliced in from separate source documents, and the seams are left in the output.
That is why the file is long and consistent: several sections are maintained elsewhere and pulled in. It is also why the language is slightly odd in places, such as a section that introduces a list and says the approach selected is a personal preference without ever stating which one the project prefers.
The licence is open source and the official builds are not
The repository is MIT licensed, and there is a callout immediately below the introduction that changes what that means for some users.
Every version released after the first of September 2026 is covered by a maintenance fee, for organisations that generate revenue and for government agencies. The callout says twice, in the same block, that the source code remains open and free.
The section below it is more precise. The project participates in a named programme for the fee. The source stays freely available under the terms of the licence file. The fee covers the use of the official binary releases and the packages published to the registry, by organisations that generate revenue from them. And the date boundary is explicit: versions released on or before the first of September are not covered.
So the model is source-available with a charge on distribution. The four tiers are five dollars a month for an organisation with fewer than forty employees, twenty for forty to two hundred, thirty for two hundred to a thousand, and a hundred above a thousand, paid by sponsoring the project at the matching tier.
The releases in this repository's history are all after the boundary: three tags in the last ten days, at version 33.x.
The check runs in your build, and the README says exactly what it does not do
From version 33, sponsorship is verified at build time by a separate tool, and the paragraph describing it is mostly reassurance.
Three things it does not do, in one sentence: it does not phone home, it adds no runtime dependency to the packages, and it issues no licence keys.
That is a specific set of denials, and each one closes a door an author of such a scheme would normally leave open. No network call means a build works offline. No runtime dependency means the packages are unchanged for everyone who is not subject to the fee. No keys means there is nothing to store, expire or leak.
What remains is a build-time comparison, and the mechanics of that are described next. A sponsoring organisation declares its account once, in a build properties file at the root of its own repository, and that single declaration covers every project and every package it consumes.
<PropertyGroup>
  <Verify_GitHubSponsorAccount>your-github-account</Verify_GitHubSponsorAccount>
</PropertyGroup>
So the declaration lives in your project, not in this one. The check compares that account against something bundled into the package.
The bundled sponsor list is frozen at pack time, so a new sponsorship needs a second property
This is the detail that will cost somebody an afternoon, and it is stated in one paragraph.
Each version bundles the sponsor list as it stood when that version was packed. So if you sponsor after a version was built, your account is not in that version's list, and the build-time check fails.
The fix is a second property: a start date for the sponsorship, which the build reads alongside the account name, valid until you upgrade to a version packed after your sponsorship began.
And there is a third case. A sponsorship made private on the GitHub side is never bundled at all, not even in a later version, because the tool cannot see it. That one needs a second property with a month-precision expiry, settable at most twelve months out, and renewed when it lapses.
So the lifecycle of a sponsorship in this scheme is: declare the account, upgrade past your start date, and then renew a rolling expiry every year if your sponsorship is private. A public sponsorship needs only the account name and one upgrade.
Seven ways to accept a snapshot and a refusal to recommend one
The snapshot management section opens by calling accepting or declining a snapshot part of the core workflow, and says there are several ways to do it.
Then it says the approach selected is a personal preference. That is the whole recommendation.
Seven routes follow. One is a Windows tray application. Two are test runner plugins for two commercial development environments, each linked to its source. One goes through the clipboard. One is to edit the file by hand inside whichever diff tool the project launched, with a note that some tools have commands to automate that. One is to edit the file system directly by renaming the file the run produced to the file the comparison expects, which the file notes can be scripted to accept everything matching a pattern in bulk. And one is a command line tool distributed as a .NET tool.
So the honest answer is that a human decides, with a diff. That is a defensible position for a tool whose value is making unexpected changes visible, and it is also why there is no built-in update flag in the core: accepting a new snapshot is a review decision, not a command.
Eight target frameworks, three of them .NET Framework, on a .NET 9 SDK floor
The requirements section is two bullets and they pull in opposite directions.
The first lists eight supported runtimes: three .NET Framework versions and .NET Framework 4.8.1, then .NET 6, .NET 8, .NET 9 and .NET 10.
The second sets a floor for the software development kit at 9.0.301 and above.
So the library ships assemblies for a framework that reached the end of its support years ago, and can only be built by a toolchain from the .NET 9 era. Those are independent choices, and both are defensible: a testing library wants to be consumable from older projects, and a project wants its contributors on a current toolchain.
What it costs is that a team on an older toolchain cannot build the project from source, which matters if you wanted to fork it. It also means the package set spans four years of runtime releases with the oldest still supported in the compatibility list.
The runtime list is not the only way to tell which frameworks matter though: seven packages are published, one per test framework the project supports plus one for clipboard integration.
The release-notes link climbs out of the repository and lands on the organisation's milestones
One line under the maintenance fee callout tells you where the release notes are, and the link is relative with two parent segments in it.
That path resolves above the repository rather than inside it, to a milestones page belonging to the organisation. So the release notes for this project are not in the project and are not in the repository: they are issue milestones on an account-level page.
That is a real choice. Milestones aggregate pull requests and issues, so a release note assembled from them is close to a generated changelog and needs no file to be maintained.
The cost is that the link is not stable. Anything that reorganised at that level breaks it, and a reader who clicks it from a local clone has no way to know whether what they are looking at is this project's history or something else that happened to be on the same page.
The rest of the file's internal links are inconsistent about this. Some are repository-relative, some are absolute paths starting at the site's documentation root, and this one is the only one that leaves.
The support section is an include, and its four sponsor links carry tracking parameters
The supporters section is four entries, and it was assembled from a source document rather than written here: it is wrapped in a comment naming an include path and an end marker.
The four are a commercial entity framework extensions library described as a major sponsor that is proud to contribute to the development, a development environment vendor described as the editor used to develop it, an identity and access vendor described as providing authentication and authorisation via, and a browser testing service described as providing browser testing via.
Each link carries two query parameters naming the project as the source and the individual as the medium. So following the supporter list from this readme lands on four vendor pages with attribution already attached.
Two of the four descriptions are phrased as capabilities, authentication via and browser testing via, where the others are phrased as relationships, a major sponsor and used to develop it. So the section mixes sponsorship with tooling credit and does not distinguish them.
None of this is hidden, and the sponsorship tiers are documented elsewhere in the same file. It is just the one part of the readme that is neither documentation nor code.
Editorial conclusion
Use Verify if you want to assert on complex objects and generated documents by reviewing a diff rather than by writing assertions, and if the cost model suits you. Seven documented routes for accepting a snapshot mean the workflow fits whatever your review process is, including a plain diff tool and a file rename. Three things to settle before you commit to it. What the fee means for you, because the source stays under its licence while the official builds and the published packages carry a maintenance tier from September 2026, for revenue-generating organisations and government agencies, ranging from a few dollars a month for a small team to a hundred for a large one, with earlier versions exempt. How the check works mechanically, because it runs inside your build rather than at runtime, adds no dependency and issues no keys, but it compares against a list frozen when the package was packed. And what you are signing up for in supported runtimes, since it targets eight frameworks including three .NET Framework ones while requiring a .NET 9 SDK to build.
Frequently asked questions
What is Verify?
It is a snapshot testing tool for .NET. During a test's assertion phase it serialises the result and stores it in a file matching the test name; on the next run it serialises again and compares, failing the test if the two differ, either because the change was unexpected or because the reference snapshot needs updating. It is MIT licensed, targets eight runtimes including three .NET Framework versions, requires a .NET 9 era SDK or above, and publishes seven packages.
What is the Open Source Maintenance Fee for Verify?
The project participates in a named programme. The source code stays freely available under the licence, while a fee covers the use of the official binary releases and the packages published to the registry, by organisations that generate revenue and by government agencies. Every version released after 1 September 2026 is covered and earlier versions are not. The tiers are five dollars a month under forty employees, twenty for forty to two hundred, thirty for two hundred to a thousand, and a hundred above a thousand.
How is Verify sponsorship checked?
At build time, from version 33, by a separate tool. The README states that nothing phones home, that the check adds no runtime dependency to the packages, and that it issues no licence keys. A sponsoring organisation declares its account once in a build properties file at the root of its own repository, and that covers every project and every package it consumes.
Why does the Verify sponsorship check fail after I start sponsoring?
Each version bundles the sponsor list as it stood when it was packed, so a sponsorship that began later is not in that version's list and needs a second property naming its start date, valid until you upgrade to a version packed after it began. A sponsorship made private on the hosting site is never bundled at all, so it needs a third property with a month-precision expiry, settable at most twelve months out and renewed when it lapses.
How do I accept a Verify snapshot?
Seven routes are documented, and the file says the approach is a personal preference rather than recommending one: a Windows tray application, test runner plugins for two commercial development environments, the clipboard, editing the file inside the diff tool the run launches, renaming the file the run produced to the expected name on disk which can be scripted by pattern, and a command line tool distributed as a .NET tool.
Which runtimes and test frameworks does Verify support?
Eight runtimes are listed, from three .NET Framework versions through .NET 6, 8, 9 and 10, and building from source requires a software development kit at 9.0.301 or above. Seven packages are published on the registry, one for each supported test framework plus one for clipboard integration. The readme itself is a generated file, produced from a separate source file at the repository root.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/verifytests-verify)Star history chart for your README
[](https://hysenlabs.com/projects/verifytests-verify)Was this useful?