FluxDown runs one Rust engine behind four client shells
FluxDown is a media downloading and processing utility with resumable transfers, queue management, and local automation controls.
At a glance
- What is it?
- A download manager for six protocols, published as a desktop application, a mobile application, a web interface and a command line tool, with a server build for network attached storage and a browser extension for three browsers. The packaging surface is the widest part of it, and the dependency file is where the engineering decisions are recorded: a pinned fork of the desktop framework and a workspace that denies two ways of panicking.
- Who is it for?
- Use this if you need one download engine behind several interfaces, especially if you run network attached storage or want the browser's downloads funnelled into a queue you control. Two things to decide before you install it.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
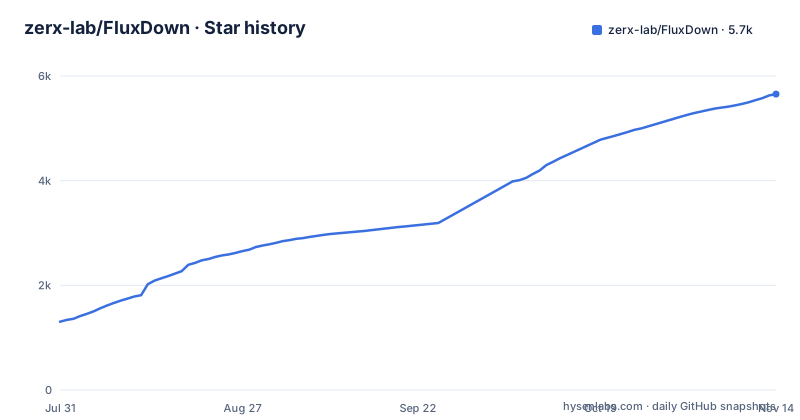
Star history
- zerx-lab/FluxDown5,655 ★ · +4,350
| Repository | 2026-07-31 | 2026-11-14 |
|---|---|---|
| zerx-lab/FluxDown | 1.3k | 5.7k |
4,350 Stars in the last 106 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
One product, five lockfiles, four client shells
Read the repository root as a manifest of what this project actually is. There are lockfiles for Rust (Cargo.lock) and JavaScript (bun.lock). There are four client implementations described as sharing one engine: a native desktop shell, a mobile application, a web interface, and a command line tool, with the desktop tray keeping the service alive after the window closes. There is a headless server build with an embedded web interface for network attached storage, packaged for two NAS vendors, a router distribution, and two container ecosystems. And there is a browser extension for three browsers plus a userscript. So the engine is the product and everything else is a shell around it, which is the right architecture for this kind of tool and a large amount of surface to keep working.
The desktop framework is a pinned fork with a version skew warning
The workspace dependency file is where this project keeps its real notes, and they are in Chinese. The desktop framework is not the upstream package. It is a fork, referenced through a renamed package with version 0.1.12, and the comment above it says that on upgrade the gpui-kit packages take the same release and gpui-fast takes the version that gpui-kit release locks. It then does the thing that trips people up: the fork packages are pinned at one version while the related base, component and asset packages sit at a different version line entirely. So the desktop stack is three related packages on two version numbers, coordinated by a comment rather than by a constraint. The rest of the file is more conventional, with serialisation crates, an error crate and a Windows resource crate, and a resolver setting that matches the newest language edition.
Unwrap and expect are both denied workspace wide
The workspace declares its own lint configuration and denies a long list of lints. Two rules are worth reading twice, because they are unusual for application code: unwrapping a result is denied, and expecting a value is denied. In a codebase that parses media container formats, tracks peers over two different distributed hash tables, and decrypts segmented streams, that is a real policy rather than a style preference. It forbids the two ways a Rust program panics on an unexpected value, which means every failure path is a returned error instead. The rest of the list follows the same instinct: no todo, no unimplemented, no ignored future, no discarded result, and unsafe operations have to be documented at the block.
The server binds every interface by default and says so
The network attached storage section is the most careful operational writing in the file. The current headless service is two binaries that must be installed into the same directory, with an embedded web interface, and the Docker image keeps the name ghcr.io/zerx-lab/fluxdown-server. The default listen address is every interface on one port, with an environment variable to override it. Then the mitigations, all of them things the operator has to do: set it up on a trusted network before exposing it, put your own TLS-terminating reverse proxy in front for remote access, supply the access token through the environment or a secret manager rather than a committed file, and note that the token initialises the key only if none has been set already. The access key itself has a stated shape, a length range and a requirement that it contain both a letter and a digit.
Analytics are opt-out and the file refuses to call itself zero telemetry
The privacy paragraph is three claims and one retraction, and the retraction is the part worth quoting. Local downloads do not require an account. The cloud features are optional. Anonymous installation counts and daily active statistics are controlled by a setting and can be switched off, and they do not collect download or task information. And then: this is not a zero telemetry application. Plenty of projects would have stopped at the third sentence. The distinction being drawn is precise, because the thing that is on by default is the count of installations and the count of daily actives, which identify the installation rather than the person or the work, and the file says so instead of rounding that up to a claim of having no telemetry at all. The account requirement is the other half: local use needs none, so the telemetry is not a toll for using the tool locally.
Alt+Click bypass overrides a deliberate user gesture
The browser integration line in the features table lists download interception, streaming media sniffing, Alt+Click bypass, right-click send and connection diagnostics. The extension is published for Chrome, Edge and Firefox, connects to the desktop agent through Native Messaging, and a Tampermonkey userscript is also available.
The BitTorrent library is patched to a commit on the author's own fork
The server build starts from a checkout with one compose command, after which you open http://<server>:17800/ and set an access key in the first-run wizard:
docker compose -f docker/docker-compose.yml up -dEditorial conclusion
Use this if you need one download engine behind several interfaces, especially if you run network attached storage or want the browser's downloads funnelled into a queue you control. Two things to decide before you install it. The licence is copyleft with network use covered, so check what that means for a deployment other than your own before you put it on a shared host. The default server build listens on every interface, and the documentation's answer is to set it up on a trusted network and put your own reverse proxy in front of it, which is advice rather than a default worth inheriting.
Frequently asked questions
What is FluxDown?
An open source download manager for HTTP and HTTPS, FTP, BitTorrent with magnet support, the legacy eD2K network with a distributed hash table, and adaptive streaming formats, published under a copyleft licence. One engine in Rust is shared by a native desktop application, a mobile application, a web interface, a command line tool and a headless server build, plus a browser extension.
What platforms does FluxDown ship builds for?
Windows on both architectures, macOS on both, Linux, Android across three binary interfaces plus a universal package, and a NAS or server build packaged as a container image, as packages for two NAS vendors, for a router distribution, and through third party templates for two container ecosystems. Each desktop platform offers an installer and a portable archive.
Does FluxDown collect telemetry?
Local downloads do not require an account and the cloud features are optional. Anonymous installation counts and daily active statistics are controlled by a setting and can be disabled, and they do not collect download or task information. The project's own wording is that this is not a zero telemetry application.
How do I run the FluxDown server build securely?
The file says server mode listens on all interfaces on one port by default, with an environment variable to override the bind address, and tells you to set it up on a trusted network before exposing it and to put your own TLS-terminating reverse proxy in front for remote access. The access key is set in a first-run wizard with a stated length and character rule, and can be initialised unattended through an environment variable rather than a committed file.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/zerx-lab-fluxdown)Star history chart for your README
[](https://hysenlabs.com/projects/zerx-lab-fluxdown)Was this useful?