CodeWhale: A Provider-Agnostic Terminal Agent That Keeps Your Model Choices Open
Open-source, community-driven agent harness. Why Codewhale:** **No lock-in.** DeepSeek, Claude, GPT, Kimi, GLM, 30+ providers, and your own vLLM, SGLang, or Ollama, no key required, run through one runtime and one toolset.
At a glance
- What is it?
- CodeWhale is an open-source, Rust-based coding agent for the terminal that connects to 30+ hosted providers or local models like Ollama and vLLM through a single runtime. It focuses on user control with Ask, Auto-Review and Full Access permissions, undo, and a `/receipts` list of the files changed and commands run.
- Who is it for?
- Adopt CodeWhale if you want a terminal-based coding agent that avoids provider lock-in, supports local models, and gives you visible approval controls and undo capabilities. Skip it if you need a fully documented, production-hardened agent with detailed security guarantees, or if you prefer a project with a longer track record.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
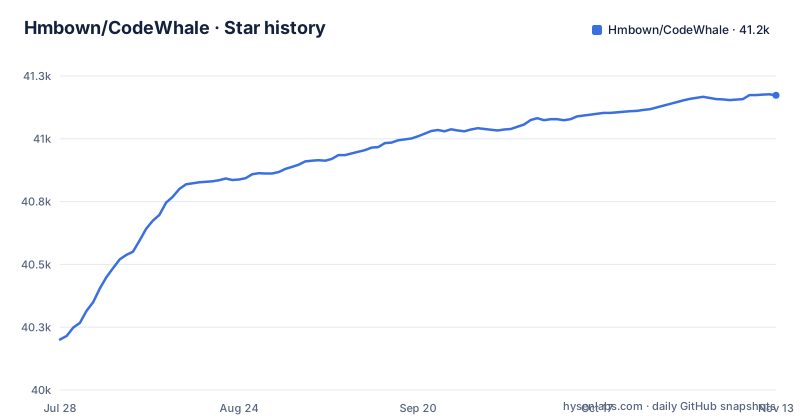
- Hmbown/CodeWhale41,173 ★ · +972
| Repository | 2026-07-28 | 2026-11-13 |
|---|---|---|
| Hmbown/CodeWhale | 40.2k | 41.2k |
972 Stars in the last 108 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What CodeWhale Actually Solves
The value proposition is not just about choice. It is about control. CodeWhale offers approval modes that make the agent's actions visible, and it has commands like `/undo` and `/restore` to revert changes. This addresses a real concern: agents that operate autonomously can make unwanted edits. CodeWhale's design tries to give you a safety net. It is for developers who want to delegate coding tasks but keep the ability to stop or reverse the agent's work.
How CodeWhale Works: The Mechanism Under the Hood
CodeWhale is a Rust application that runs in your terminal. It is not a library; it is a harness that connects your prompts to a model provider and executes actions on your local machine. The README describes a flow: you give a natural language instruction like "Fix the failing tests and explain what changed," and the agent reads your repository, edits files, runs commands, inspects results, and keeps working toward the goal. The core architecture involves a runtime that manages the conversation with the model, a toolset for file operations and command execution, and a policy stack for authorization. The documentation references an "authorization order" in `docs/AUTHORIZATION_ORDER.md`, which defines the exact policy stack. This suggests a layered system: repository rules, approval modes, and optional OS sandboxing. The README defines three modes, Plan, Work and Operate, and three permissions, Ask, Auto-Review and Full Access. Plan reads and searches but changes nothing, Work edits files and runs commands, and Operate keeps going until the goal is verified or it needs input. The agent can also coordinate multiple agents in a "fleet," as mentioned in `docs/FLEET.md`, and it supports MCP servers and skills for extensibility.
Getting CodeWhale Running: Installation and First Steps
On macOS and Linux the README gives `curl -fsSL https://codewhale.net/install.sh | sh`, and `npm install -g codewhale` is one of the alternatives, followed by `codewhale`. The first run guides you through connecting a provider or staying offline. There are also alternative installation methods: Cargo, Docker, Nix, Scoop, prebuilt archives, Android/Termux, and a CNB mirror. This breadth is useful for users on different platforms. Once installed, you can either open the interactive TUI by typing `codewhale` or run a one-off task with `codewhale exec "fix the failing tests and explain what changed"`. The `exec` command is for non-interactive use, which is handy for scripting or CI. Tab completion is available for shells: `codewhale completion bash|zsh|fish|powershell|elvish`. To switch providers or models, you use the `/model` command inside the TUI. The README also mentions `/goal` to set a durable objective, `/undo` to revert the last turn, and `/restore` to return to an earlier snapshot. Configuration is documented in `docs/CONFIGURATION.md`, and there is a local web client mentioned in `docs/WEB.md`.
The Safety Model: Approval Modes and Undo
CodeWhale's safety approach is built around visibility and reversibility. The README lists approval modes: Ask, Auto-Review, and Full Access. The README describes them: Ask applies file edits in your repository without asking and asks before shell commands that are not read-only, Auto-Review lets rules and a reviewer model approve routine calls and refuses high-risk ones, and Full Access never asks and turns off Codewhale's sandbox. The documentation for "authorization order" in `docs/AUTHORIZATION_ORDER.md` is meant to clarify the exact policy stack, but verify what it says. There is also optional OS sandboxing for a stronger execution boundary where supported. This is a meaningful feature because running an agent that edits files and executes commands on your machine carries risk. The `/undo` and `/restore` commands are the key safety nets. `/undo` reverts the last turn, which is useful for rolling back a single mistake. `/restore` returns the workspace to an earlier snapshot, which suggests the agent takes snapshots of the repository state. This is a practical approach: you can experiment with agent-driven changes and revert if things go wrong. The safety model is a trade-off: it gives you control, but it relies on you actively using these commands. Full Access turns off Codewhale's sandbox.
Limitations and Failure Modes
The README points to the docs folder for details, so read the docs to understand the safety guarantees. Another limitation is that CodeWhale is a young project, with a version number of 0.10.2 (released 2026-10-24). That suggests it is pre-1.0 and may have breaking changes or incomplete features. The README says it is "improved in public with the people who use it," which is a community-driven approach, but it also means the project's direction is not fully stable. A specific failure mode: if you use a provider with unknown pricing, the README says "Unknown model prices stay unknown instead of being reported as free." This is an honest approach, but it means you might not know the cost of a task until after it runs. Also, the agent runs on your machine with the access you grant it. If you grant Full Access, the agent can run arbitrary commands. `codewhale exec --auto` uses Full Access by default, so shell commands have no Codewhale sandbox unless you add `--sandbox workspace-write`. For scripts and CI, `codewhale exec` runs one task without the interface, and its `--auto` option uses Full Access, so add `--sandbox workspace-write` if you want to keep the shell sandbox.
Comparison with Alternatives
The main alternatives are agents that are tied to a specific provider. CodeWhale's key difference is provider neutrality. CodeWhale lets you use any of 30+ providers or local models, and you can switch with `/model`. Another alternative is Aider, which is an open-source terminal-based coding agent that supports multiple models, but Aider is Python-based and focuses on git integration. CodeWhale is Rust-based, which may offer better performance for a terminal tool, but the README does not provide benchmarks. The difference is in the runtime and the extensibility: CodeWhale supports MCP servers and skills and has an agent fleet feature. If you want to run your own vLLM or SGLang server, CodeWhale explicitly supports that, which is a strong point for users who want privacy or cost control. The choice depends on whether you prioritize a Rust-based tool with a TUI and fleet coordination, or a Python tool with a longer history.
Maintenance and Upgrade Cost
The project is actively maintained, with three recent releases: v0.10.2 on 2026-10-24, v0.10.1 on 2026-10-08 and v0.10.0 on 2026-09-22. That indicates a fast release cadence, which is good for bug fixes but also means you will need to update frequently to get new features. `codewhale update` upgrades an installed copy. However, frequent releases can introduce regressions, and you should check the changelog for each version. The project is MIT licensed, which is permissive and allows commercial use, but you should review the third-party notices in `THIRD_PARTY_NOTICES.md` for any obligations from adapted code. The README mentions that portions are adapted from other open-source projects, so there may be additional license requirements. The upgrade cost is moderate: you need to track releases and test your workflows after updates. The documentation is in a `docs` folder, and the README is available in many languages, which helps a global community. The repository still contains an `npm/deepseek-tui` workspace. But for new users, the learning curve involves reading the docs to understand the configuration options and safety features.
Editorial conclusion
Adopt CodeWhale if you want a terminal-based coding agent that avoids provider lock-in, supports local models, and gives you visible approval controls and undo capabilities. Skip it if you need a fully documented, production-hardened agent with detailed security guarantees, or if you prefer a project with a longer track record. Before adopting, verify the actual behavior of approval modes, the stability of the Rust runtime on your platform, and the completeness of the docs for your specific provider. The project is under active development, so check the latest release notes and the docs folder for any changes.
Frequently asked questions
what is codewhale
It is an open-source, community-driven agent harness written in Rust that reads your project, edits files, runs commands, and checks its work using a hosted or local model you choose. The pitch is no lock-in: DeepSeek, Claude, GPT, Kimi, GLM, thirty or more providers, and your own vLLM, SGLang or Ollama, all through one runtime and one toolset.
how to install codewhale
On macOS and Linux the file gives one line, `curl -fsSL https://codewhale.net/install.sh | sh`, which puts `codewhale` and its short alias `codew` in `~/.local/bin`; if the shell says `command not found`, run the PATH line the installer prints. On Windows the README lists `winget install HunterBown.CodeWhale` (or Scoop, or the installer from GitHub Releases), and `codewhale update` upgrades an existing install.
codewhale vscode
The VS Code extension is not part of this repository. It is community-maintained, connects to the local Runtime from a sidebar, and its source is at github.com/HengQuWorld/CodeWhale-VSCode with a listing on the VS Code Marketplace under the item name HengQuWorld.brotherwhale-vscode.
code whale vs claude code
CodeWhale lets you choose the model, listing Claude alongside DeepSeek, GPT, Kimi, GLM and thirty or more providers, and also run local models through Ollama, vLLM or SGLang, switching provider with `/provider` and model with `/model`.
Is there a DeepSeek coding agent?
Codewhale is one, and DeepSeek is its default provider. The example environment file lists DEEPSEEK_API_KEY under DeepSeek API as the default provider, alongside NVIDIA NIM keys, an AtlasCloud OpenAI-compatible endpoint, Mistral AI, and a Codewhale account key with the models:infer scope.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/hmbown-codewhale)Star history chart for your README
[](https://hysenlabs.com/projects/hmbown-codewhale)Was this useful?