Dive maintains two desktop architectures, and one of its env vars is a build-time secret
Dive is an open-source MCP Host Desktop Application that seamlessly integrates with any LLMs supporting function calling capabilities. ✨
At a glance
- What is it?
- OpenAgentPlatform/Dive is a cross-platform desktop host for Model Context Protocol servers with a cloud catalogue attached. Windows gets its runtimes bundled, Linux users are told to disable the sandbox, and the cloud token lives in a variable the build inlines into the client.
- Who is it for?
- This suits someone who wants to run several protocol servers from one window and switch models without losing local configuration, since local servers stay supported and the cloud catalogue is described as additive. Three things to know first.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 107 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
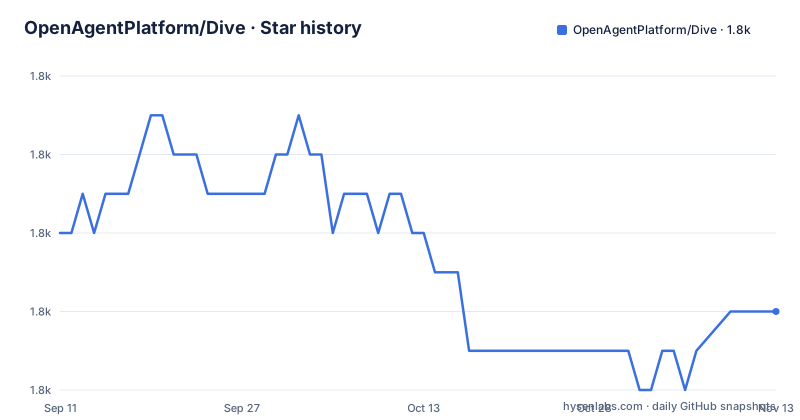
- OpenAgentPlatform/Dive1,824 ★ · -2
| Repository | 2026-09-11 | 2026-11-13 |
|---|---|---|
| OpenAgentPlatform/Dive | 1.8k | 1.8k |
-2 Stars in the last 63 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Two desktop architectures are shipped and maintained together
Dive exists as both an Electron application and a Tauri application, and the page describes them as a dual architecture rather than a migration. The availability table is the honest summary: Windows has both, Linux has both, and macOS has only the Electron build, with the Tauri one marked as coming. That single cell explains the rest of the install section, because the macOS instructions offer one disk image and nothing else. In the repository the duplication is visible as separate directories for the two shells alongside shared, packaged, patched and prebuilt directories, two Vite configurations with one per target, an Electron packaging configuration, a Rust configuration and a lock file. Two front ends means two build pipelines, two sets of native dependencies and one product surface to keep in step.
Windows bundles its runtimes and Linux does not
The build scripts fetch language runtimes per platform, and the sets differ. For Windows there are three fetch steps in one script: the Node binary, a Python environment installer, and Python itself. For macOS the same three steps are repeated once per architecture. For Linux there are two: the environment installer and Python, with no Node binary. The install documentation lines up with that and adds one more asymmetry. On Windows the environments are downloaded automatically after launching. On macOS and on Linux you are told to install Python and Node yourself, and Linux carries extra steps on top: marking the image file executable, adding a sandbox bypass flag or changing system settings to permit the sandbox, and an Arch package whose name differs from the repository's.
Linux users are told how to turn the sandbox off
The Linux section is the most operational part of the documentation and it is worth reading closely. For Ubuntu and Debian it offers two routes: pass a flag that disables the sandbox, or modify system settings to allow it. For Arch it points at an AUR helper with a worked command:
paru -S dive-aiand that package name is not the repository name, which is a small trap for anyone automating an install. The image file also needs its execute bit set before it will run. None of this is exotic for a desktop application packaged as an image file, but it is the difference between an install that works on the first try and one that does not, and the documentation is candid that two of these steps reduce a containment boundary.
The language claim says twenty-four and lists twenty-two
The multi-language feature line claims support for more than twenty-four languages and then names them: English, two varieties of Chinese, Spanish, Japanese, Korean, German, French, Italian, Portuguese, Russian, Thai, Vietnamese, Filipino, Indonesian, Polish, Turkish, Ukrainian, Swedish, Norwegian, Finnish and Lao. That is twenty-two. The gap is small enough to be a counting slip and large enough to matter if you are checking whether your language is covered, because the list is the only place the information exists. The build scripts do at least take translation coverage seriously: there is a dedicated script whose only job is to check it, wired as its own command, so the languages in the interface are machine-verified even if the count in the readme is not.
The cloud token is a variable the bundler inlines
The environment template has five entries and they fall into two groups. Three are Apple signing credentials: a team identifier, an account identifier and a password. The fifth is the interesting one, a token for the hosted catalogue with the prefix that tells the bundler to substitute its value into the client code at build time. That is the standard convention for frontend variables, and it is the reason to be careful here: a value with that prefix is compiled into the shipped application, where anyone can read it out of the bundle. Nothing in the template says whether the token is meant to be a user credential or a shared build secret, and the project describes the hosted service as a one-click sign-in rather than as something a developer configures, so the answer is probably the first. Treating it as public anyway costs nothing.
The updates section is four months old and labelled for another version
The page has a section headed as recent updates, dated 26 February 2026 and labelled for version 0.14.0 and later. The current version is 0.14.3, released on 30 July 2026. So the newest thing described on the page is two releases behind, and the date on it is the date of the 0.14.1 line rather than of the current build. The release history explains why: the gap between 0.14.1 and 0.14.2 is a month, and the gap between 0.14.2 and 0.14.3 is four. A reader looking for what changed recently is looking at a page that has not been revisited since February, and the two features it does mention, skills with slash commands and chat history search, are the only ones announced anywhere on the page.
The Rust workspace has had its dependencies commented out
The Rust configuration is three lines of substance. It declares a workspace, sets the resolver to the current generation, and lists exactly one member, the Tauri shell. Beneath that, a shared dependency section contains two entries that are both commented out: a library referenced by repository and pinned to a specific commit revision, and a local path dependency on a package that the workspace glob is also commented out for. So the Tauri side currently builds with no shared library from this file, whether because the library moved into the repository, moved out, or is not being used yet. The lock file is committed, so a build is reproducible, but the manifest no longer says why the dependency that once structured it is gone.
The project flags its own authentication feature as unstable
The feature list ends with the caveat that matters most, written by the authors themselves. Support for authenticating to protocol servers has been added, and the note under it says the feature is currently unstable and may require frequent re-authorization. That is a candid admission for something that touches credentials, and it sits directly above the features that make the application powerful: built-in local tools that make web requests, read and write files, and execute commands, plus an agent whose job is to install and configure servers for you. The permission surface here is the whole machine, not a sandbox, so the feature to read closely before enabling anything is the one the project has marked unstable.
Editorial conclusion
This suits someone who wants to run several protocol servers from one window and switch models without losing local configuration, since local servers stay supported and the cloud catalogue is described as additive. Three things to know first. Two desktop codebases are maintained at once and macOS has only one of them, so a macOS user is on the older architecture with no stated timeline for the other. The build downloads a different set of language runtimes per platform, which is why the install instructions differ more than you would expect. And the token for the hosted catalogue is read from a variable the bundler inlines, so treat it as public rather than secret.
Frequently asked questions
What is Dive?
It is an MIT-licensed open-source desktop application that hosts Model Context Protocol servers, built with TypeScript and available as both an Electron and a Tauri build. It connects to any model that supports function calling, supports protocol servers over both stdio and server-sent events, and ships with local tools for web requests, file reading and writing, and command execution.
Which platforms does Dive support?
Windows, Linux and macOS, with two builds on Windows and Linux, one Electron and one Tauri. macOS has only the Electron build and the Tauri one is marked as coming. On Windows the smaller Tauri installer is recommended; on Linux the Electron image file is recommended.
Do I need Python and Node.js to run Dive?
On Windows the environments are downloaded automatically after launching the application. On macOS and Linux you are told to install Python and Node yourself, and the build scripts fetch a Python environment installer and Python for Linux but not a Node binary, which matches those instructions.
Can Dive use my own local MCP servers?
Yes. Servers run locally over stdio or server-sent events, individual tools can be enabled or disabled, and the documentation states that existing local server and model configurations remain fully supported with the hosted catalogue treated as an addition that does not affect current workflows. There is also a built-in agent that helps install and configure servers automatically.
Is Dive's MCP server authentication stable?
Not according to the project's own note. Support for authenticating to protocol servers is listed as a feature, and the note under it says the feature is currently unstable and may require frequent re-authorization. It is worth reading that alongside the built-in local tools, which include command execution and file writing.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/openagentplatform-dive)Star history chart for your README
[](https://hysenlabs.com/projects/openagentplatform-dive)Was this useful?