clownfish: an OpenClaw cluster cleanup harness that executes almost nothing
Clownfish is a maintainer codex harness for resolving clusters of issues identified in bulk at scale. 🐠
At a glance
- What is it?
- clownfish classifies issue and PR clusters that a human or a dedupe tool already grouped, and is allowed to close items for three reasons only. Its own dashboard records two executed fix actions out of 316 attempts, which is the clearest statement of how conservative it is.
- Who is it for?
- clownfish suits an OpenClaw maintainer who already has clusters grouped and wants a second pass that proposes rather than acts, with a recorded audit trail of every attempt. It does not suit anyone expecting a backlog sweeper, since discovery is somebody else's job, and it is not a security triage tool by design.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- No. The owners have archived the repository on GitHub, so it is read-only and no longer receives changes.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
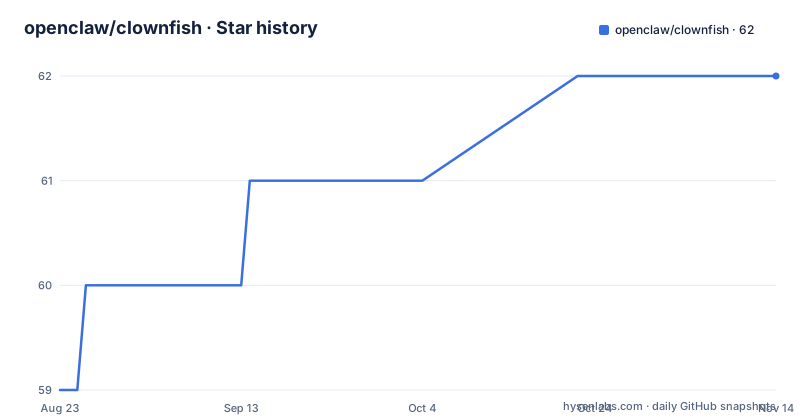
- openclaw/clownfish62 ★ · +3
| Repository | 2026-08-23 | 2026-11-14 |
|---|---|---|
| openclaw/clownfish | 59 | 62 |
3 Stars in the last 83 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Only three close reasons are permitted
The allowlist is the whole policy, and it is three lines long. An automated close is permitted when the item is a duplicate of a clear canonical thread, when it is superseded by a clear canonical thread, or when it is fixed by a specific candidate fix. Each of the three demands evidence: a canonical thread to point at, or a named fix. Everything else stays open or is escalated for maintainer review, which is stated without softening. The classification step is delegated to a Codex worker, so the model decides which of these applies and the harness decides whether the decision is allowed to become an action. The work is described as complementary to the pre-pass work done by clawsweeper, and as a second pass based on intent rather than a first pass over the whole backlog.
Proposal-first, with execution off in the shipped defaults
The default workflow does not comment and does not close. It writes proposals, and an action only happens when a job is explicitly promoted and the deterministic applicator confirms that live GitHub state has not changed since the proposal was made. The environment file ships the same opinion in configuration form:
CLOWNFISH_ALLOWED_OWNER=openclaw
CLOWNFISH_ALLOW_EXECUTE=0
CLOWNFISH_ALLOW_FIX_PR=0
The owner is pinned rather than configurable to anything wider, and both the execute switch and the fix pull request switch are zero. Reading the file top to bottom shows the same shape elsewhere: three GitHub token variables and an OpenAI key, a Codex key, hydration toggles for cluster references and comments that are on, and hard caps at 30 comments per item, 20 linked references and 50 review comments per pull request, with two Codex review attempts and review-thread resolution enabled.
Two executed fix actions out of 316 attempts
The dashboard in the README is the most useful page in the repository, because it reports the tool's own effectiveness against itself. Out of 316 fix action attempts, 2 were executed, which the table puts at 0.6 percent. 68 attempts failed, 21.5 percent, and 115 were blocked, 36.4 percent, with 94 latest clusters showing fix failures at 2.2 percent. Below that sit two more rows that explain the arithmetic: 198 blocked mutation attempts at 42.5 percent and 156 skipped mutation attempts at 33.5 percent. The close actions split into 72 completed closes at 15.5 percent, 40 completed merge actions at 8.6 percent, and by reason 25 duplicate closes, 22 superseded closes and 15 fixed-by-candidate closes, while low-signal PR closes stand at exactly zero.
More than a quarter of clusters end as needs human
Scope and outcomes are reported separately, and the numbers describe a machine that mostly declines. The scope line covers 4,178 active latest cluster reports, with 4 policy-archived clusters excluded from the health statistics and run attempts tracked as audit history only. Of those clusters, 2,722 completed clean at 65.2 percent and 1,188 are marked needs human at 28.4 percent. On the run side, 4,022 latest clusters succeeded at 96.3 percent, 99 failed at 2.4 percent and 3 were cancelled at 0.1 percent, with 5,340 run attempts archived. The dashboard carries its own timestamp, last update Jun 16, 2026 at 09:45 UTC, so these are a snapshot of one day rather than a live figure, and the state line at the top says failed clusters need inspection.
Security-sensitive refs are routed out, not closed
Security reports are declared out of scope on purpose. When such a ref appears in a cluster, clownfish routes it to central OpenClaw security handling and keeps processing the unrelated ordinary bugs, provider gaps and duplicate cleanup in the same cluster, so one quarantined item does not stall the rest. The boundary is defined by following OpenClaw's SECURITY.md, and the definition is narrower than most people expect: trusted-operator exec behaviour, provider gaps, feature gaps and hardening-only parity drift are not treated as vulnerabilities unless there is a real trust-boundary bypass. The inspection table shows the mechanism at work, with one cluster reporting that a ref was required by deterministic validation to route to security, which quarantined the previously selected open canonical path.
The low-signal policy exists and has closed nothing
There is a second, wider policy for manual backlog cleanup, and it is opt-in per job. It lives in `instructions/low-signal-prs.md` and covers drive-by pull requests that are clearly blank-template, docs-only discoverability churn, test-only coverage spam, refactor-only noise, third-party capabilities that belong on ClawHub, risky unapproved infra, or dirty branches. The same file requires such a job to return `needs_human` for a plausible bug fix or for anything carrying active maintainer signal, so the categories describe noise rather than disagreement. The dashboard's corresponding row, low-signal PR closes, is 0 at 0.0 percent, which is the honest reading: the policy is defined, wired into the importers, and has not yet been used to close a pull request.
Discovery is somebody else's job
The scope statement draws a line against clawsweeper. ClawSweeper scans the whole OpenClaw backlog on a cadence; clownfish is intentionally smaller and handles targeted clusters that were already grouped by a human, by gitcrawl, or by another dedupe tool, and cluster discovery currently comes from openclaw/gitcrawl. That division is why the script list in package.json is so import-heavy: separate importers exist for gitcrawl clusters, gitcrawl low-signal pull requests, gitcrawl pull request inventory and GitHub pull request inventory, the last of which accepts a low-signal strategy flag. Around them sit the worker, the applicator, an execute-fix script, a mutation integrity assertion, external merge preflights, a post-flight, open pull request finalisation, a comment router, stuck job promotion and a job sweeper. The package is private, typed as a module, versioned 0.1.0, and tested with node's own test runner.
Editorial conclusion
clownfish suits an OpenClaw maintainer who already has clusters grouped and wants a second pass that proposes rather than acts, with a recorded audit trail of every attempt. It does not suit anyone expecting a backlog sweeper, since discovery is somebody else's job, and it is not a security triage tool by design. Before running it, read the environment defaults, where execution and fix pull requests both ship disabled and the allowed owner is pinned, and expect most clusters to end in needs human: the dashboard puts that at 28.4 percent, with 65.2 percent completing clean. The repository is now archived and read-only; check the project documentation for its current status.
Frequently asked questions
What can clownfish close automatically in OpenClaw?
Three reasons only: a duplicate of a clear canonical thread, superseded by a clear canonical thread, or fixed by a specific candidate fix. Everything else stays open or is escalated for maintainer review, and the default workflow does not comment or close unless a job is explicitly promoted.
What does clownfish need to run?
The environment file lists three GitHub token variables, an OpenAI key and a Codex key, since a Codex worker does the classification. It also pins the allowed owner to openclaw and ships with CLOWNFISH_ALLOW_EXECUTE=0 and CLOWNFISH_ALLOW_FIX_PR=0, so no mutation happens until those are changed.
How does clownfish differ from clawsweeper?
clawsweeper scans the whole OpenClaw backlog on a cadence, while clownfish is intentionally smaller and only handles targeted clusters that were already grouped by a human, by gitcrawl, or by another dedupe tool. It acts as a second pass based on intent rather than a first pass over everything.
Does clownfish handle security vulnerability reports?
No, security-sensitive reports are deliberately out of scope. Those refs are routed to central OpenClaw security handling while unrelated ordinary bugs, provider gaps and duplicate cleanup continue in the same cluster, following OpenClaw's SECURITY.md definition of what counts as a vulnerability.
How often does clownfish actually change anything?
Rarely, by its own dashboard. Of 316 fix action attempts, 2 were executed at 0.6 percent, 68 failed and 115 were blocked, while of 4,178 active latest cluster reports 2,722 completed clean at 65.2 percent and 1,188 ended as needs human at 28.4 percent.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/openclaw-clownfish)Star history chart for your README
[](https://hysenlabs.com/projects/openclaw-clownfish)Was this useful?